
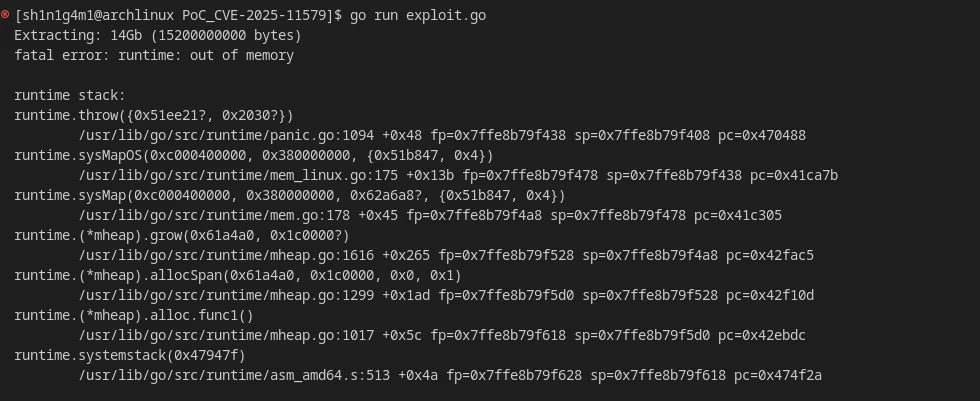
PoC_CVE-2025-11579
 shinigami-777/poc_cve-2025-11579
Proof-of-concept exploit for CVE-2025-11579, a denial-of-service vulnerability in rardecode that triggers an out-of-memory crash via a crafted RAR…
binary-analysisexploitationfuzzing+1
shinigami-777/poc_cve-2025-11579Proof-of-concept exploit for CVE-2025-11579, a denial-of-service vulnerability in rardecode that triggers an out-of-memory crash via a crafted RAR…
 kiyochii/cve-2026-29628
Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 dsecuredcom/ffufpostprocessing
Golang tool which helps dropping the irrelevant entries from your ffuf result file.
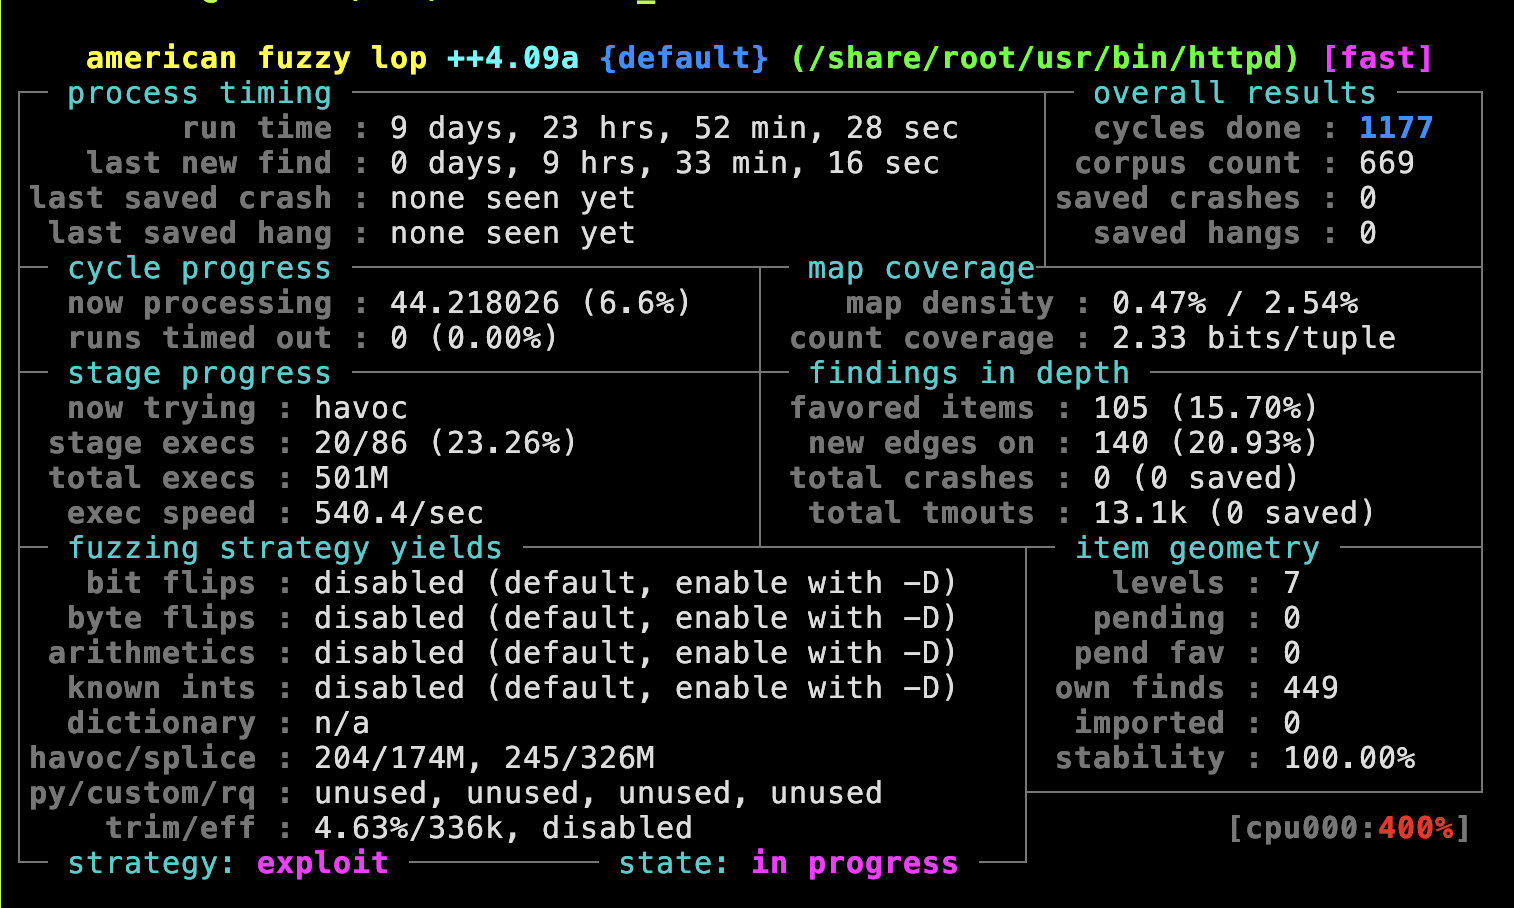 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
 nccgroup/triforceafl
AFL/QEMU fuzzing with full-system emulation.
 nccgroup/triforcelinuxsyscallfuzzer
A linux system call fuzzer using TriforceAFL
 noxxi/mime-is-broken
Test cases for broken MIME and tools to generate and process these
 alone/mutator
Generate mutations over a wordlist
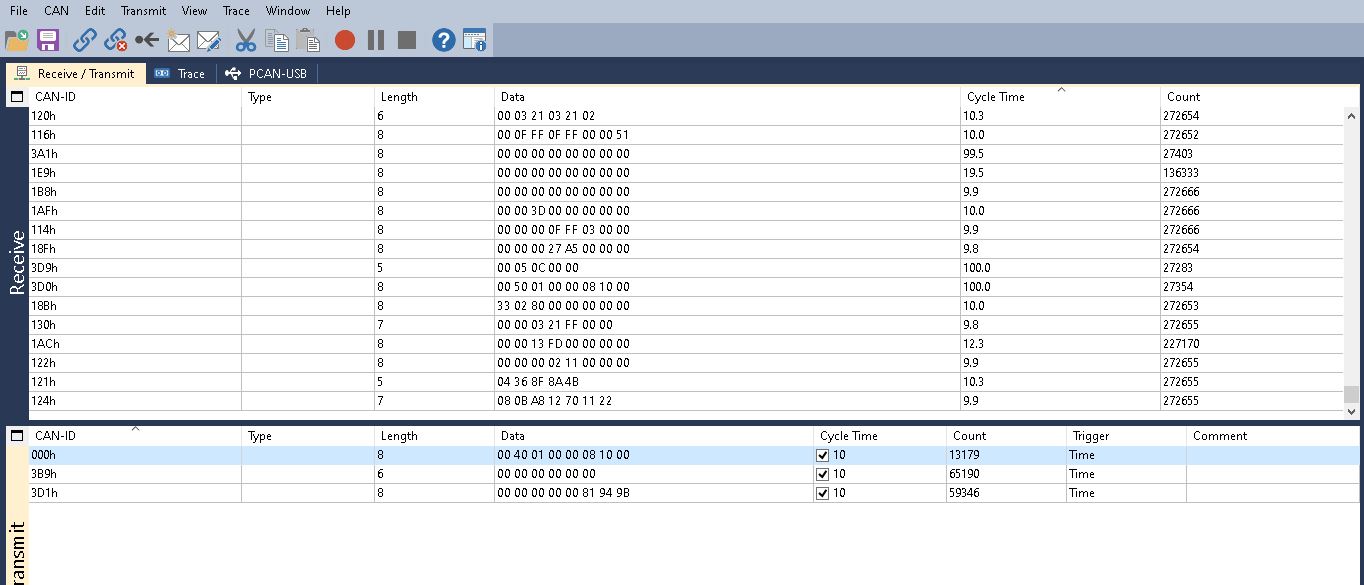 nsbogam/cve-2022-26269
Suzuki connect app is used to get the car information like Fuel, Ignition status, Current location, Seat buckle status etc. In Ignis, Zeta variant…
 rishvic/xpdf-docker
Docker images of Xpdf 4.04, vulnerable to CVE-2022-30524
 halcy0nic/cve-2022-36234
Proof of concept for CVE-2022-36234
 manhndd/cve-2019-19012
Integer overflow in Oniguruma
 tarantula-team/cve-2019-19012
An integer overflow in the search_in_range function in regexec.c in Oniguruma 6.x before 6.9.4_rc2 leads to an out-of-bounds read
 mk219533/cve-2010-1205
sample exploit of buffer overflow in libpng
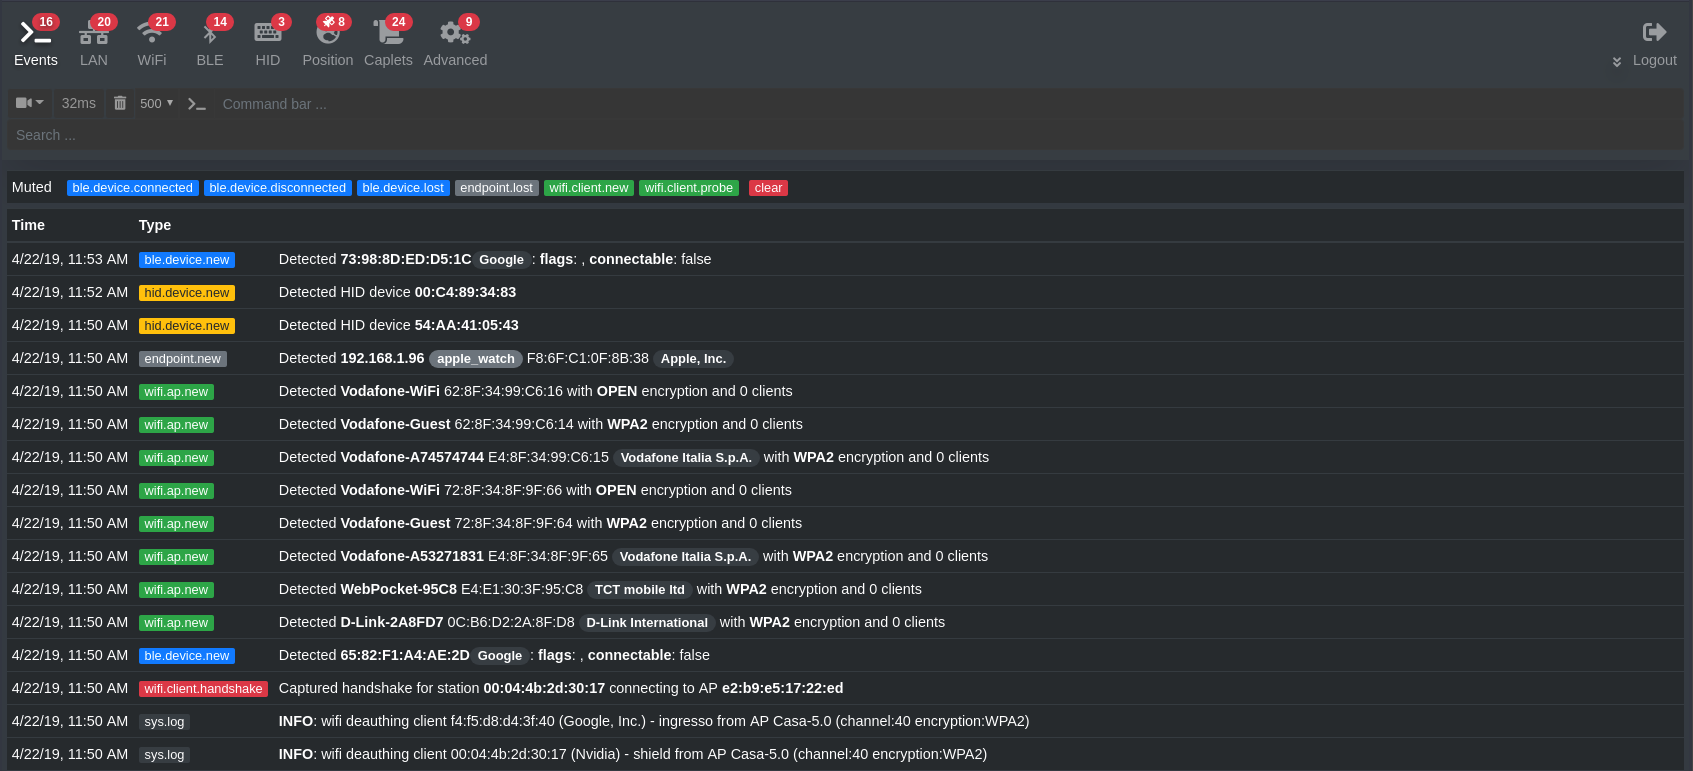 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 jgajek/killasa
Exploit tool for CVE-2016-1287 that tests Cisco ASA devices by sending crafted IKEv2 fragments with invalid lengths to trigger denial of service.
 caoweiquan322/notenough
This tool calculates tricky canonical huffman histogram for CVE-2023-4863.