
rcekit
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
command-and-controlexploitationfuzzing+8
14
kabiri-labs/rcekitRCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 safety-research/red-teaming-auto-mode
Research code for red-teaming AI auto-mode monitors, including simulation evals, fuzzing, and monitor implementations for Claude Code and Codex…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
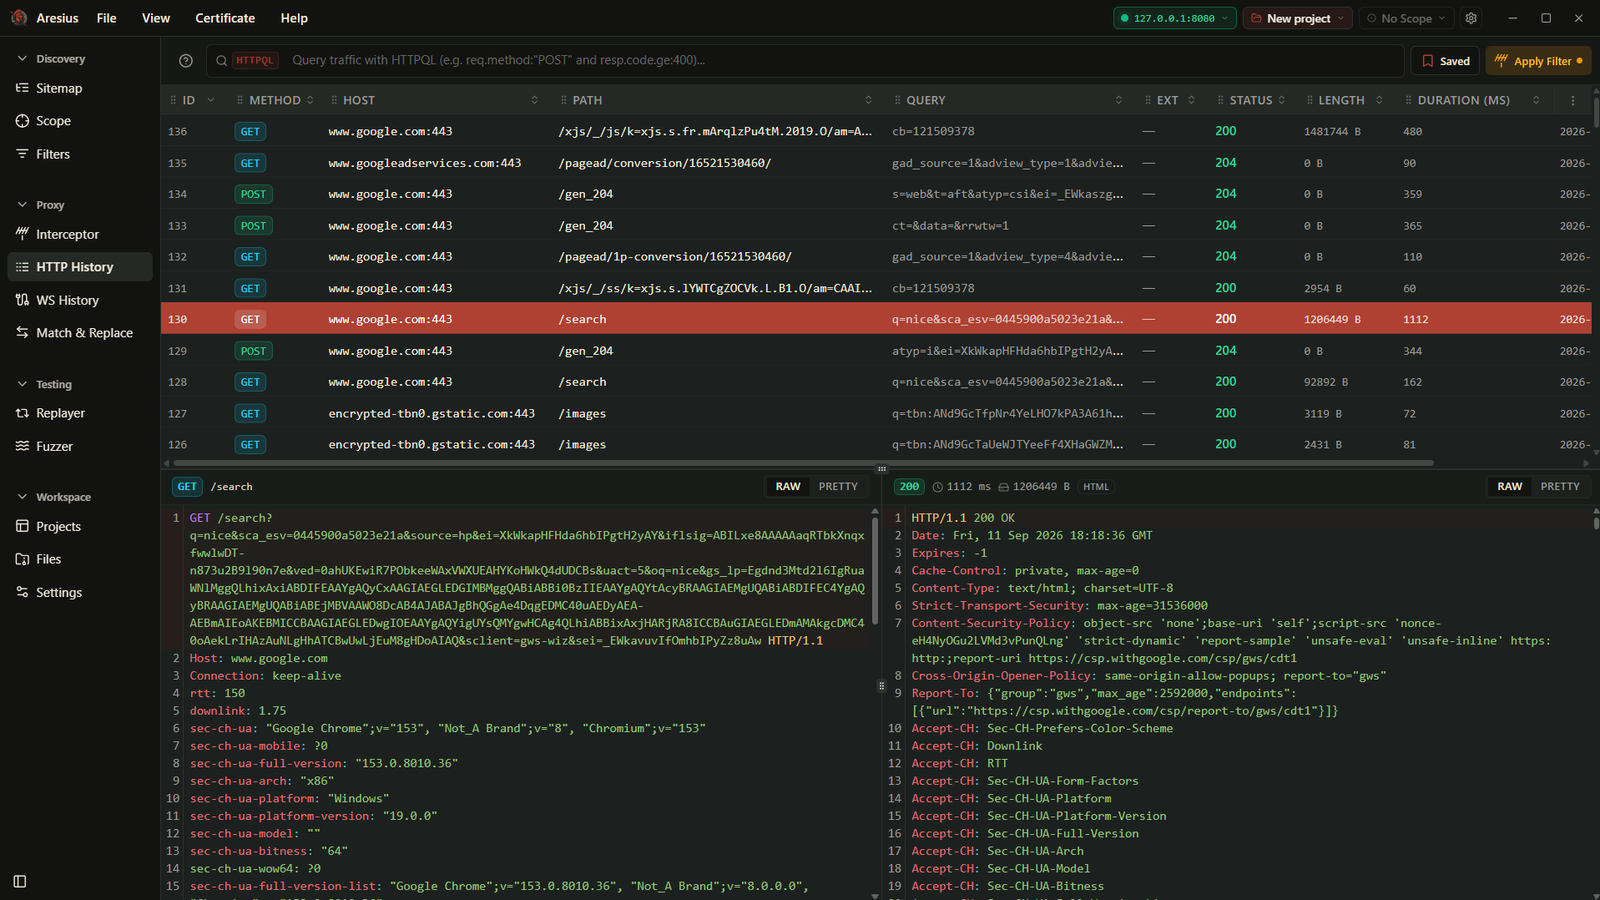 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 vardhan0257/upb-any-recursion-audit
Audit harness testing whether the CVE-2026-0994 Any-unwrapping recursion bug class affects upb's C core in Ruby and PHP protobuf bindings, with…
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 yolkfull/cve-2026-52910-poc
Race reproducer and stress toolkit for CVE-2026-52910, a Linux kernel use-after-free in reuseport cBPF selector programs, with dmesg and leak checks.
 m4rc0s-s3c/cve-2025-5548-freefloat-ftp-lab
Laboratorio académico de análisis y explotación de CVE-2025-5548 en FreeFloat FTP Server 1.0.
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 harshrajsinghania/cve-2026-90781-alsa-lib-oob
Standalone reproducer for CVE-2026-90781: 1-byte OOB write in alsa-lib __snd_ctl_ascii_elem_id_parse() name= parsing (quoted and unquoted)
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 harshrajsinghania/cve-2026-86547-mrubyc-op-enter
Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
 nathan-luevano/silica
Exhaustive differential validation of all 4.3B AArch64 instruction encodings.