Bug-Bounty-Wordlists

Curated collection of wordlists for bug bounty hunting, covering directories, subdomains, parameters, usernames, passwords, and web fuzzing payloads.

Curated collection of wordlists for bug bounty hunting, covering directories, subdomains, parameters, usernames, passwords, and web fuzzing payloads.

针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)

Proof of Concept (PoC) for a stack-based buffer overflow in Steghide 0.5.1. Demonstrates how long file paths trigger a crash (DoS) and leak sensitive…

Git All the Payloads! A collection of web attack payloads.

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…

WiFi Penetration Testing & Auditing Tool

Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…

Super Simple Python Word List Generator for Fuzzing and Brute Forcing in Python

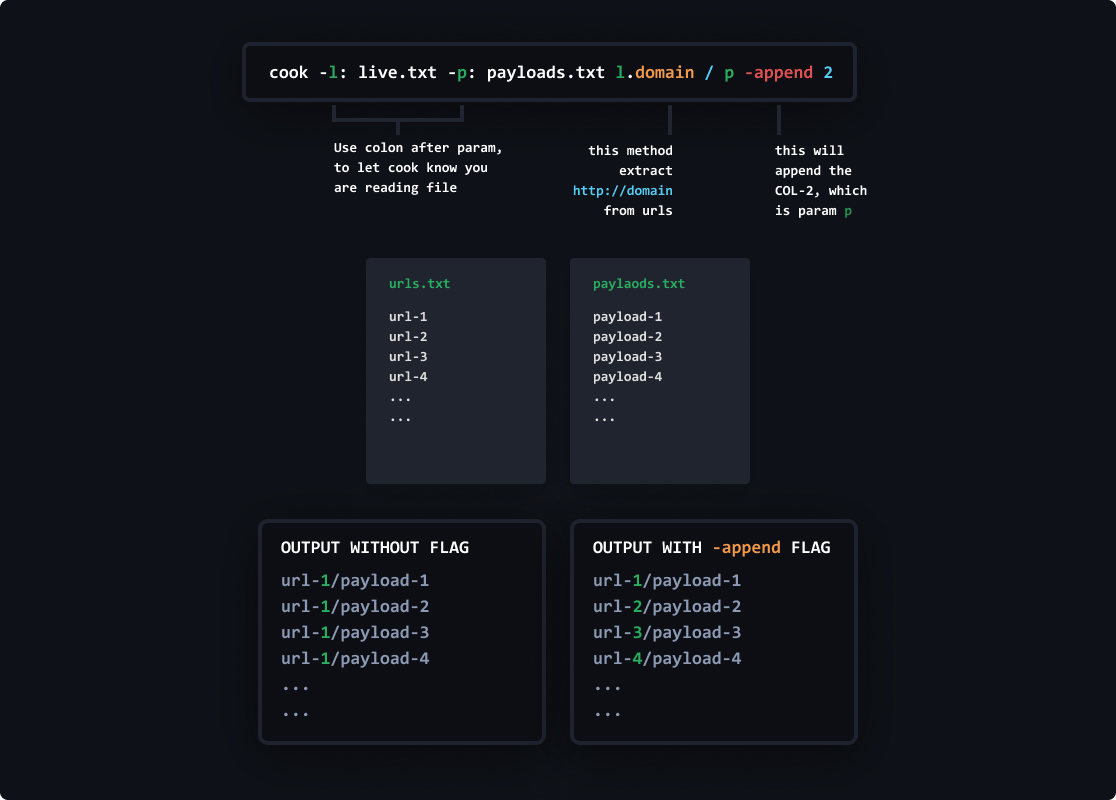
A wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.

A full-featured open-source Wi-Fi fuzzer