
log4j-fuzzer
 mr-vill4in/log4j-fuzzer
Automated scanner for CVE-2021-44228 (Log4Shell) that tests single or multiple web targets for the vulnerability using remote callback servers.
exploitationfuzzingpenetration-testing+2
mr-vill4in/log4j-fuzzerAutomated scanner for CVE-2021-44228 (Log4Shell) that tests single or multiple web targets for the vulnerability using remote callback servers.
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 wireghoul/dotdotpwn
DotDotPwn - The Directory Traversal Fuzzer
 juanschallibaum/cve-2024-38473-nuclei-template
Nuclei template to detect Apache servers vulnerable to CVE-2024-38473
 ianxtianxt/cve-2019-5096-goahead-web-server-dos-exploit
Python exploit for CVE-2019-5096, a use-after-free vulnerability in GoAhead web server's upload handler, causing denial of service via double-free.
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 liamg/scout
🔭 Lightweight URL fuzzer and spider: Discover a web server's undisclosed files, directories and VHOSTs
 musana/fuzzuli
Domain-aware URL fuzzer that dynamically generates wordlists to discover exposed backup and sensitive files on web servers.
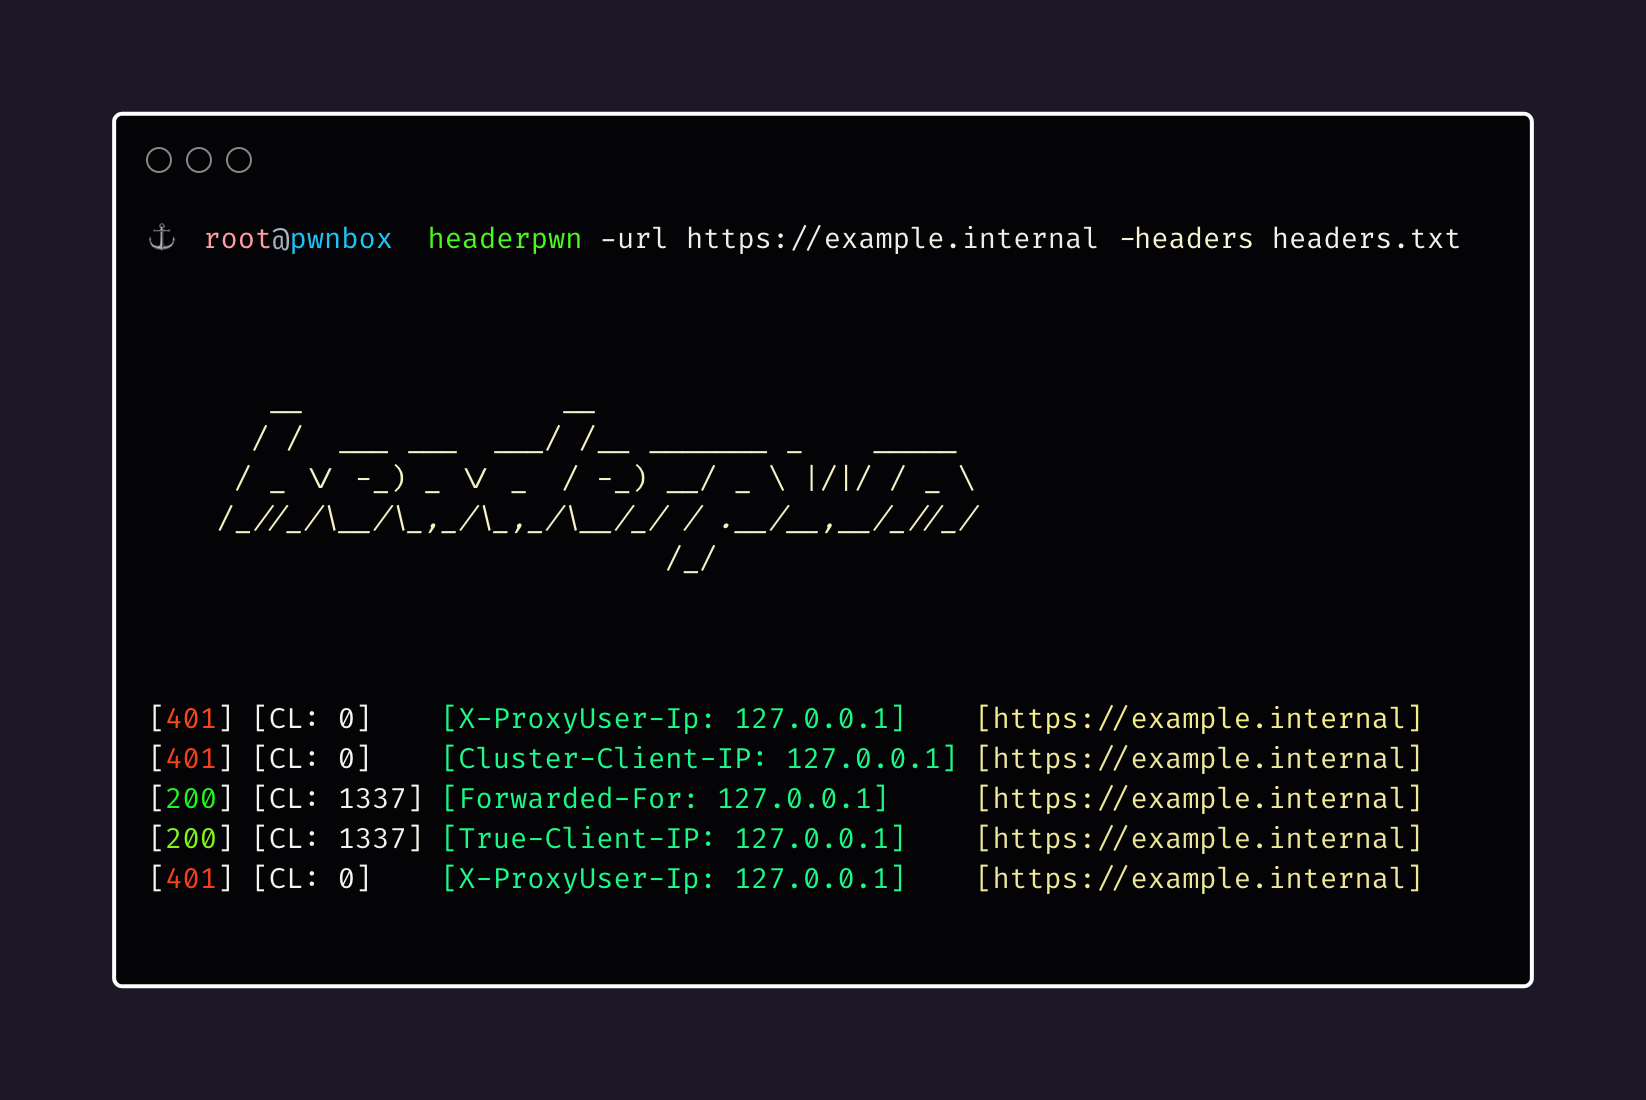 devanshbatham/headerpwn
A fuzzer for finding anomalies and analyzing how servers respond to different HTTP headers
 sec-tools/litefuzz
A multi-platform fuzzer for poking at userland binaries, network clients and servers