
Rogue-Framework
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
binary-analysisdebuggersdynamic-analysis-sandboxing+4
19
thisistfs/rogue-frameworkDesktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
 openrce/paimei
A reverse engineering framework written in Python.
 bishopfox/joro
A collaborative web exploitation framework.
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 jesusprubio/bluebox
A collection of exploits for different VoIP products.
 payatu/cve-2018-14442
PoC for Foxit Reader CVE-2018-14442
 j4ck3lsyn-gen2/cve-2026-39047
Epson Printer RAW Protocol Exploit Framework
 dark-life944/cve-2025
This is POC for IOS 0click CVE-2025-43300
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)

 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
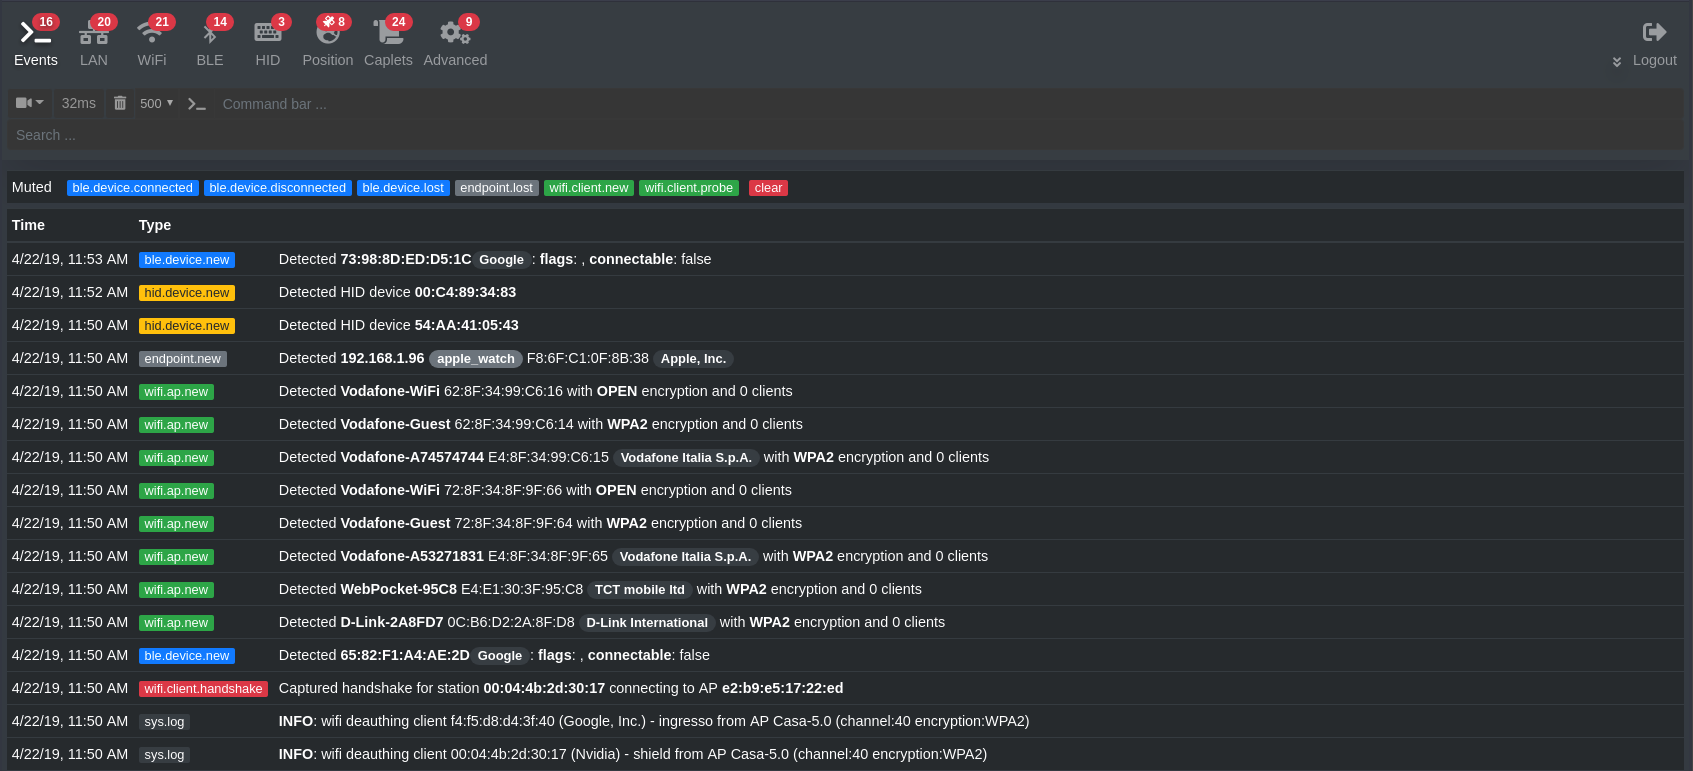 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.