
Awesome-Hacking
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
ctfcurated-resourceseducation+7
121.9k
hack-with-github/awesome-hackingA collection of various awesome lists for hackers, pentesters and security researchers
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
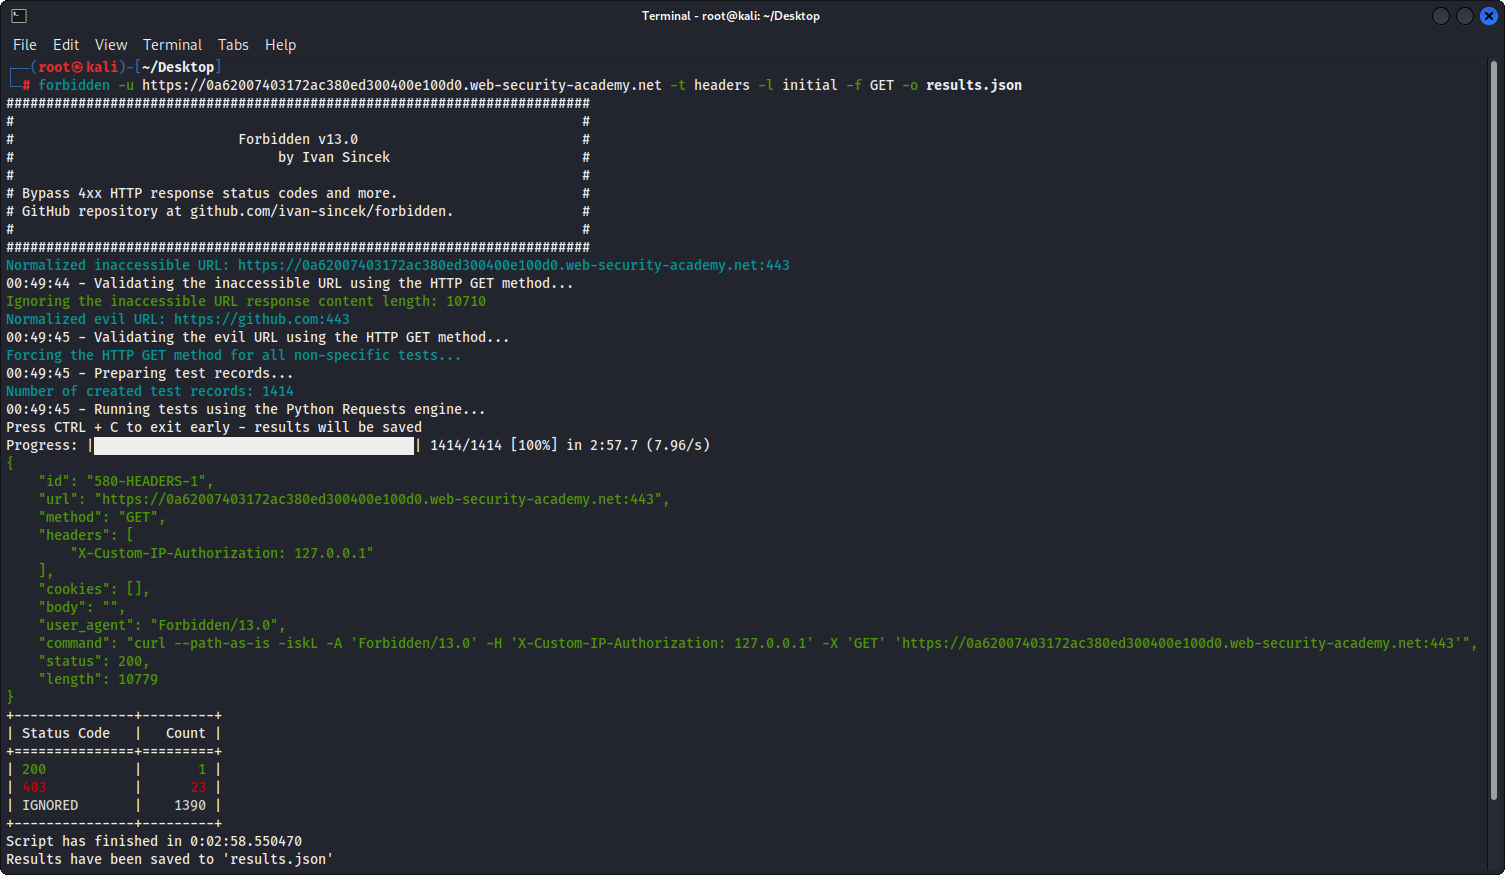 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing

 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 d3ckx1/omniscan
Multi-engine vulnerability scanner with built-in Nuclei Lite, Afrog, and XRay engines. Features asset discovery via FOFA/Shodan, OOB interaction…
 quarkslab/rewind
Snapshot-based coverage-guided windows kernel fuzzer
 niloofarkheirkhah/nili
Nili is a Tool for Network Scan, Man in the Middle, Protocol Reverse Engineering and Fuzzing.
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…