

ESP32-DIV
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
bluetooth-securityeducationembedded-systems-security+8
4.1k
cifertech/esp32-divESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 yolkfull/cve-2026-52910-poc
Race reproducer and stress toolkit for CVE-2026-52910, a Linux kernel use-after-free in reuseport cBPF selector programs, with dmesg and leak checks.
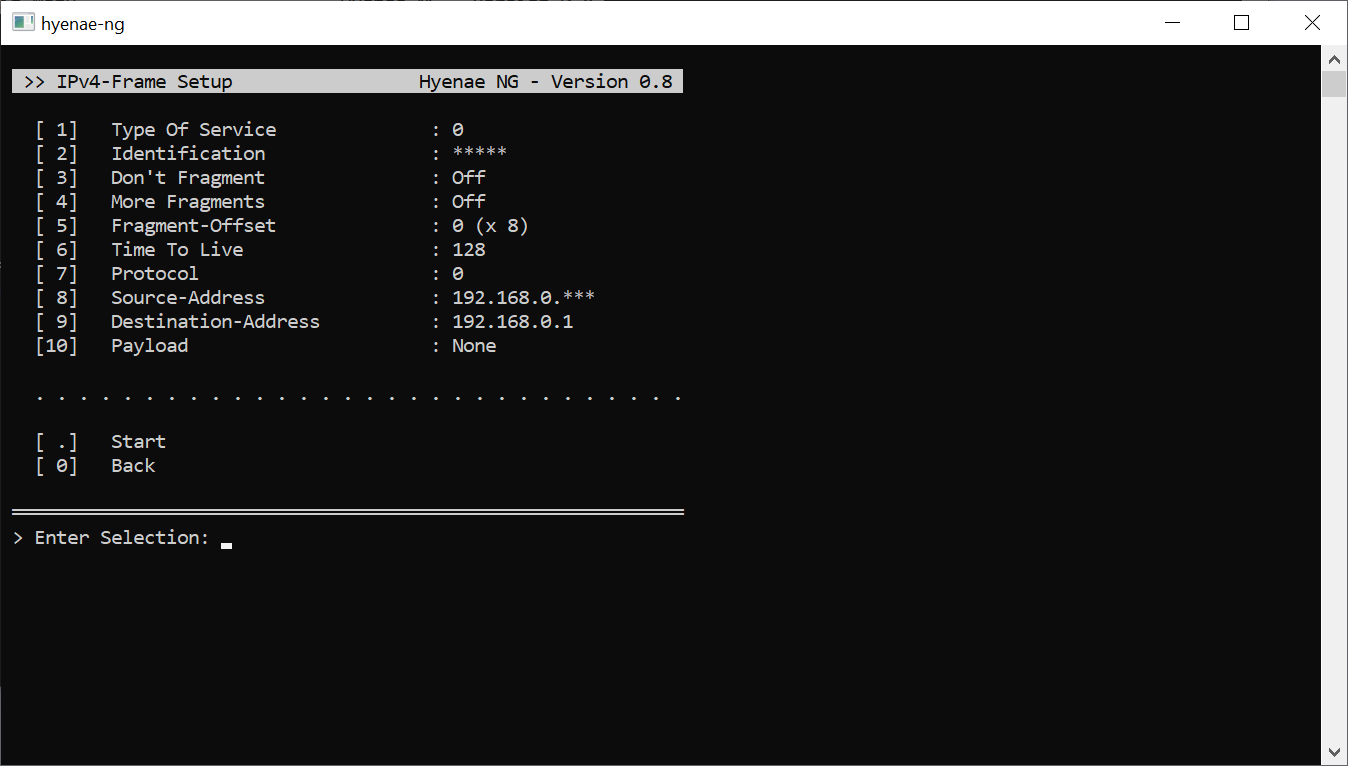 r-richter/hyenae-ng
Cross-platform network packet generator with full layer spoofing, pattern-based address randomization, and flood detection evasion for stress-testing…
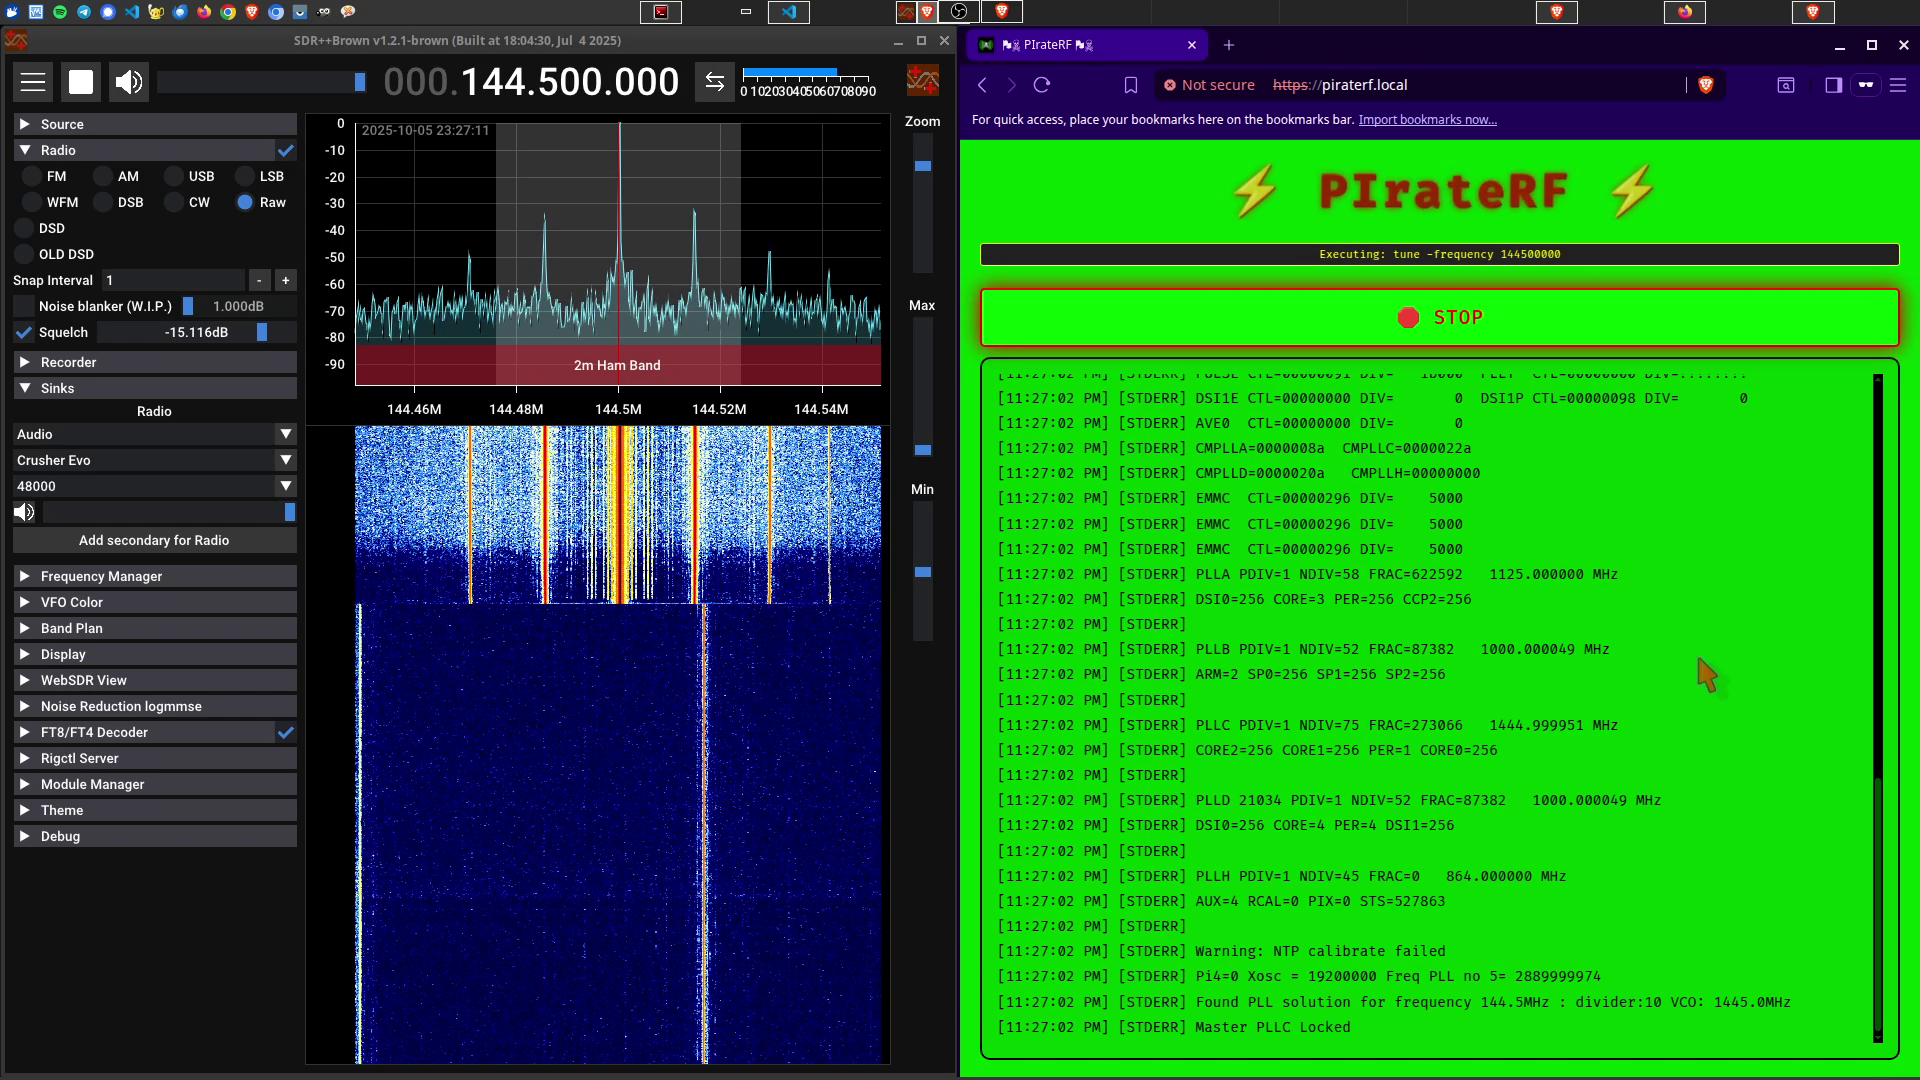 psyb0t/piraterf
PIrateRF transforms your Raspberry Pi Zero W into a portable RF signal generator that spawns its own WiFi hotspot. Control everything from FM…
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 dzonerzy/gowapt
Go Web Application Penetration Test
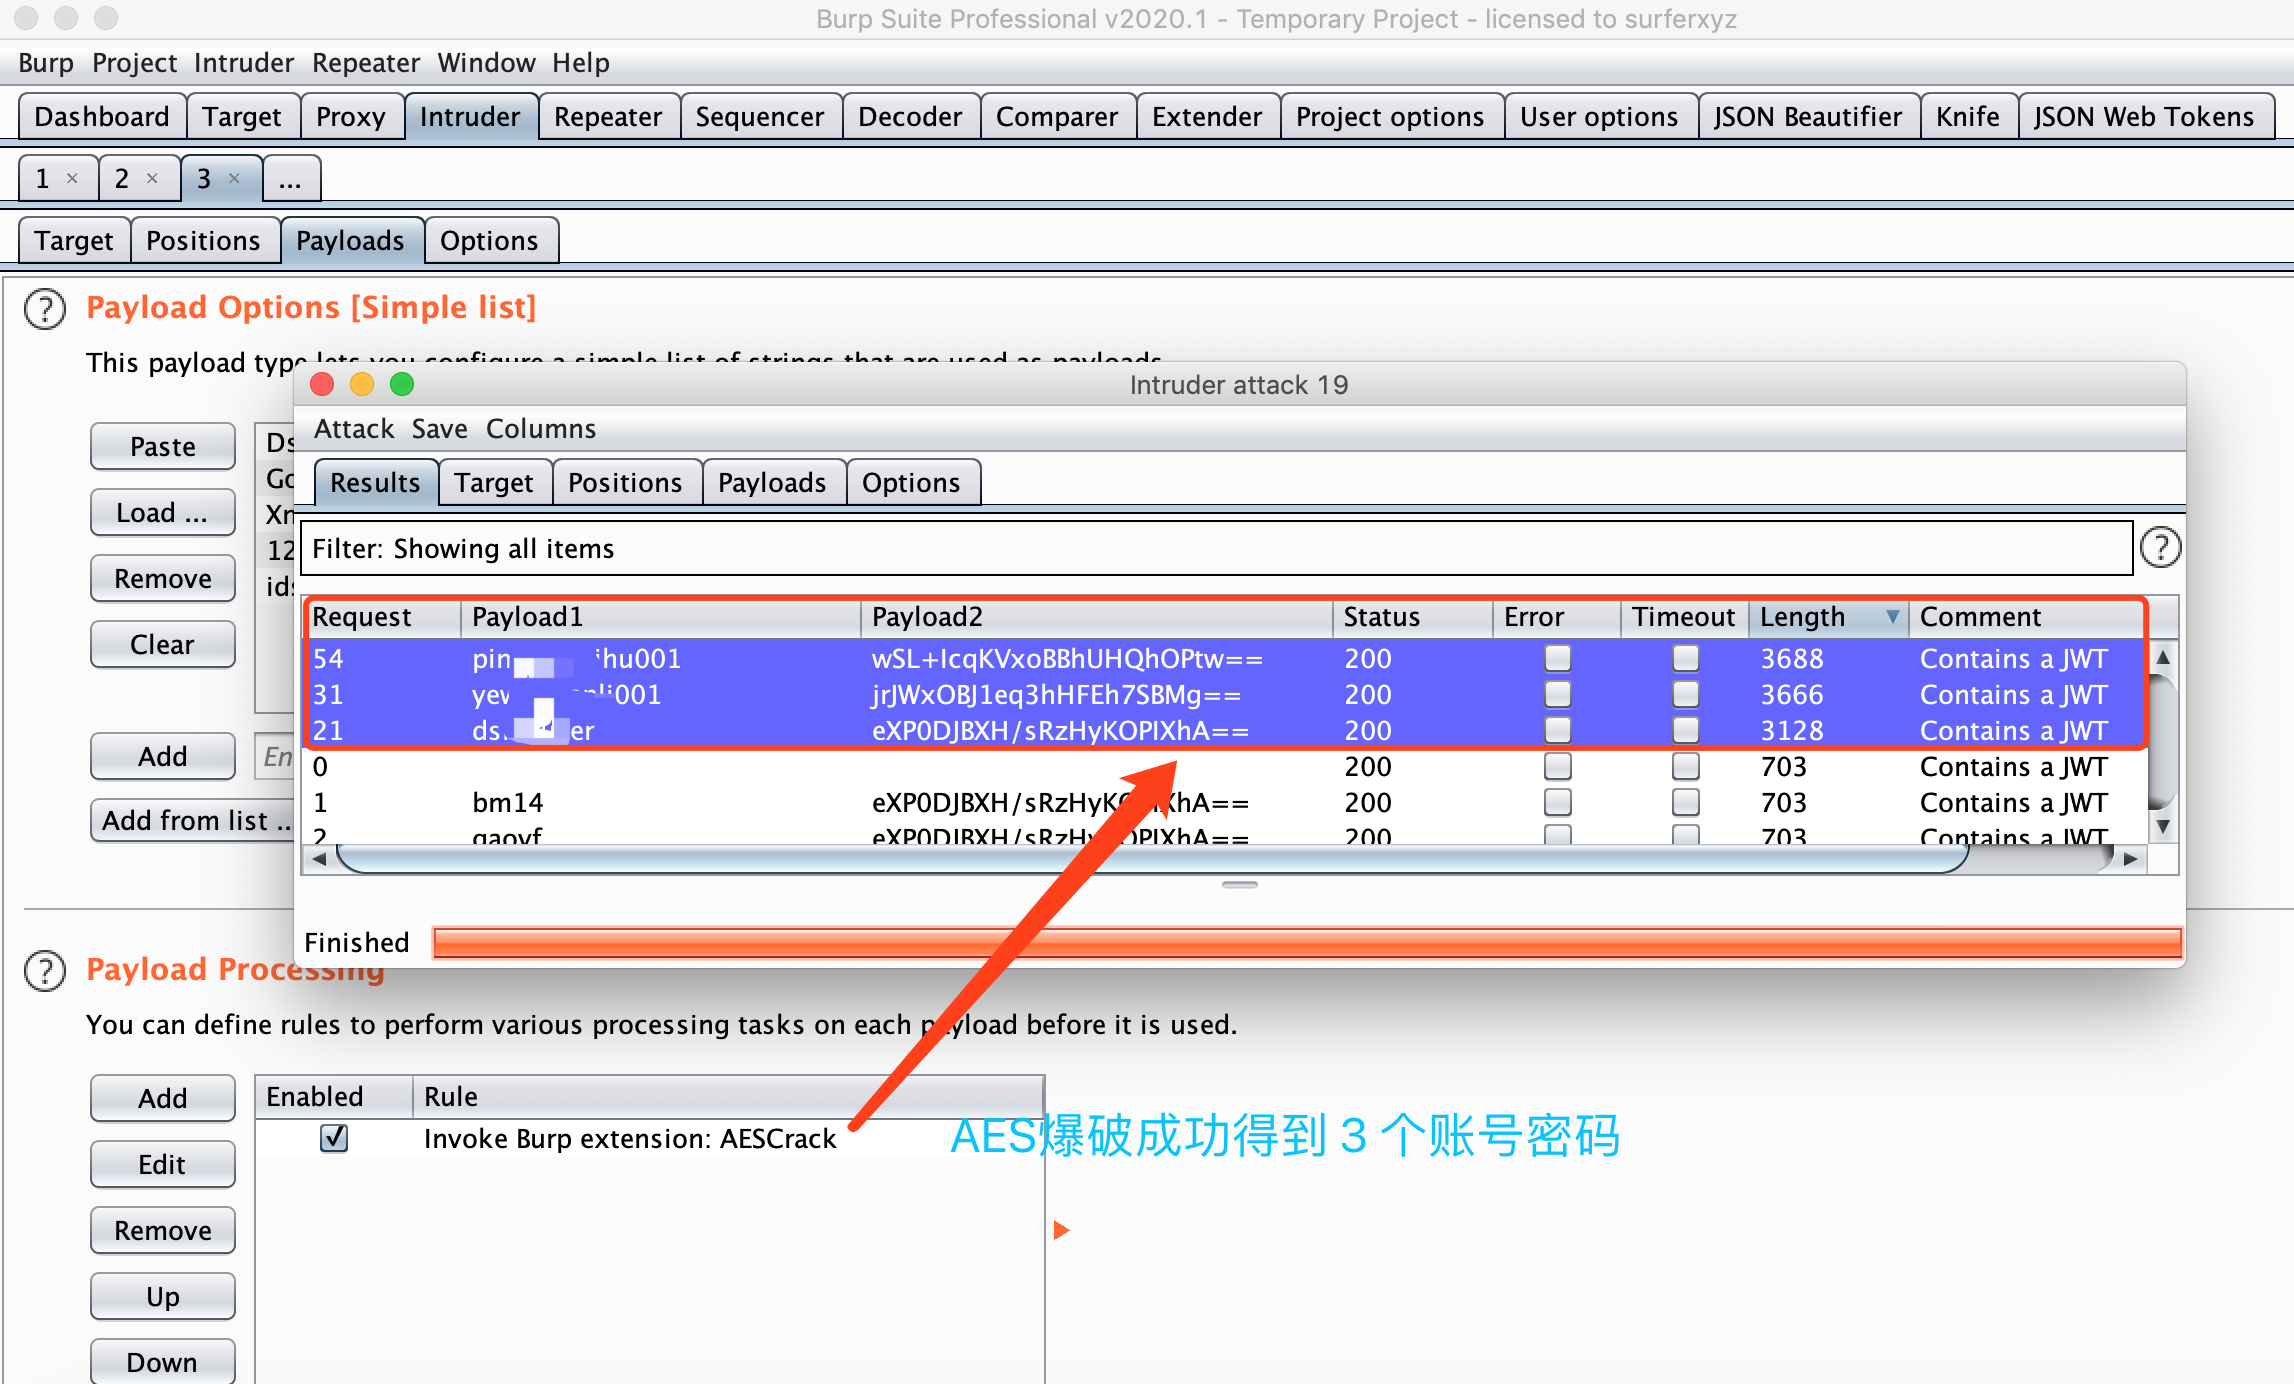 jas502n/burp_aes_plugin
Burpsuite Plugin For AES Crack
 personnumber3377/dns_client_fuzzing
Fuzzing the Microsoft Windows DNS client library. Inspired by CVE-2026-41096.
 liveoverflow/webp-cve-2023-4863
Educational repository demonstrating CVE-2023-4863 exploitation in libwebp using AFL++ fuzzing, with step-by-step video walkthroughs for…
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)