ActiveScanPlusPlus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…

PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo

PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.

Advisory for CVE-2025-69720: stack-based buffer overflow in GNU ncurses infocmp (CWE-121)

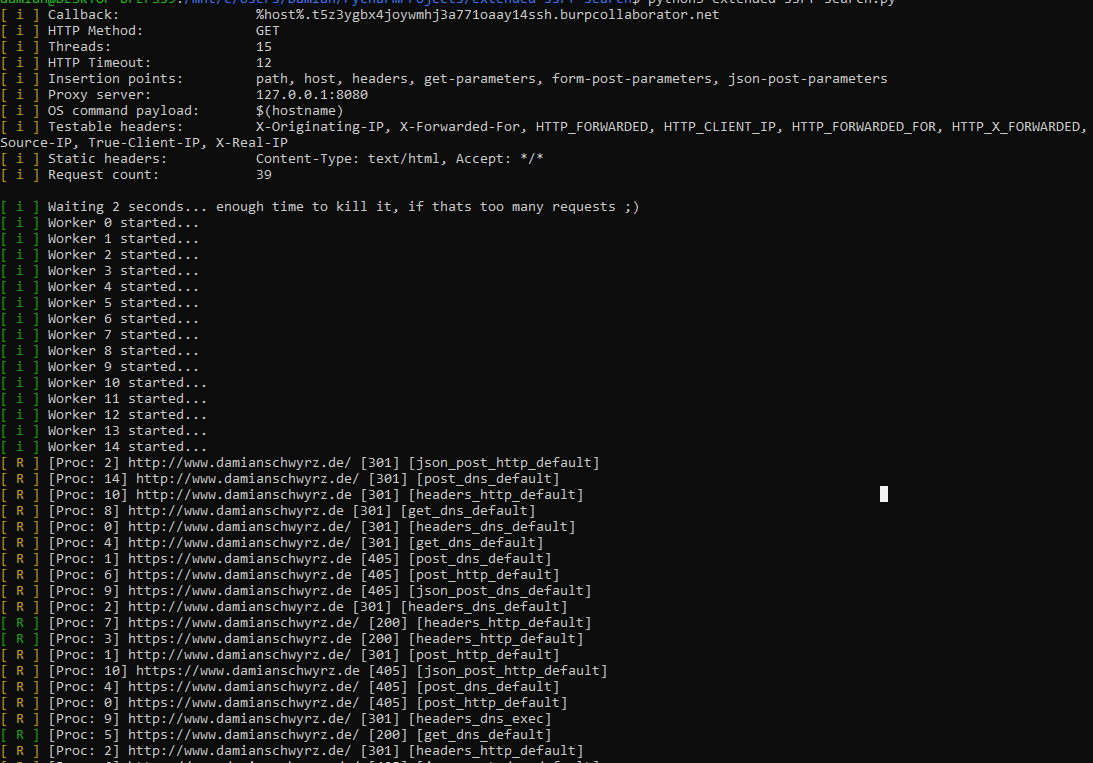
Smart ssrf scanner using different methods like parameter brute forcing in post and get...

Directory/File, DNS and VHost busting tool written in Go

A multi-platform fuzzer for poking at userland binaries, network clients and servers

Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.

An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…

A fake host that can be "managed" by Dell OMSA, getting you past the login screen.

Umap2 is the second revision of NCC Group's python based USB host security assessment tool.


ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…

Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…