

rcekit
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
command-and-controlexploitationfuzzing+8
27
kabiri-labs/rcekitRCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…

 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 4minx/cve-2026-14266
CVE-2026-14266 - XZ Heap Buffer Overflow PoC Generator for 7-Zip
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
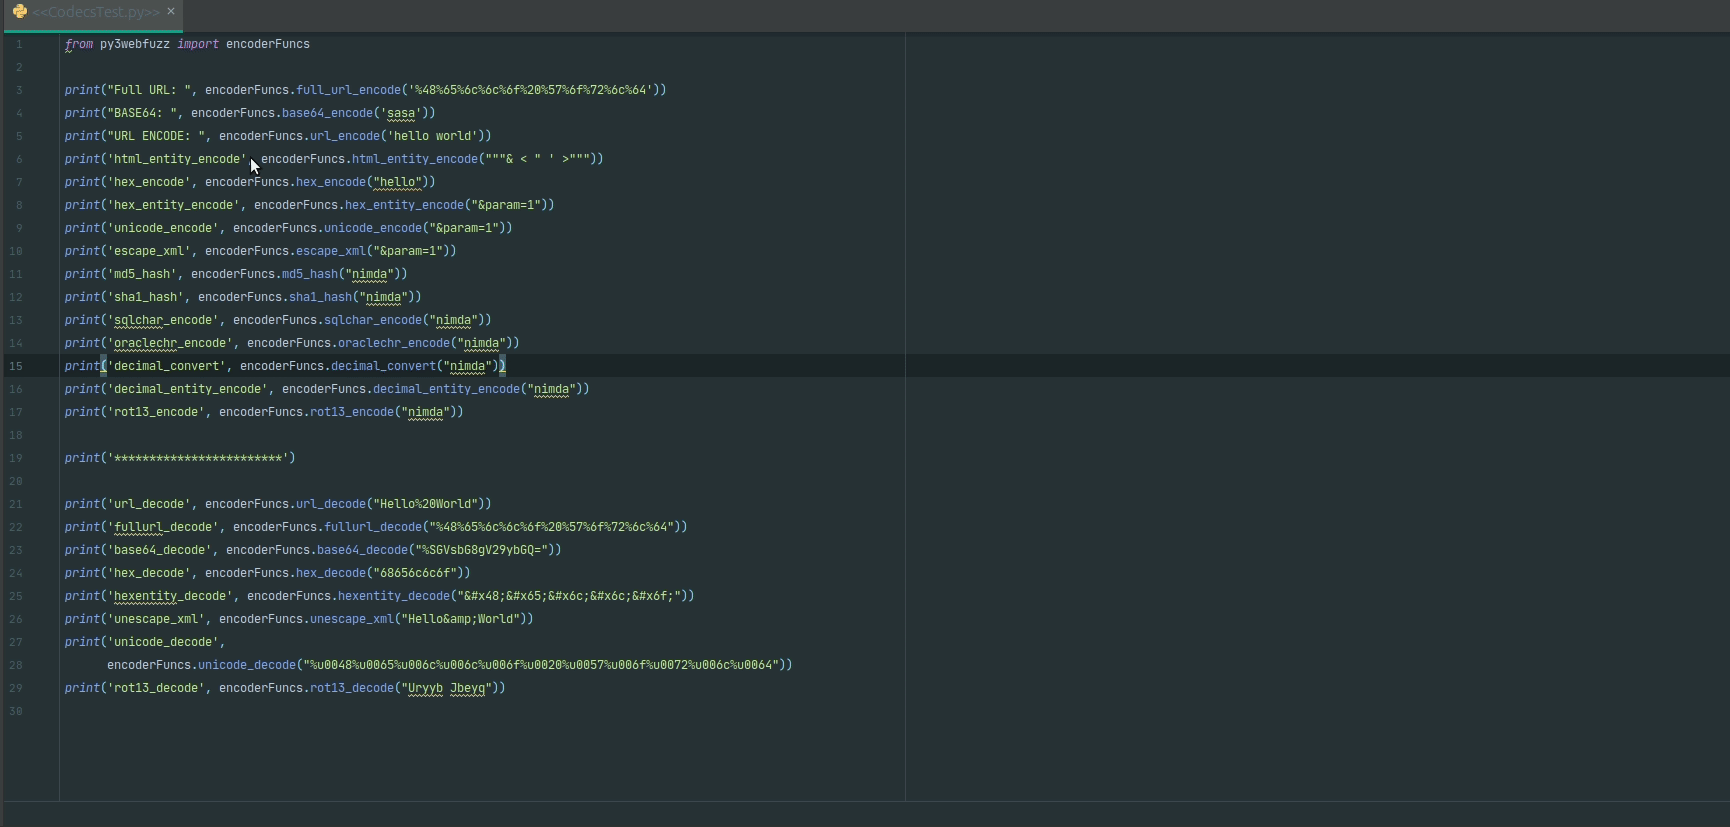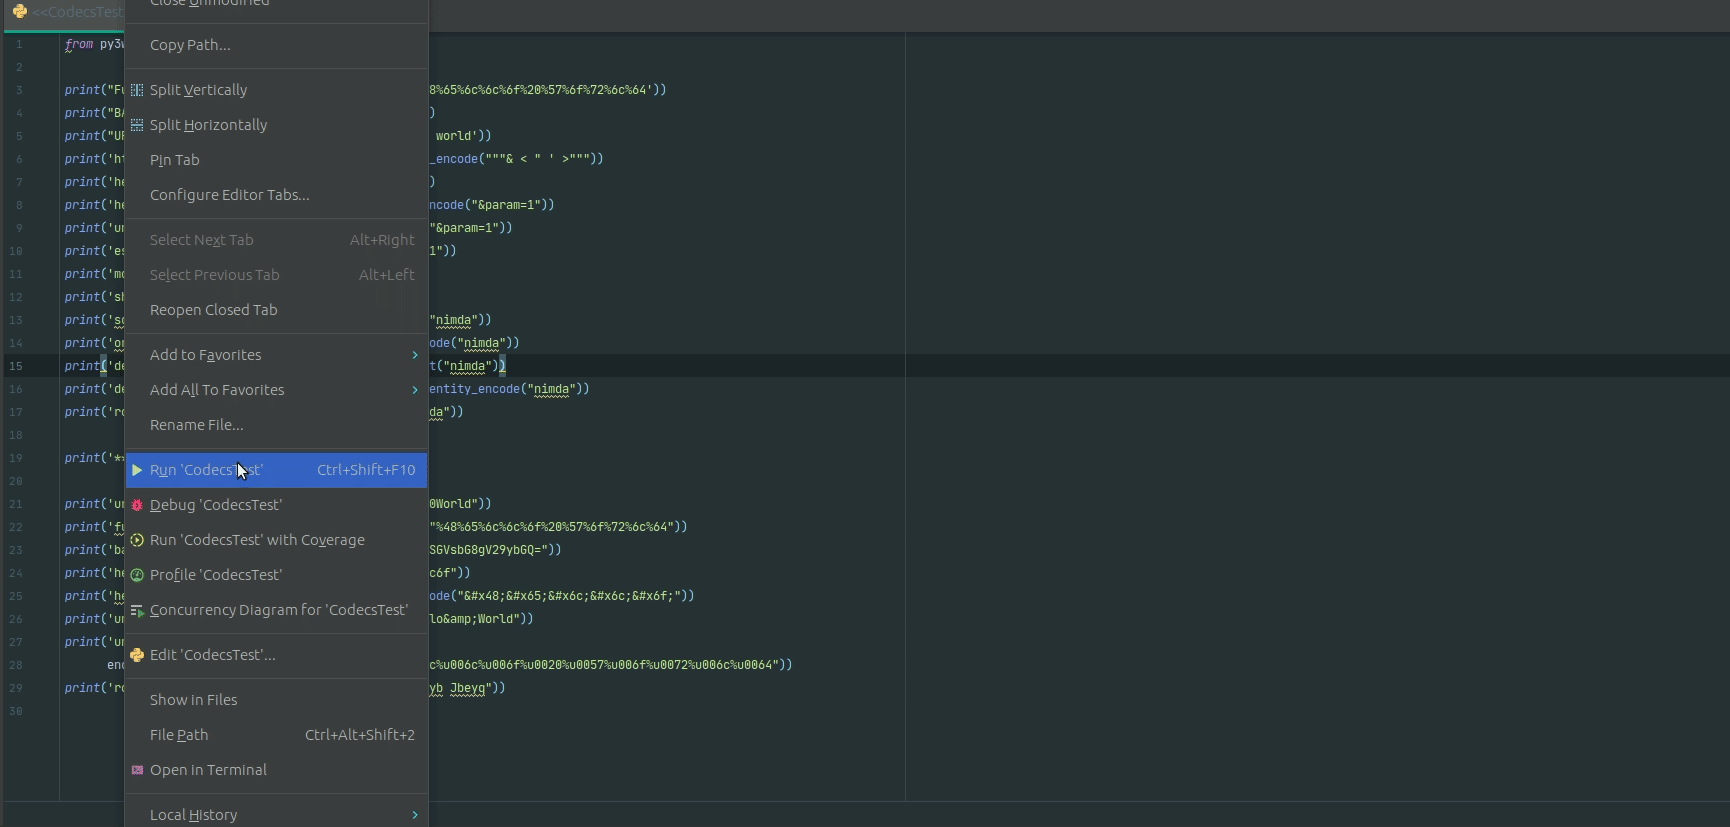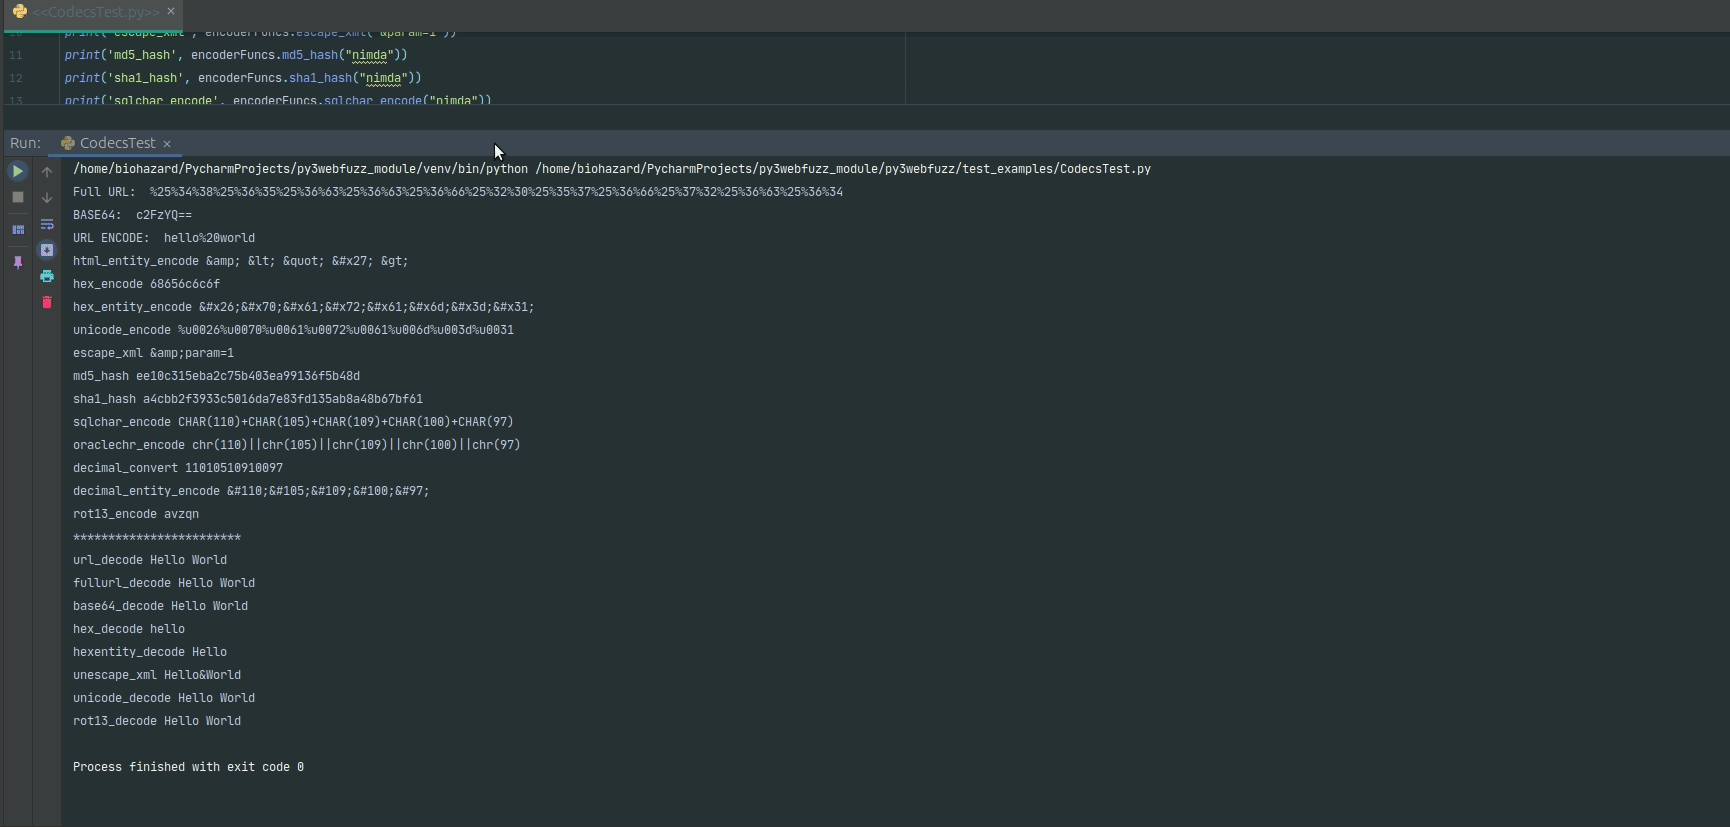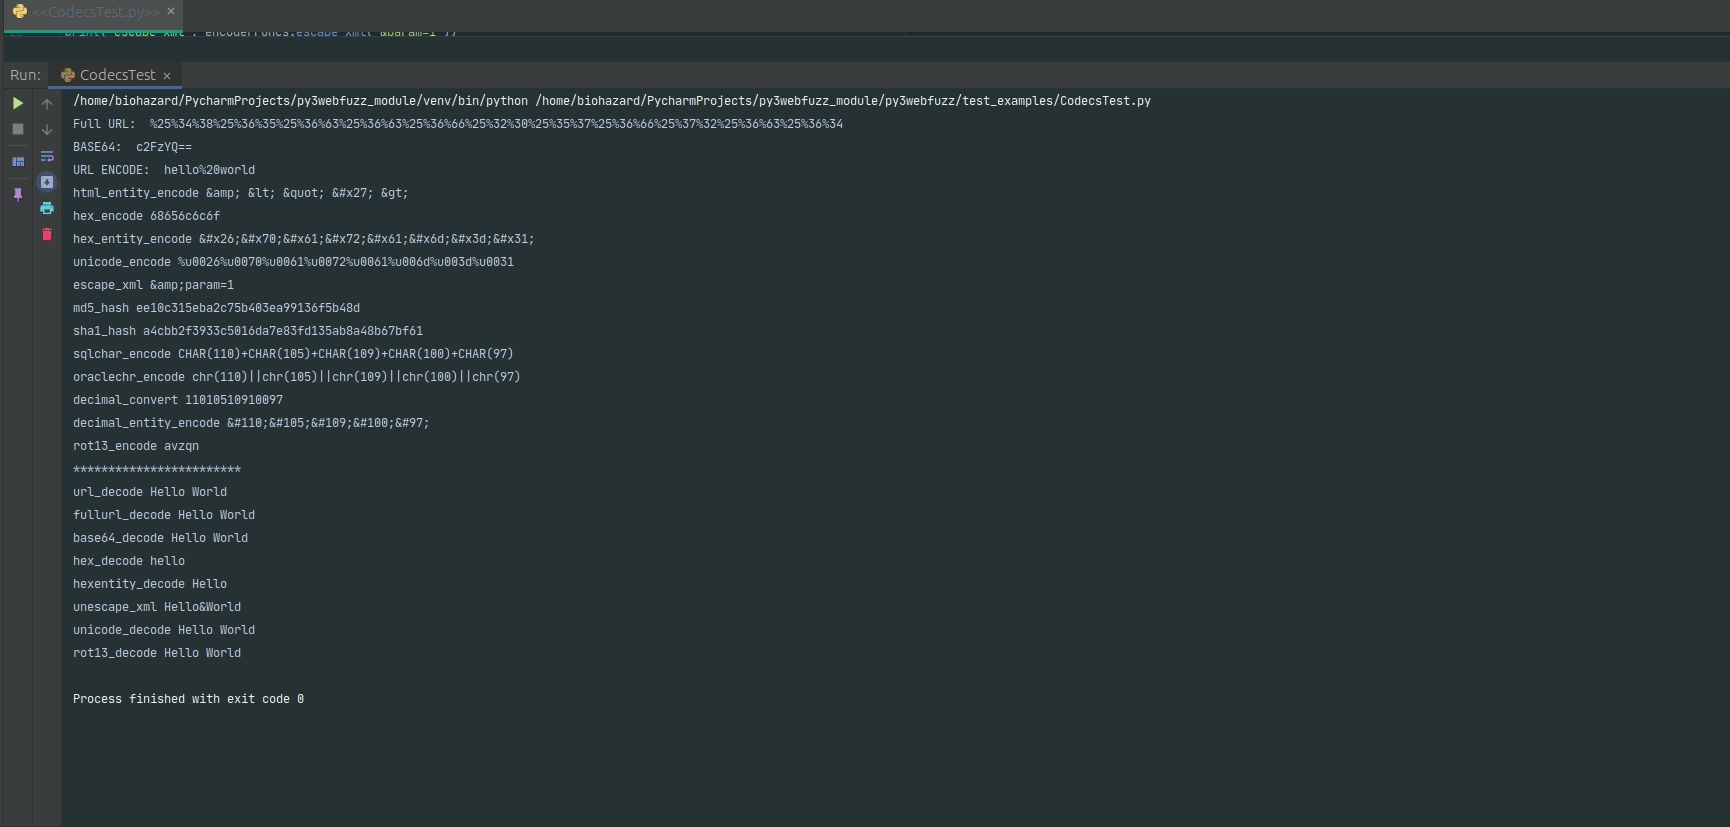 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 luisfontes19/xxexploiter
Tool to help exploit XXE vulnerabilities
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
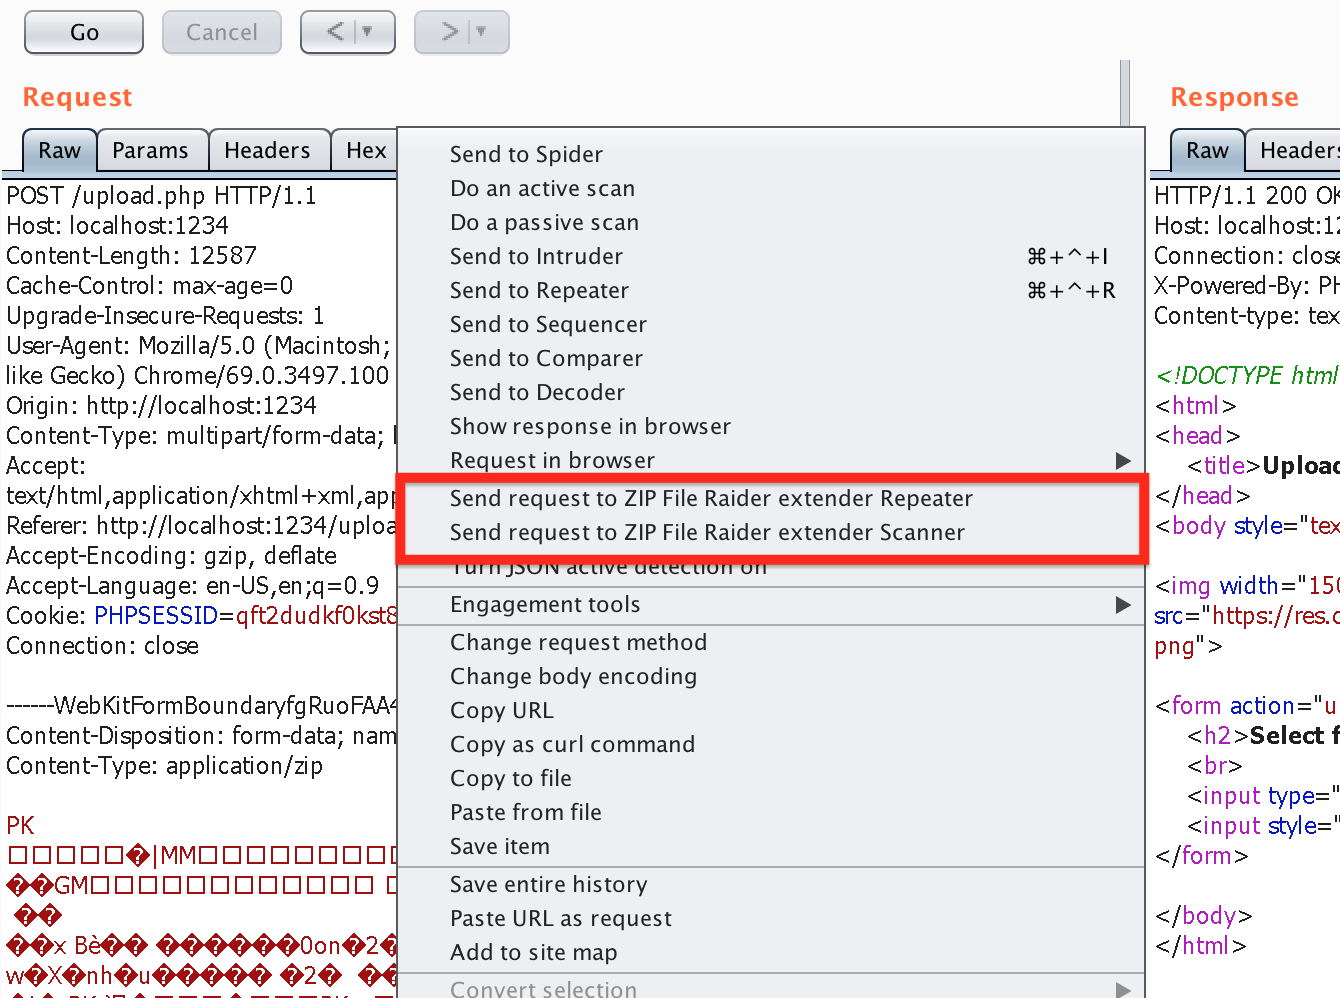 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 infiniteloopers/cve-2019-2107
Proof-of-concept exploit for CVE-2019-2107, demonstrating remote code execution via crafted HEVC video on Android media framework. Includes crash…
 brum3ns/firefly
High-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…
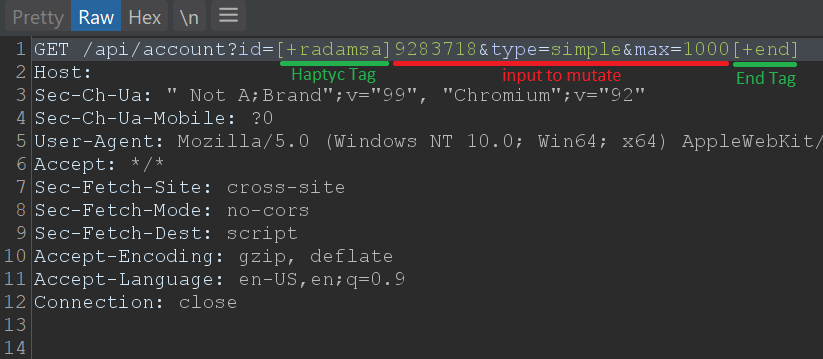 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…