
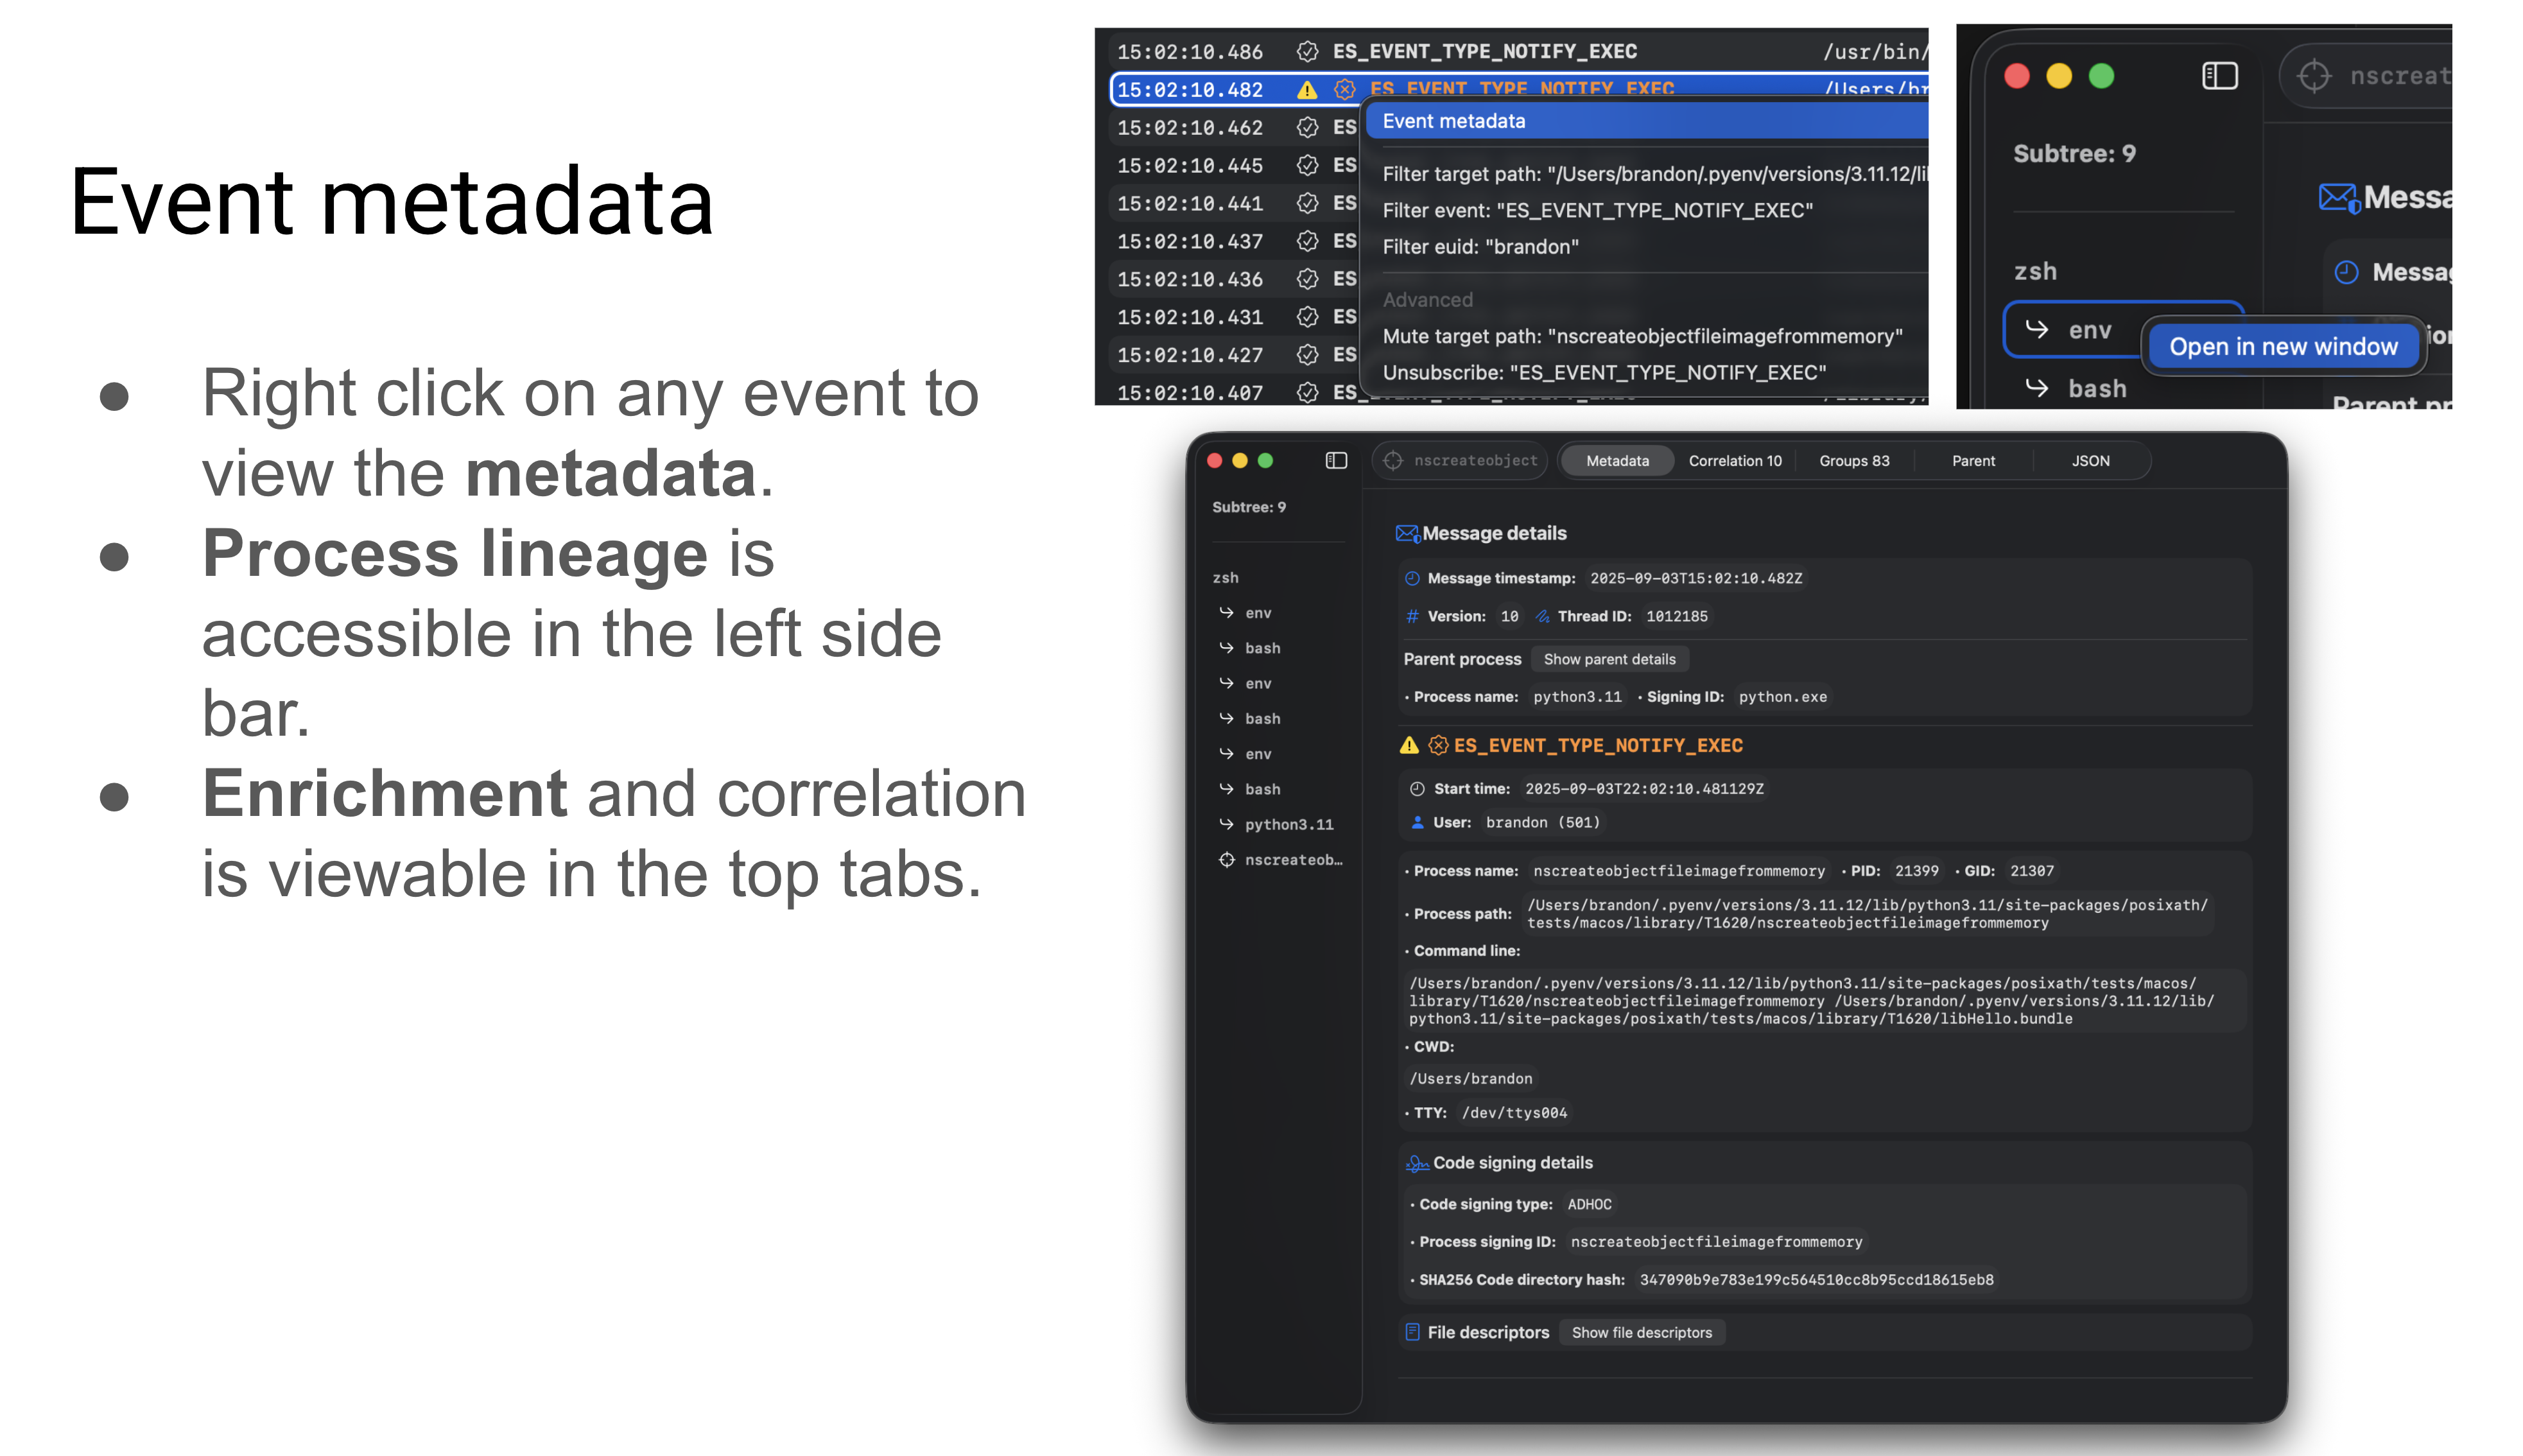
mac-monitor
 brandon7cc/mac-monitor
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
dynamic-analysis-sandboxingeducationforensics+2
1.4k
brandon7cc/mac-monitorAdvanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 eurecom-s3/linux_screenshot_xwindows
Volatility plugin to extract X screenshots from a memory dump
 andreafortuna/autotimeliner
Automagically extract forensic timeline from volatile memory dump
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 jordelmir/elysium-vanguard-sentinel-audit
The official Sentinel Edition v7.11 - Hypervisor Detection & Kernel Memory Audit Suite for Honor Magic V2. Investigating CVE-2025-38352 and EL2 RKP…
 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
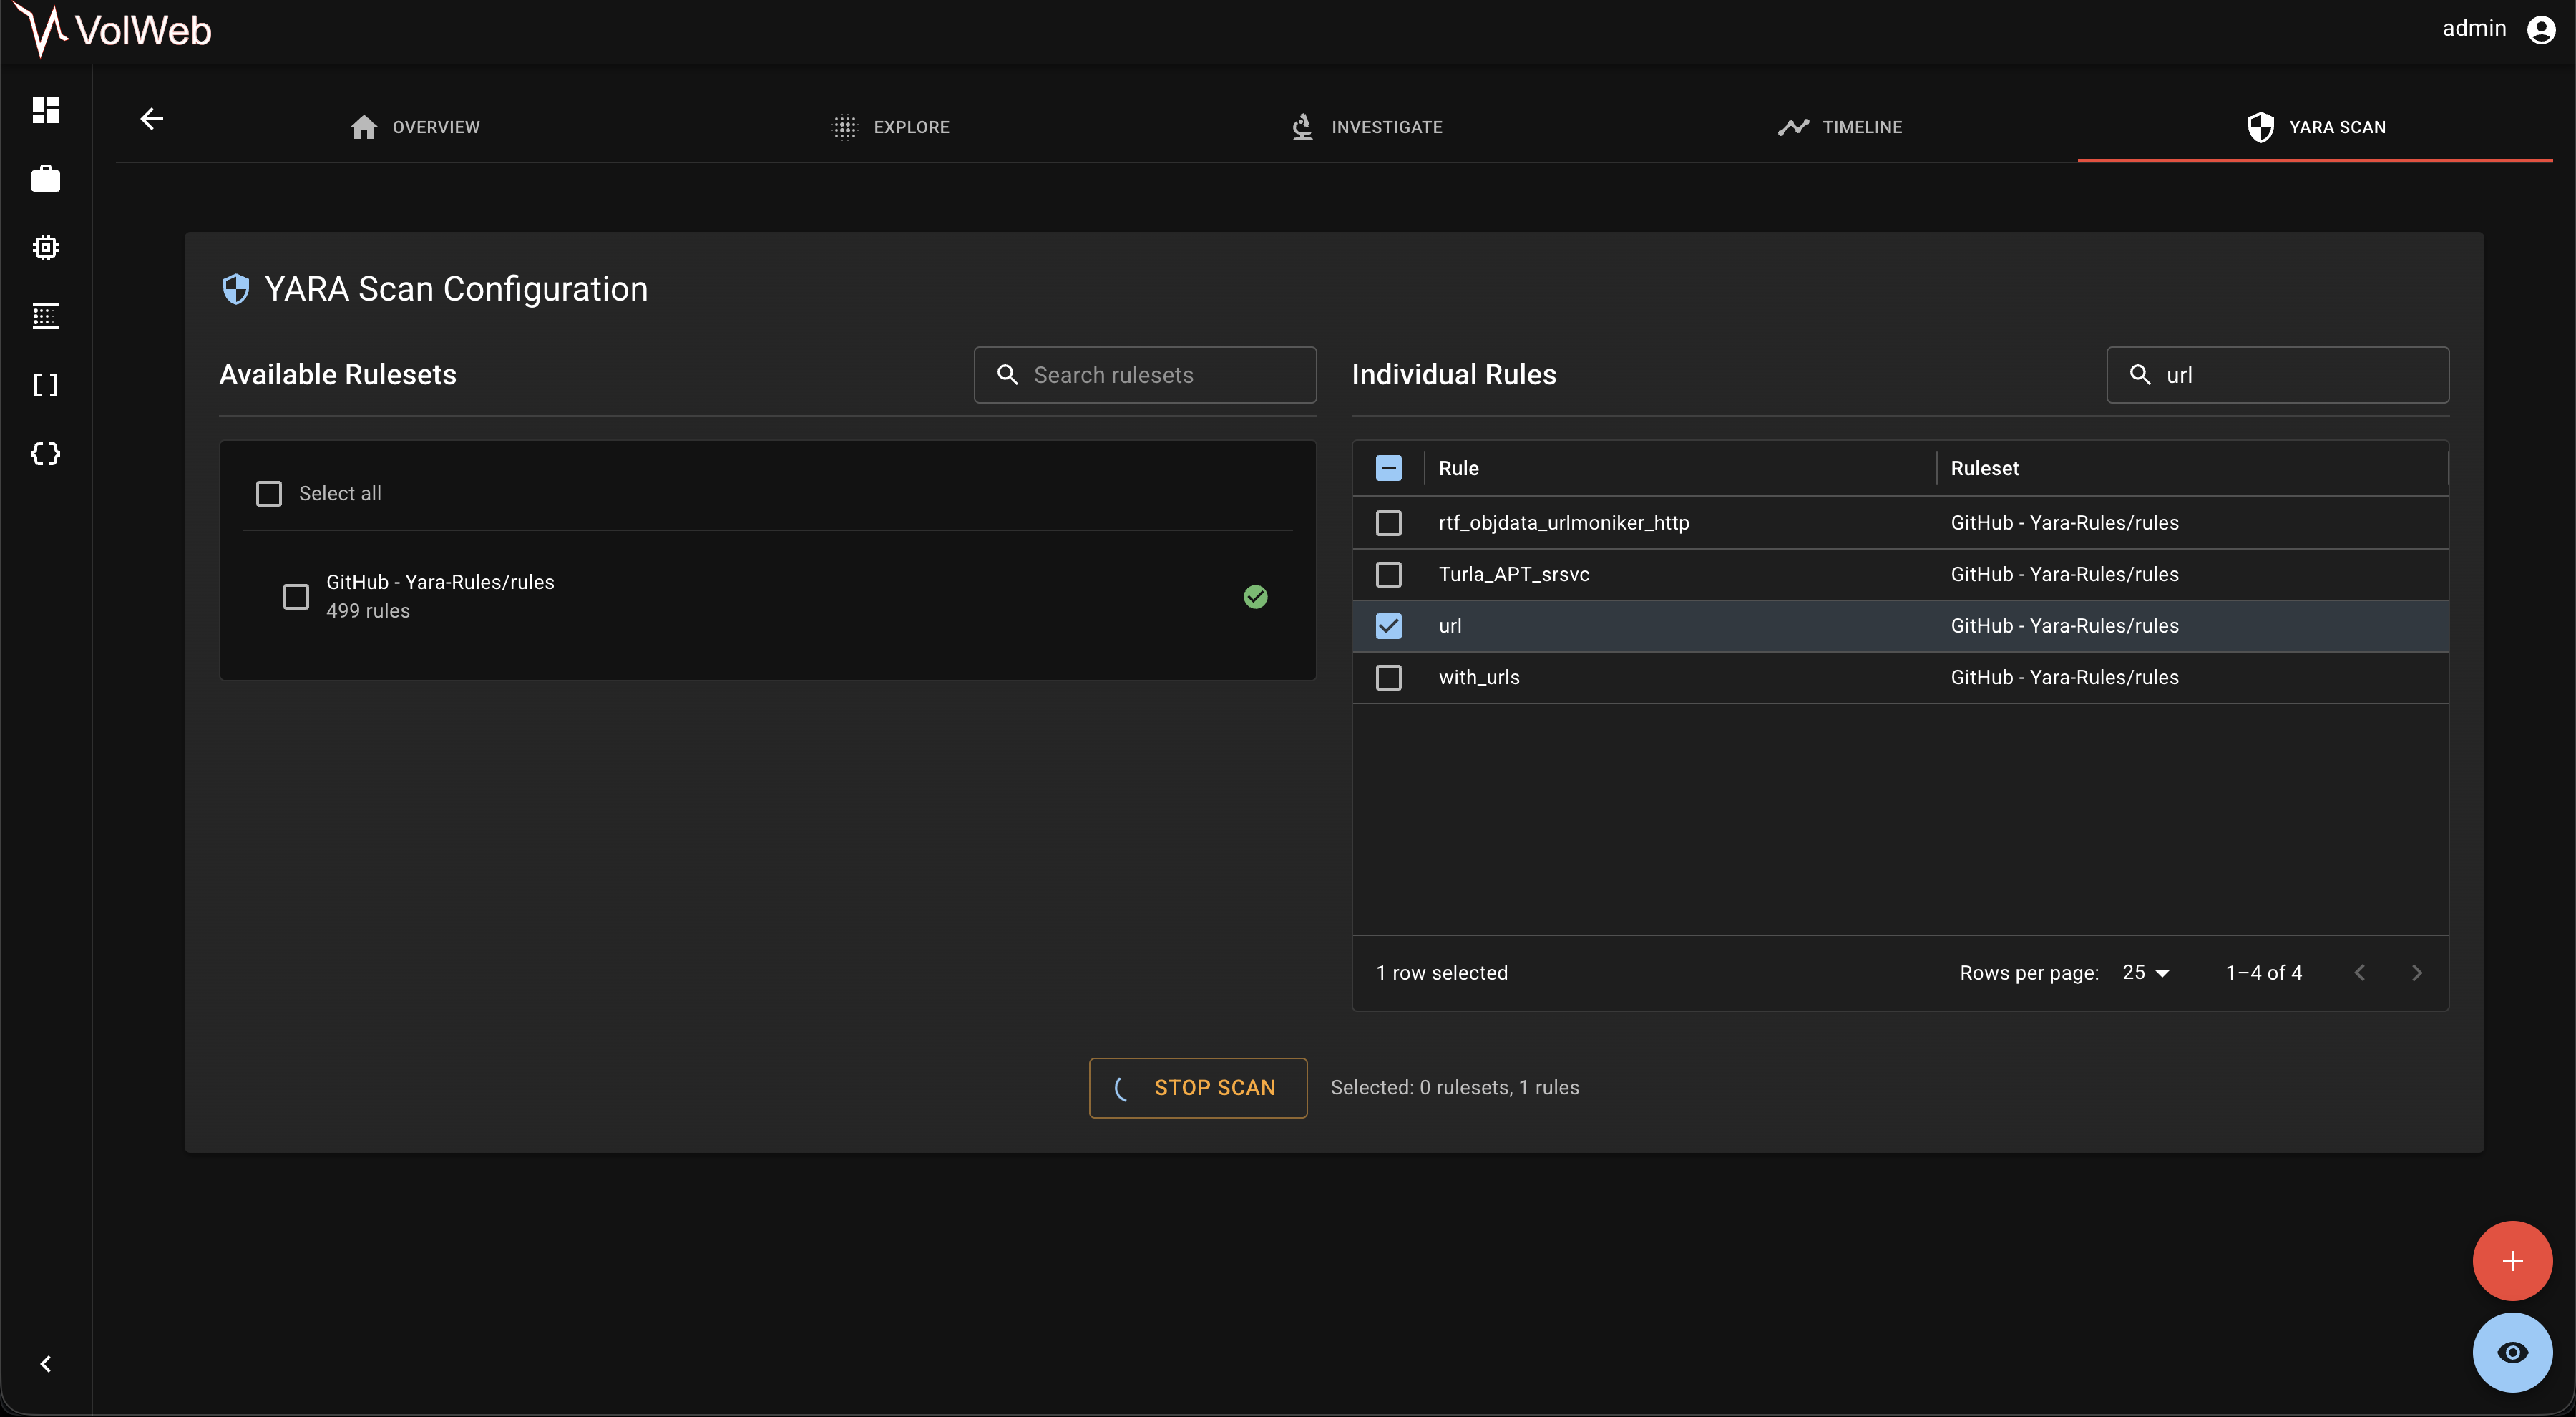 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 504ensicslabs/damm
Differential Analysis of Malware in Memory
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 bedazzlinghex/memory-analysis
Contains tools to perform malware and forensic analysis in Memory