

osquery
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
anomaly-detectiondefensive-toolsemail-security+8
osquery/osquerySQL powered operating system instrumentation, monitoring, and analytics.
 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…

 satheesh575555/external_tcpdump_aosp10_r33_cve-2019-15166
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting, analysis, and…
 trinadh465/external_tcpdump_cve-2018-14879
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 trinadh465/external_tcpdump_cve-2018-14469
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 lupovis/honeypot-for-cve-2025-59287-wsus
Defensive PoC decoy for CVE-2025-59287 (WSUS) - emulates WSUS endpoints, captures request bodies and metadata, saves evidence for forensic analysis,…
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
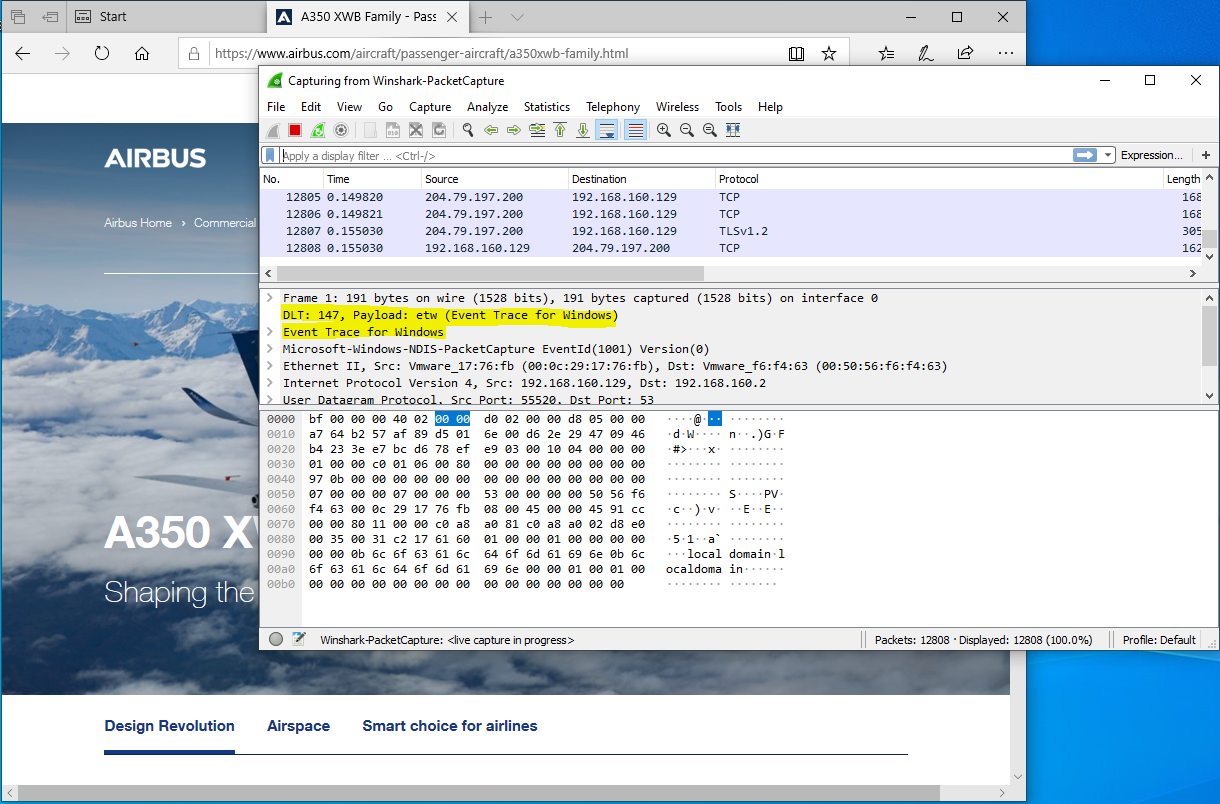 airbus-cert/winshark
A wireshark plugin to instrument ETW
 iyargross/smb-cve-2025-33073
Advanced SMB Honeypot: CVE-2025-33073 Research & Implementation
 mhils/honeyproxy
This project is now part of @mitmproxy.
 fox-it/cisco-ios-xe-implant-detection
Cisco IOS XE implant scanning & detection (CVE-2023-20198, CVE-2023-20273)
 malejdj/cve-2026-30784-rustdesk-poc
CVE-2026-30784: RustDesk hbbs Traffic Amplification PoC & PCAP Analysis
 redscan/cve-2019-19781
CVE-2019-19781 Attack Triage Script
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 bitranox/fingerprint
Monitoring Registry and File Changes in Windows
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.