HiddenNetworks-Python

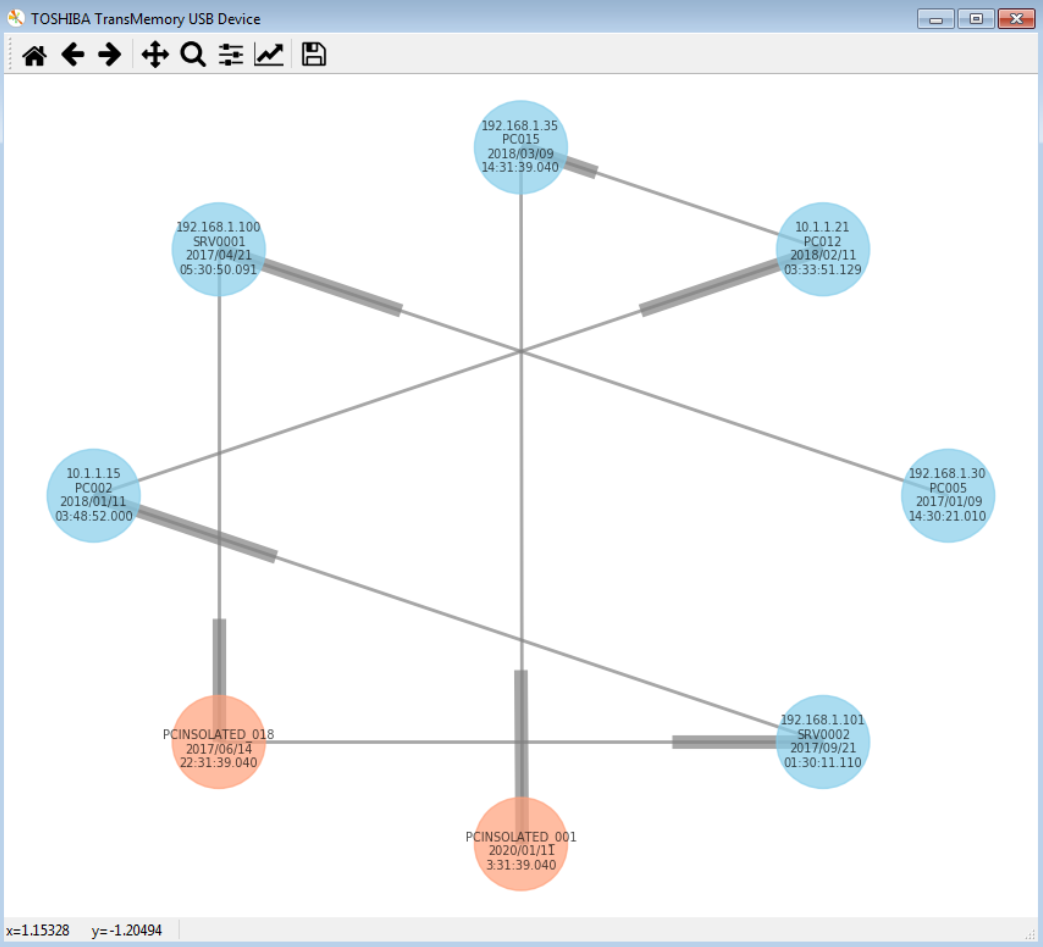
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…

USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…

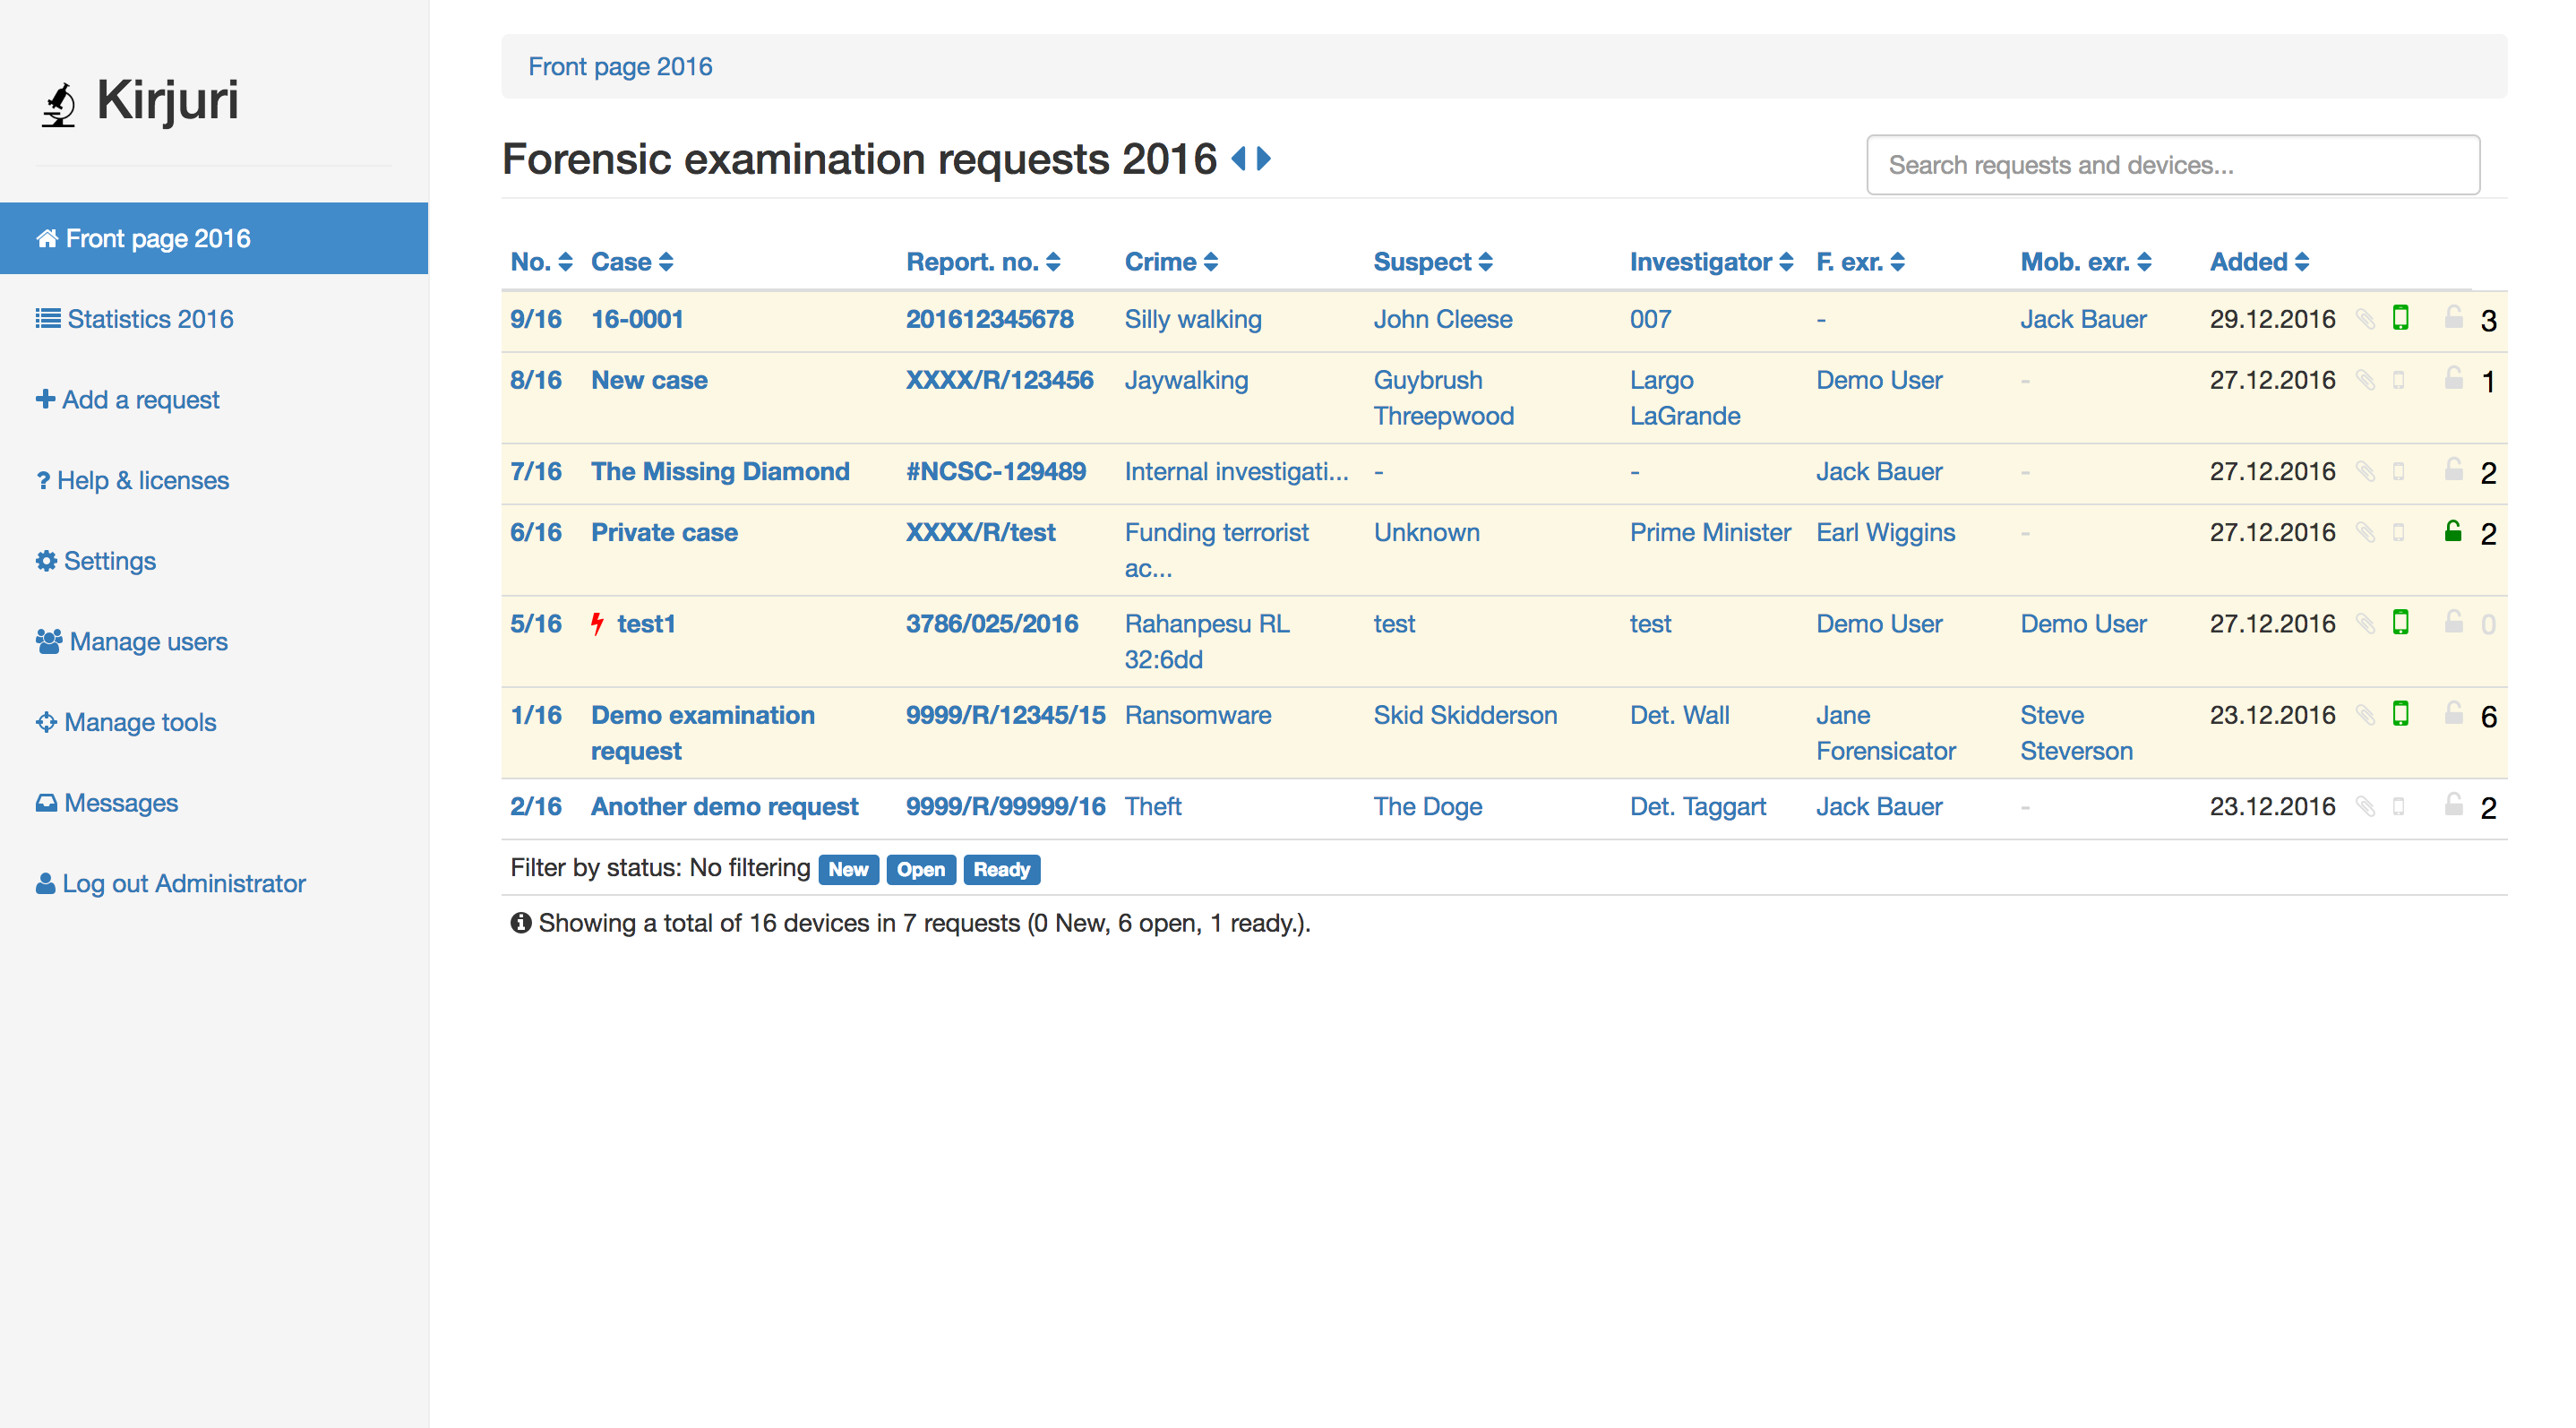
Kirjuri is a web application for managing cases and physical forensic evidence items.

Extract Windows credentials directly from VM memory snapshots and virtual disks

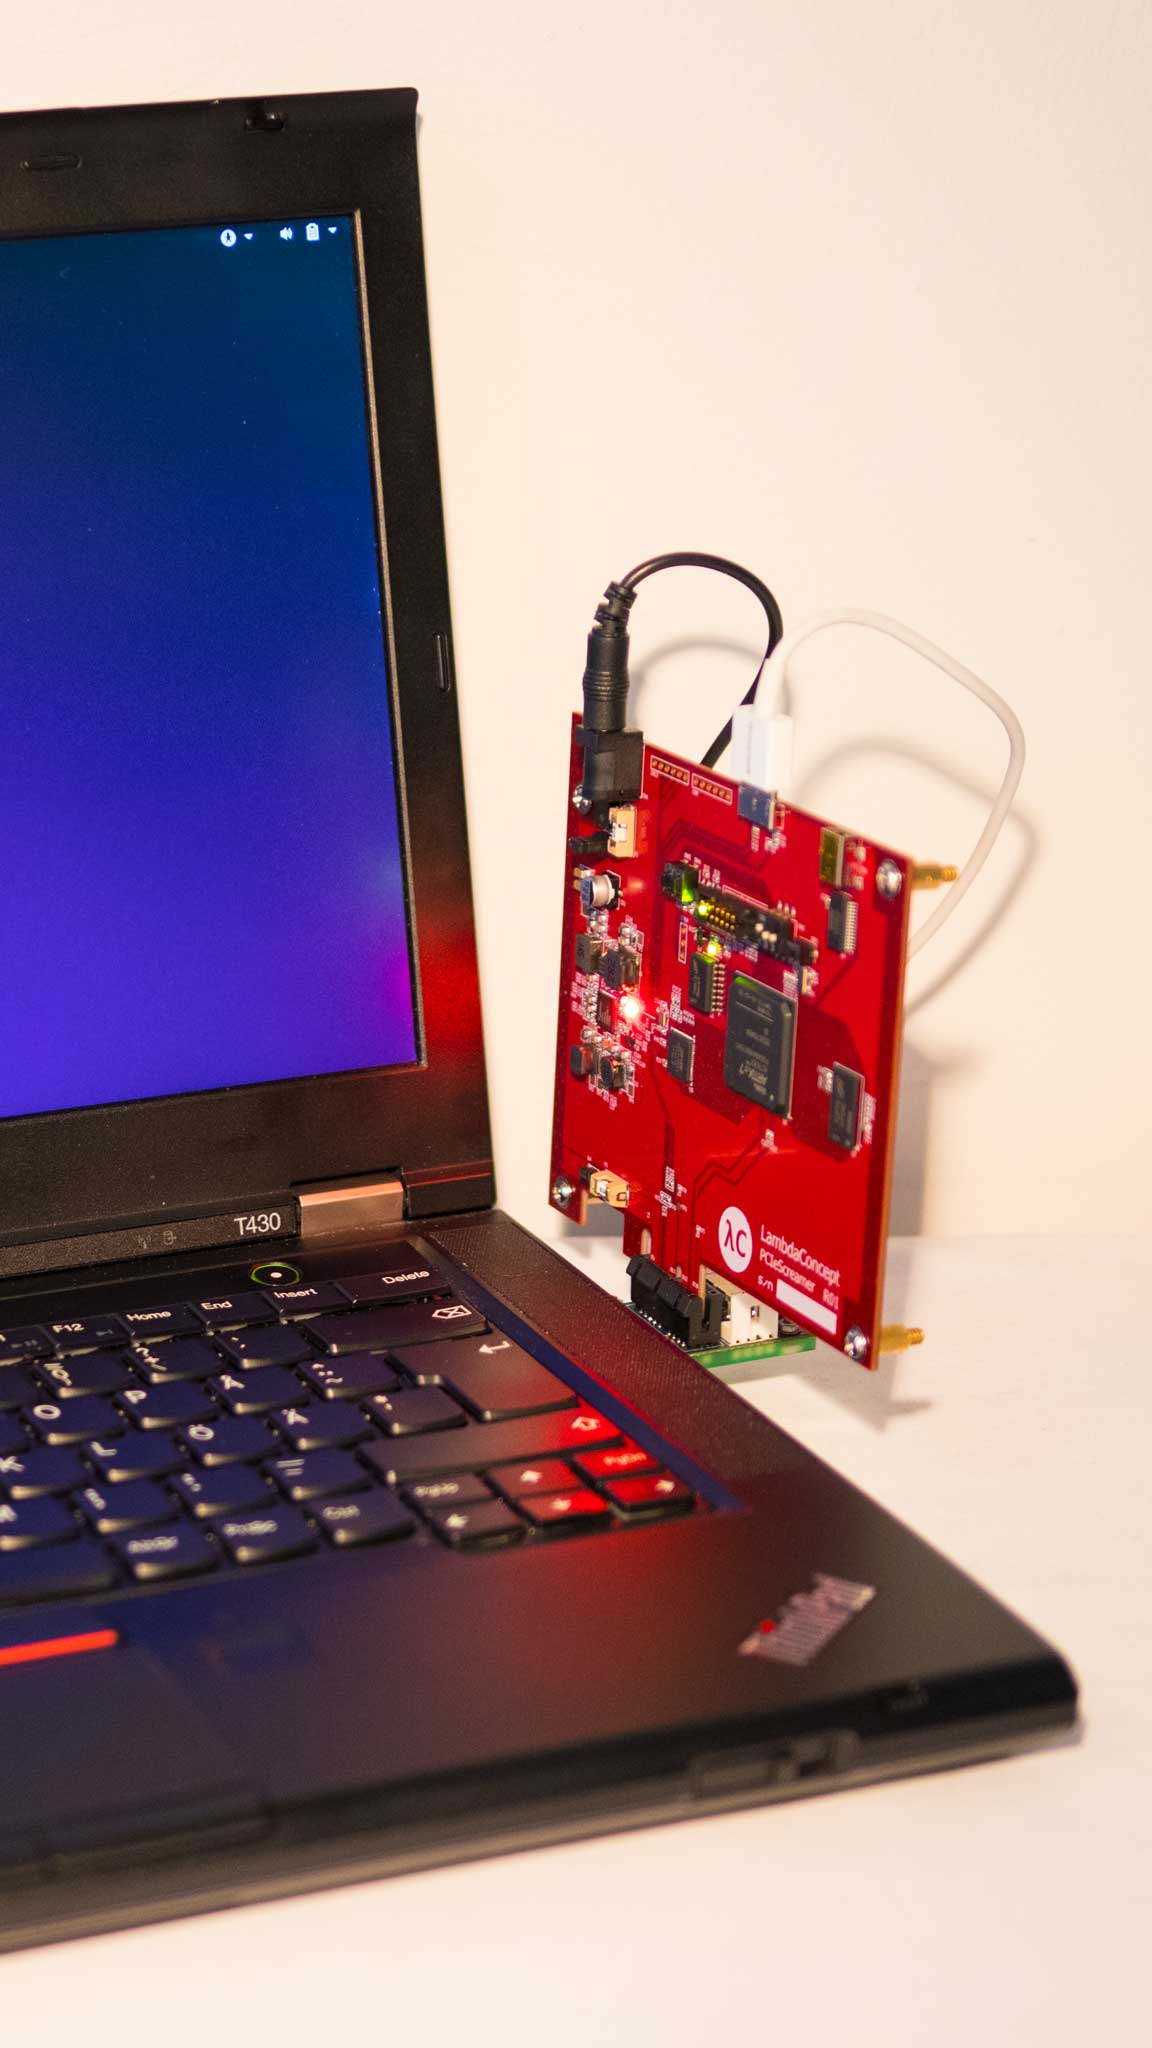
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.

Linux kernel driver for physical memory acquisition, enabling read access to any physical address including reserved memory and memory holes, with…

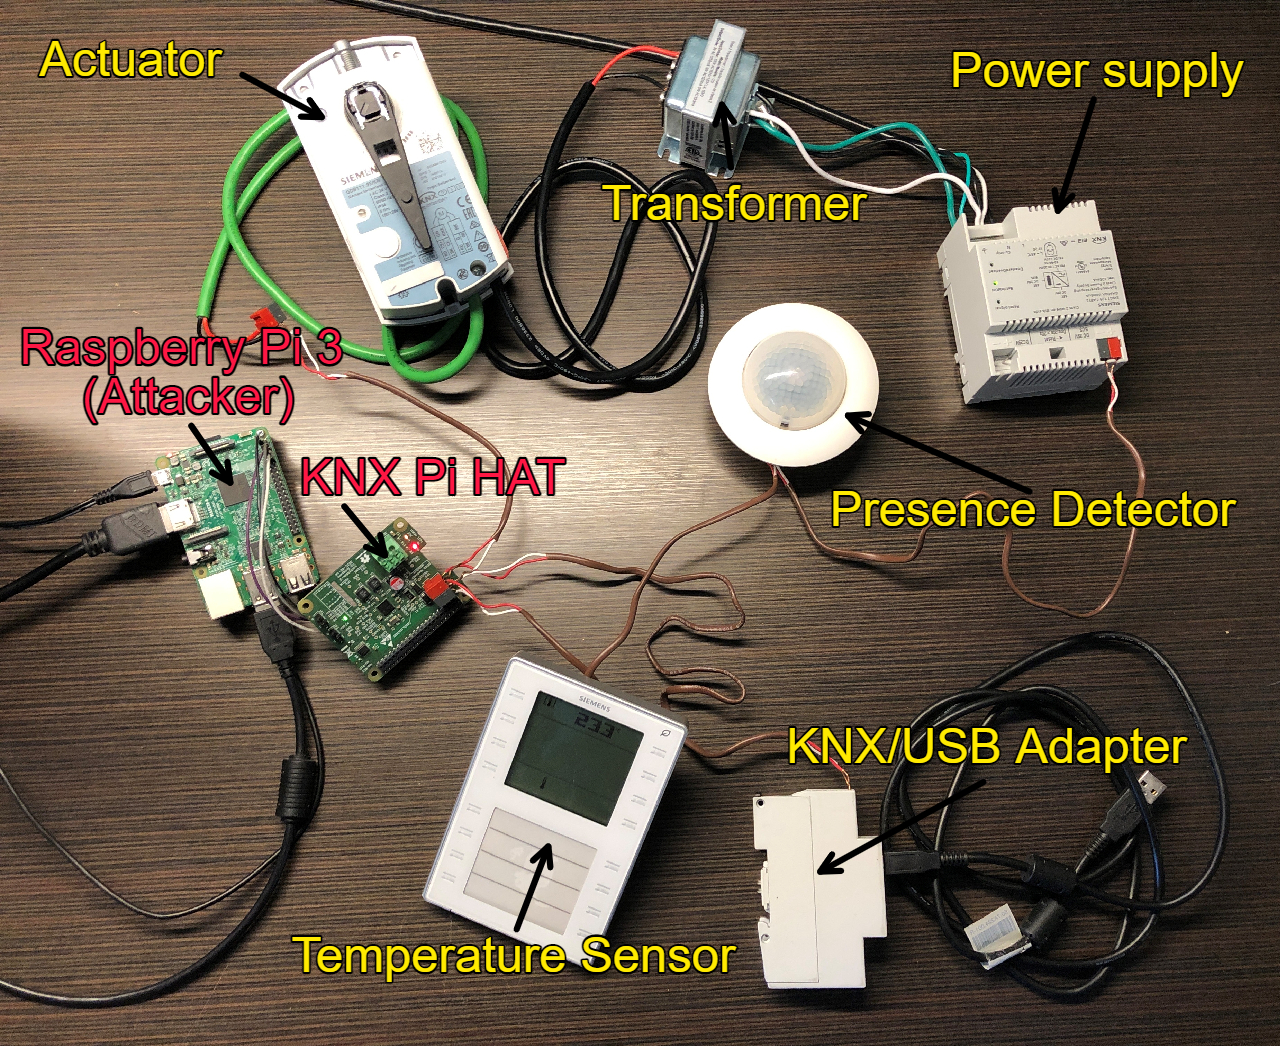
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…

Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality

Platform Security Assessment Framework