

Z-Jail
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
binary-analysiscontainer-securityctf+7
73
division-36/z-jailA lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
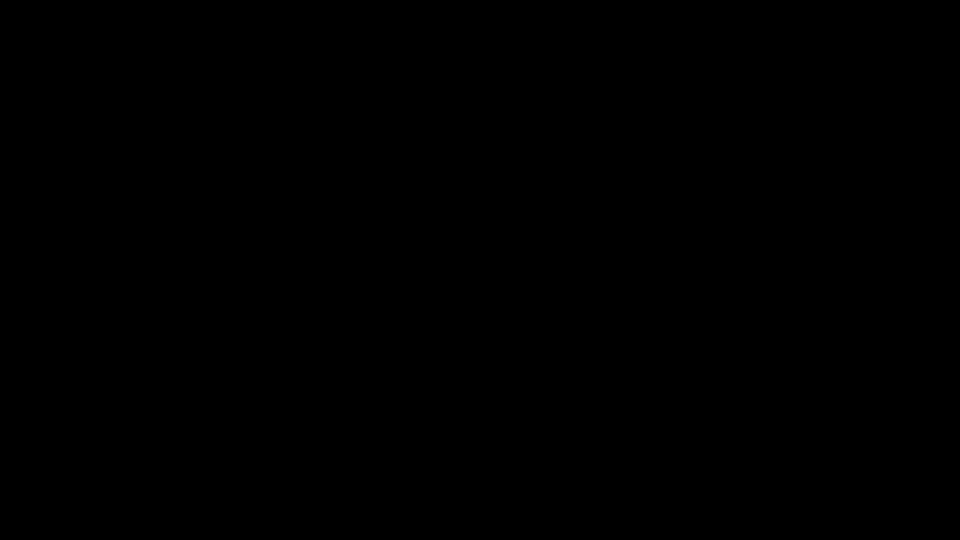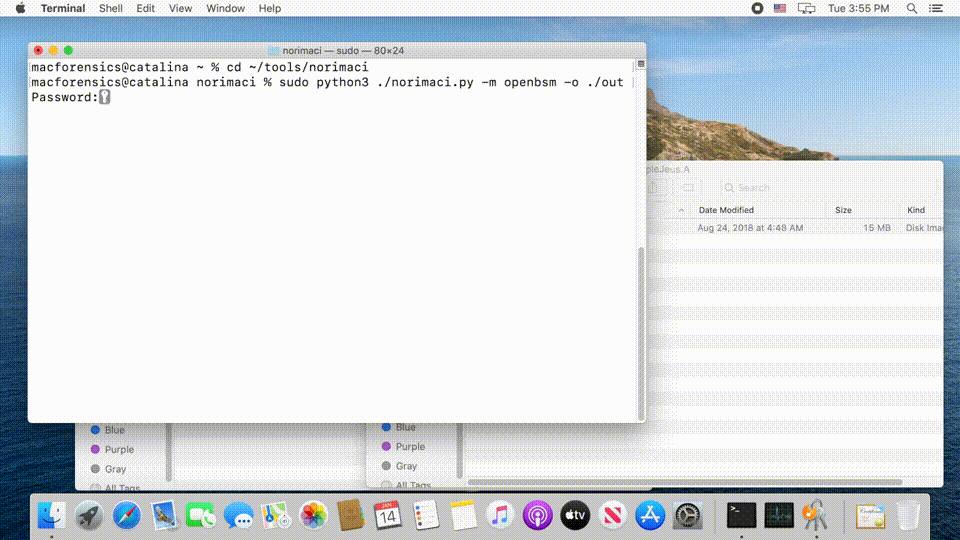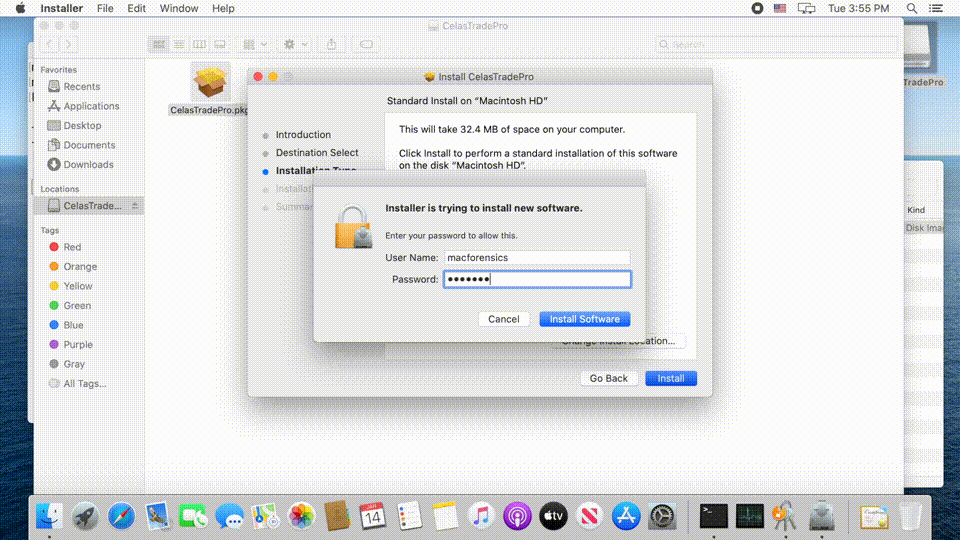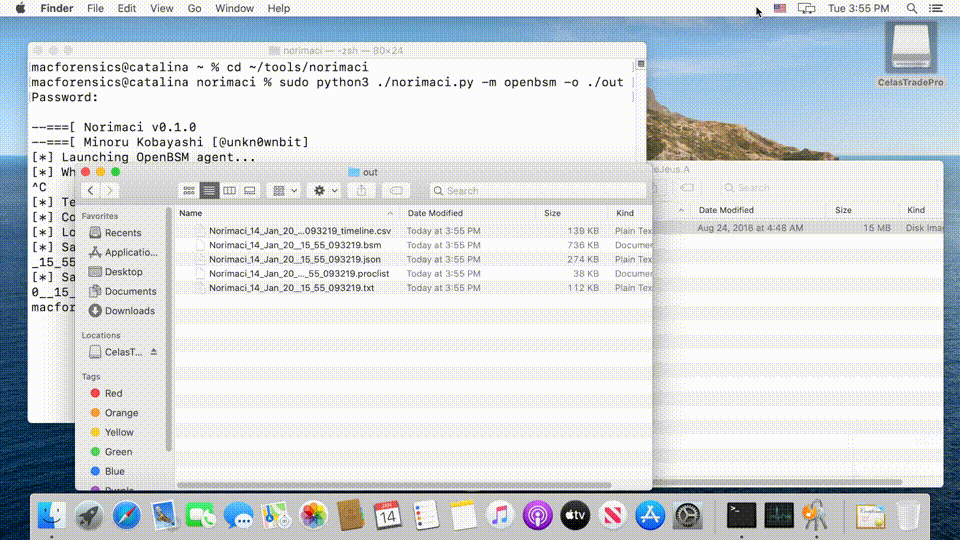 mnrkbys/norimaci
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…
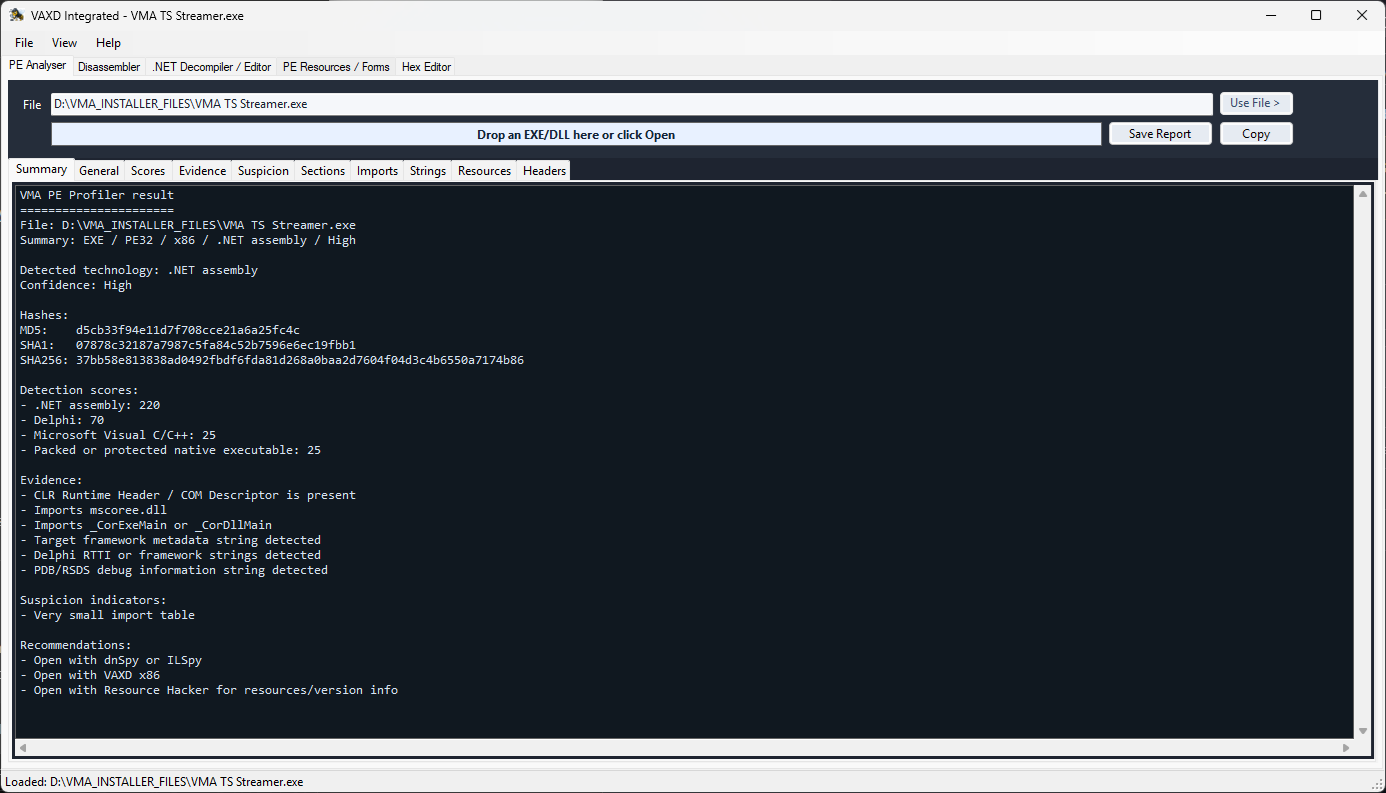 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 harshavmb/fim-ebpf
A lightweight eBPF program to monitor file creation and modification events on Linux. This tool leverages eBPF (Extended Berkeley Packet Filter) to…
 iqbaalilmii/acropalypse-reconstructor
A lightweight CLI tool to detect and reconstruct cropped images vulnerable to Acropalypse (CVE-2023-21036 and CVE-2023-28303) written in Python.
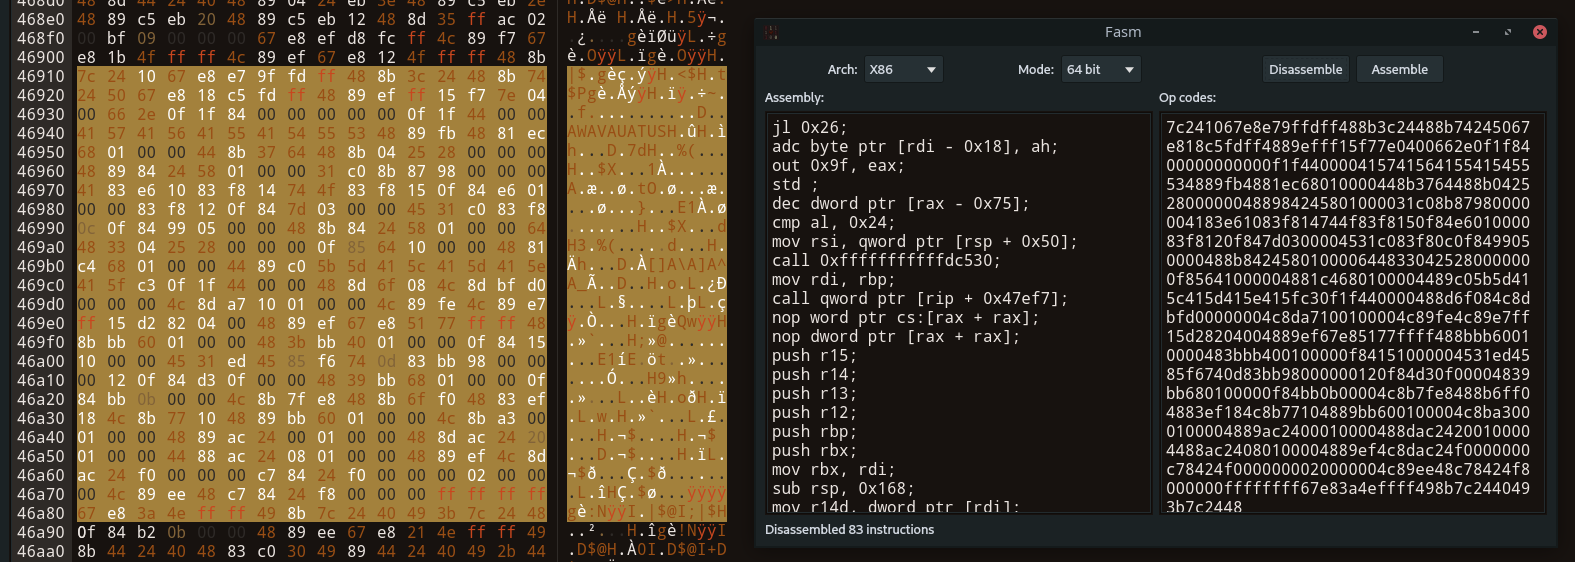 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
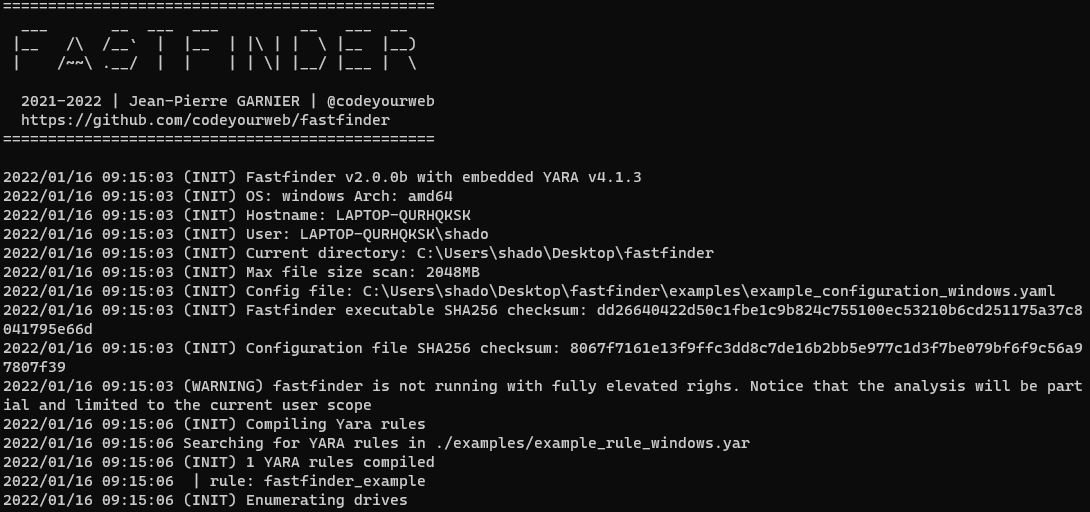 codeyourweb/fastfinder
Incident Response - Fast suspicious file finder
 mhils/honeyproxy
This project is now part of @mitmproxy.
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
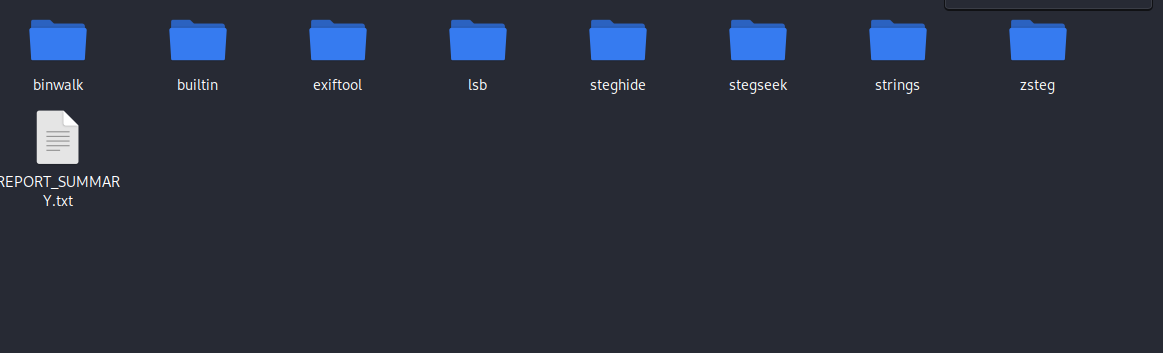 vatsal200600/stegolab
All-in-one Image Steganography Toolkit for CTFs & Forensics
 sucuri-labs/cve-2025-57819-ioc-check
This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819