
andriller
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
android-securitydata-recoverydigital-forensics+4
1.6k
den4uk/andriller📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
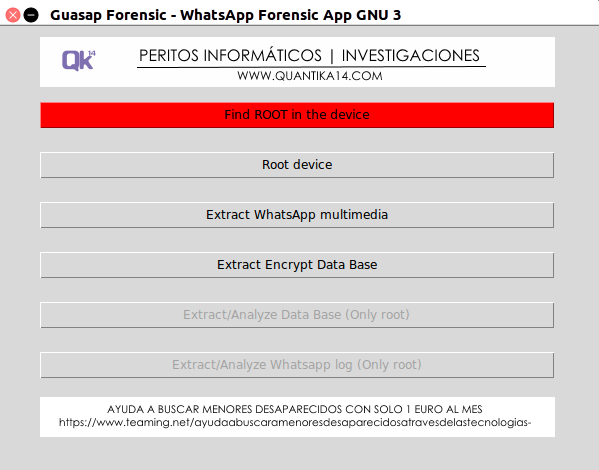 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 nowsecure/android-forensics
Open source Android Forensics app and framework
 thehackingsage/hackdroid
Curated catalog of 364 Android pentesting and security APKs organized by category, covering forensics, MITM, sniffing, OSINT, wireless, and privacy…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 canyie/transitionplayer
CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.