
chatlog
 sjzar/chatlog
chat log tool, easily use your own chat data. 聊天记录工具,轻松使用自己的聊天数据
database-securityforensicsinformation-gathering+1
sjzar/chatlogchat log tool, easily use your own chat data. 聊天记录工具,轻松使用自己的聊天数据
 cert-polska/mquery
YARA malware query accelerator (web frontend)
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 eyesecurity/wp2shell-compromise-scanner-plugin
Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 rishi-kaul/cve-2025-14847-mongobleed
Analysis and remediation guide for CVE-2025-14847 (MongoBleed), a MongoDB zlib compression memory disclosure. Includes detection indicators,…
 bi8d0/driversentinel
DriverSentinel is a security tool developed in Go that detects malicious and vulnerable drivers on Windows systems by comparing them against the…
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 ytisf/thezoo
Curated repository of live malware samples and source code for educational malware analysis and research, with an organized database and CLI tools…
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
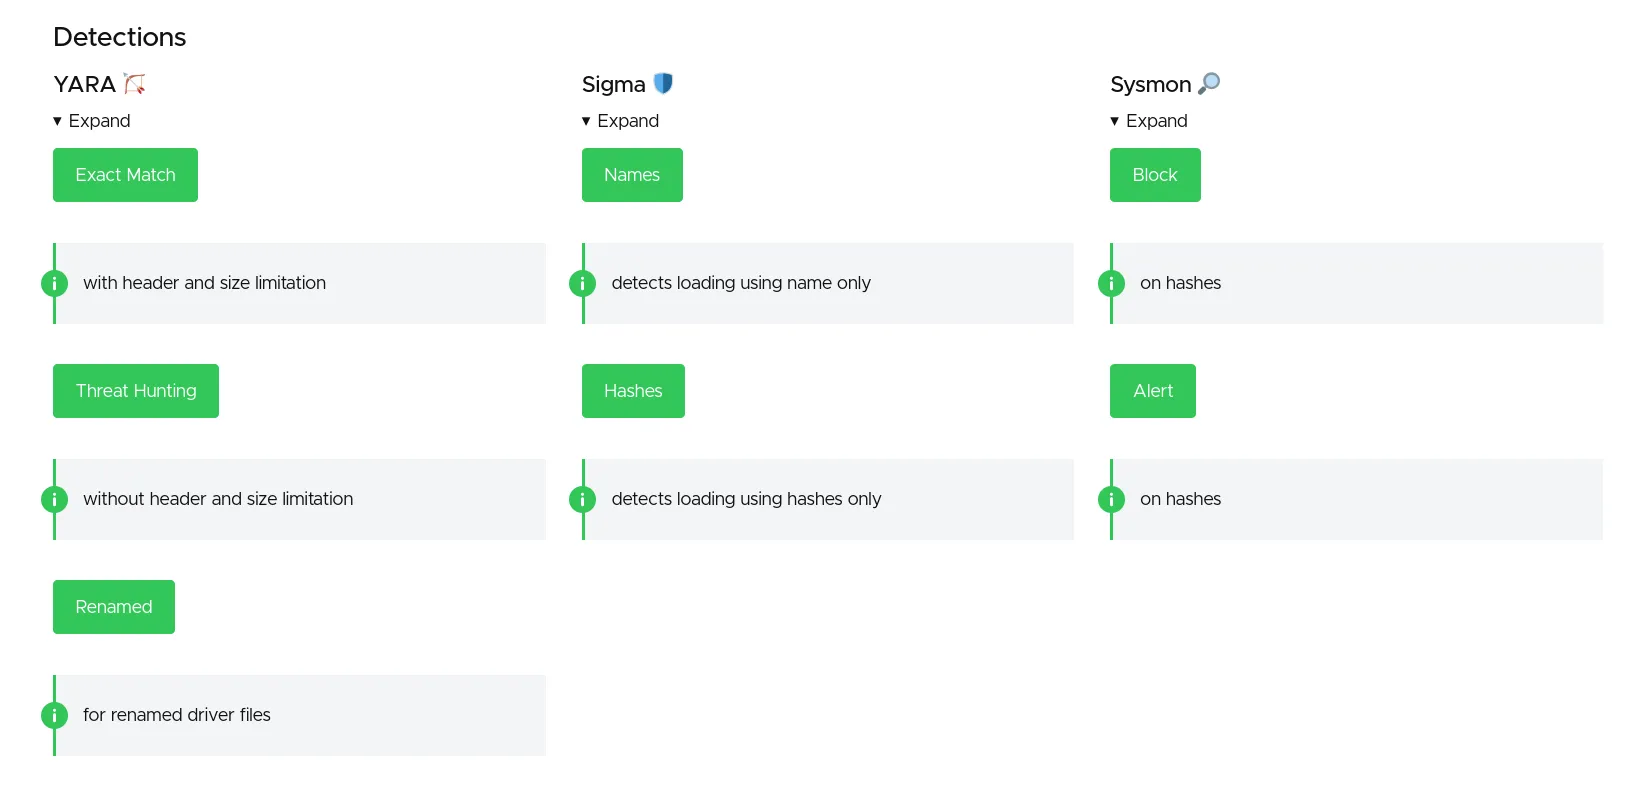 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 rainkin1993/remote-access-trojan-database
A database of RAT collected from Internet
 tjnel/certgraveyard_yara
Automated YARA rule generation from the Cert Central compromised certificate database.
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.