Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
53 results
litespeed-cpanel-cve-2026-54420-fix preview

litespeed-cpanel-cve-2026-54420-fix

GitHubresellnom/litespeed-cpanel-cve-2026-54420-fix

Defensive mitigation and auditing toolkit for CVE-2026-54420 in LiteSpeed cPanel plugin, providing symlink detection, IOC hunting, and remediation…

cloud-securityconfiguration-auditingdefensive-tools+6
4 months ago
cyberbro preview

cyberbro

GitHubstanfrbd/cyberbro

A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.

defensive-toolsdns-analysiseducation+9
6989 days ago
Android-Disassembler preview

Android-Disassembler

GitHubyhs0602/android-disassembler

Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…

android-securitybinary-analysisdebuggers+4
7197 months ago
dfirtrack preview

dfirtrack

GitHubdfirtrack/dfirtrack

System-based incident response tracking application for managing large-scale DFIR cases, with import/export, task workflows, and artifact tracking…

digital-forensicsforensicsincident-response
5409 months ago
OpenPetya preview

OpenPetya

GitHubiss4cf0ng/openpetya

A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++

binary-exploitationcryptographyeducation+4
2841 month ago
LiMEaide preview

LiMEaide

GitHubkd8bny/limeaide

A python application designed to remotely dump RAM of a Linux client and create a volatility profile for later analysis on your local host.

digital-forensicsforensicsmemory-forensics
1577 years ago
noia preview

noia

GitHub0x742/noia

Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…

android-securitydynamic-analysis-sandboxingforensics+3
1295 years ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

android-securitycryptographydynamic-analysis-sandboxing+8
104 days ago
NeuroCore preview

NeuroCore

GitHubfarukalpay/neurocore

NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…

binary-analysisdigital-forensicsforensics+3
289 months ago
damn-vulnerable-log4j-app preview

damn-vulnerable-log4j-app

GitHubsnapattack/damn-vulnerable-log4j-app

Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack

digital-forensicseducationexploitation+3
54 years ago
cve_2023_38831_scanner preview

cve_2023_38831_scanner

GitHubyezzfusl/cve_2023_38831_scanner

This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.

dynamic-analysis-sandboxingeducationexploitation+5
11 year ago
kirjuri preview
Archived

kirjuri

GitHubanttikurittu/kirjuri

Kirjuri is a web application for managing cases and physical forensic evidence items.

digital-forensicsforensicsincident-response
1095 months ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

encryption-decryption-toolsforensicshash-analysis+8
11.1k1 year ago
FACT_core preview

FACT_core

GitHubfkie-cad/fact_core

Firmware Analysis and Comparison Tool

binary-analysisdynamic-analysis-sandboxingembedded-systems-security+9
1.5k15h 27m ago
hollows_hunter preview

hollows_hunter

GitHubhasherezade/hollows_hunter

Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…

defensive-toolsforensicsincident-response+2
2.4k4 months ago
USBvalve preview

USBvalve

GitHubcecio/usbvalve

Expose USB activity on the fly

dynamic-analysis-sandboxingembedded-systems-securityforensics+2
1.3k2 months ago
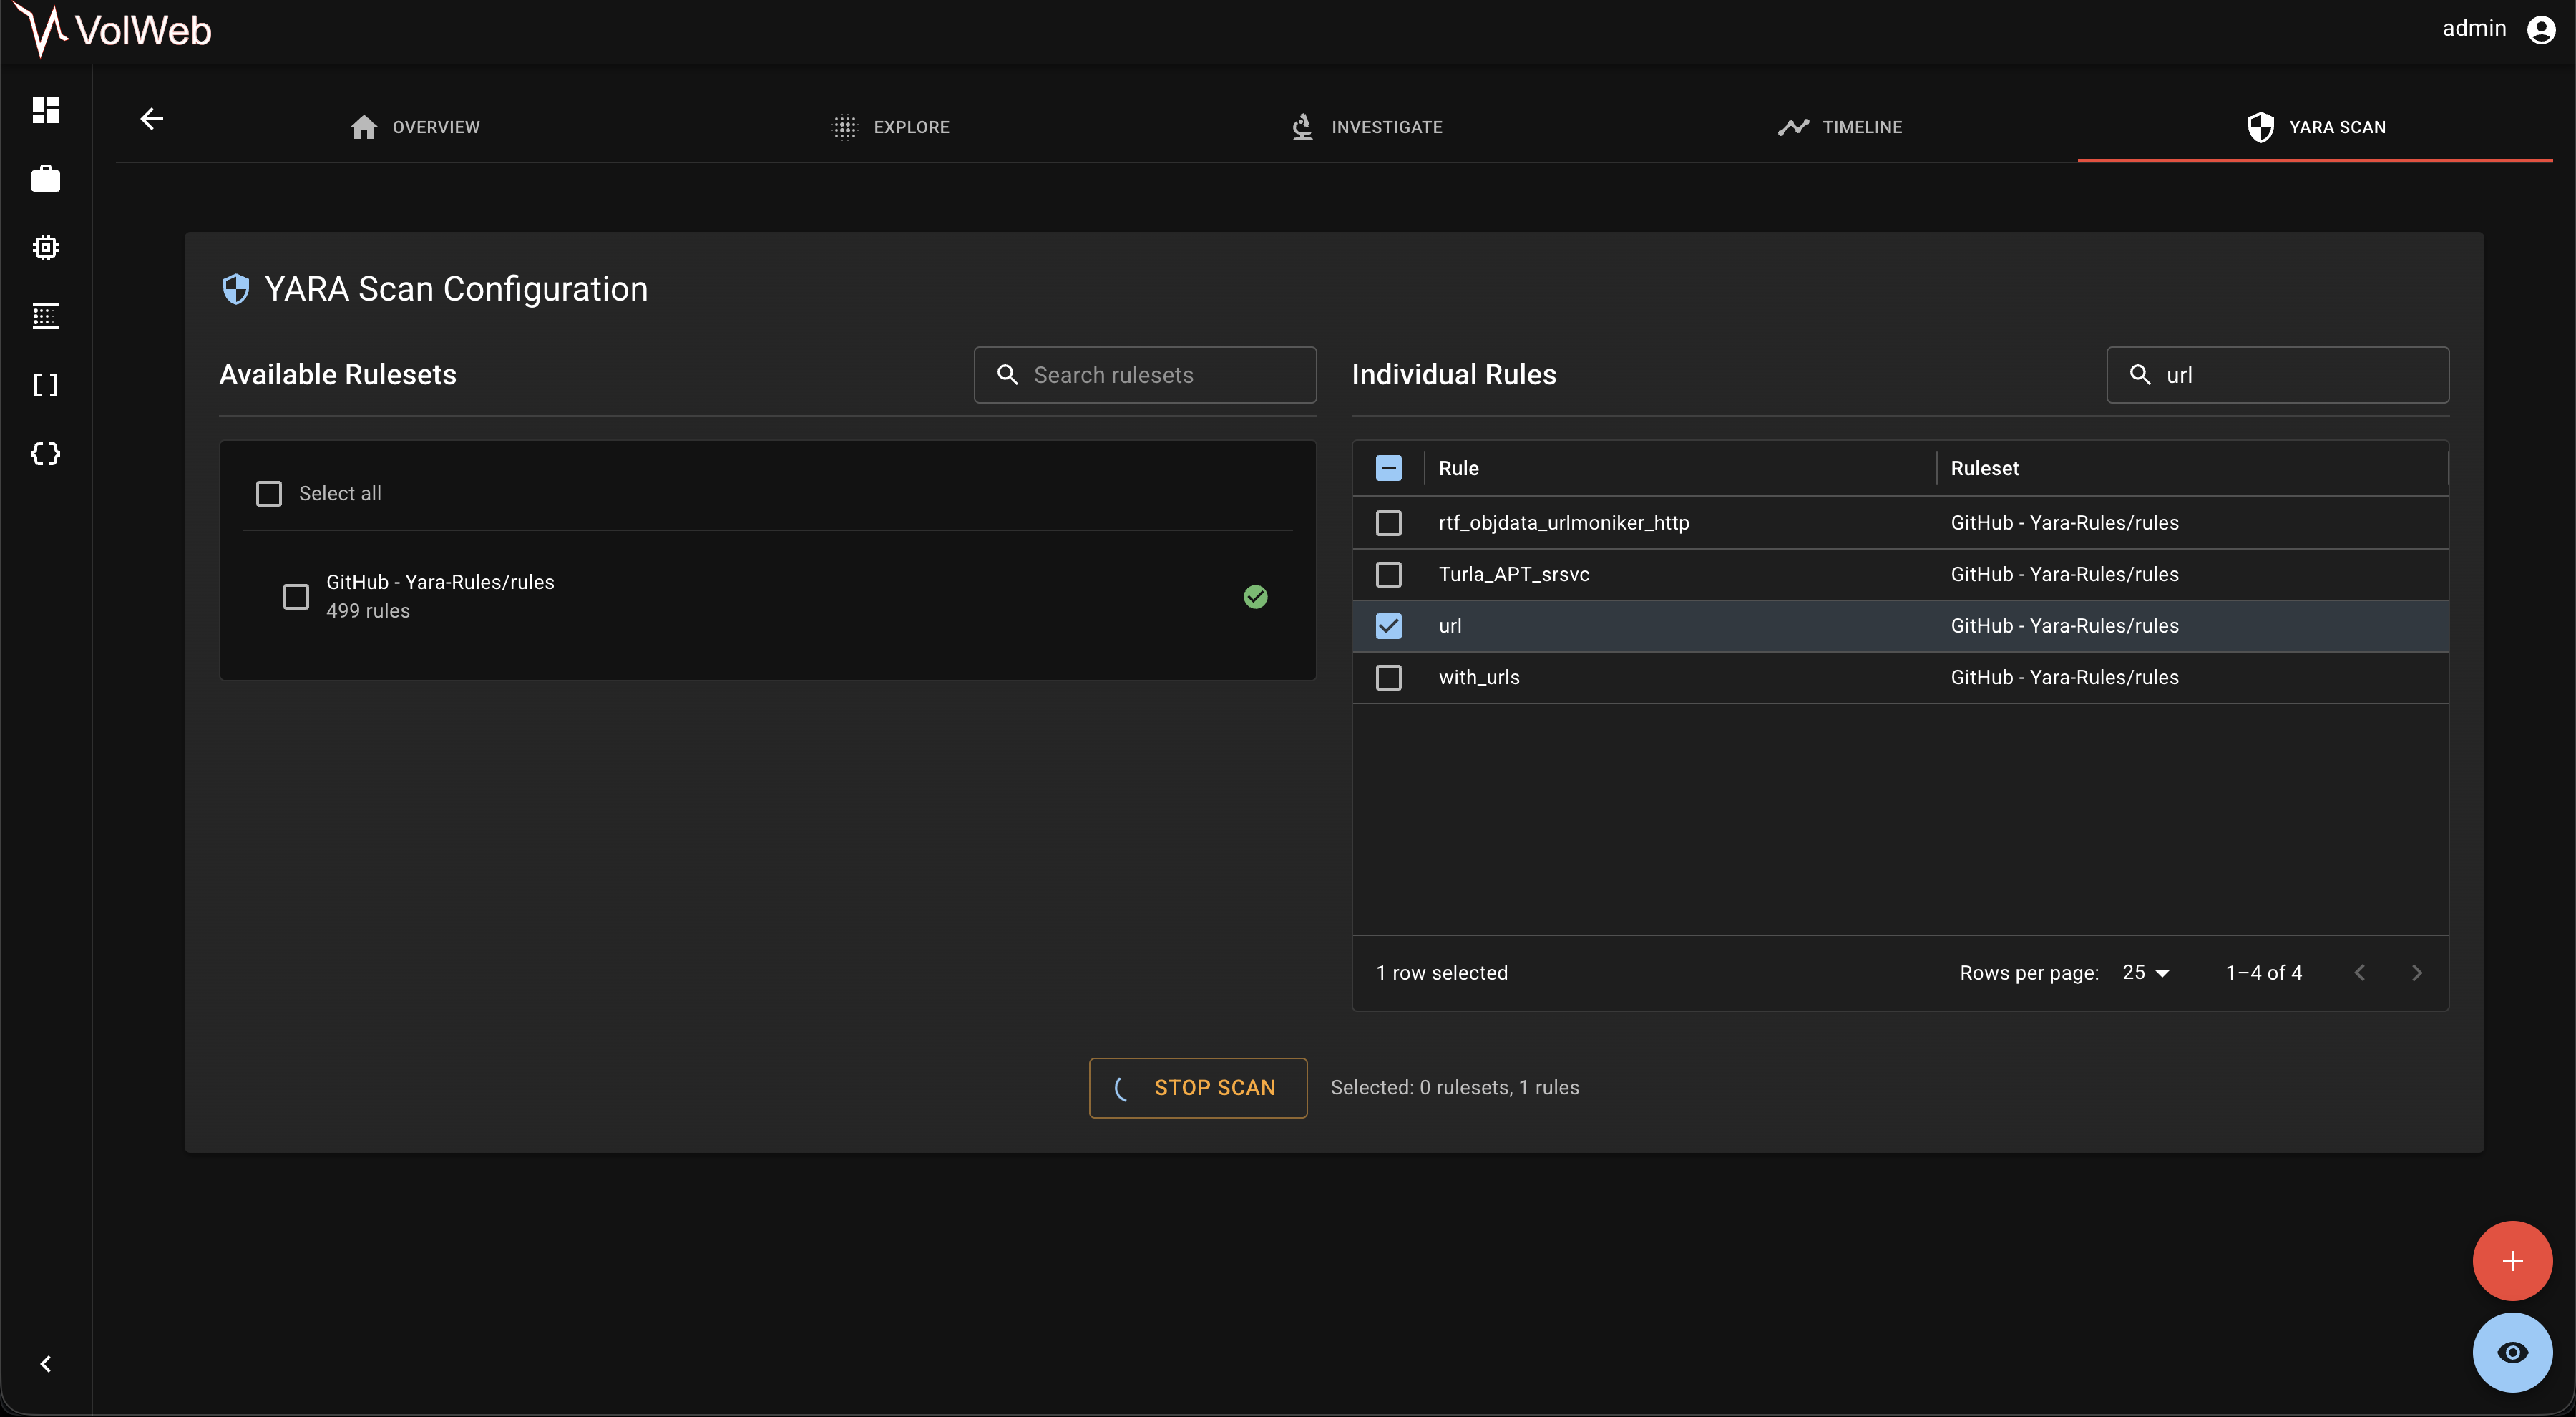
VolWeb preview

VolWeb

GitHubk1nd0ne/volweb

A centralized and enhanced memory analysis platform

digital-forensicseducationforensics+5
54028 days ago
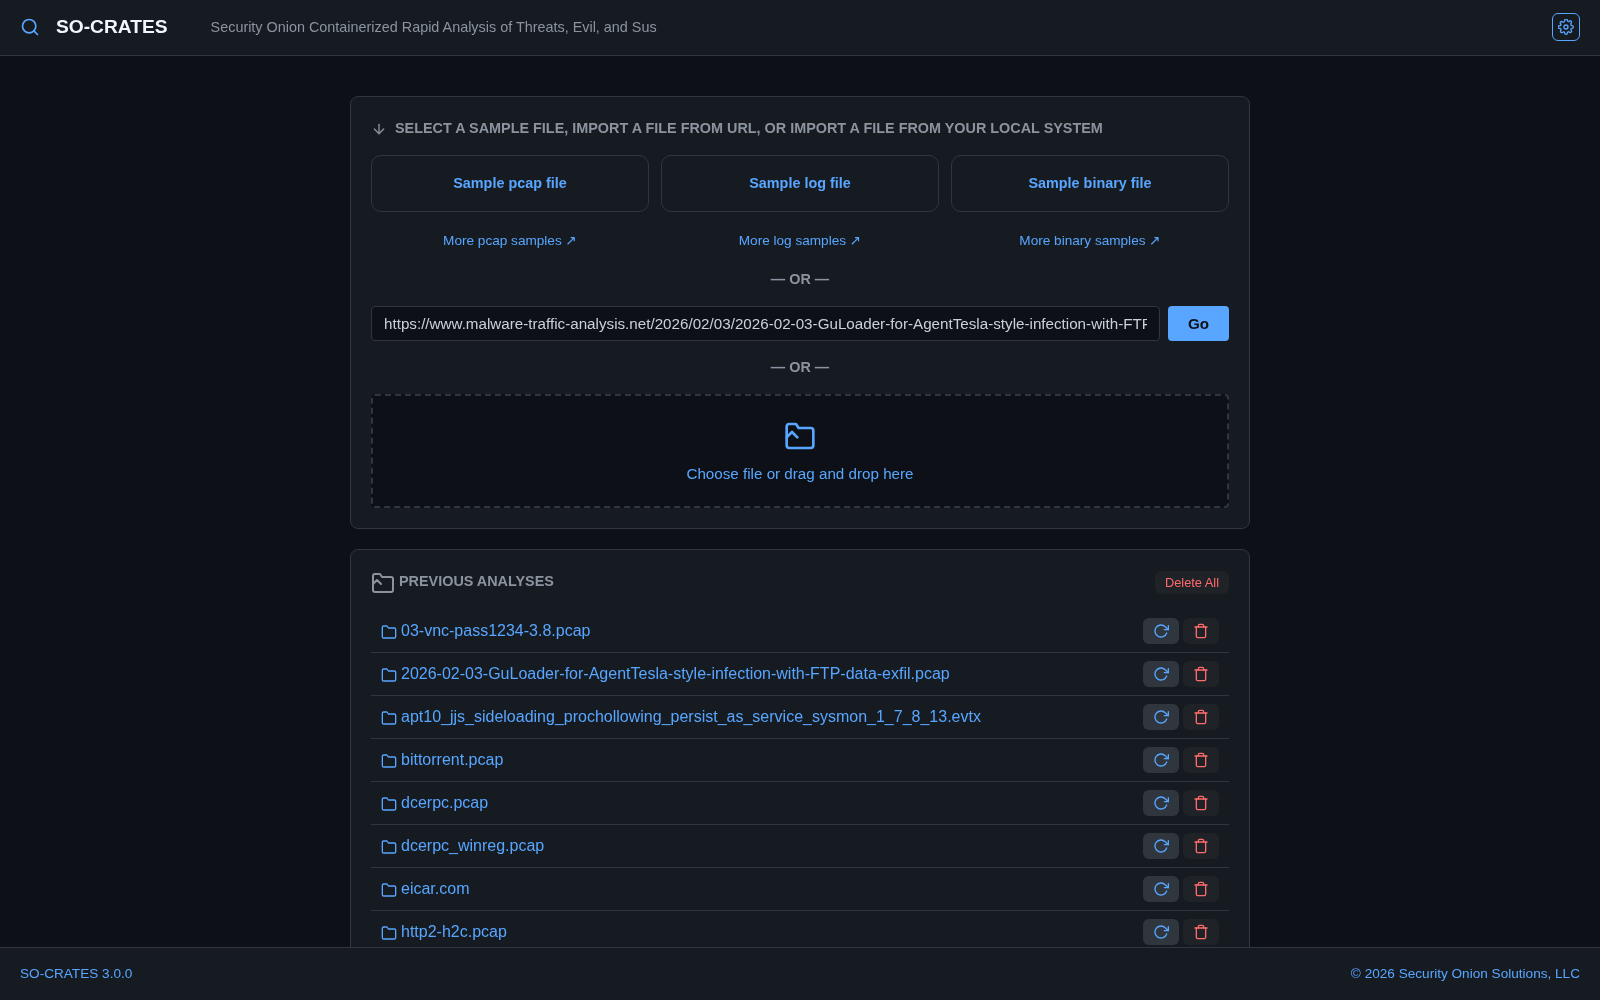
so-crates preview

so-crates

GitHubdougburks/so-crates

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

container-securitydigital-forensicseducation+8
6221 day ago
Previous123Next