
artifacts-kit
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
forrest-orr/artifacts-kitPseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
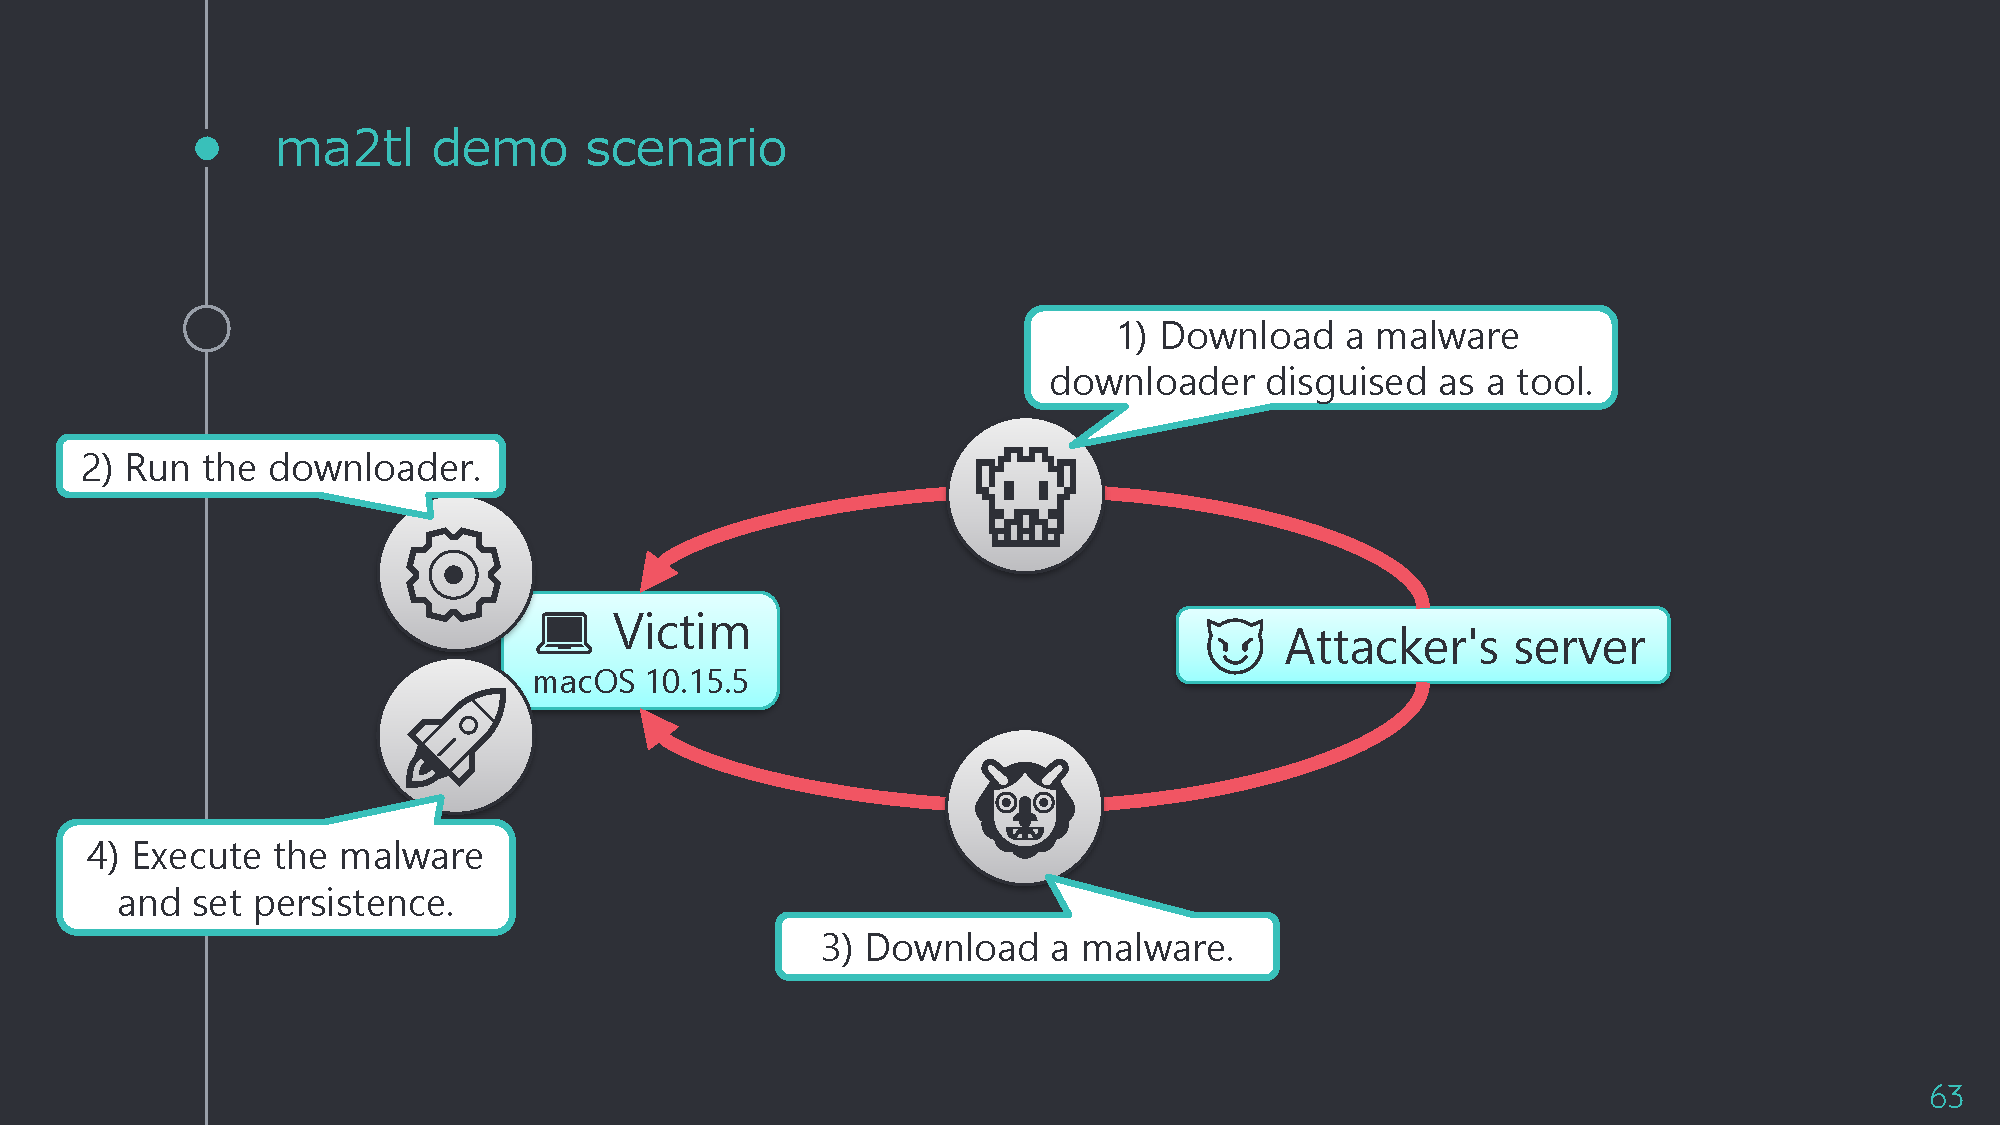 mnrkbys/ma2tl
macOS forensic timeline generator using the analysis result DBs of mac_apt
 circl/factual-rules-generator
Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…