

ir-rescue
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
digital-forensicsdisk-forensicsforensics+6
489
diogo-fernan/ir-rescueA Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 guardicore/ipcdump
BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…
 gmh5225/maldec-edr
Unix endpoint detection and response solution using kernel-level mechanisms to detect anomalies and malware attacks in real time.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor
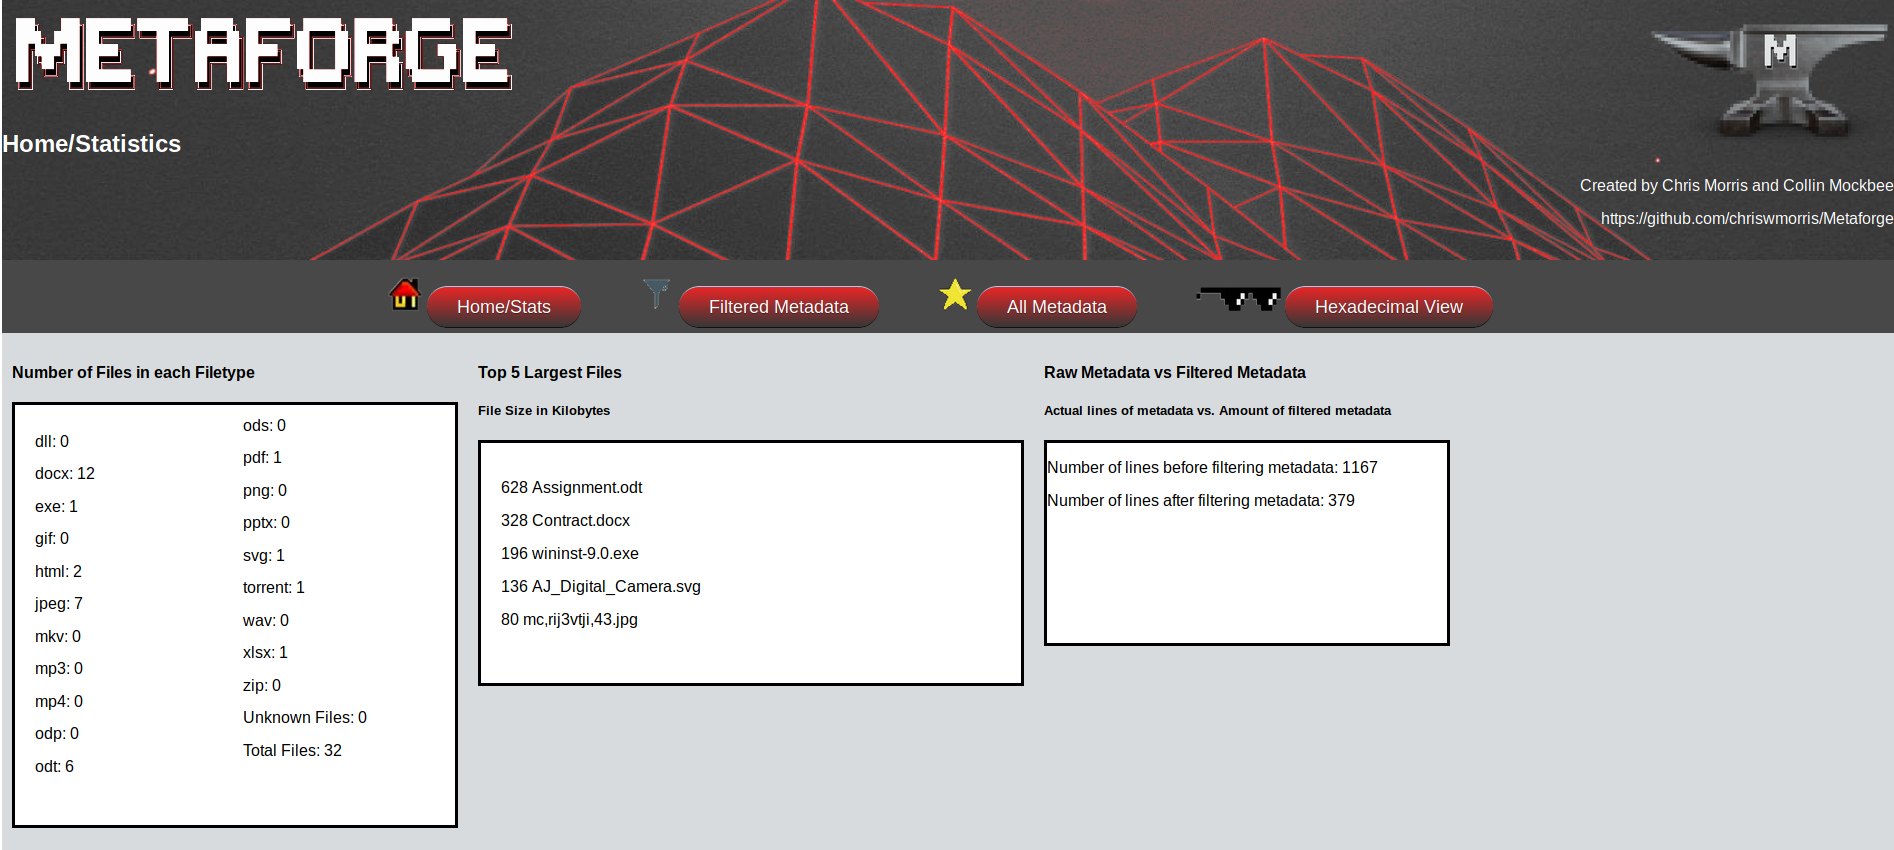 chriswmorris/metaforge
An OSINT Metadata analyzing tool that filters through tags and creates reports
