Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
111 results
ImpossibleTravelLogAnalysis preview

ImpossibleTravelLogAnalysis

GitHubnccgroup/impossibletravelloganalysis

Basic log analysis tool to detect impossible travel via IP address geographic information
anomaly-detectionforensicsincident-response+3
20
7 years ago
FOCA preview

FOCA

GitHubelevenpaths/foca

Tool to find metadata and hidden information in the documents.

forensicsinformation-gatheringosint+1
3.6k5 years ago
DeadMatter preview

DeadMatter

GitHubqsecure-labs/deadmatter

Offset Independent Credential Extraction Tool

data-recoverydigital-forensicsforensics+7
721 year ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
2188 years ago
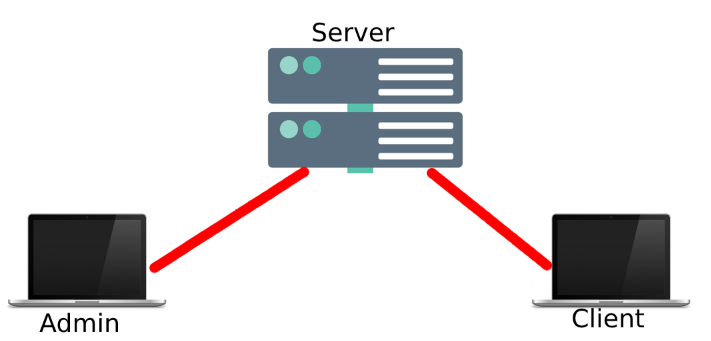
Simple-Live-Data-Collection preview

Simple-Live-Data-Collection

GitHubletsdefendio/simple-live-data-collection

Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
digital-forensicsforensicsincident-response+1
226 years ago
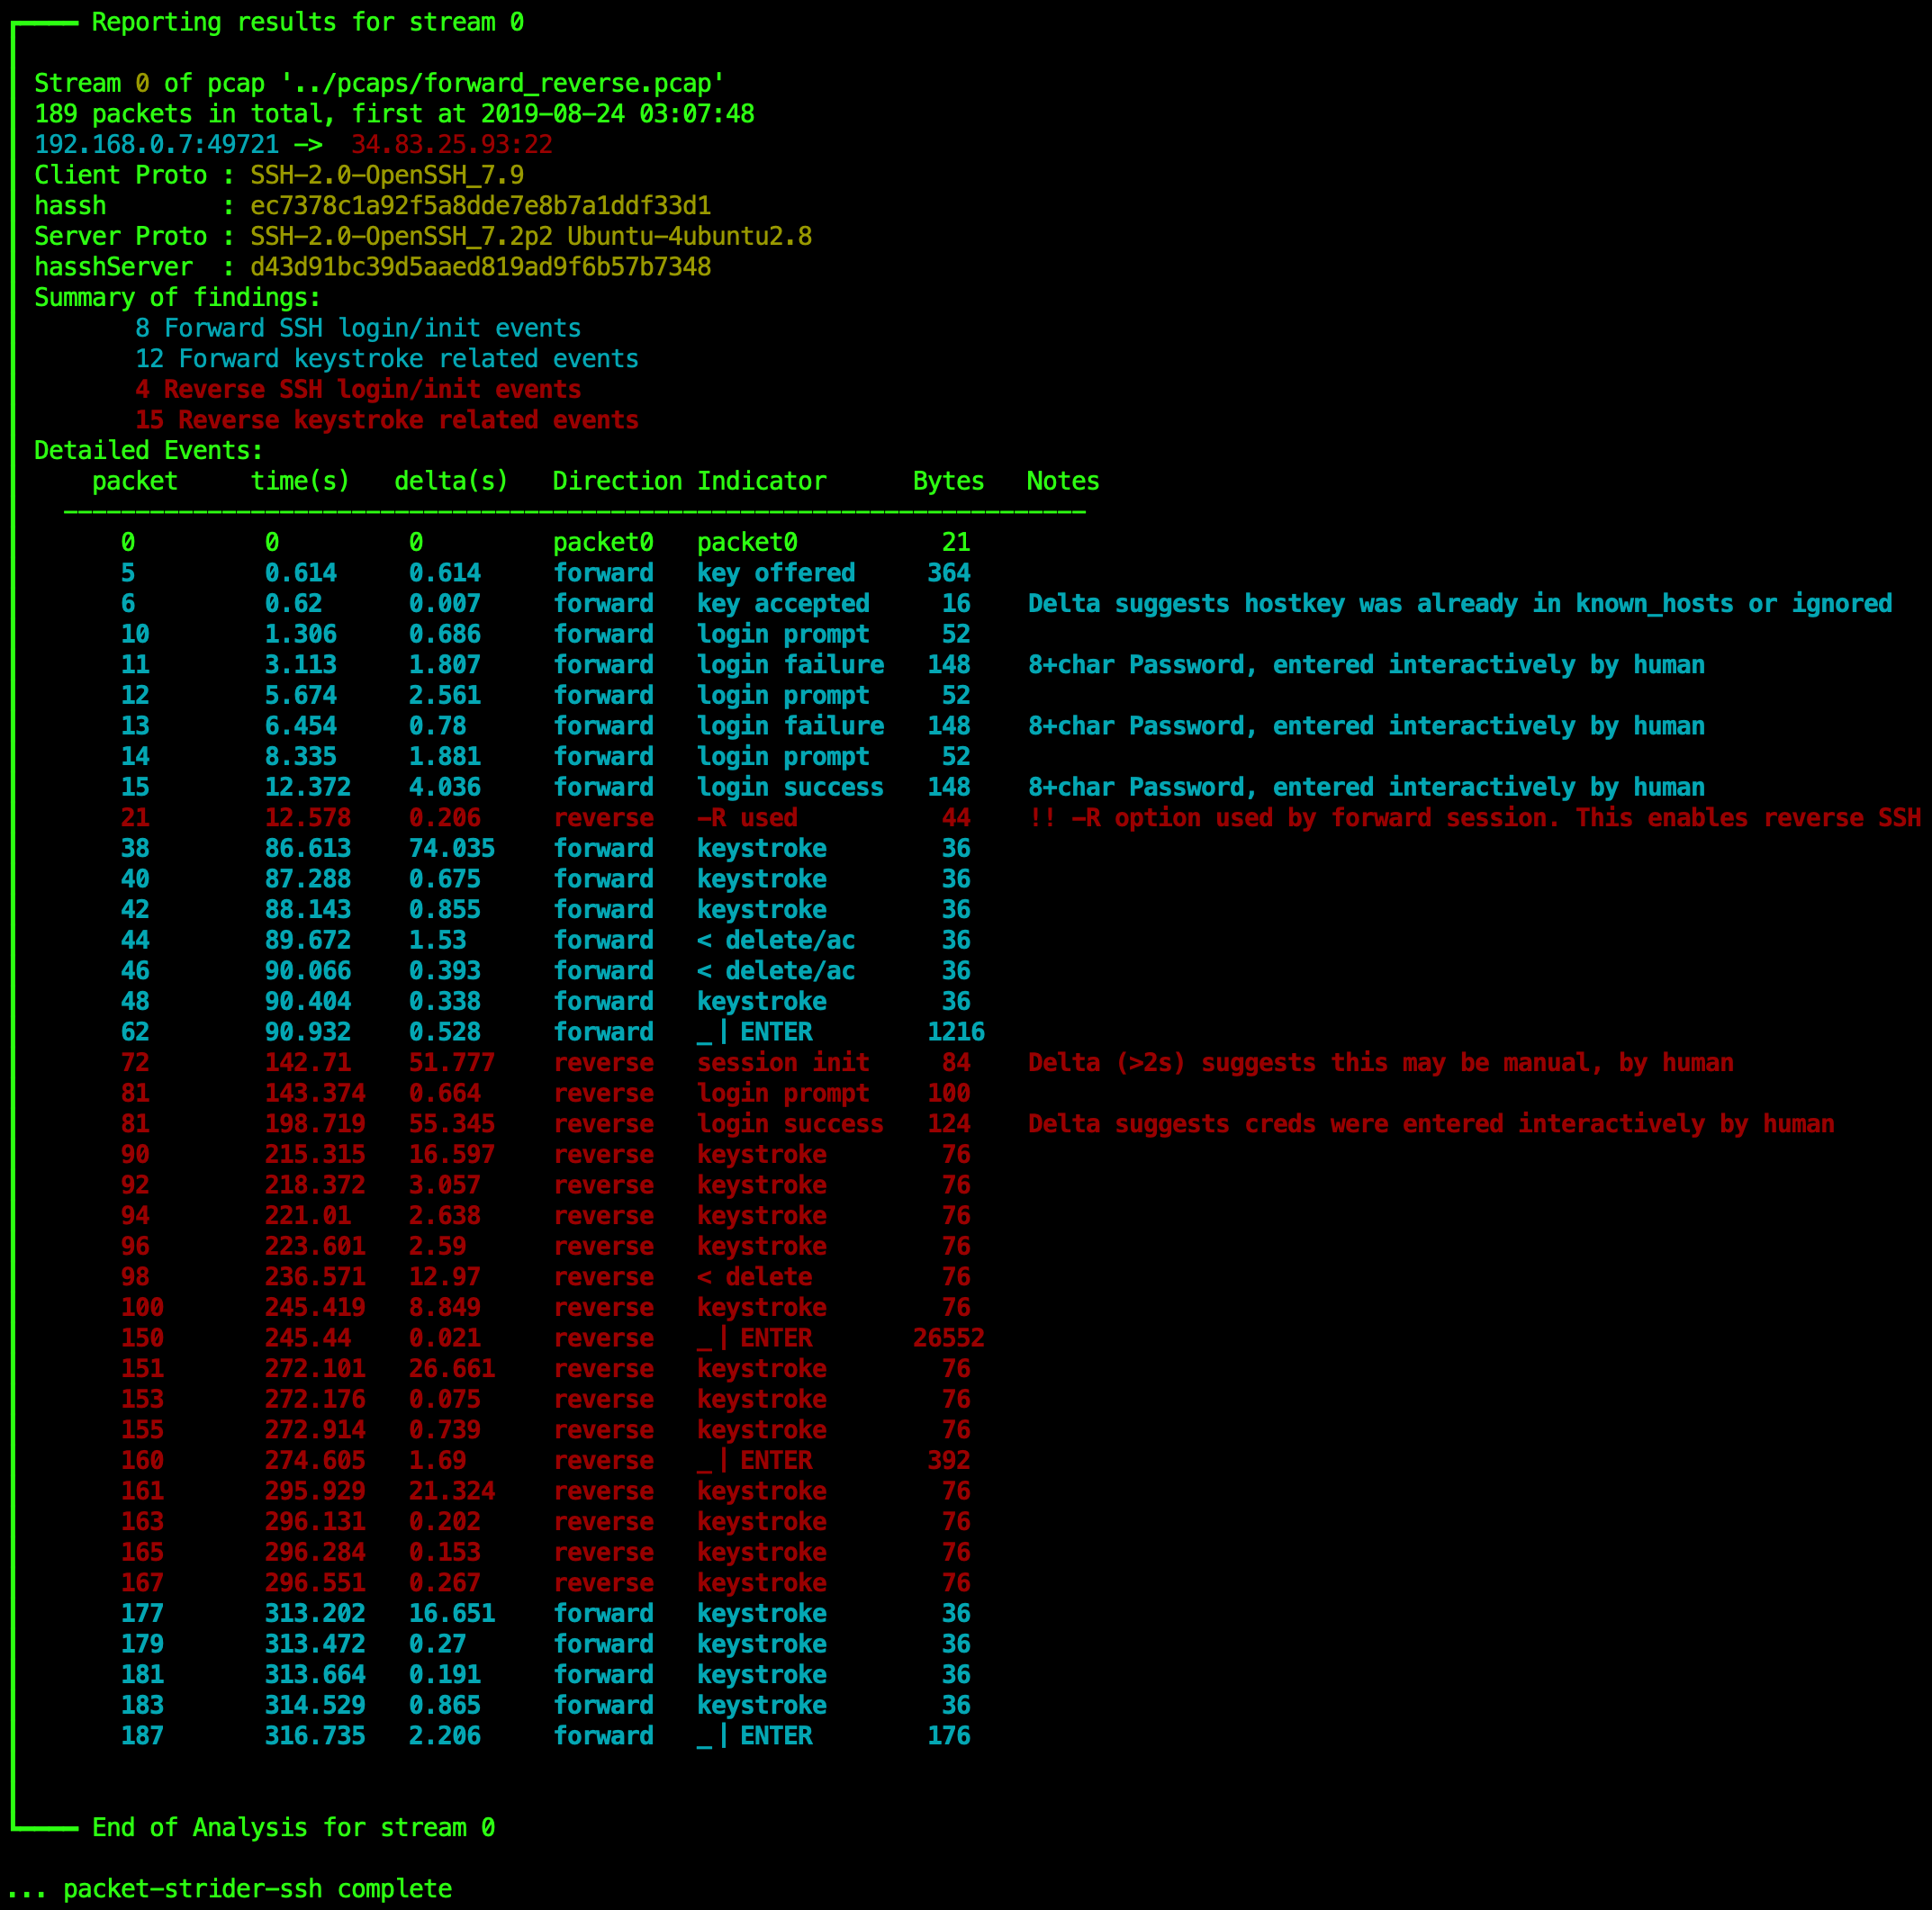
packetStrider preview

packetStrider

GitHubbenjeems/packetstrider

A network packet forensics tool for SSH
anomaly-detectionforensicsintrusion-detection+5
2547 years ago
Total-Commander-FTP-Password-Recovery-Tool-Python preview

Total-Commander-FTP-Password-Recovery-Tool-Python

GitHubpelock/total-commander-ftp-password-recovery-tool-python

Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…

data-recoveryencryption-decryption-toolsforensics+2
16 months ago
mailMeta preview

mailMeta

GitHubgr33nm0nk2802/mailmeta

An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
digital-forensicsemail-securityforensics+2
1755 years ago
MetadataPlus preview

MetadataPlus

GitHubnccgroup/metadataplus

A tool to use novel locations to extract metadata from Office documents.
digital-forensicsforensicsinformation-gathering+1
643 years ago
acropadetect preview

acropadetect

GitHublordofpipes/acropadetect

Browser-based tool to detect Acropalypse (CVE-2023-21036) by analyzing PNG/GIF images for truncated pixel data, enabling quick vulnerability…
exploitationforensicsinformation-gathering+2
33 years ago
iOSForensic preview
Archived

iOSForensic

GitHubflo354/iosforensic

iOS forensic tool

digital-forensicsforensicsinformation-gathering+3
6512 years ago
passivedns preview

passivedns

GitHubgamelinux/passivedns

A network sniffer that logs all DNS server replies for use in a passive DNS setup
dns-analysisforensicsincident-response+3
1.7k17 days ago
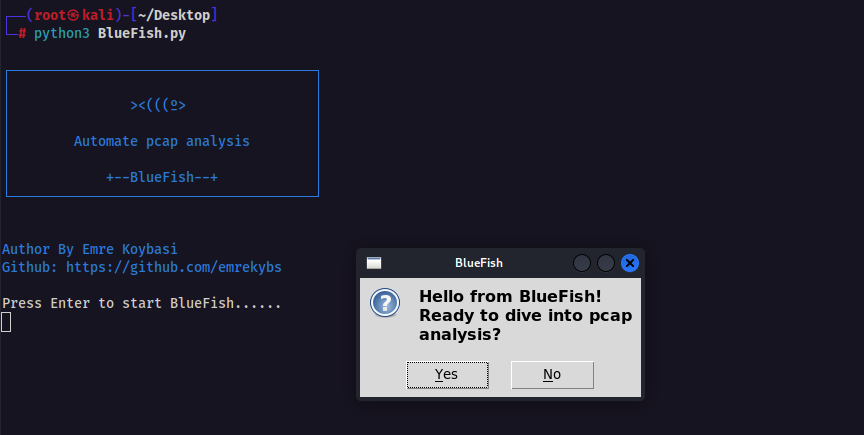
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
197 months ago
TEx preview

TEx

GitHubguibacellar/tex

Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…
digital-forensicsforensicsinformation-gathering+2
3752 years ago
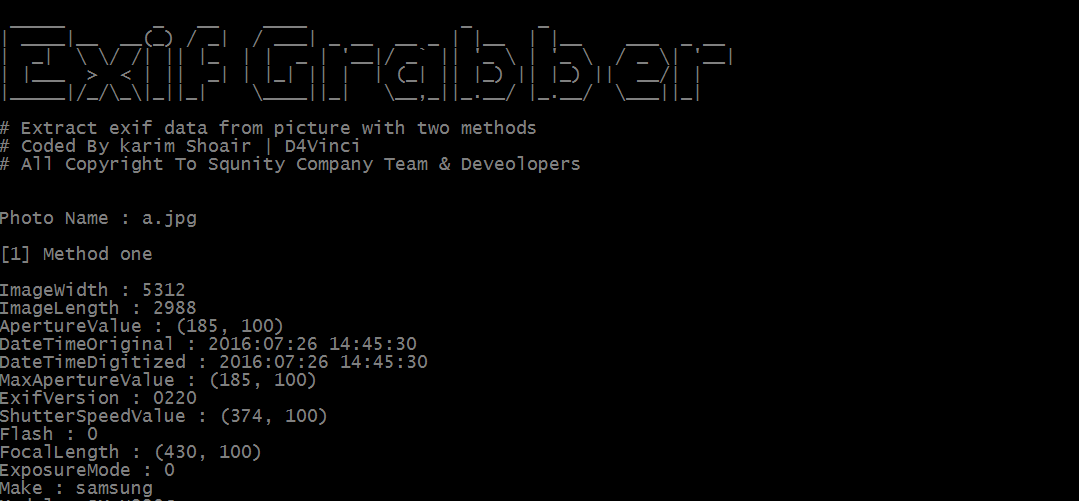
Exif-Grabber preview

Exif-Grabber

GitHubd4vinci/exif-grabber

A python tool that will extract exif data from picture with two methods
data-recoverydigital-forensicsforensics+3
4210 years ago
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
digital-forensicsforensicsinformation-gathering+3
8567 years ago
ngrep preview

ngrep

GitHubjpr5/ngrep

ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…

dns-analysisforensicsinformation-gathering+3
1.0k9 months ago
wholeaked preview

wholeaked

GitHubutkusen/wholeaked

a file-sharing tool that allows you to find the responsible person in case of a leakage

data-exfiltrationforensicsinformation-gathering+2
1.1k4 years ago
Previous1234567Next