An-Integrated-Wireless-Network-Forensic-Analysis-Framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

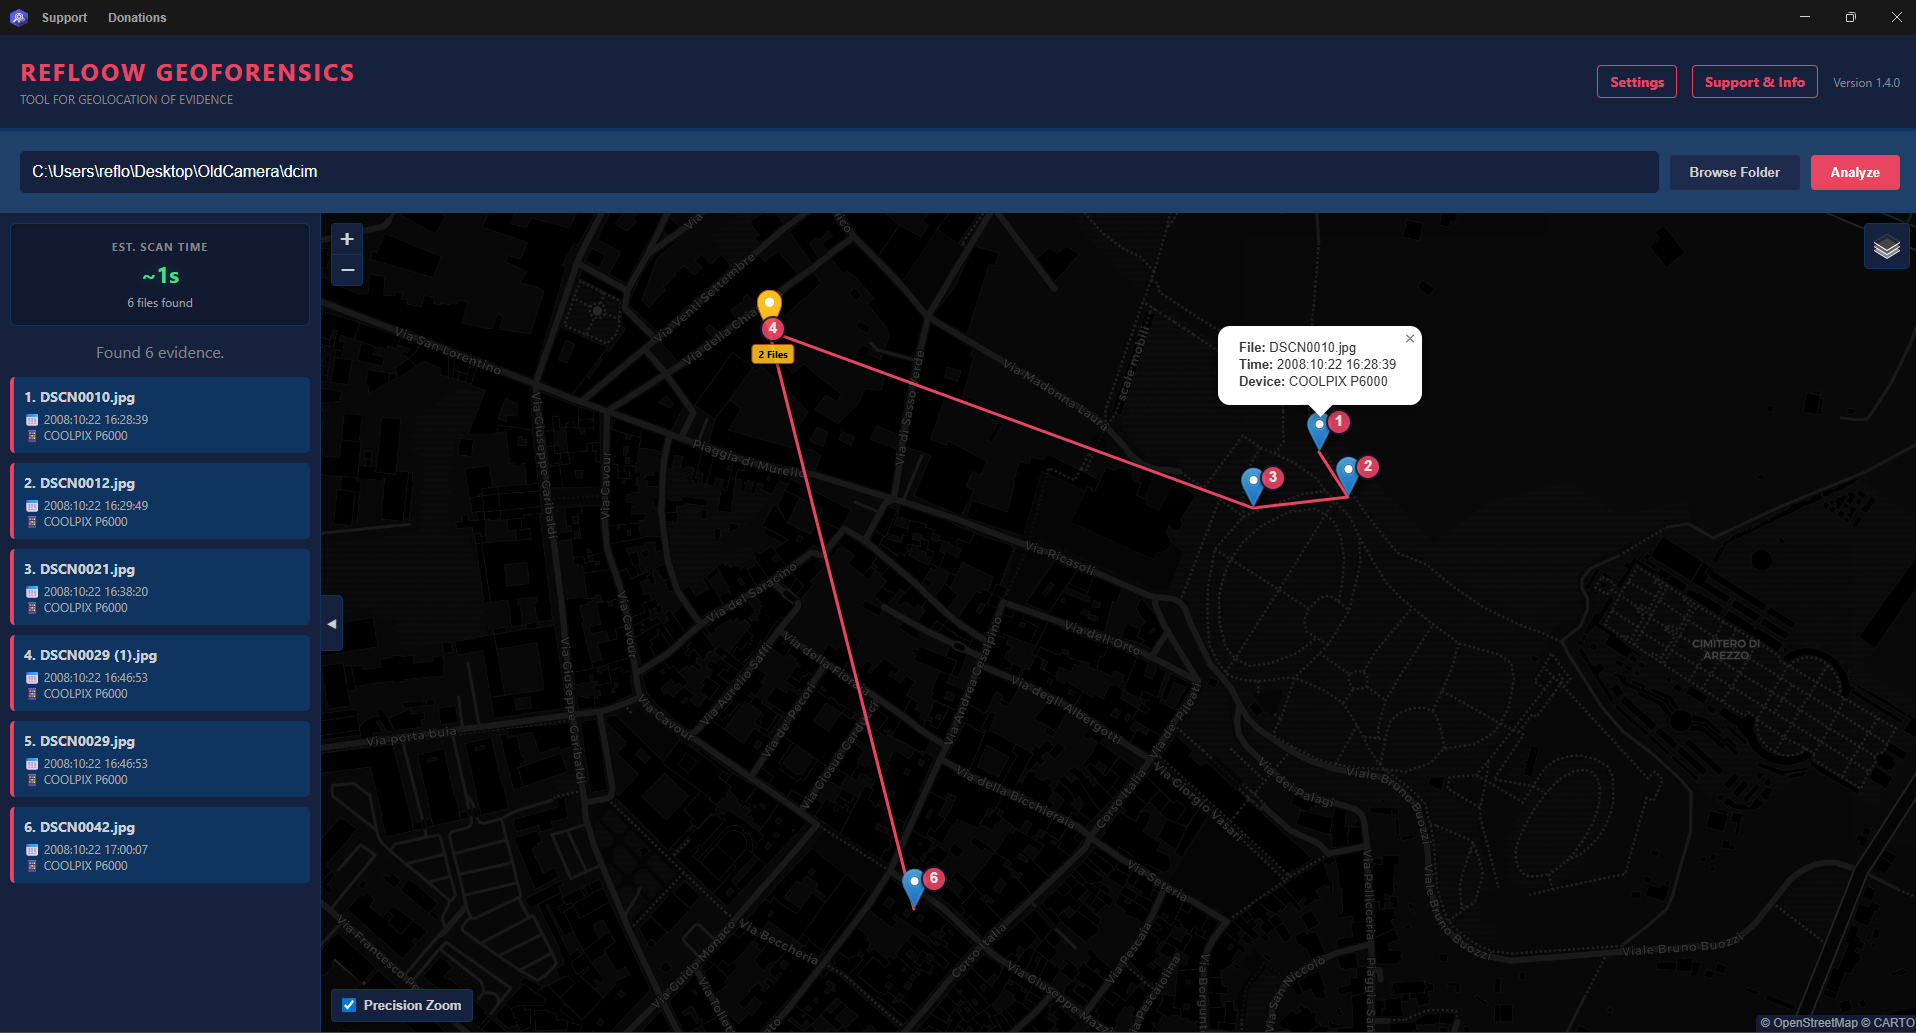
❤️ Free batch image & video geolocation digital forensics tool. Automatically extract EXIF data, visualize GPS coordinates on maps, and reconstruct…

Digital Forensics Intelligence Framework

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

Forensics artefact collection tool for systems running Microsoft Windows


OpenFPC, Open Source Full Packet Capture

Bramble is a hacking Open source suite.

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.

Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

A curated list of awesome Hacking tutorials, tools and resources

Defund the Police.

privacy-first, open-source and free idevice management tool written in Rust and Qt

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project