

Loki
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k
neo23x0/lokiIOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
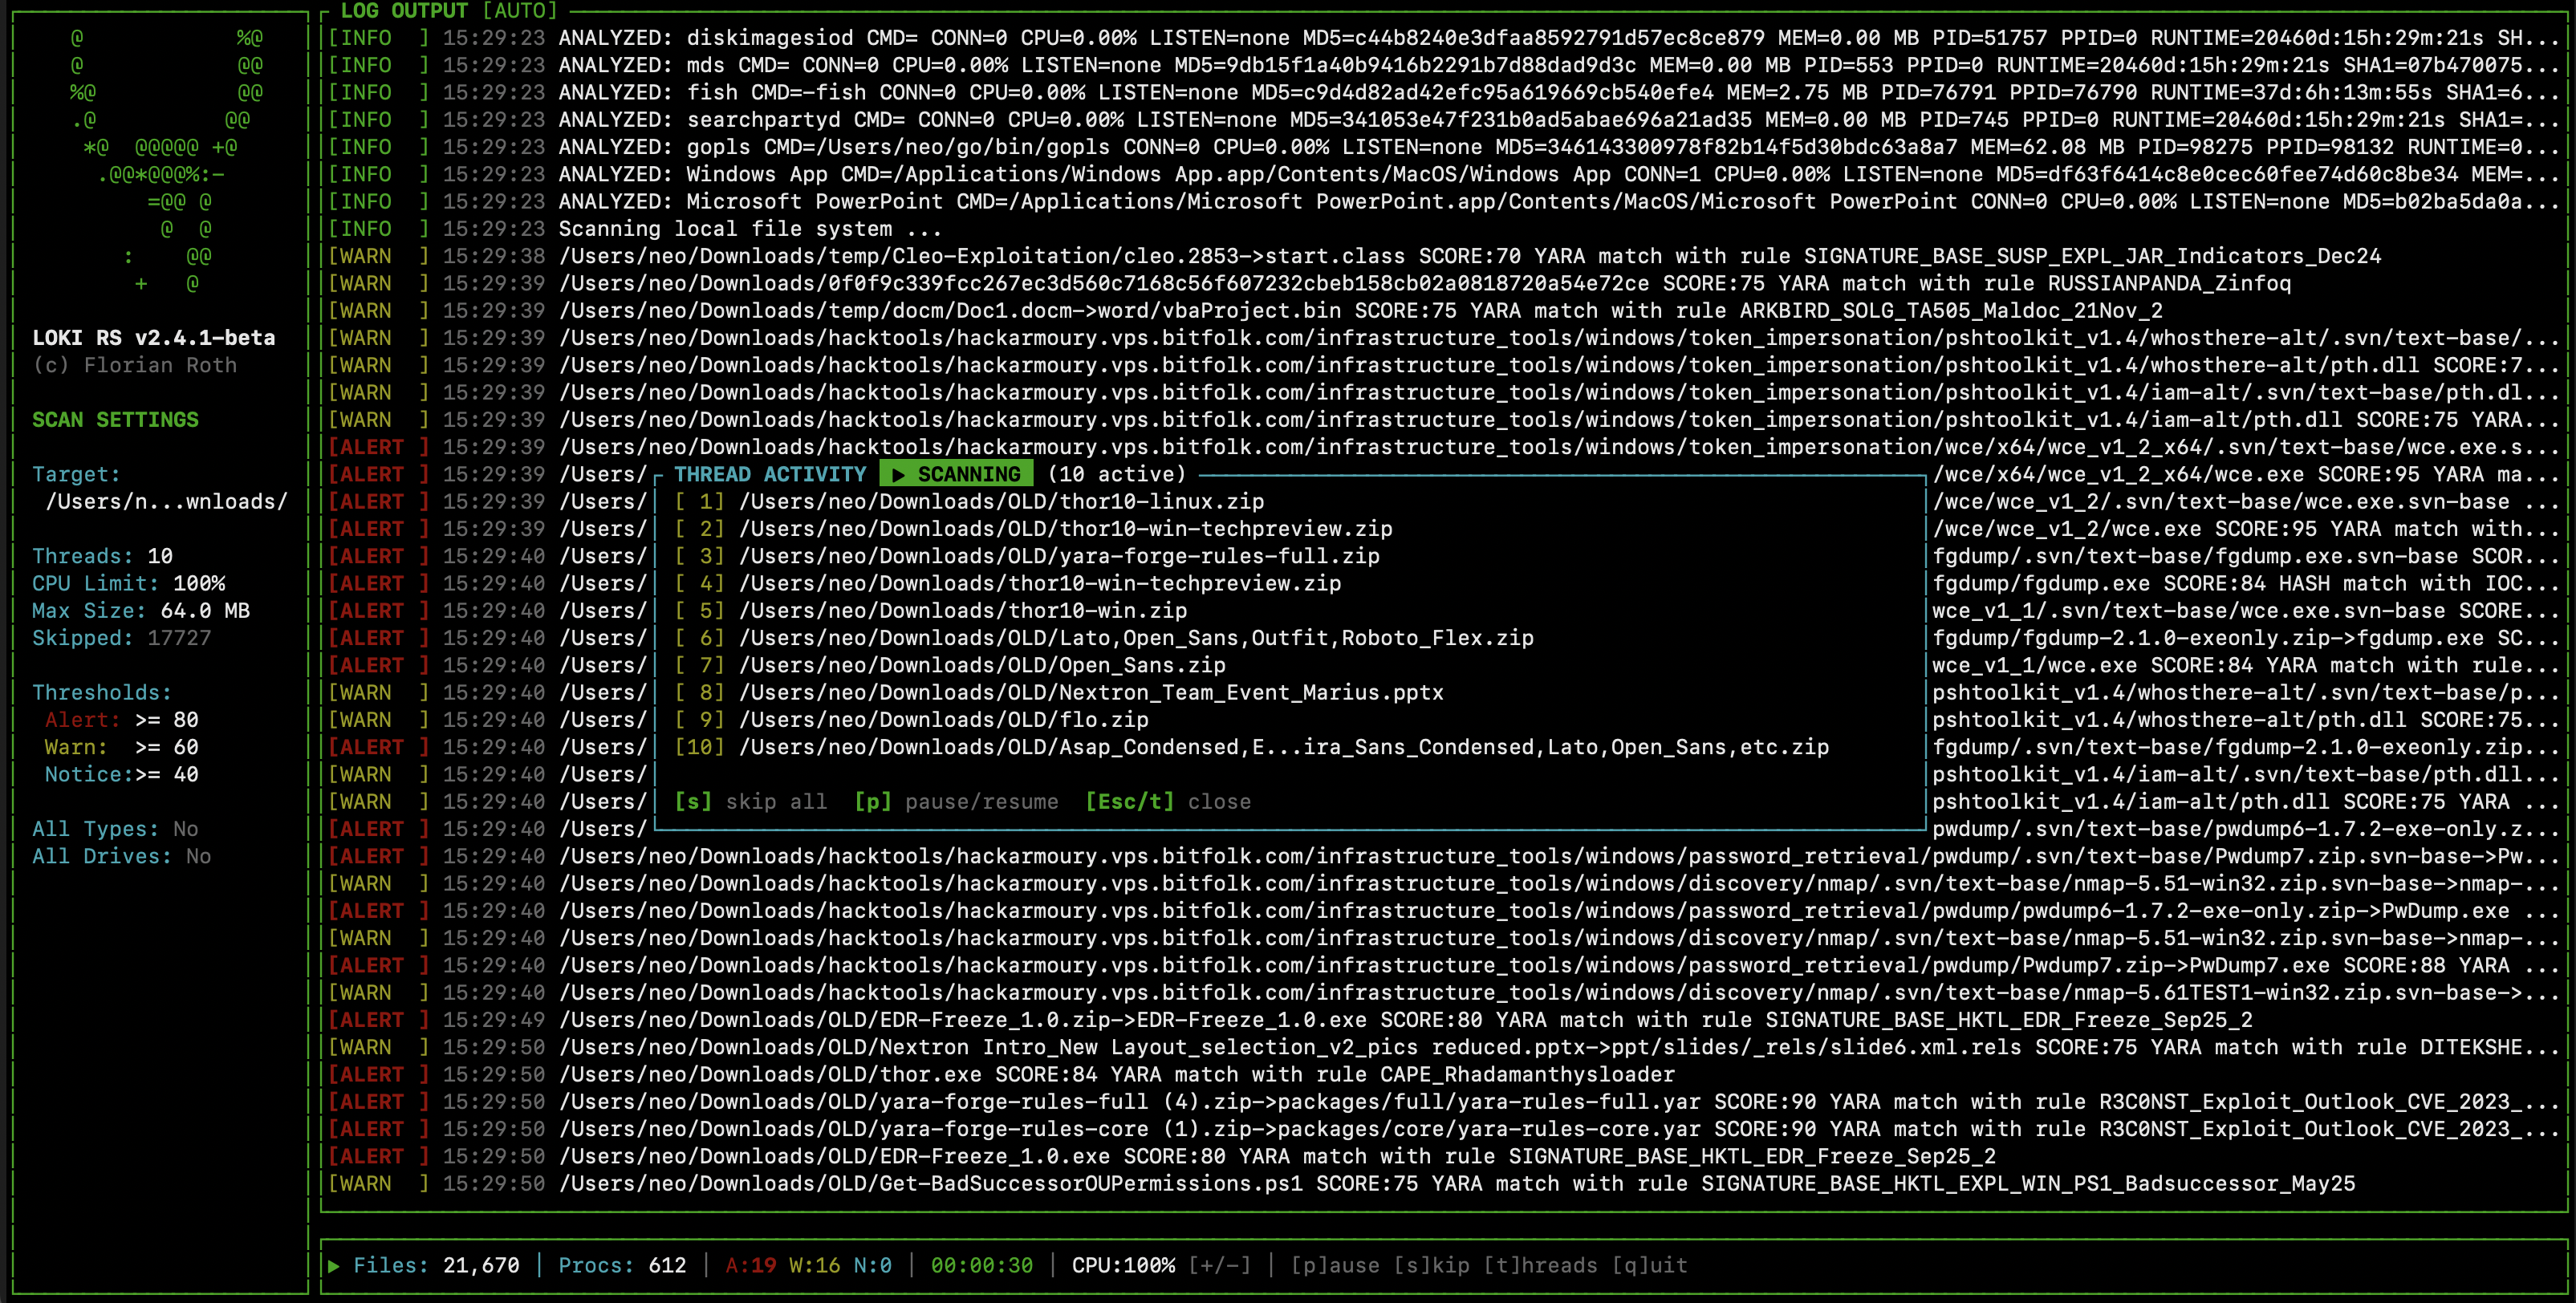 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…

 botherder/kraken
Cross-platform Yara scanner written in Go
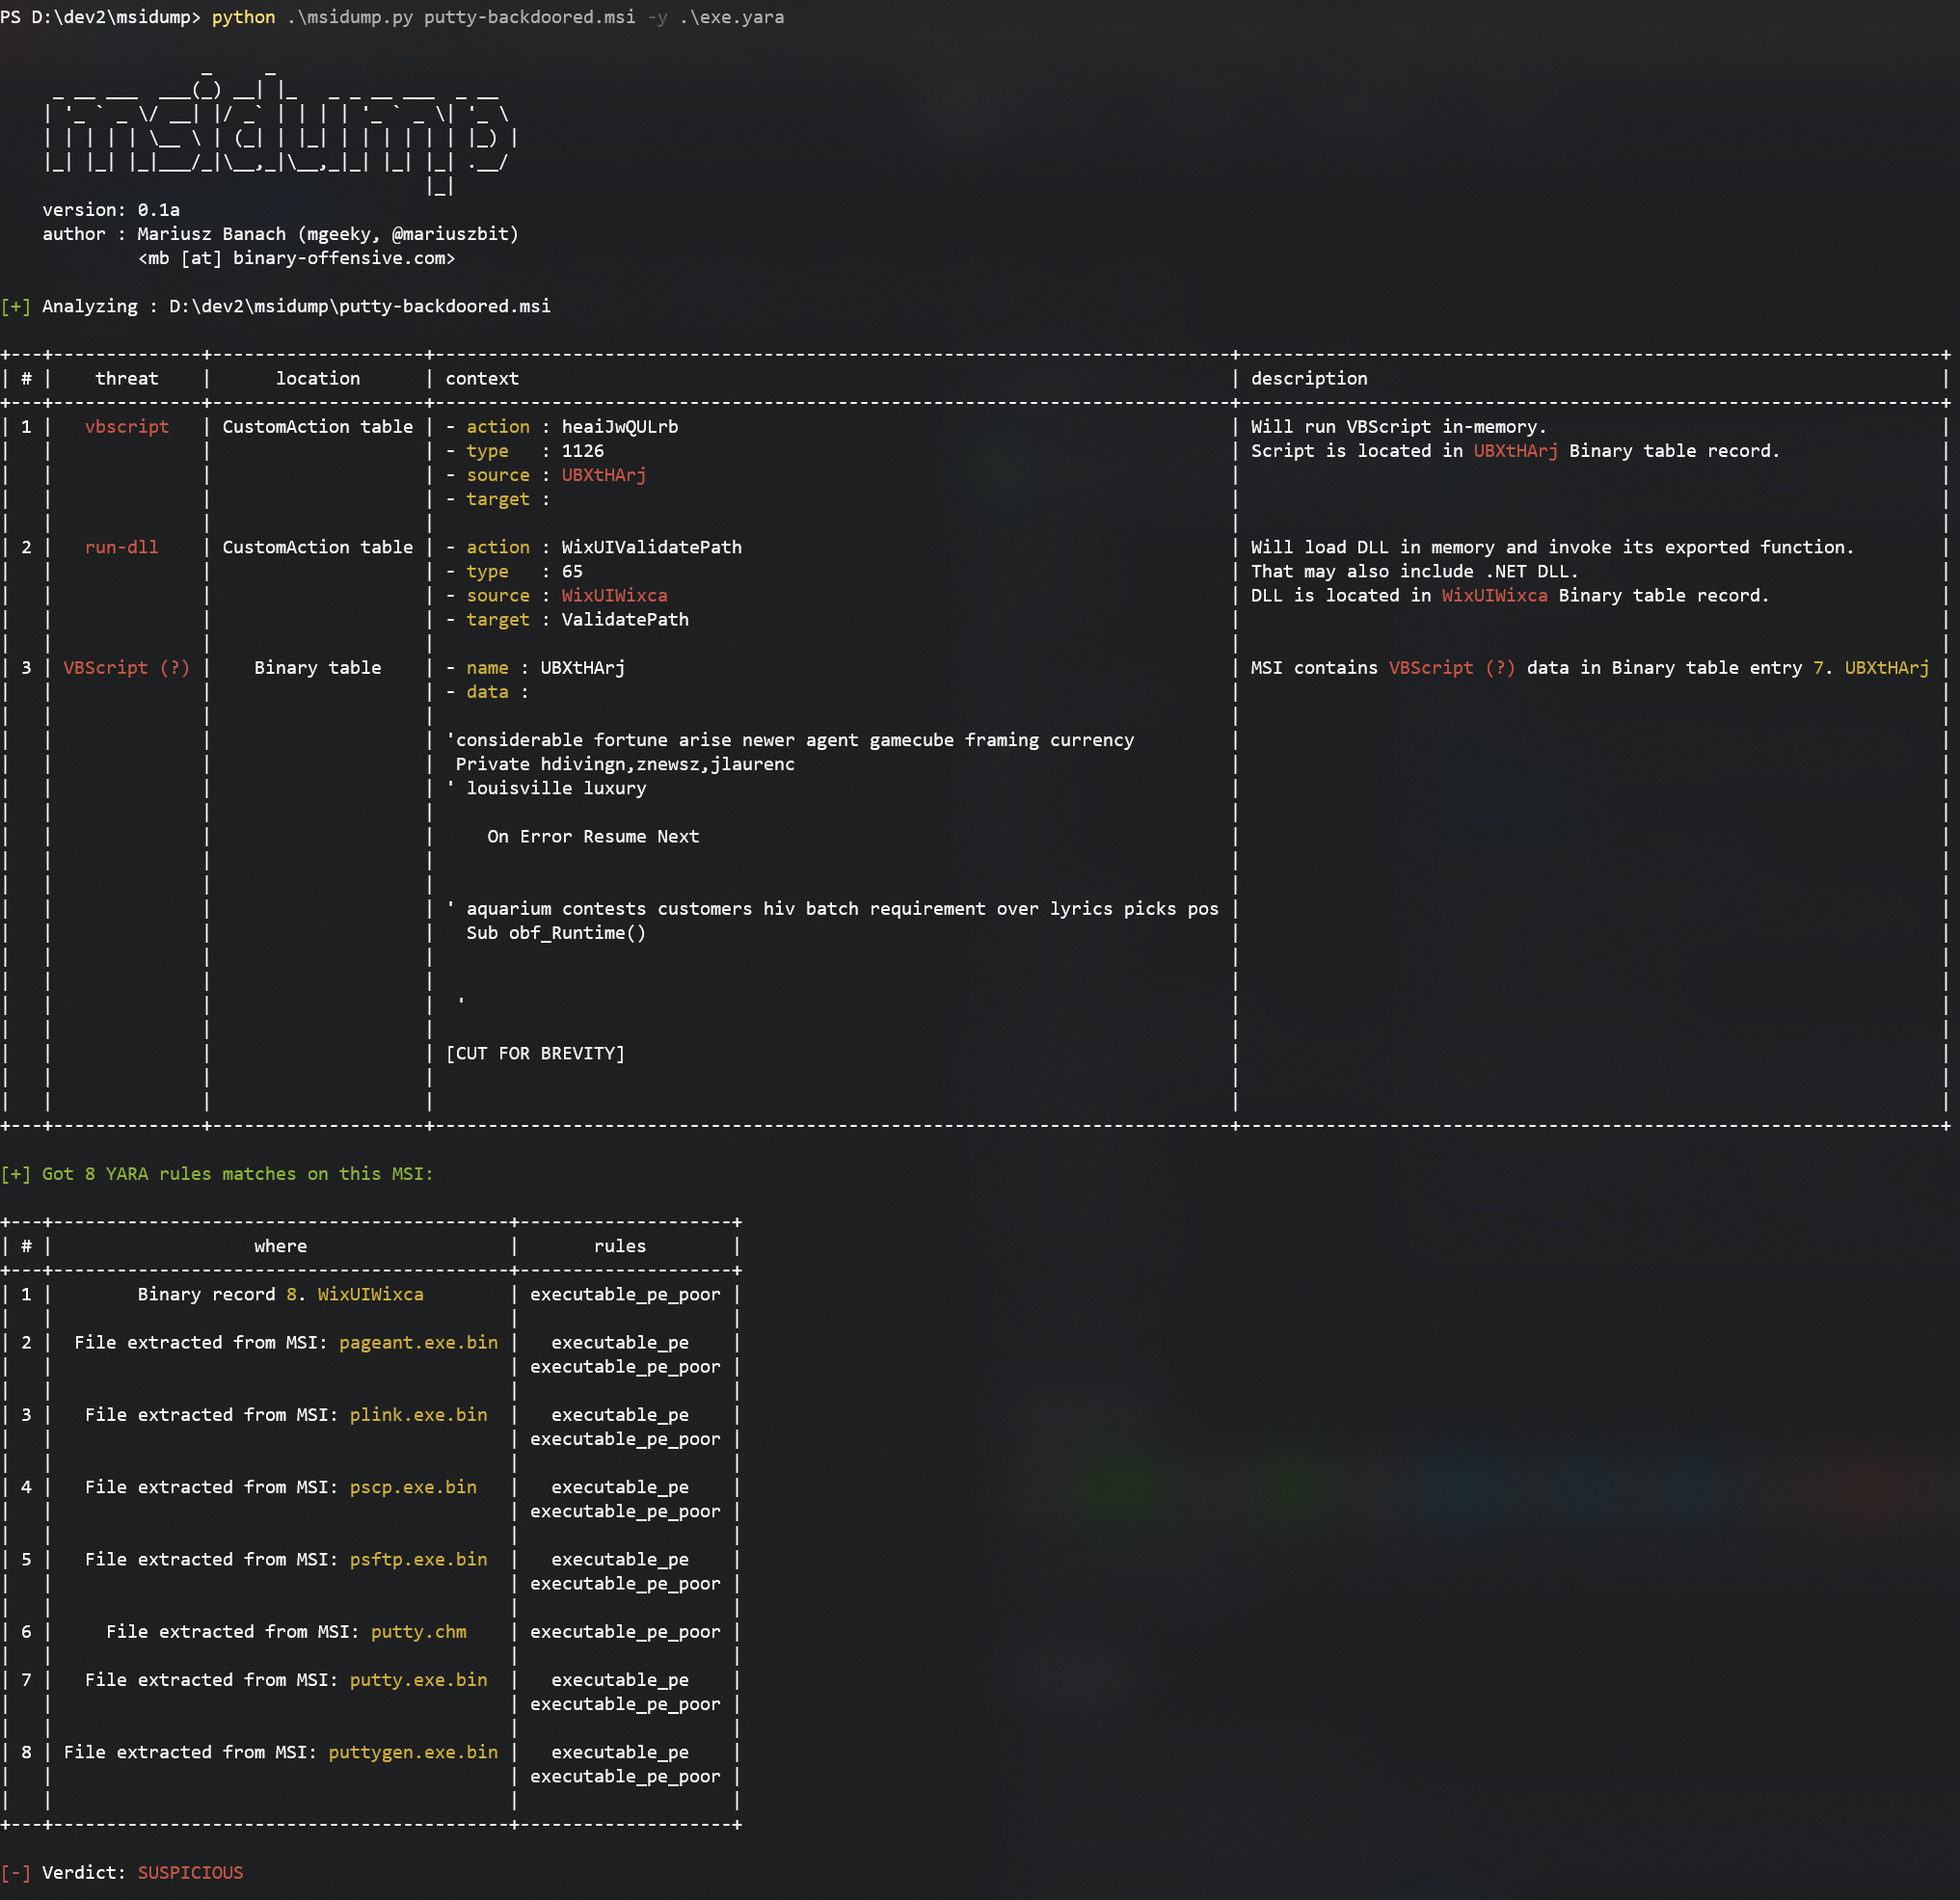 mgeeky/msidump
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
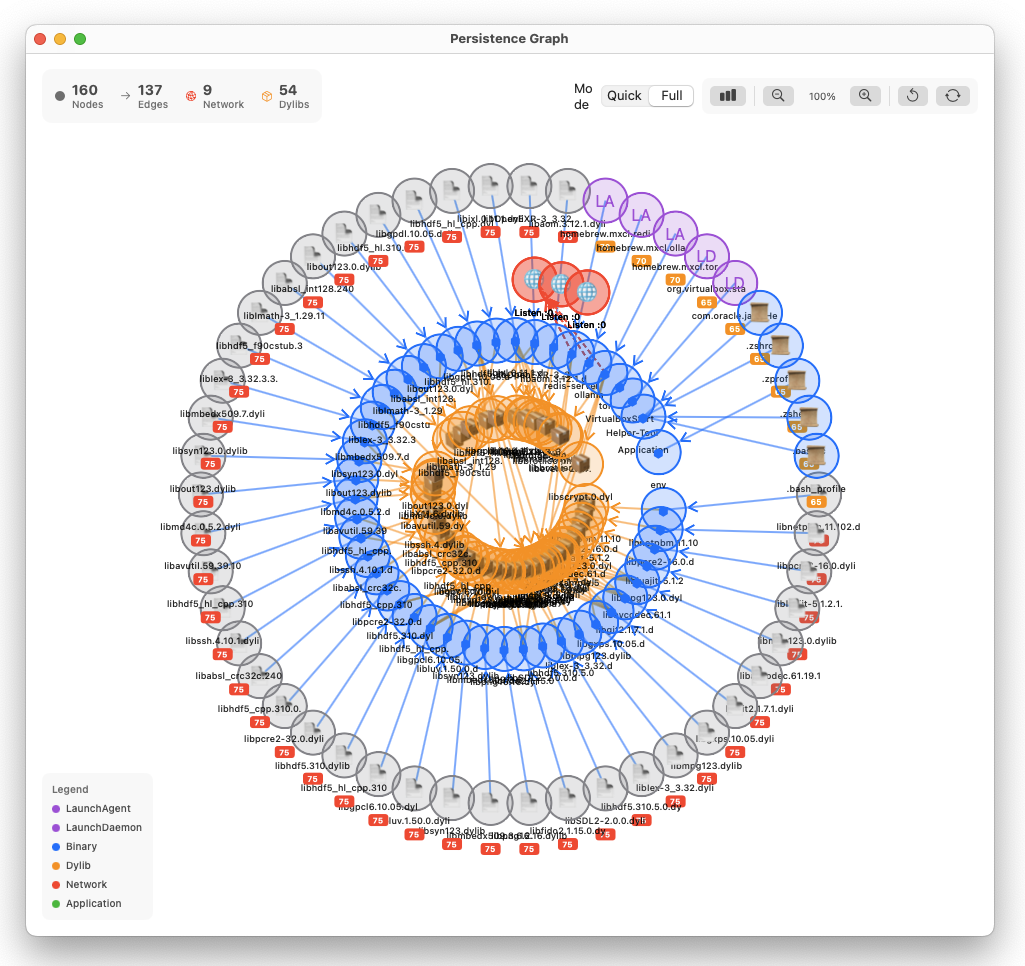 pinperepette/macpersistencechecker
macOS persistence mechanism scanner with code signature verification and timeline tracking.
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 tstillz/webshell-analyzer
Web shell scanner and analyzer.
 crowdstrike/xwf-yara-scanner
Native YARA scanner X-Tension for X-Ways Forensics, enabling in-snapshot file scanning with multi-threaded RVS support, report table output, and no…
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 jfrog/cve-2024-3094-tools
Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…

 onapsis/cve-2020-6287_recon-scanner
Black-box vulnerability scanner and indicator-of-compromise analyzer for CVE-2020-6287 (RECON) in SAP NetWeaver Java applications, enabling rapid…
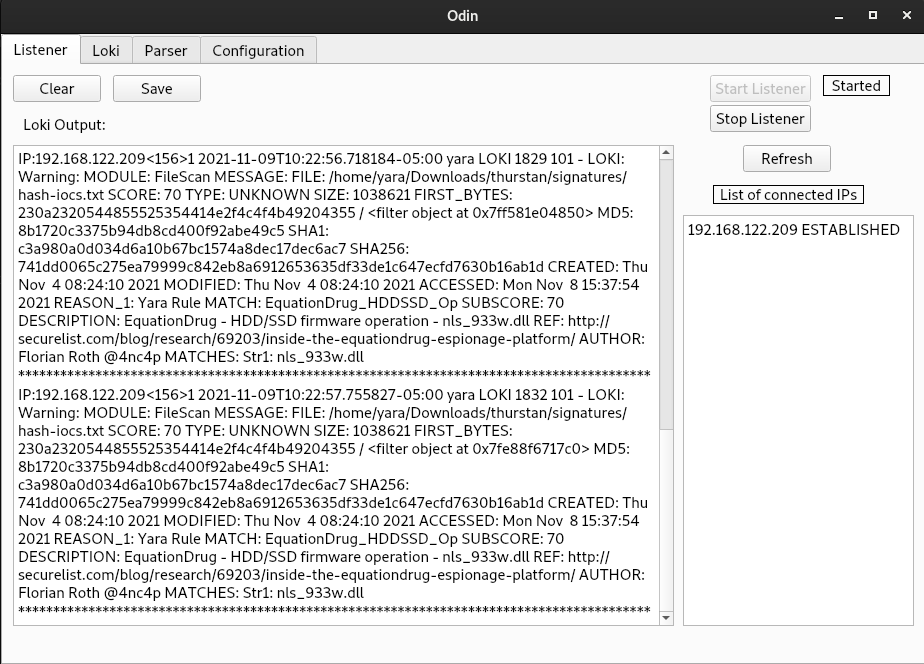 hamza-megahed/odin
Centralized IoC scanner that deploys Loki across endpoints, collects detection results, and parses logs into CSV for incident response and forensic…