

rvbbit-arsenal
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
command-and-controldefensive-toolseducation+5
16
buter-chkalova/rvbbit-arsenalOffensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 matheuzsecurity/modtracer
Detects hidden Linux kernel rootkits (LKM-based) and restores their visibility using kernel-level inspection techniques for forensic analysis and…

 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 velocidex/linpmem
Linux kernel driver for physical memory acquisition, enabling read access to any physical address including reserved memory and memory holes, with…
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 sebinxavi/cve-checker-2026
Multi-OS vulnerability checker for CVE-2026-31431 (Linux kernel) and CVE-2026-41940 (cPanel)
 tangjie1/cve-2026-31431-check
CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…
 atlasvector/dirty-frag-cve-2026-43284
Lab detection exercise for DirtyFrag (CVE-2026-43284) - Linux kernel privilege escalation via xfrm-ESP page cache corruption. Full write-up covering…
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
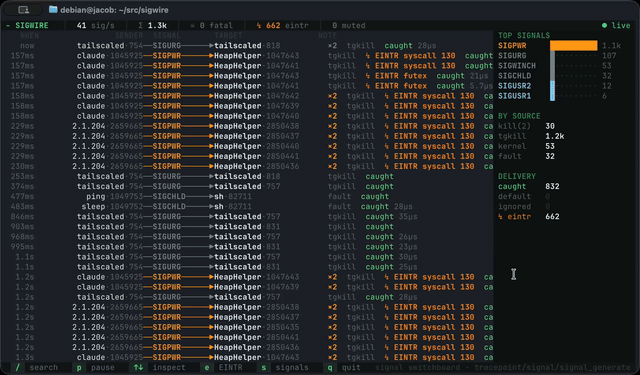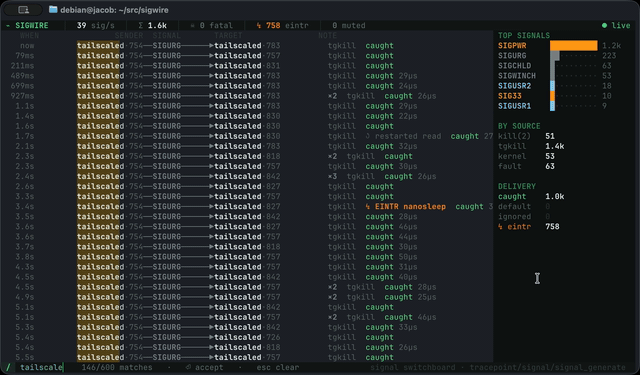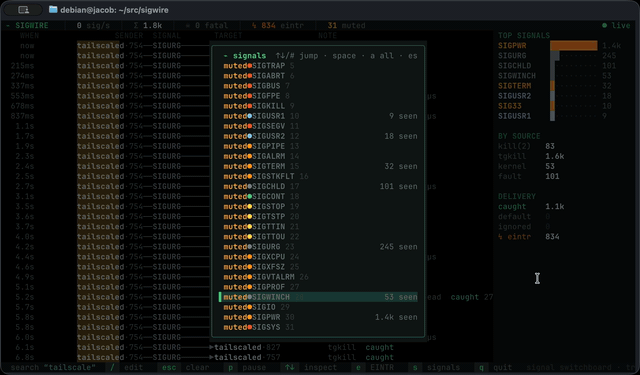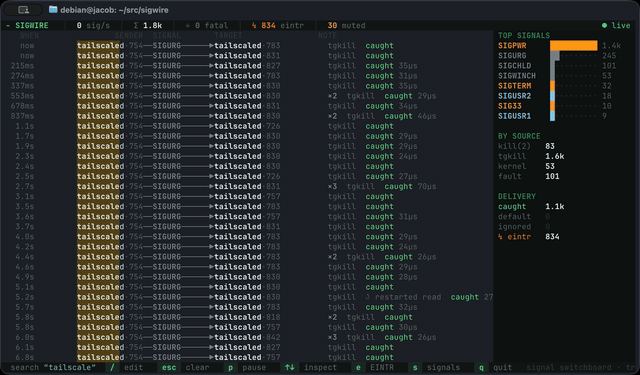 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 harshavmb/fim-ebpf
A lightweight eBPF program to monitor file creation and modification events on Linux. This tool leverages eBPF (Extended Berkeley Packet Filter) to…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…