
Dirty-Frag-CVE-2026-43284
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
educationexploitationforensics+5
2
kuniyal08/dirty-frag-cve-2026-43284A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
 atlasvector/dirty-frag-cve-2026-43284
Lab detection exercise for DirtyFrag (CVE-2026-43284) - Linux kernel privilege escalation via xfrm-ESP page cache corruption. Full write-up covering…
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 g0thamrabb1t/cve-2026-43284-dirtyfrag-detection
Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…
 makitos666/cve-2026-31431-copy-fail-detection-toolkit
Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 mellen9999/cmdchamp
bash CLI trainer — 30 levels from ls to privilege escalation
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 drolley919/joomla-cve-2015-8562-exploit-and-linux-forensic-analysis
Exploit for Joomla CVE-2015-8562 combined with Linux forensic analysis capabilities for post-exploitation investigation and evidence collection.
 mahfuzreham/cpanel-cve-2026-41940
cPanel CVE-2026-41940 nuclear.x86 Security Audit & Cleanup Script
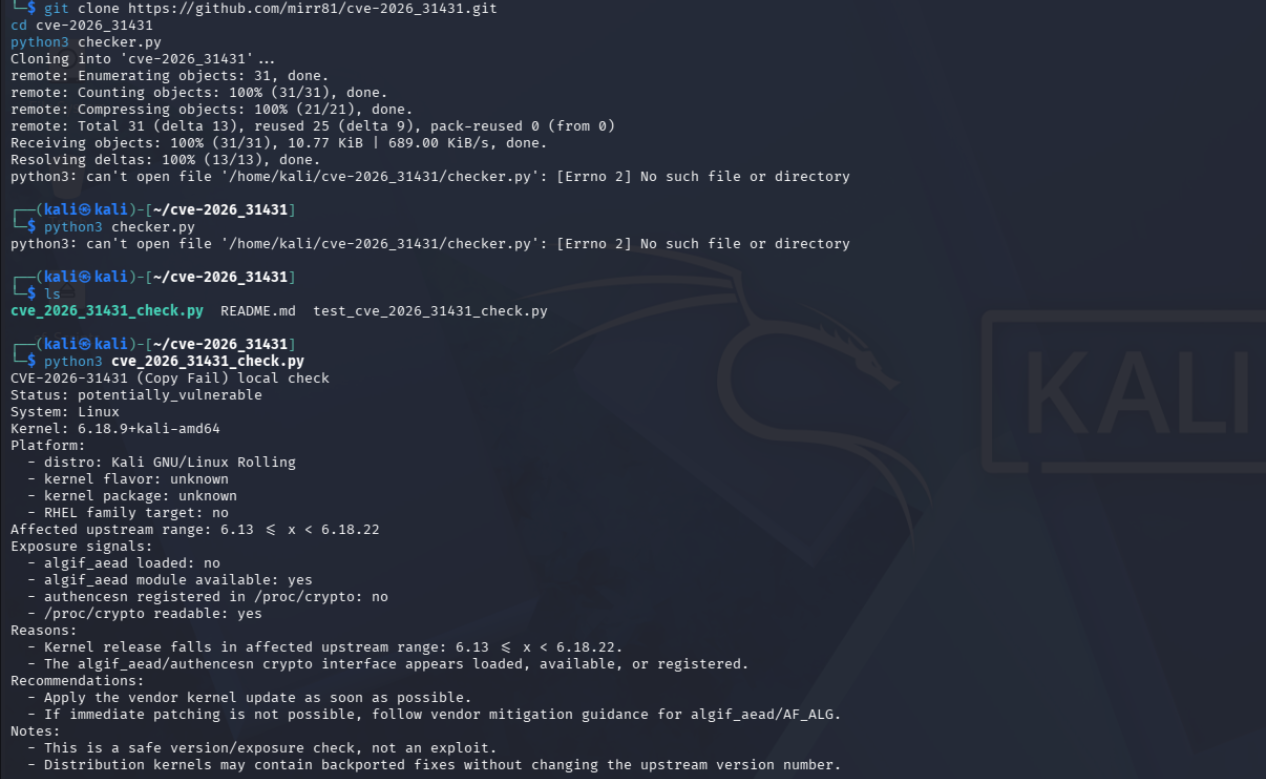 kuniyal08/copy-fail-cve-2026-31431-lab
Reproduced the fileless LPE CVE‑2026‑31431 (“Copy Fail”) on Kali Linux, then built auditd, Sigma & YARA detections to catch this stealthy kernel…
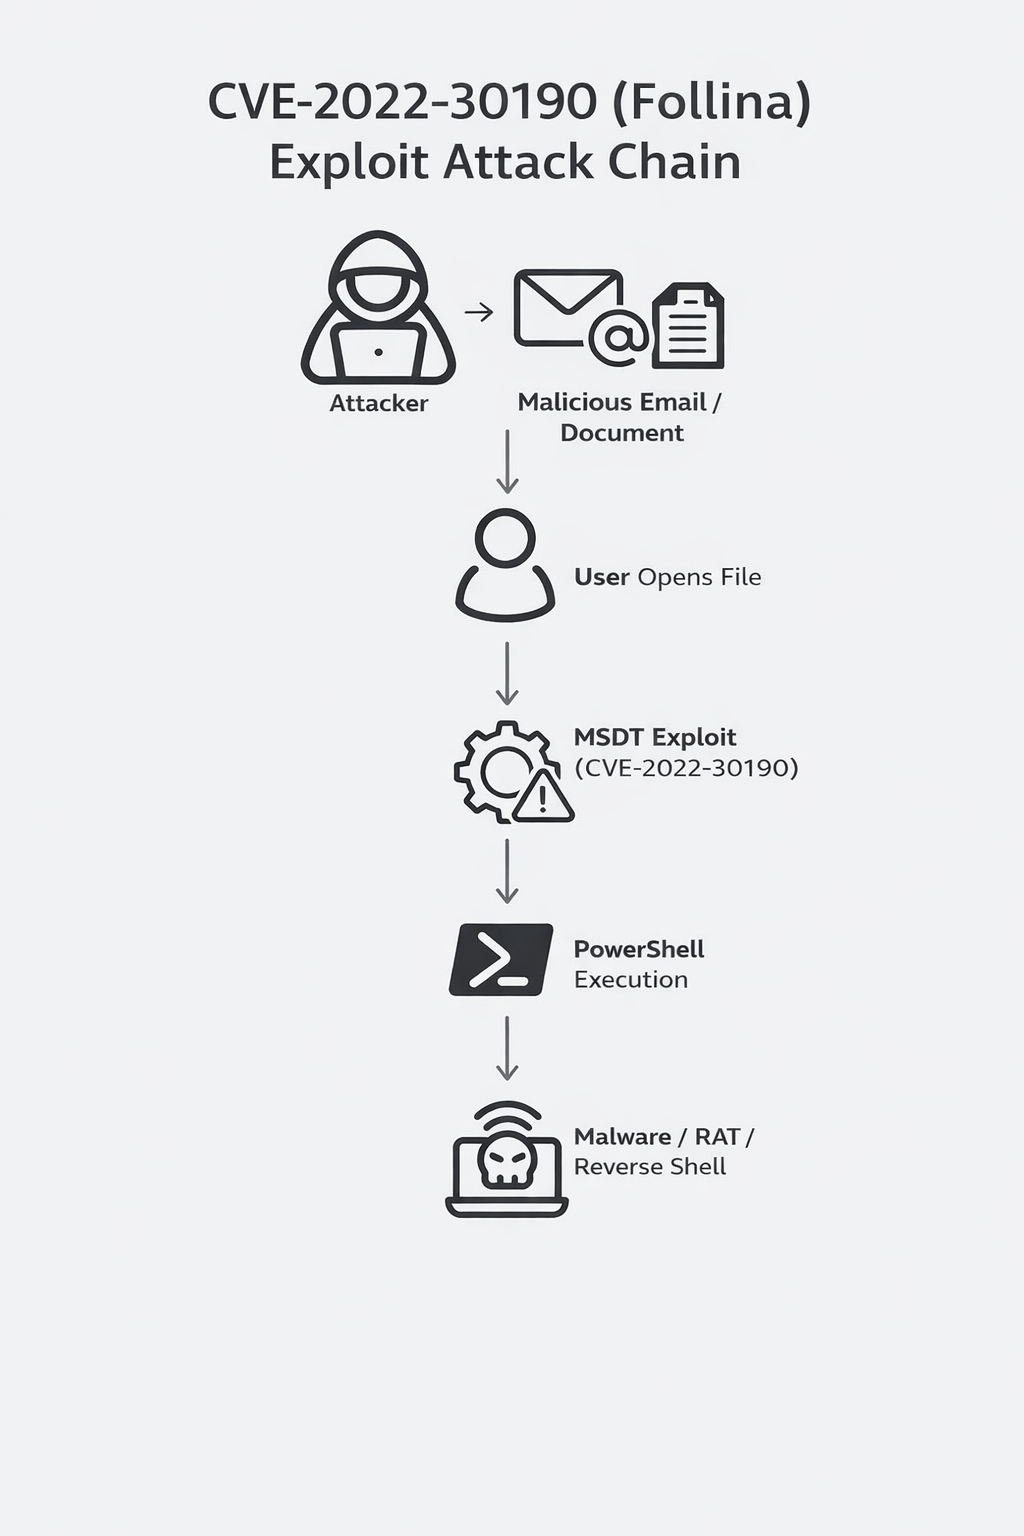 nimesh895/malware-analysis-follina-cve-2022-30190
Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…
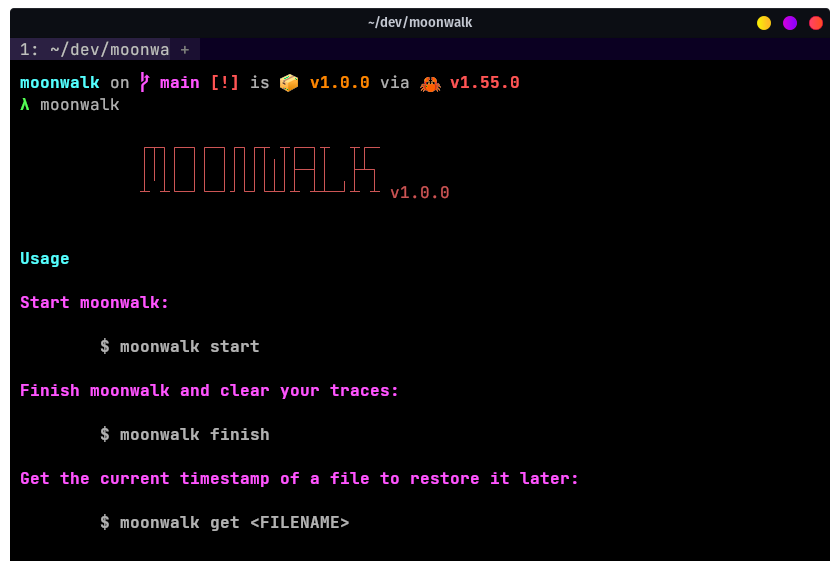 mufeedvh/moonwalk
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.