

DOCxNGINxFX
 hellgatecorp/docxnginxfx
Deep File Forensic. Create or manipulate Wordlists out of Text Documents (ex: for BruteForcing). Save it Line by Line as a Binary .BIN File or as a…
forensicspassword-crackingutilities-frameworks
hellgatecorp/docxnginxfxDeep File Forensic. Create or manipulate Wordlists out of Text Documents (ex: for BruteForcing). Save it Line by Line as a Binary .BIN File or as a…
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.

 netspooky/inhale
A malware analysis and classification tool.
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool

 psypanda/hashid
Software to identify the different types of hashes -
 jessek/hashdeep
Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 ciscocxsecurity/creddump7
Offline Windows credential extractor that dumps LM/NT hashes, cached domain passwords, and LSA secrets from registry hives without relying on system…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
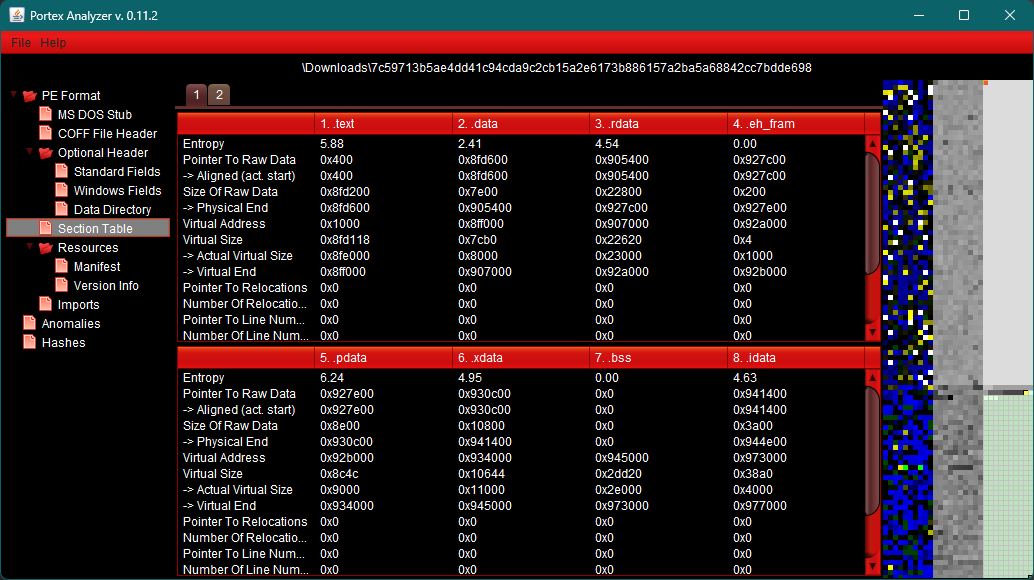 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 neorai/vt-py-scanner
Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…
 g4sp4rcs/cve-2023-32784-password-combinator-fixer
After using the KeePass password dumper maybe some character parsed as ● is incorrect and you want to know the real character
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…