
pyshark
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
digital-forensicsencryption-decryption-toolsforensics+5
2.5k6 months ago
kiminewt/pysharkPython wrapper for tshark, allowing python packet parsing using wireshark dissectors
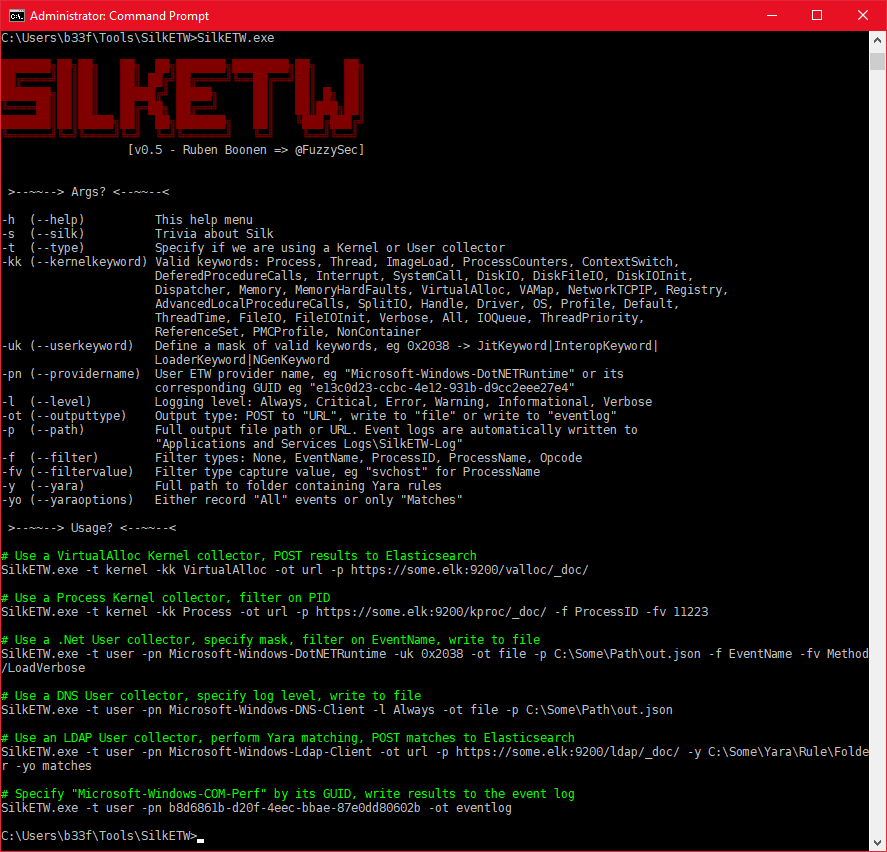 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
 zerkereod/krakenhashes
Distributed password cracking platform coordinating GPU/CPU agents via Hashcat for high-speed hash recovery, with real-time job management,…