
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
83 results
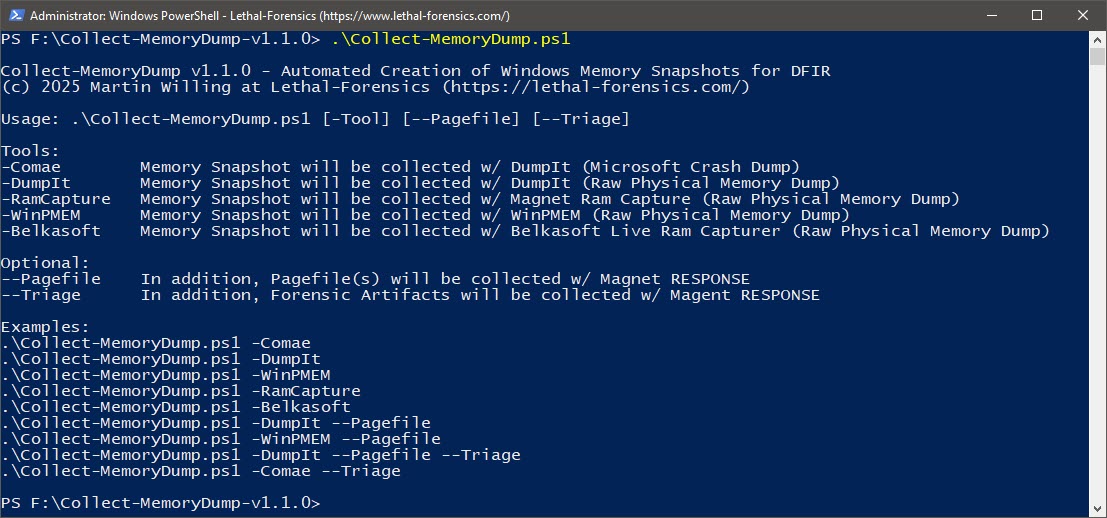
Trawler preview

Trawler

GitHubjoeavanzato/trawler

PowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
defensive-toolsdigital-forensicsforensics+2
3401 year ago
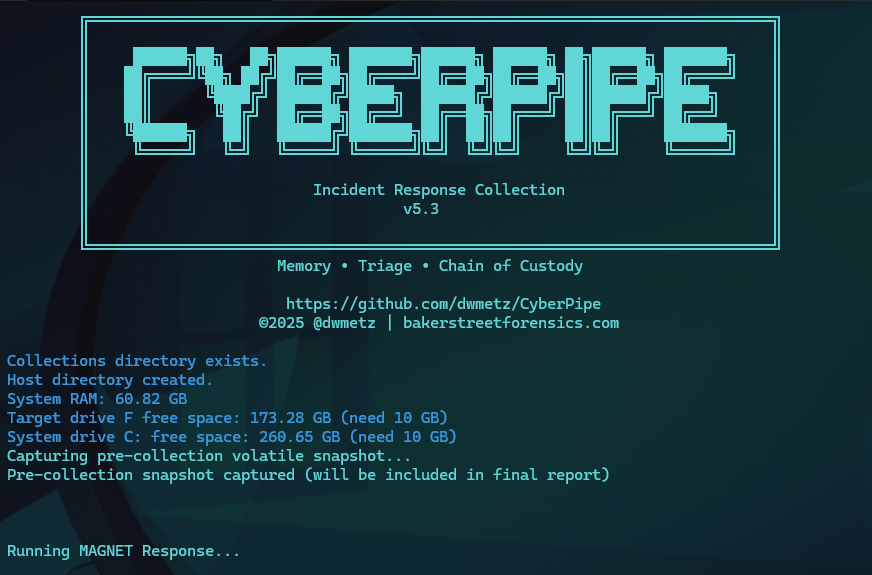
Collect-MemoryDump preview

Collect-MemoryDump

GitHublethal-forensics/collect-memorydump

Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…
digital-forensicsforensicsincident-response+1
2651 year ago
CyberPipe preview

CyberPipe

GitHubdwmetz/cyberpipe

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
digital-forensicsdisk-forensicsforensics+2
34311 months ago
Invoke-DumpMDEConfig preview

Invoke-DumpMDEConfig

GitHubblacksnufkin/invoke-dumpmdeconfig

PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
configuration-auditingdefensive-toolsforensics+3
1552 years ago
FarsightAD preview

FarsightAD

GitHubqazeer/farsightad

PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
forensicsincident-responseinformation-gathering+5
989 months ago
CVE-2020-1472-visualizer preview

CVE-2020-1472-visualizer

GitHubmingchen-script/cve-2020-1472-visualizer

PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…
digital-forensicsforensicsincident-response+2
16 years ago
HAFNIUM-IOC preview
Archived

HAFNIUM-IOC

GitHubsoteria-security/hafnium-ioc

A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
digital-forensicsforensicsincident-response+3
225 years ago
Douglas-042 preview

Douglas-042

GitHubemrekybs/douglas-042

Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…

forensicsincident-responseinformation-gathering+1
442 months ago
proxynotshell-IOC-Checker preview

proxynotshell-IOC-Checker

GitHubrjsudlow/proxynotshell-ioc-checker

Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)
forensicsincident-responseioc-management+3
54 years ago
CVE-2022-47966_checker preview

CVE-2022-47966_checker

GitHubace-responder/cve-2022-47966_checker

Run on your ManageEngine server

forensicsincident-responseioc-management+3
23 years ago
SharePointSecurityMonitor preview

SharePointSecurityMonitor

GitHubpaolokappa/sharepointsecuritymonitor

A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…

cloud-securityconfiguration-auditingforensics+8
11 year ago
ToolShellFinder preview

ToolShellFinder

GitHubzach115th/toolshellfinder

Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
digital-forensicsforensicsincident-response+5
11 months ago
NorkNork preview

NorkNork

GitHubn00py/norknork

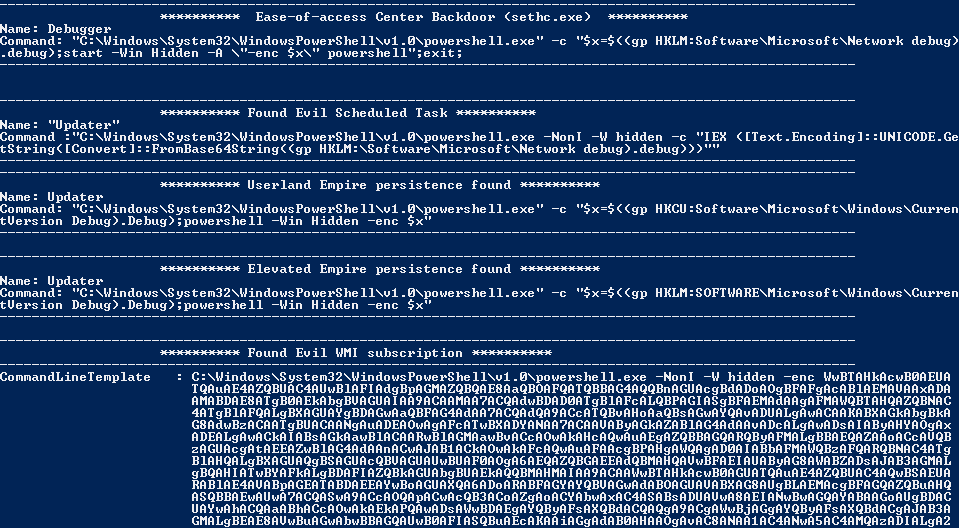
Powershell Empire Persistence finder
defensive-toolsforensicsincident-response+2
1189 years ago
PowerShell-Suite preview

PowerShell-Suite

GitHubfuzzysecurity/powershell-suite

My musings with PowerShell

binary-analysisdebuggersforensics+5
2.7k4 years ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
8075 months ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
digital-forensicsforensicsincident-response+3
1.4k1 month ago
python-exe-unpacker preview

python-exe-unpacker

GitHubwithsecurelabs/python-exe-unpacker

A helper script for unpacking and decompiling EXEs compiled from python code.

binary-analysisdynamic-analysis-sandboxingforensics+2
1.0k8 years ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

digital-forensicsdisk-forensicsforensics+6
4895 years ago
Previous12345Next