

Process-Dump
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k1 month ago
glmcdona/process-dumpWindows tool for dumping malware PE files from memory back to disk for analysis.
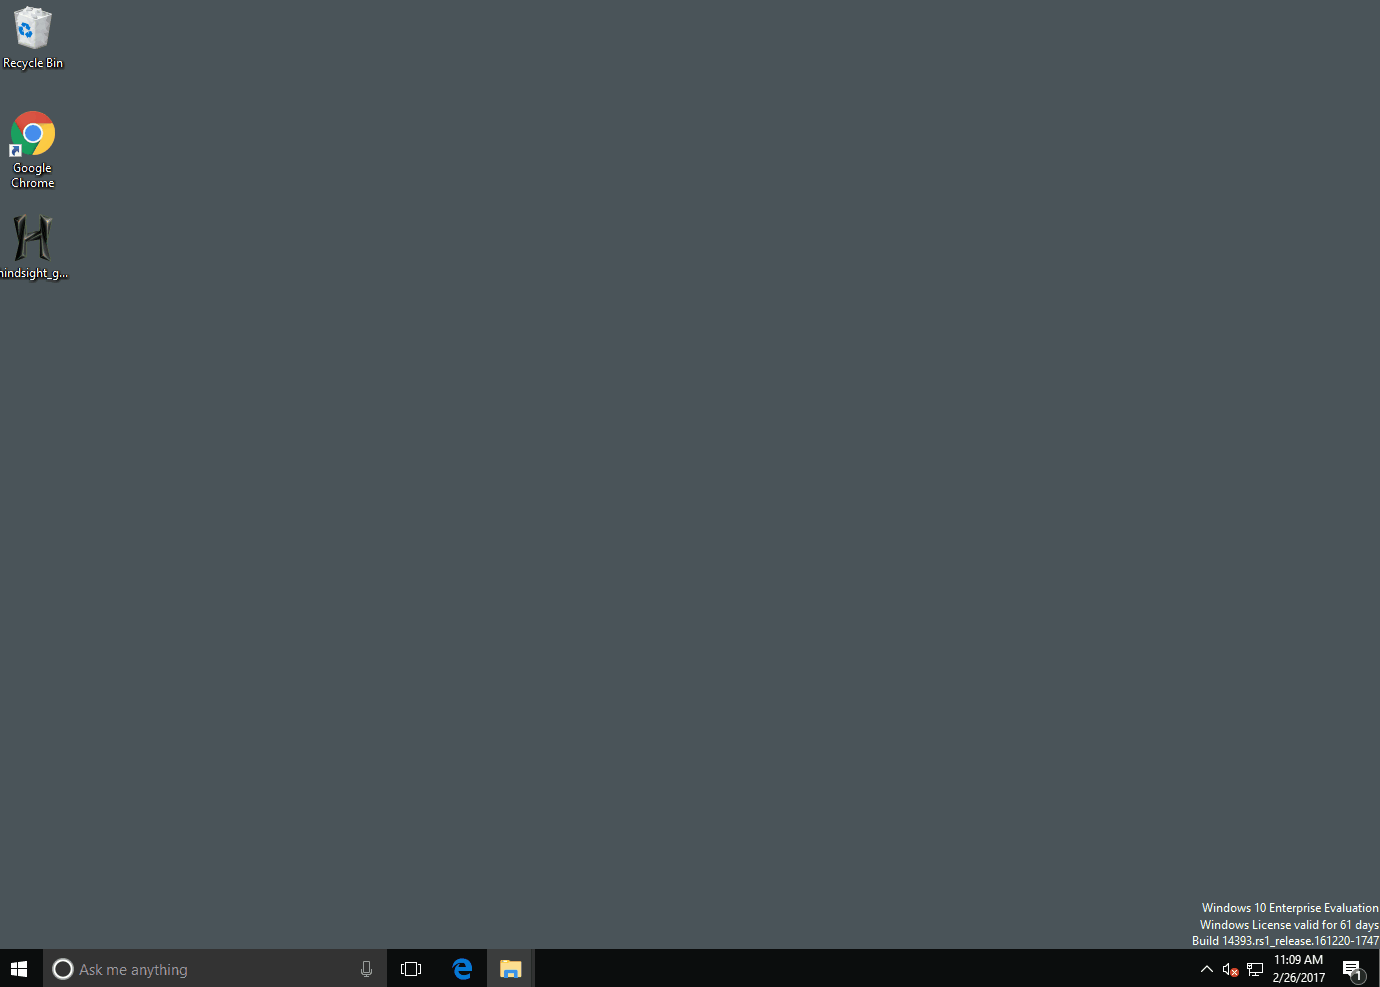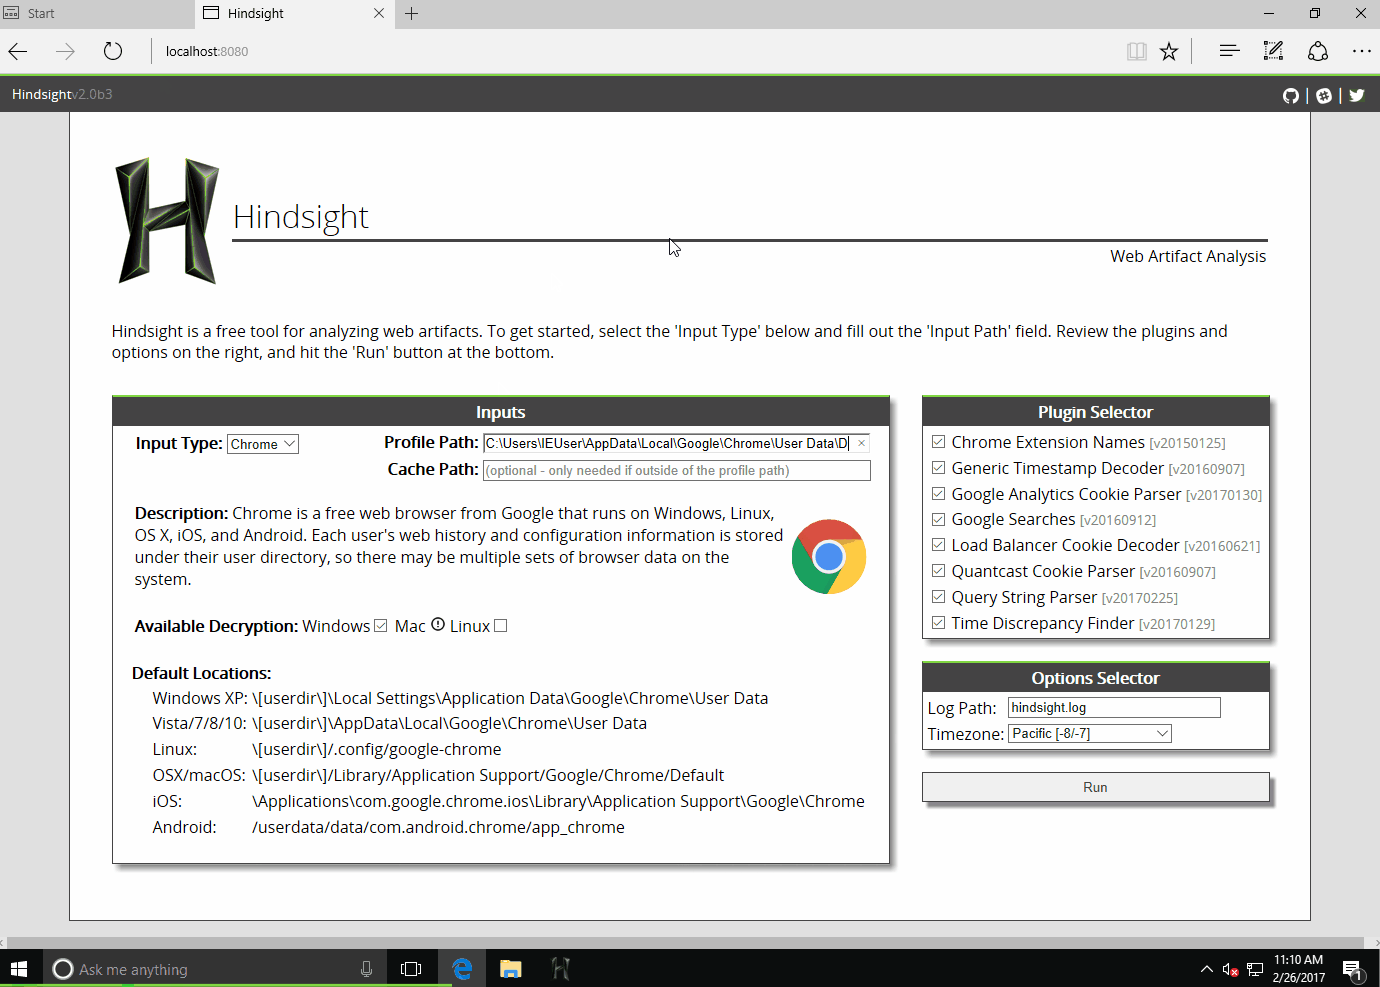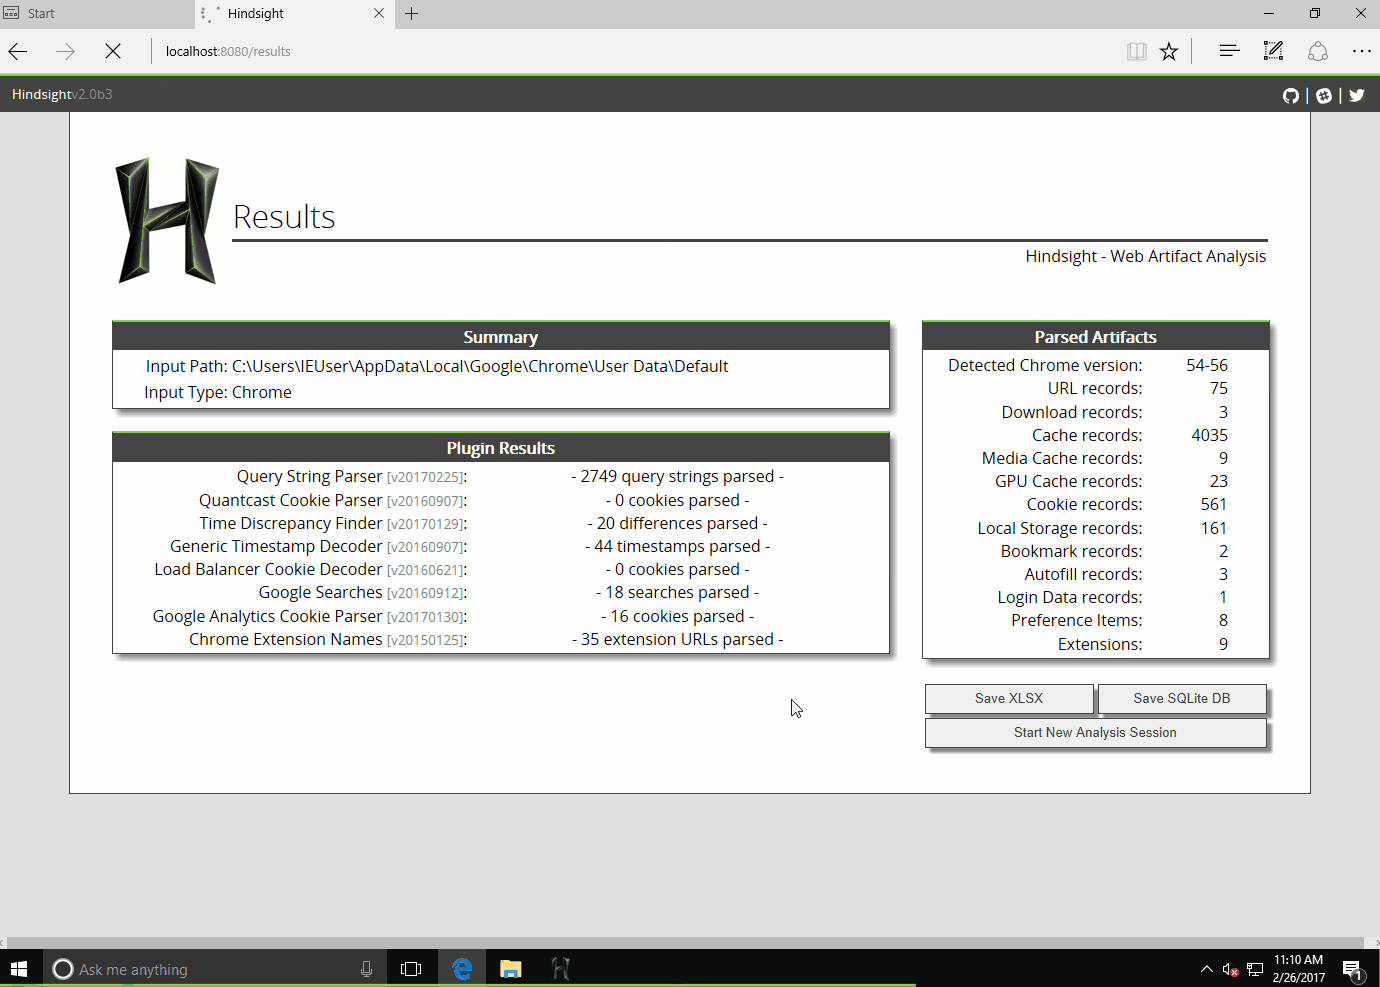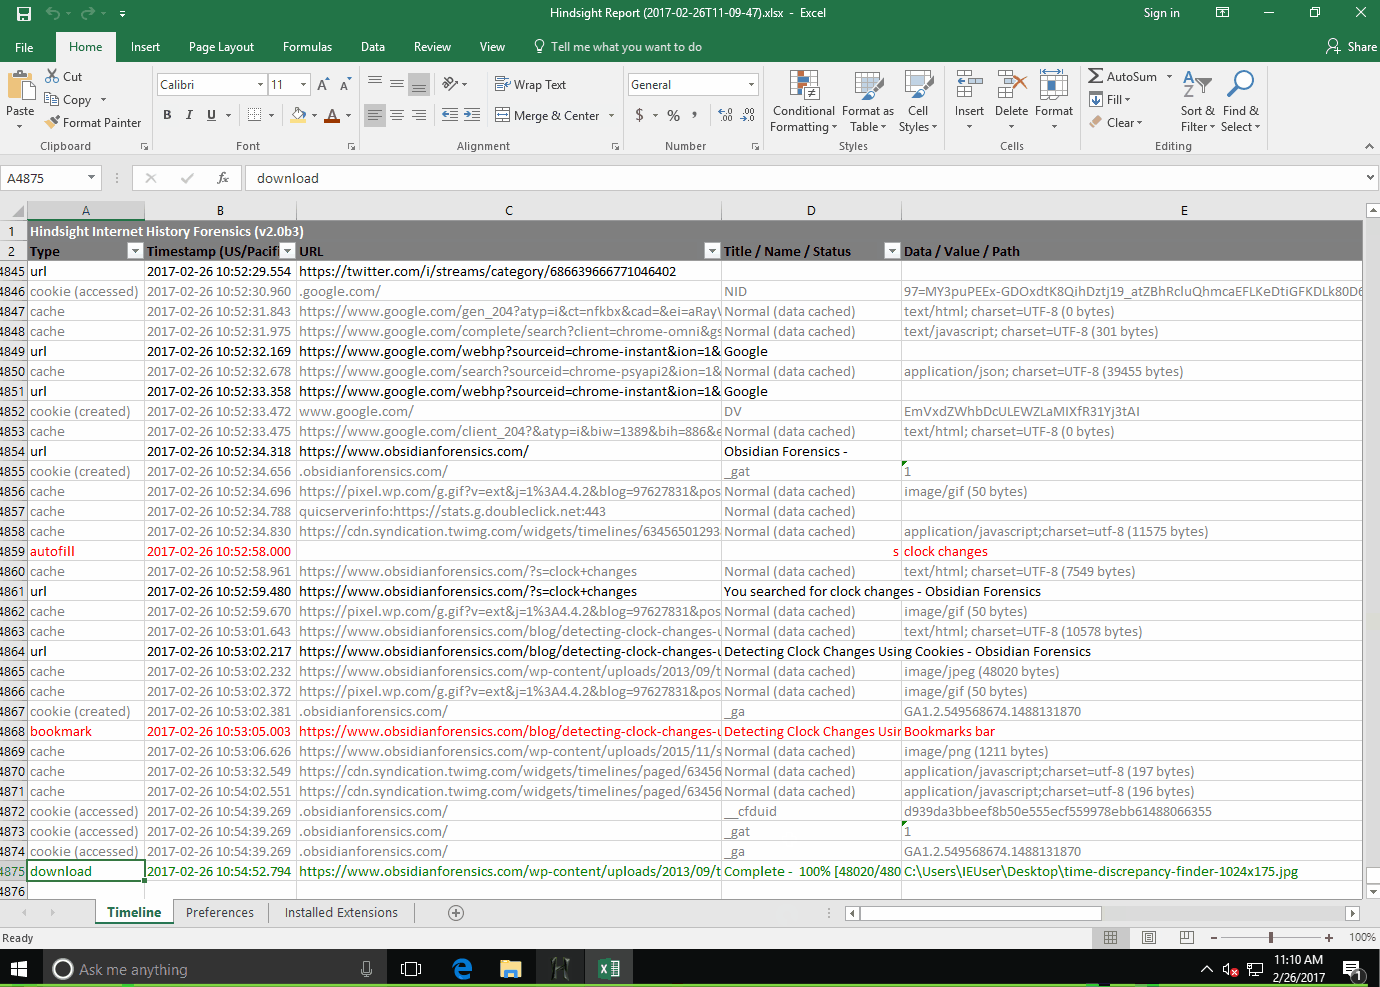 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox
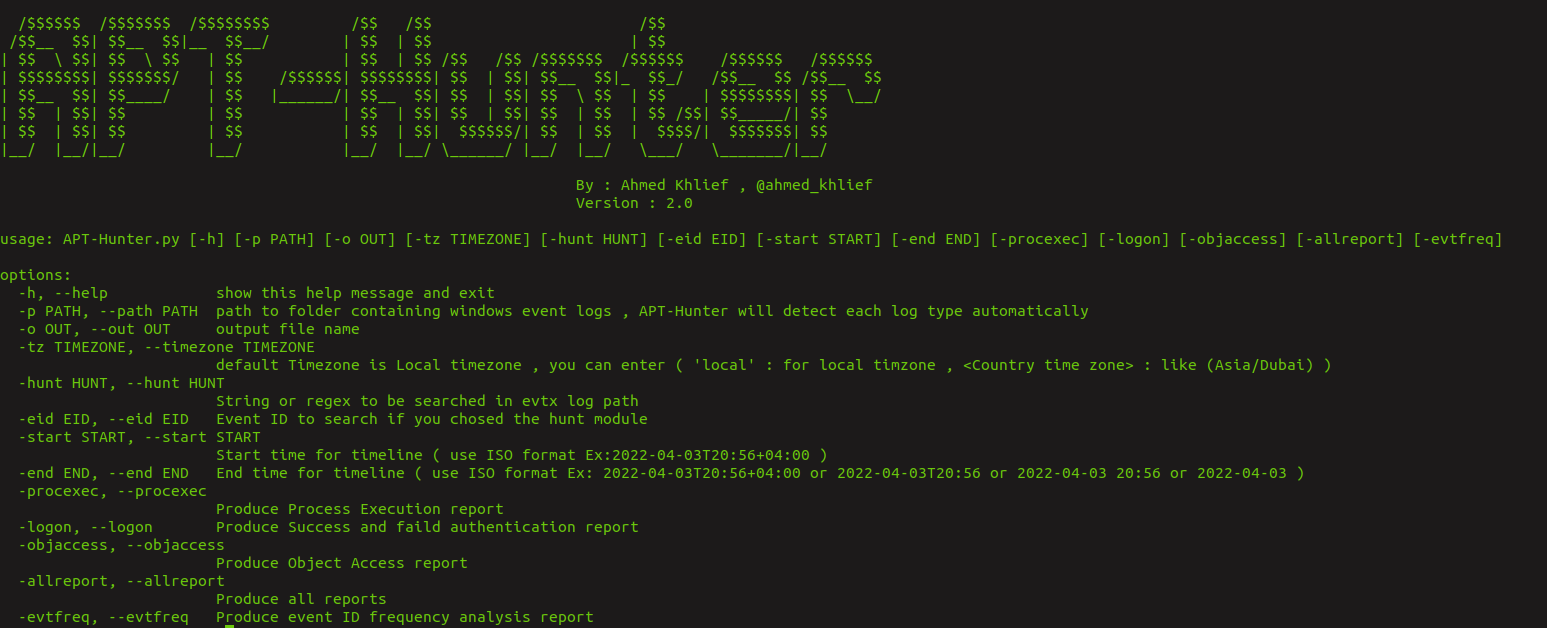 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 capacitorset/box-js
A tool for studying JavaScript malware.
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
 lazza/recuperabit
A tool for forensic file system reconstruction.
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
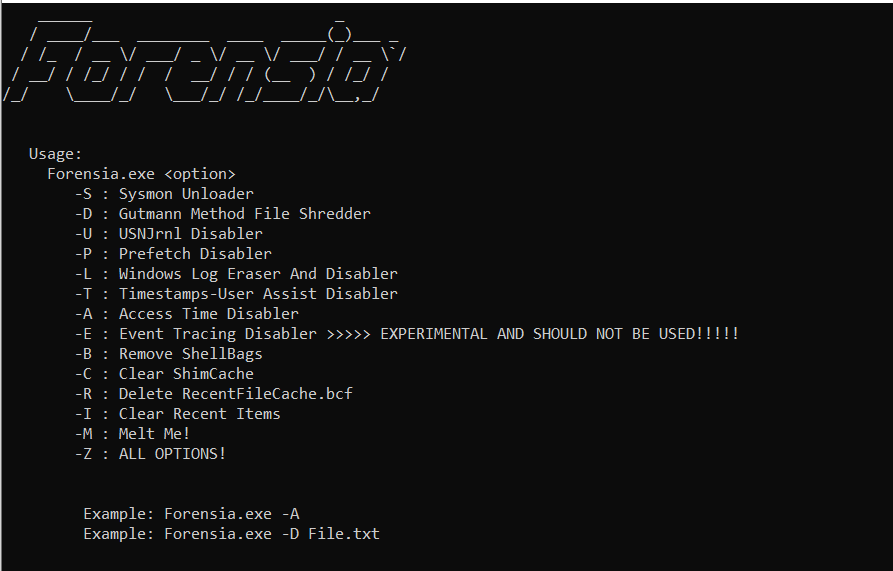 paulnorman01/forensia
Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 themittenmac/truetree
A command line tool for pstree-like output on macOS with additional pid capturing capabilities
 guibacellar/tex
Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark