

Malware-Exhibit
 alvin-tosh/malware-exhibit
🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈,…
cryptographycurated-resourceseducation+3
1.2k
alvin-tosh/malware-exhibit🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈,…
 aquasecurity/tracee
Linux Runtime Security and Forensics using eBPF
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 thirdbyte/ssj
Your everyday Linux distribution gone Super Saiyan.
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 maliceio/malice
VirusTotal Wanna Be - Now with 100% more Hipster
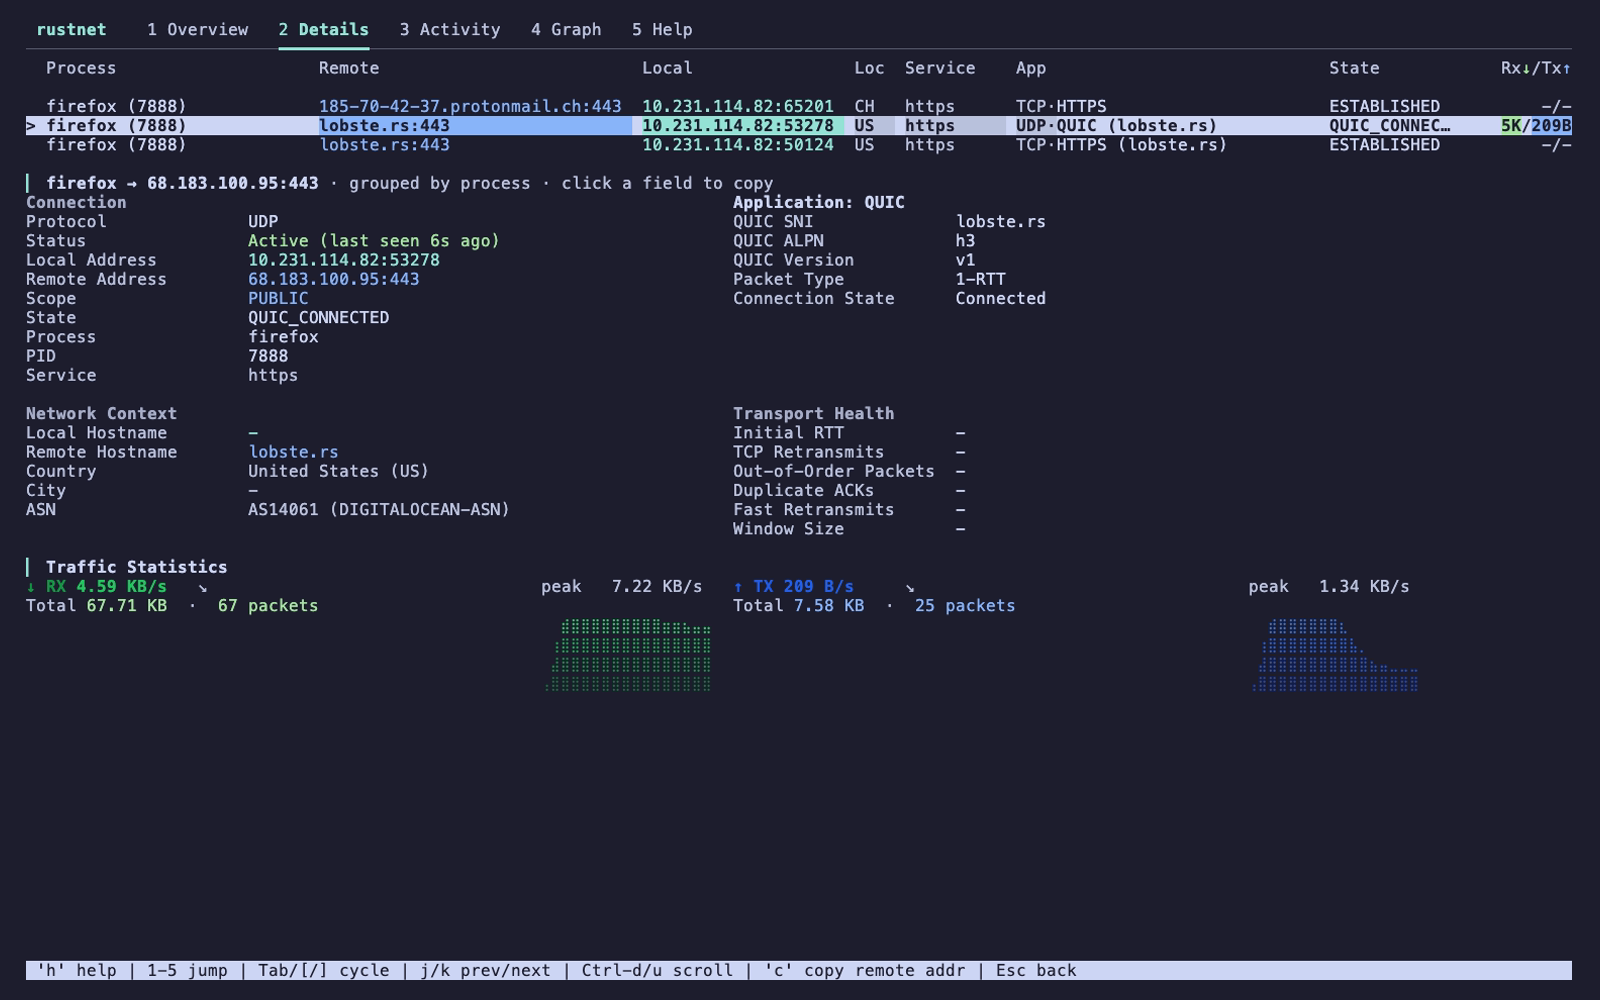 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 target/strelka
Real-time, container-based file scanning at enterprise scale
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
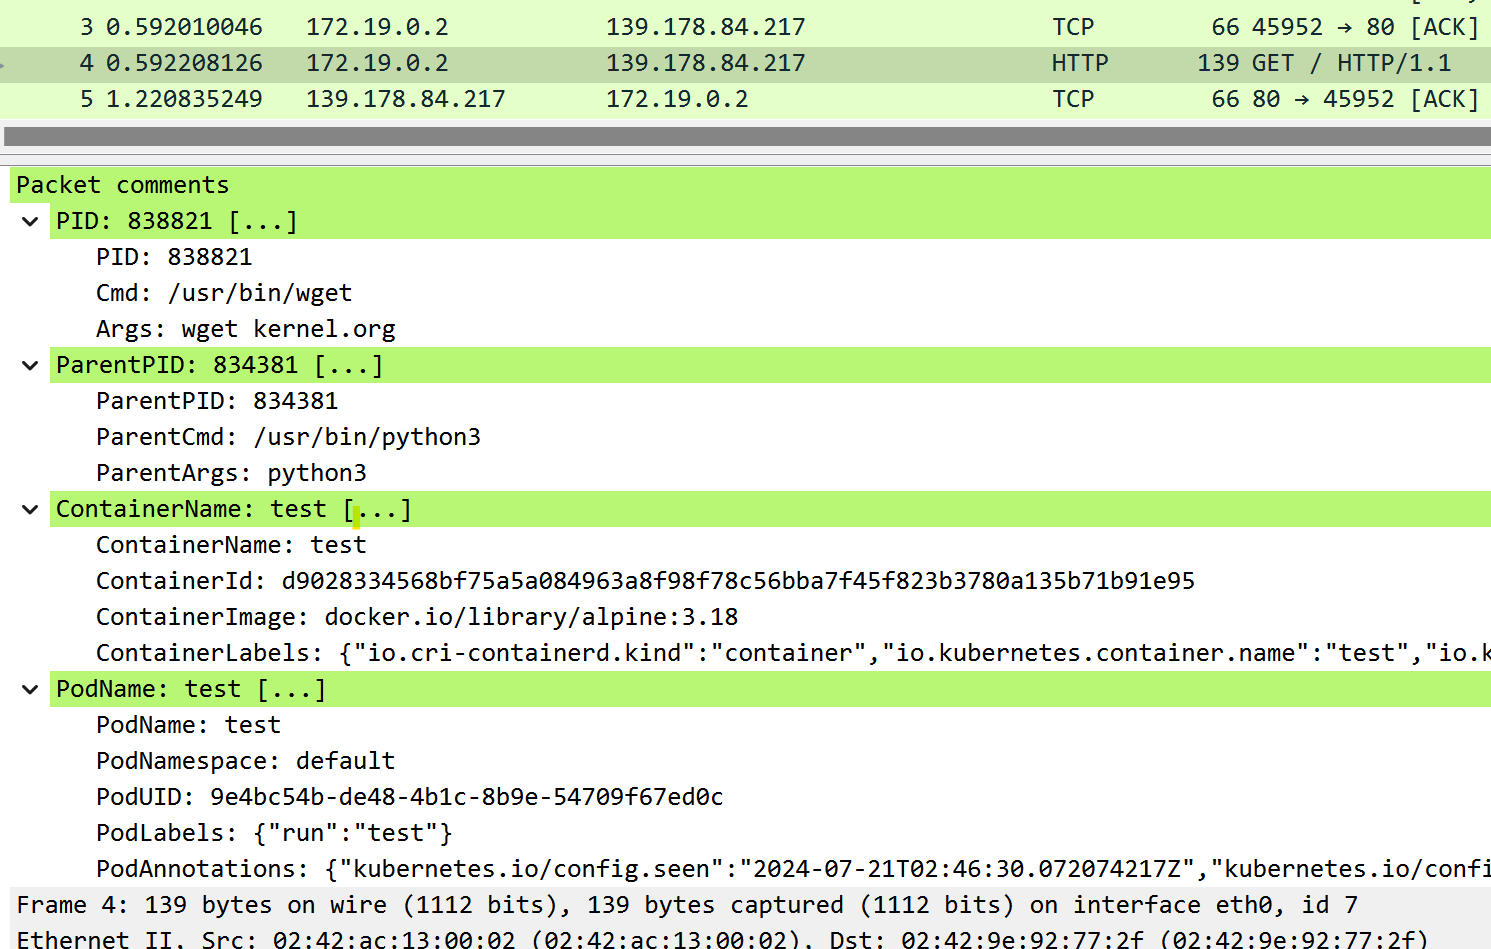 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 loresuso/psc
the ps utility, with an eBPF twist and container context
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 tangjie1/cve-2026-31431-check
CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script