
whids
 0xrawsec/whids
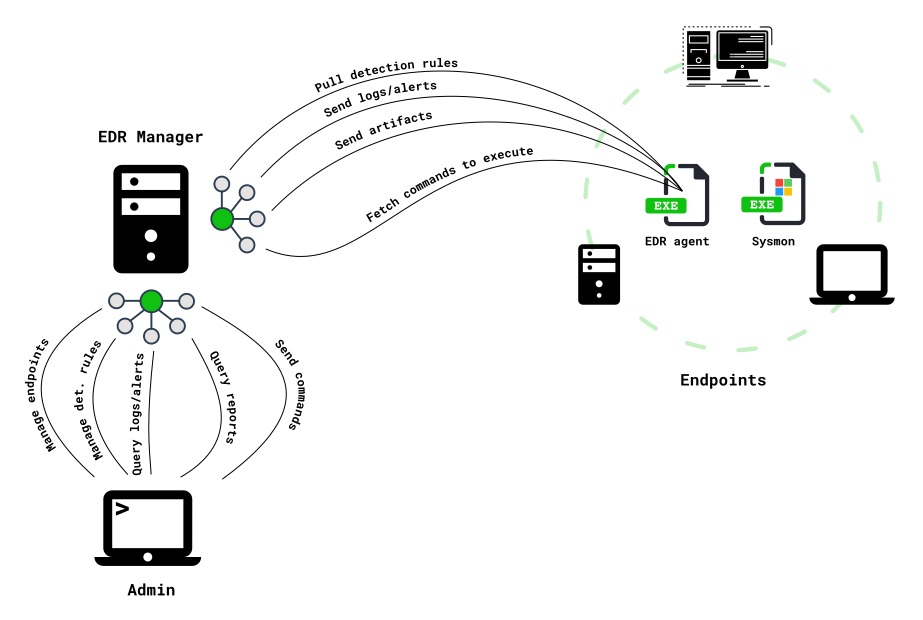
Windows EDR with Gene-based detection engine, real-time artifact collection, Sysmon integration, and REST API for managing endpoints, rules, and…
forensicsincident-response
0xrawsec/whidsWindows EDR with Gene-based detection engine, real-time artifact collection, Sysmon integration, and REST API for managing endpoints, rules, and…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 malwaretech/phasedump
Python tool for decrypting W32/Phase modules
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…