
xz-cve-2024-3094
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
digital-forensicseducationforensics+6
hackura/xz-cve-2024-3094Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
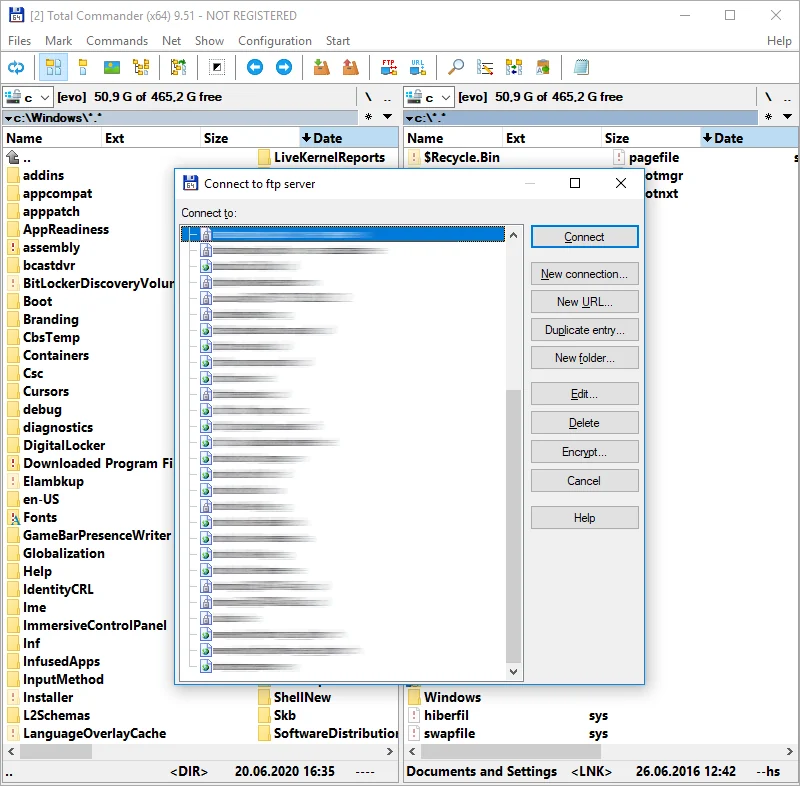 pelock/total-commander-ftp-password-recovery-tool-python
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…
 eonraider/violent-python3
Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 eurecom-s3/linux_screenshot_xwindows
Volatility plugin to extract X screenshots from a memory dump
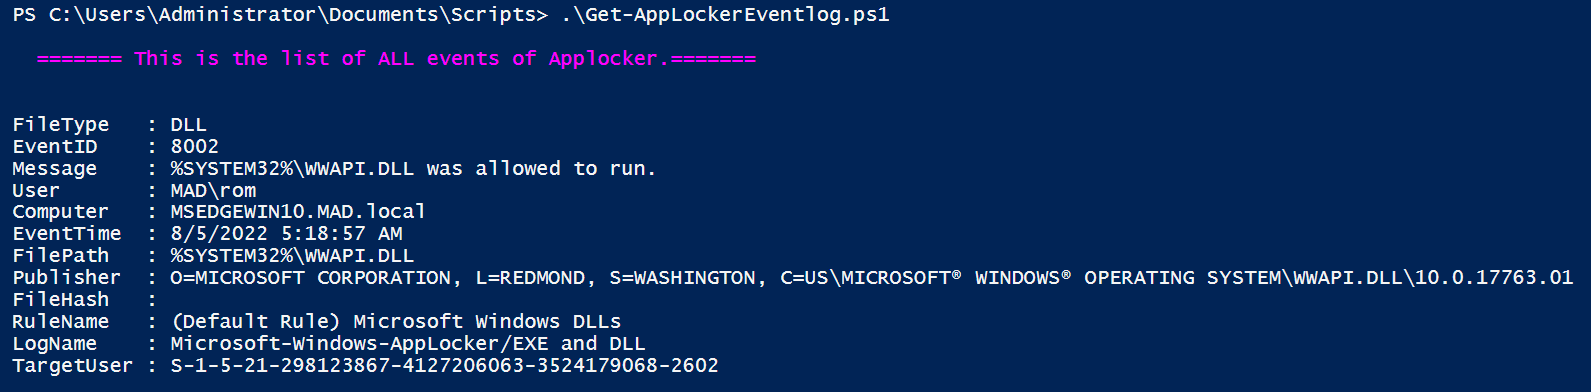 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
 soteria-security/hafnium-ioc
A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
 mubix/cve-2021-44228-log4shell-hashes
Hashes for vulnerable LOG4J versions
 paul-tew/lifer
Windows link file (shortcuts) examiner
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 acinq/detection-tool-cve-2019-13000
A tool that detect if your node has been victim of the invalid funding tx attack.
 adulau/the-art-of-pivoting
The Art of Pivoting - Techniques for Intelligence Analysts to Discover New Relationships in a Complex World
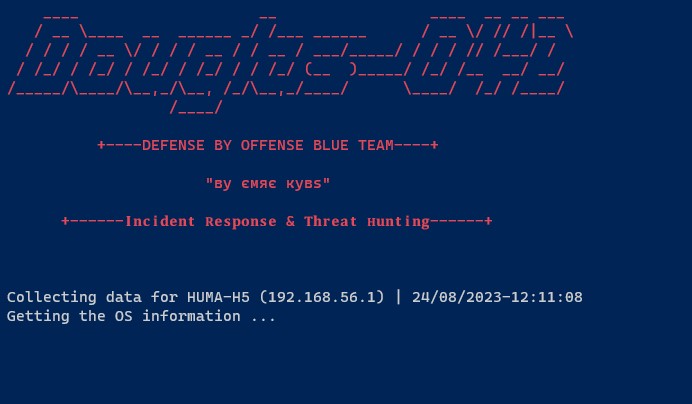 emrekybs/douglas-042
Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…
 jumpseclabs/printnightmare
Information on the Windows Spooler vulnerability - CVE-2021-1675; CVE 2021 34527
 airbus-cert/cve-2025-24985
Detection of malicious VHD files for CVE-2025-24985