
DFIR-O365RC
 anssi-fr/dfir-o365rc
PowerShell module for Office 365 and Azure log collection
cloud-securitydigital-forensicsforensics+2
anssi-fr/dfir-o365rcPowerShell module for Office 365 and Azure log collection
 cybermaggedon/cyberprobe
Capturing, analysing and responding to cyber attacks
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 marcog3/whatsdump
Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
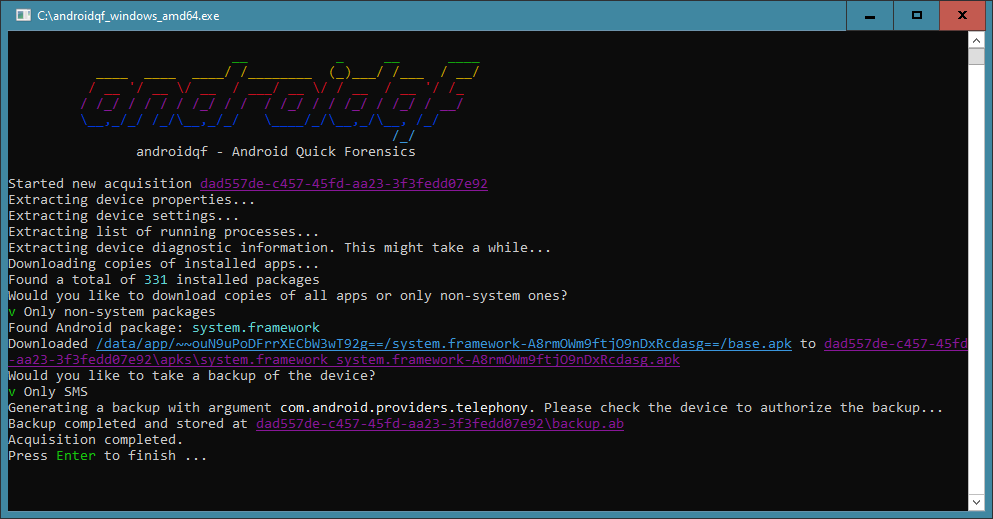 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 realitynet/ios_triage
Bash script to extract data from a "chekcra1ned" iOS device
 packetlss/android-locdump
android location service cache dumper
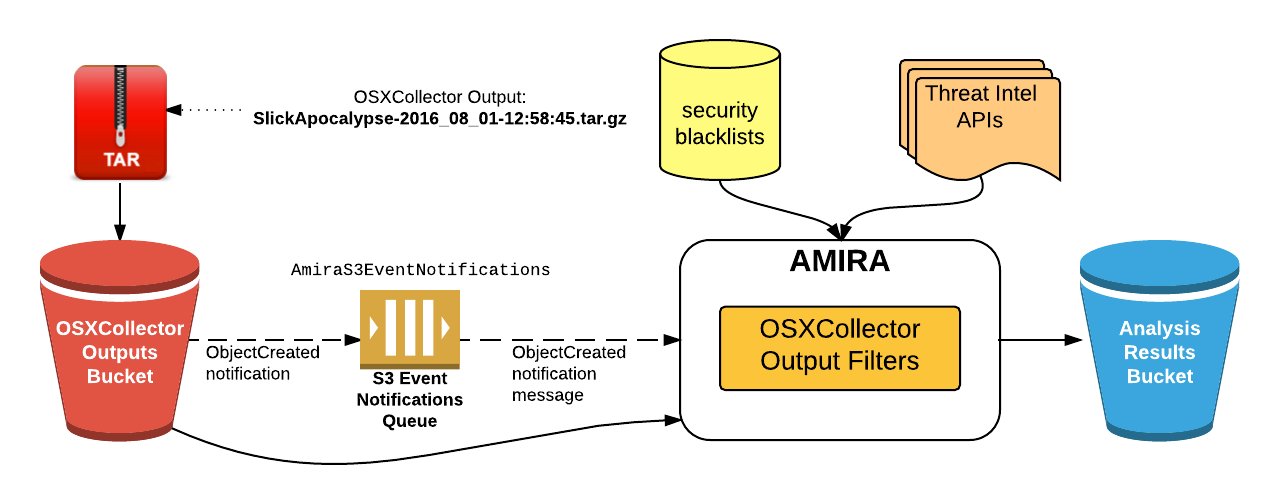 yelp/amira
AMIRA: Automated Malware Incident Response & Analysis
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 0x48piraj/incarcero
Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
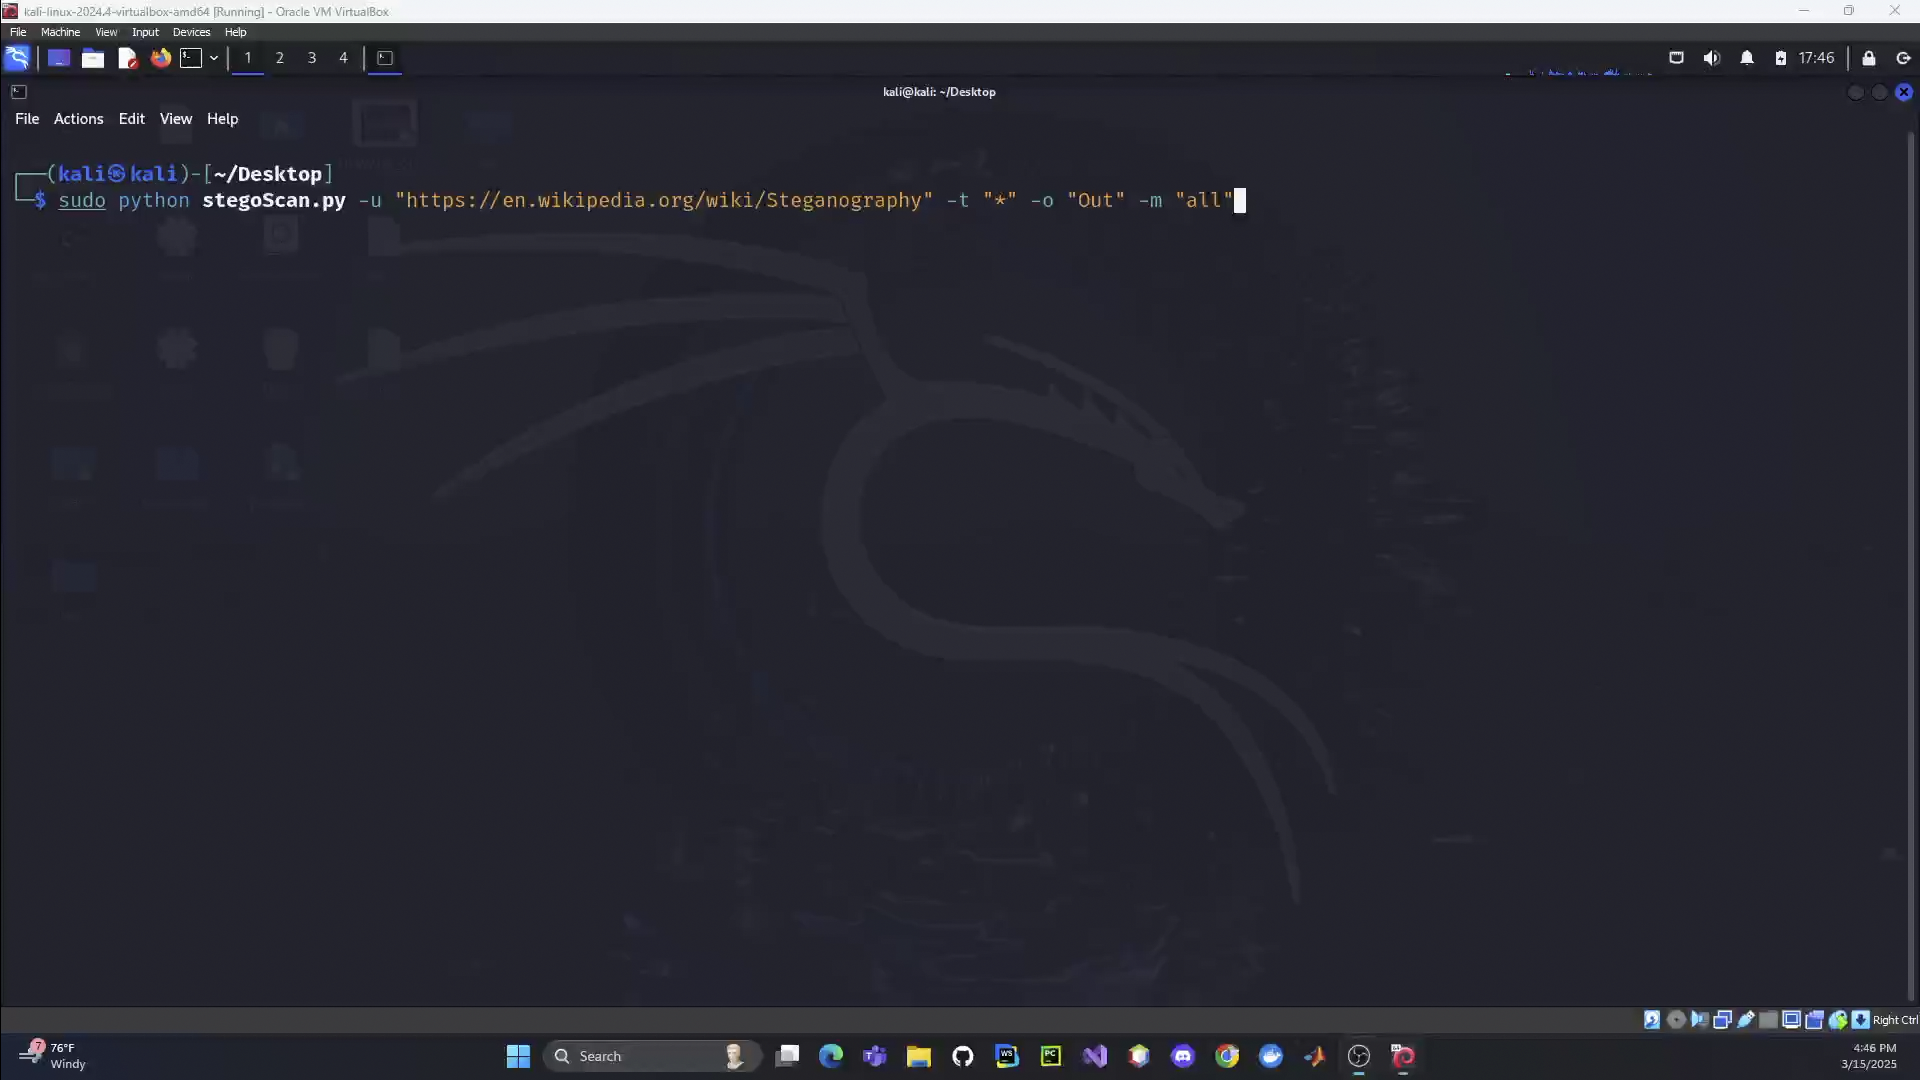 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices