
pcapinator
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
forensicsinformation-gatheringnetwork-forensics+2
mspicer/pcapinatorA tool for processing a lot of pcaps using tshark
 krisnova/xpid
Linux Process Discovery. C Library, Go bindings, Runtime.
 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.
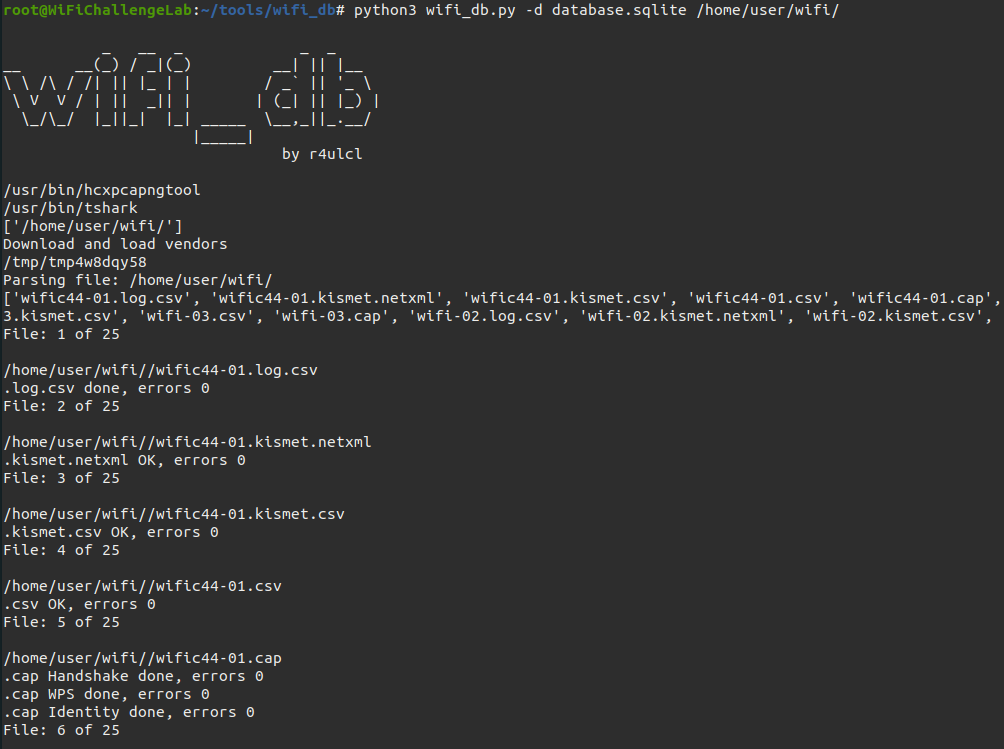 r4ulcl/wifi_db
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations…
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 scalabli/sashay
Sashay is an automatic installer for useful tools.
 emrekybs/douglas-042
Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…
 chriswmorris/metaforge
An OSINT Metadata analyzing tool that filters through tags and creates reports
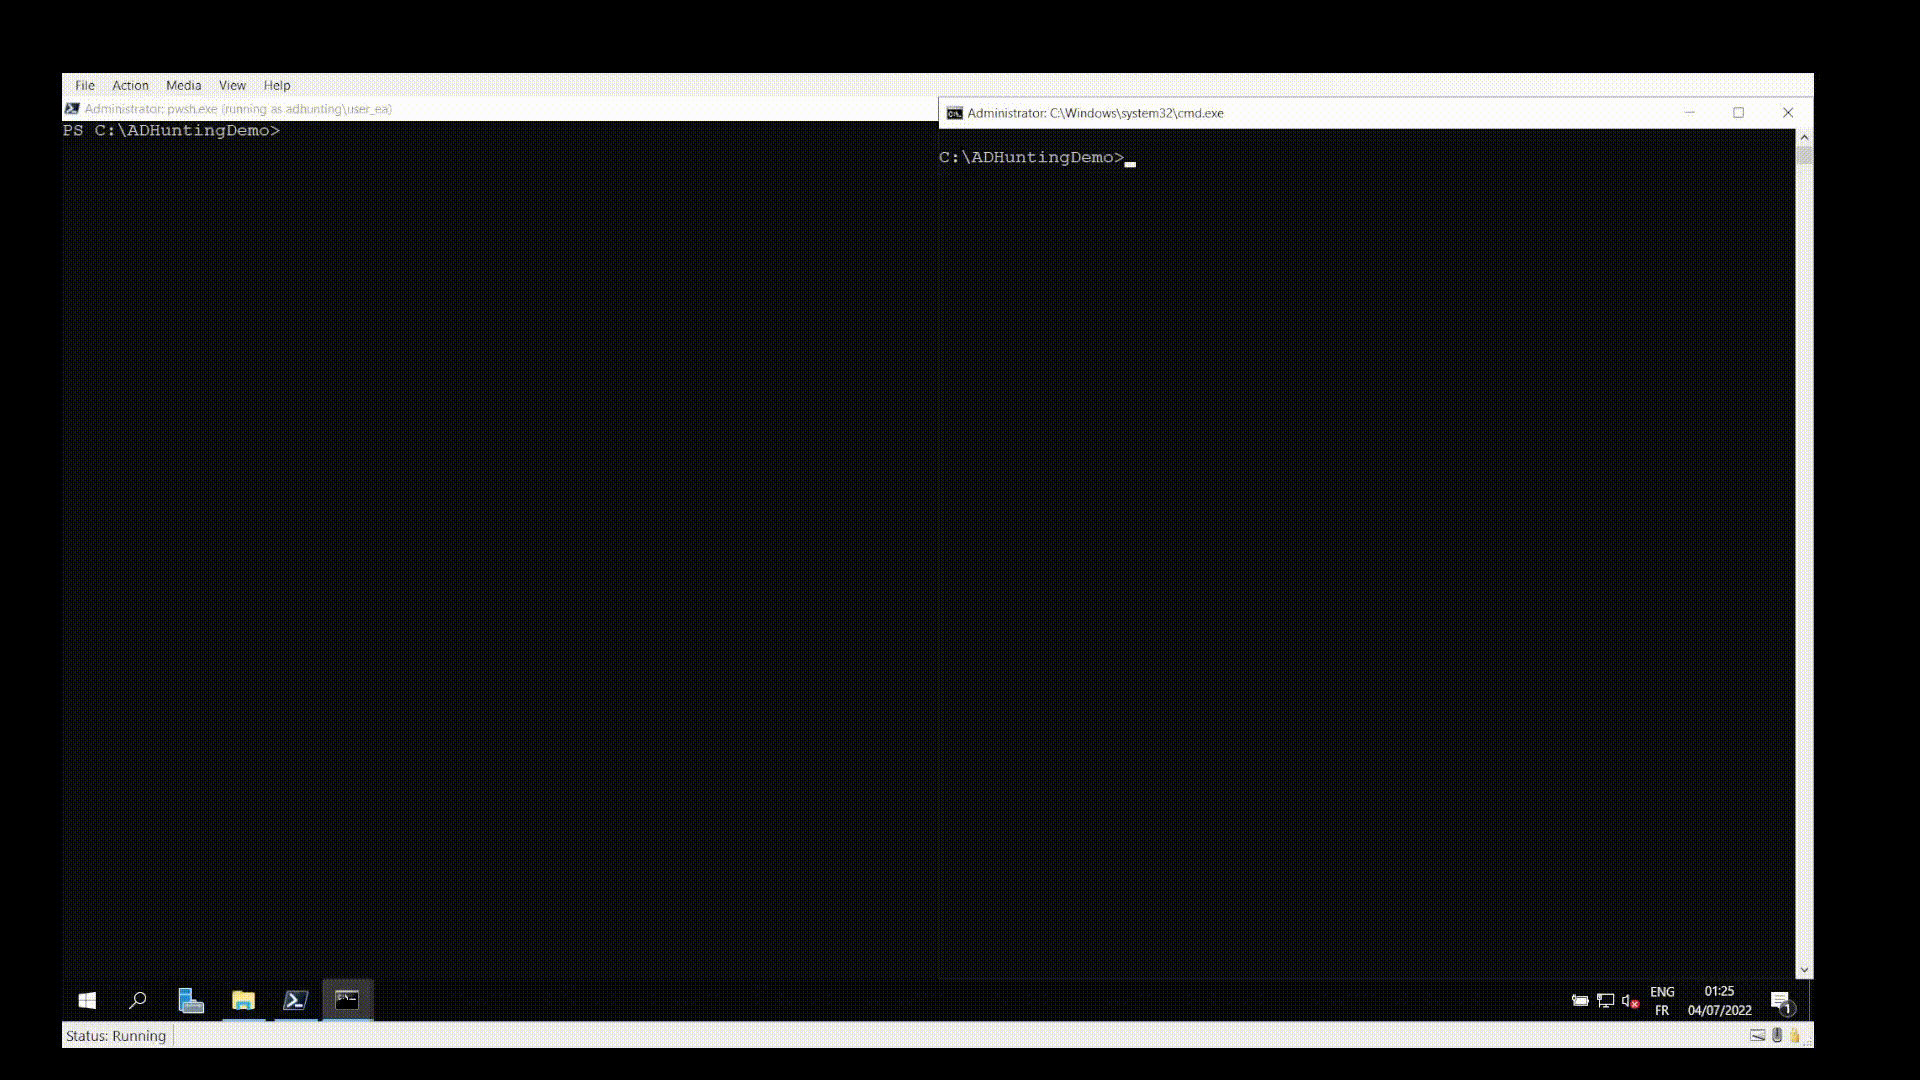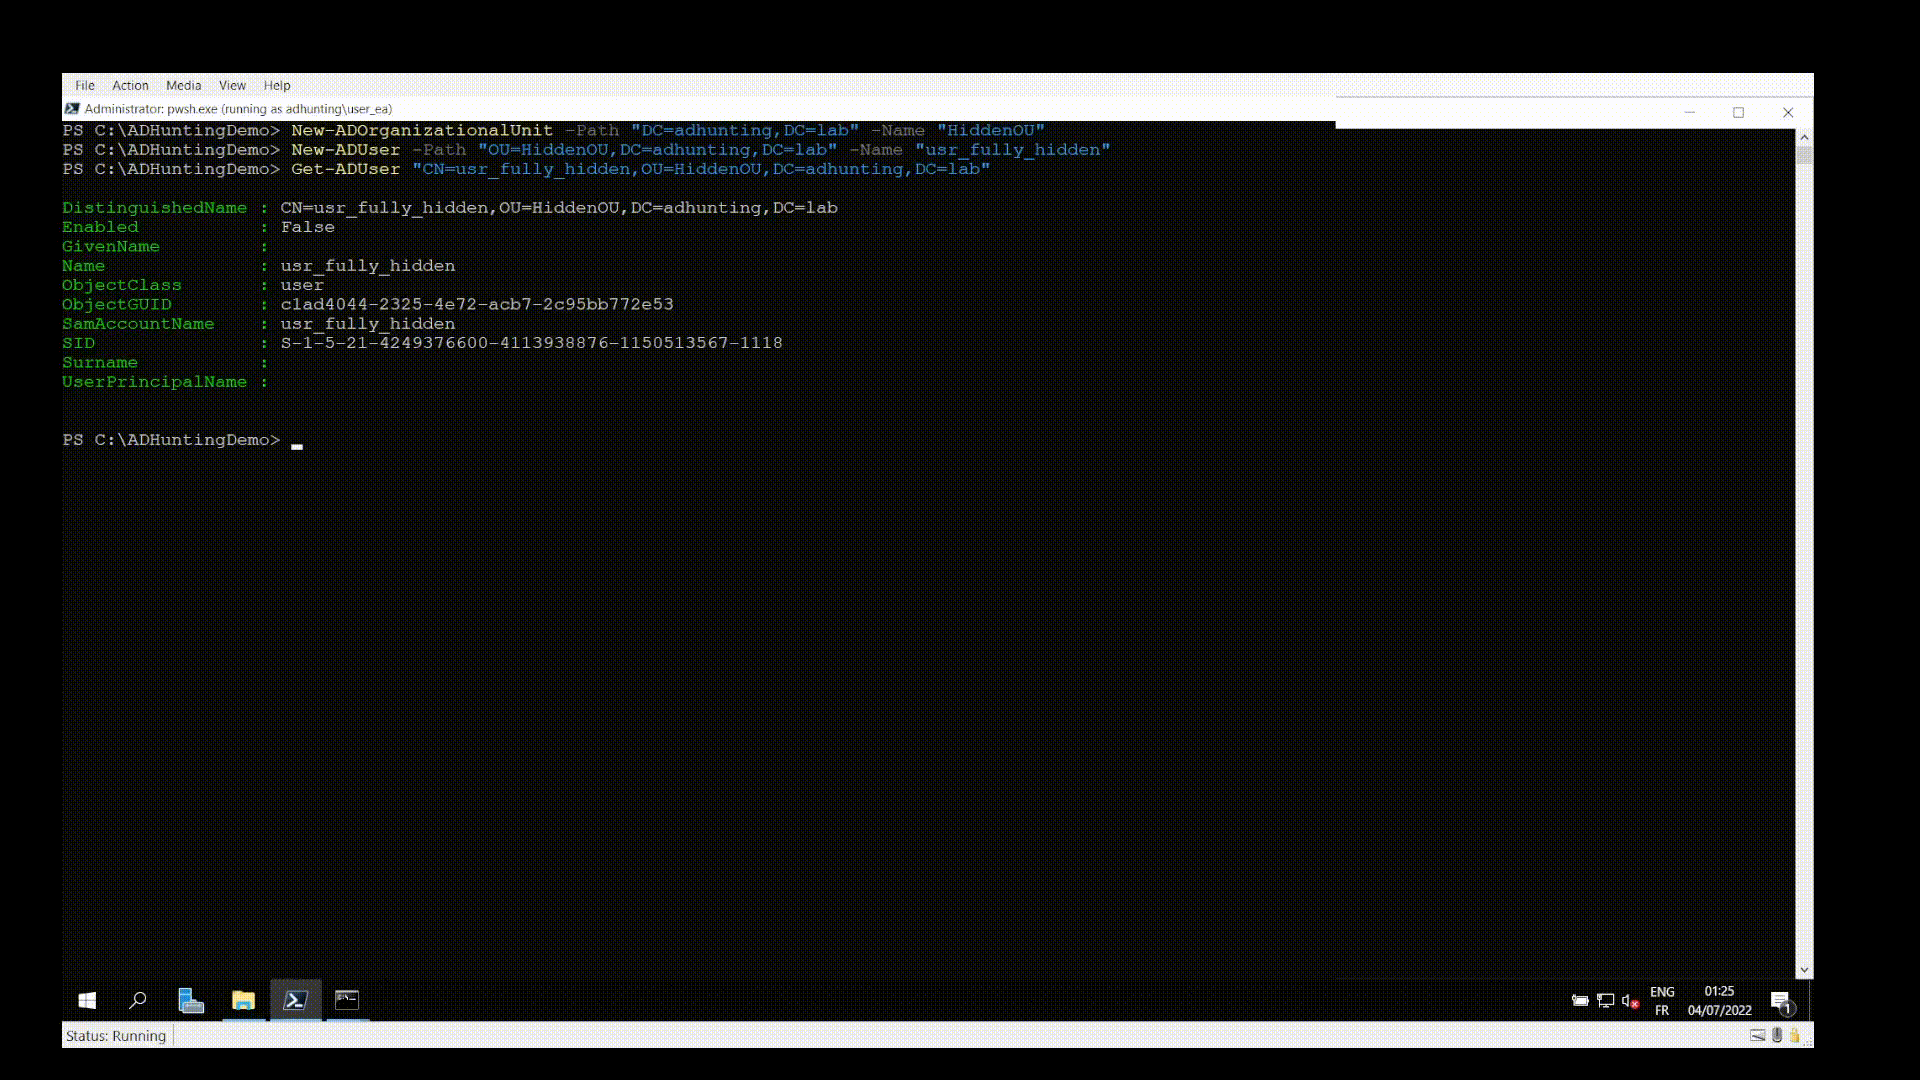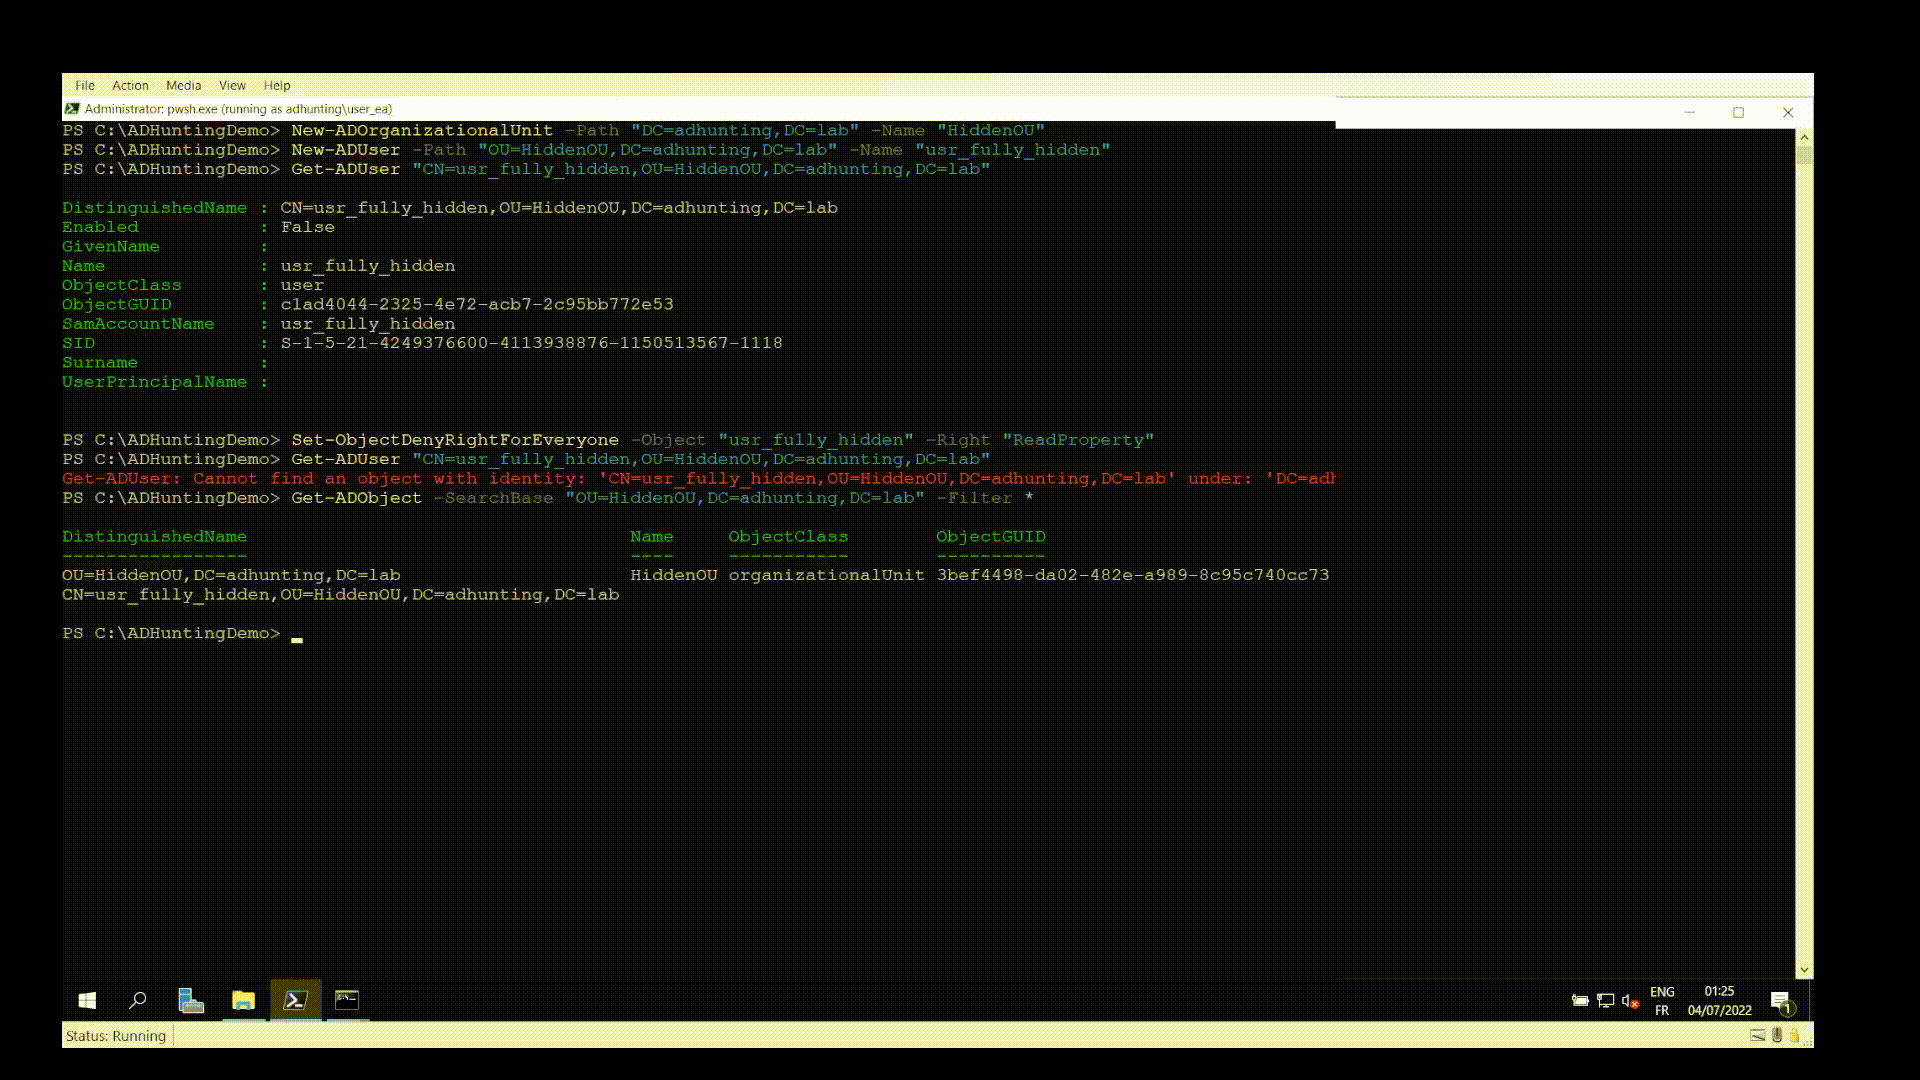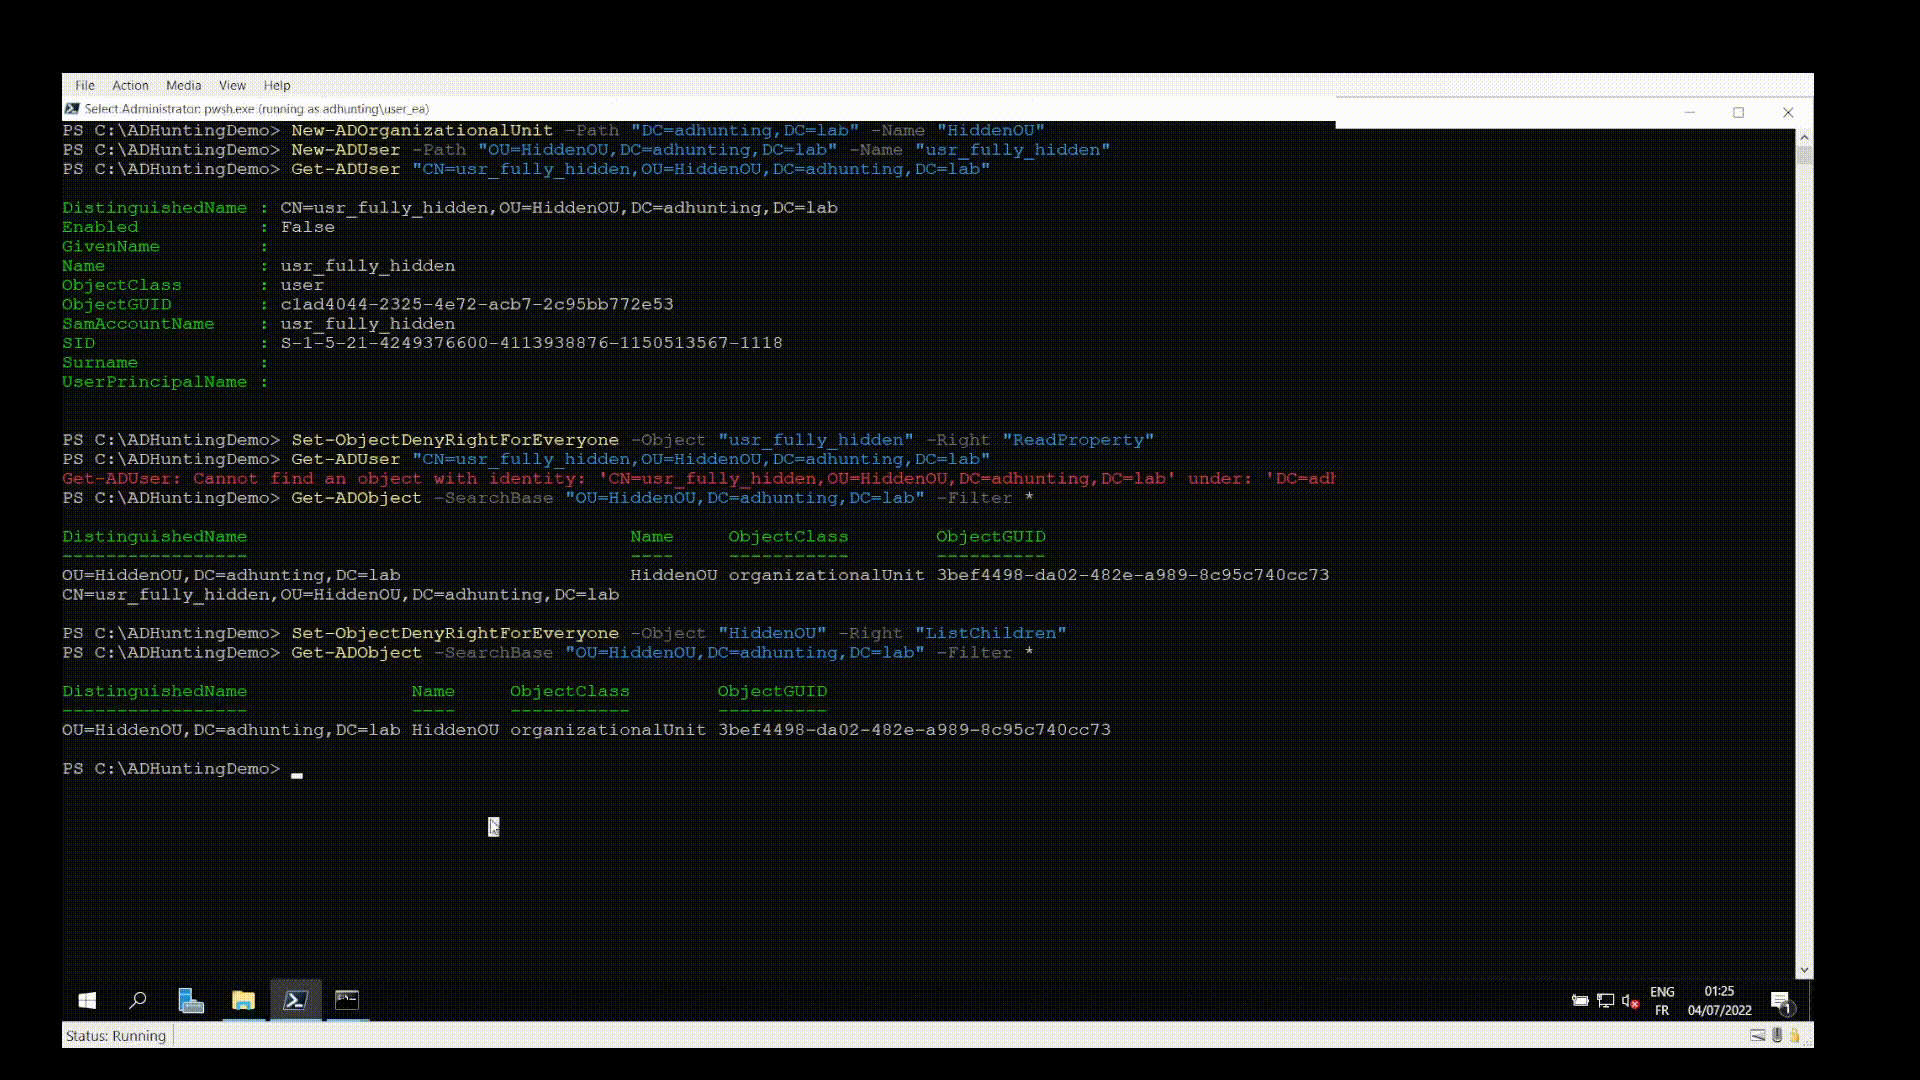 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 puckblush/tofu
Windows offline filesystem hacking tool for Linux
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
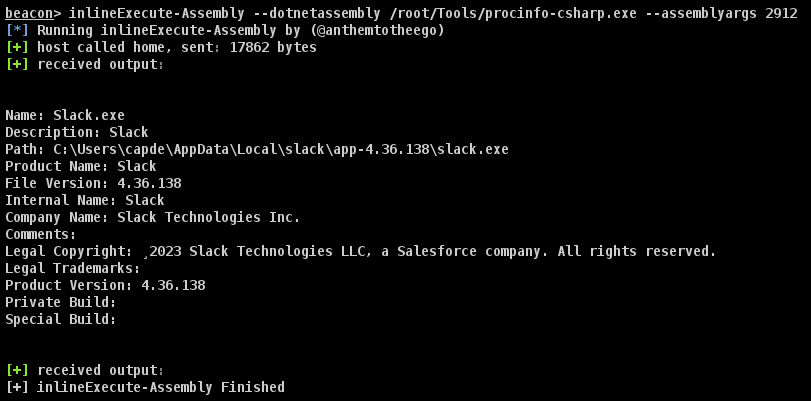 mlcsec/proctools
Small toolkit for extracting information and dumping sensitive strings from Windows processes
 lgggreg/skype-log-viewer
Download and View Skype History Without Skype
 paul-tew/lifer
Windows link file (shortcuts) examiner
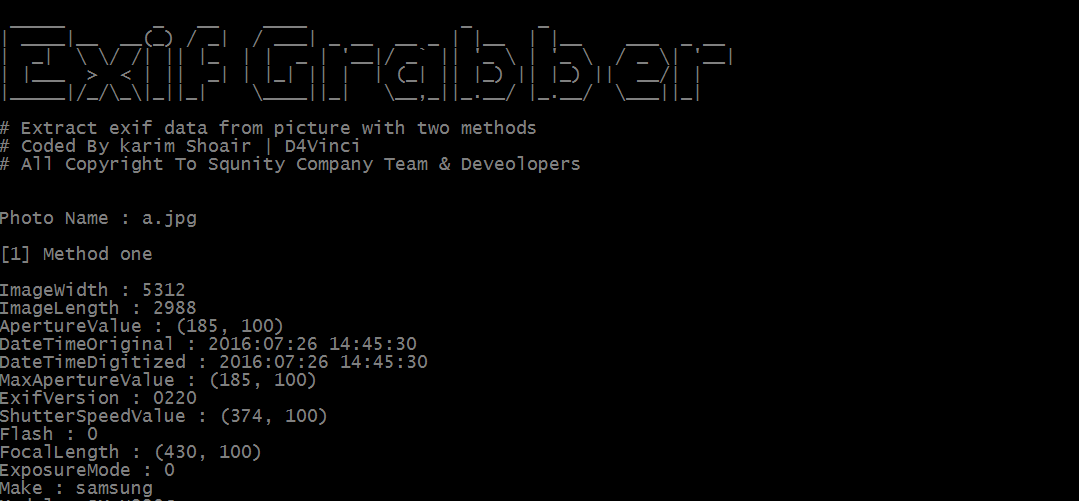 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting