

sorry-ransomware-analysis
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
cryptographydigital-forensicsforensics+4
6
habibkaratas/sorry-ransomware-analysisSorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 mmozeiko/aes-finder
Utility to find AES keys in running processes
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
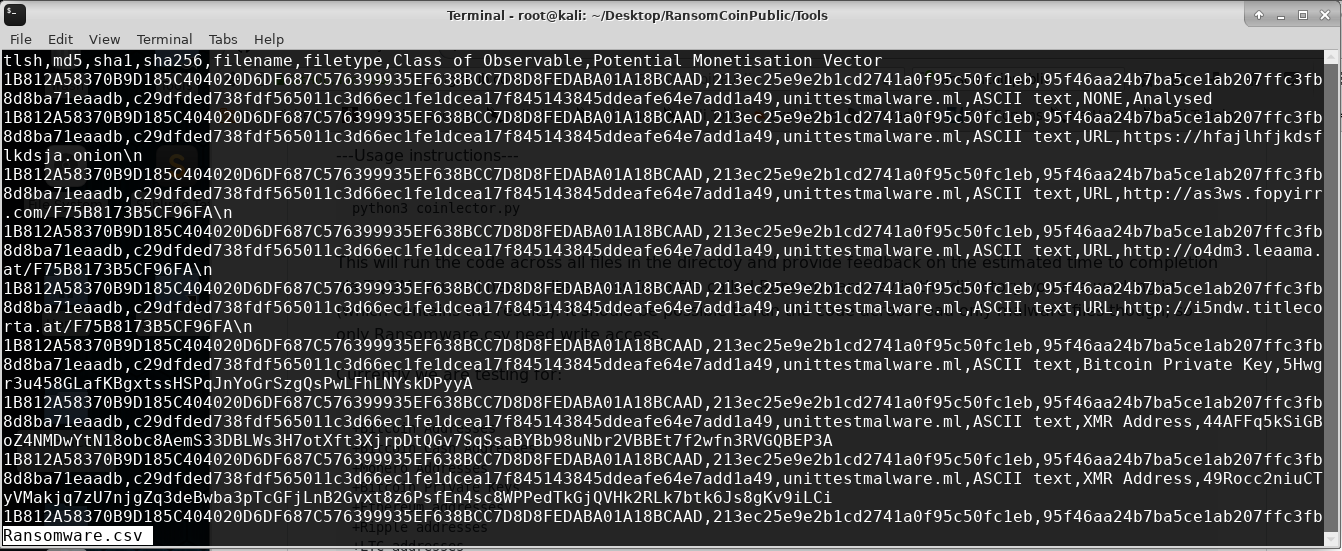 concinnity-risks/ransomcoinpublic
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 233laoliu/mt6985-cve-2026-43499
CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)
 trinadh465/platform_external_gptfdisk_aosp10_r33_cve-2021-0308
Disk partitioning suite for GPT and MBR disks, offering interactive and scriptable tools to create, modify, and repair partition tables, including…
 chipsec/chipsec
Platform Security Assessment Framework
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 iqbaalilmii/acropalypse-reconstructor
A lightweight CLI tool to detect and reconstruct cropped images vulnerable to Acropalypse (CVE-2023-21036 and CVE-2023-28303) written in Python.
 joydragon/detect-cve-2018-20250
Herramienta para revisar si es que un payload tiene componente malicioso de acuerdo a CVE-2018-20250
 mufeedvh/moonwalk
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
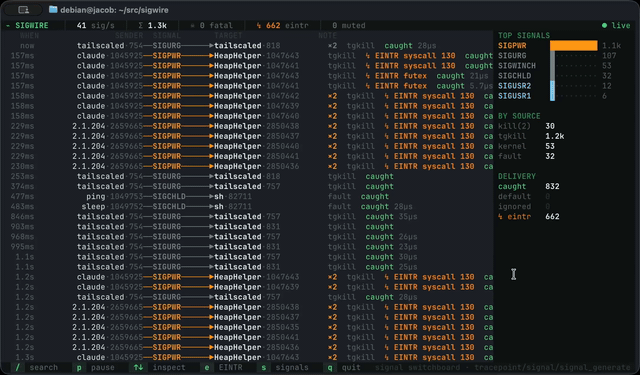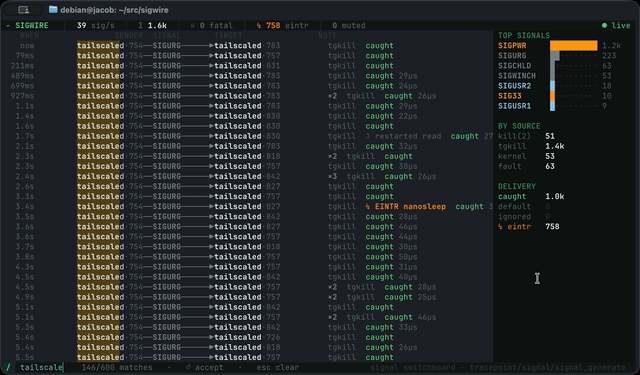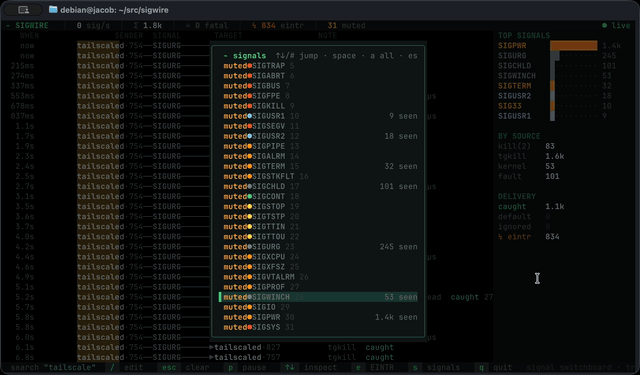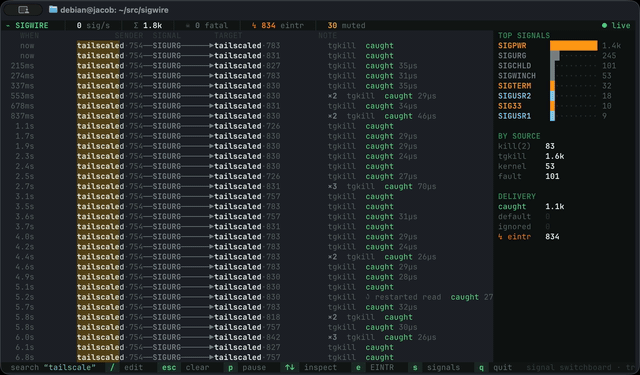 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.