
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
95 results
kraken preview

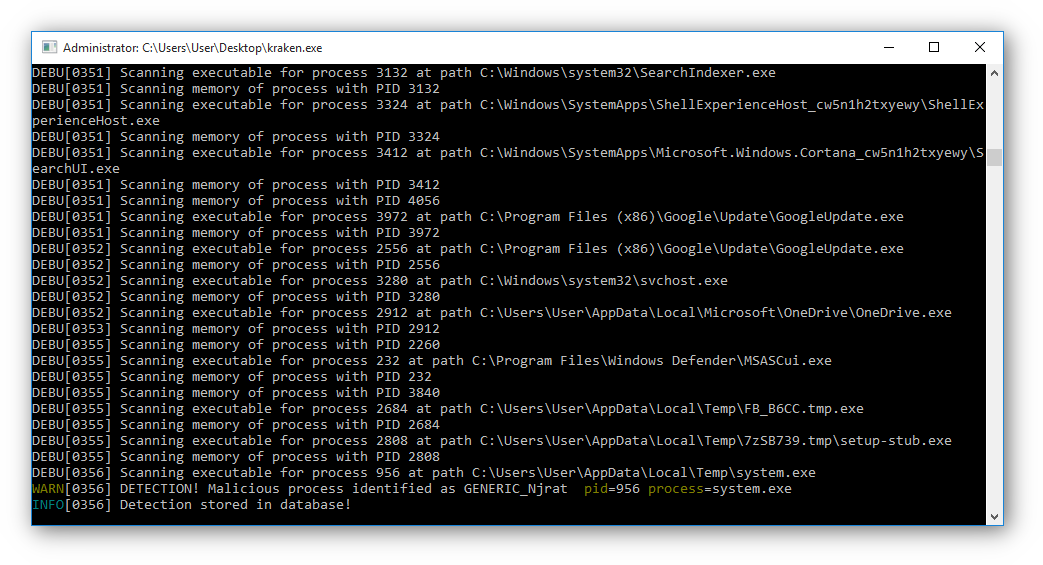
kraken

GitHubbotherder/kraken

Cross-platform Yara scanner written in Go
forensicsincident-responsemalware-analysis+1
3273 years ago
msidump preview

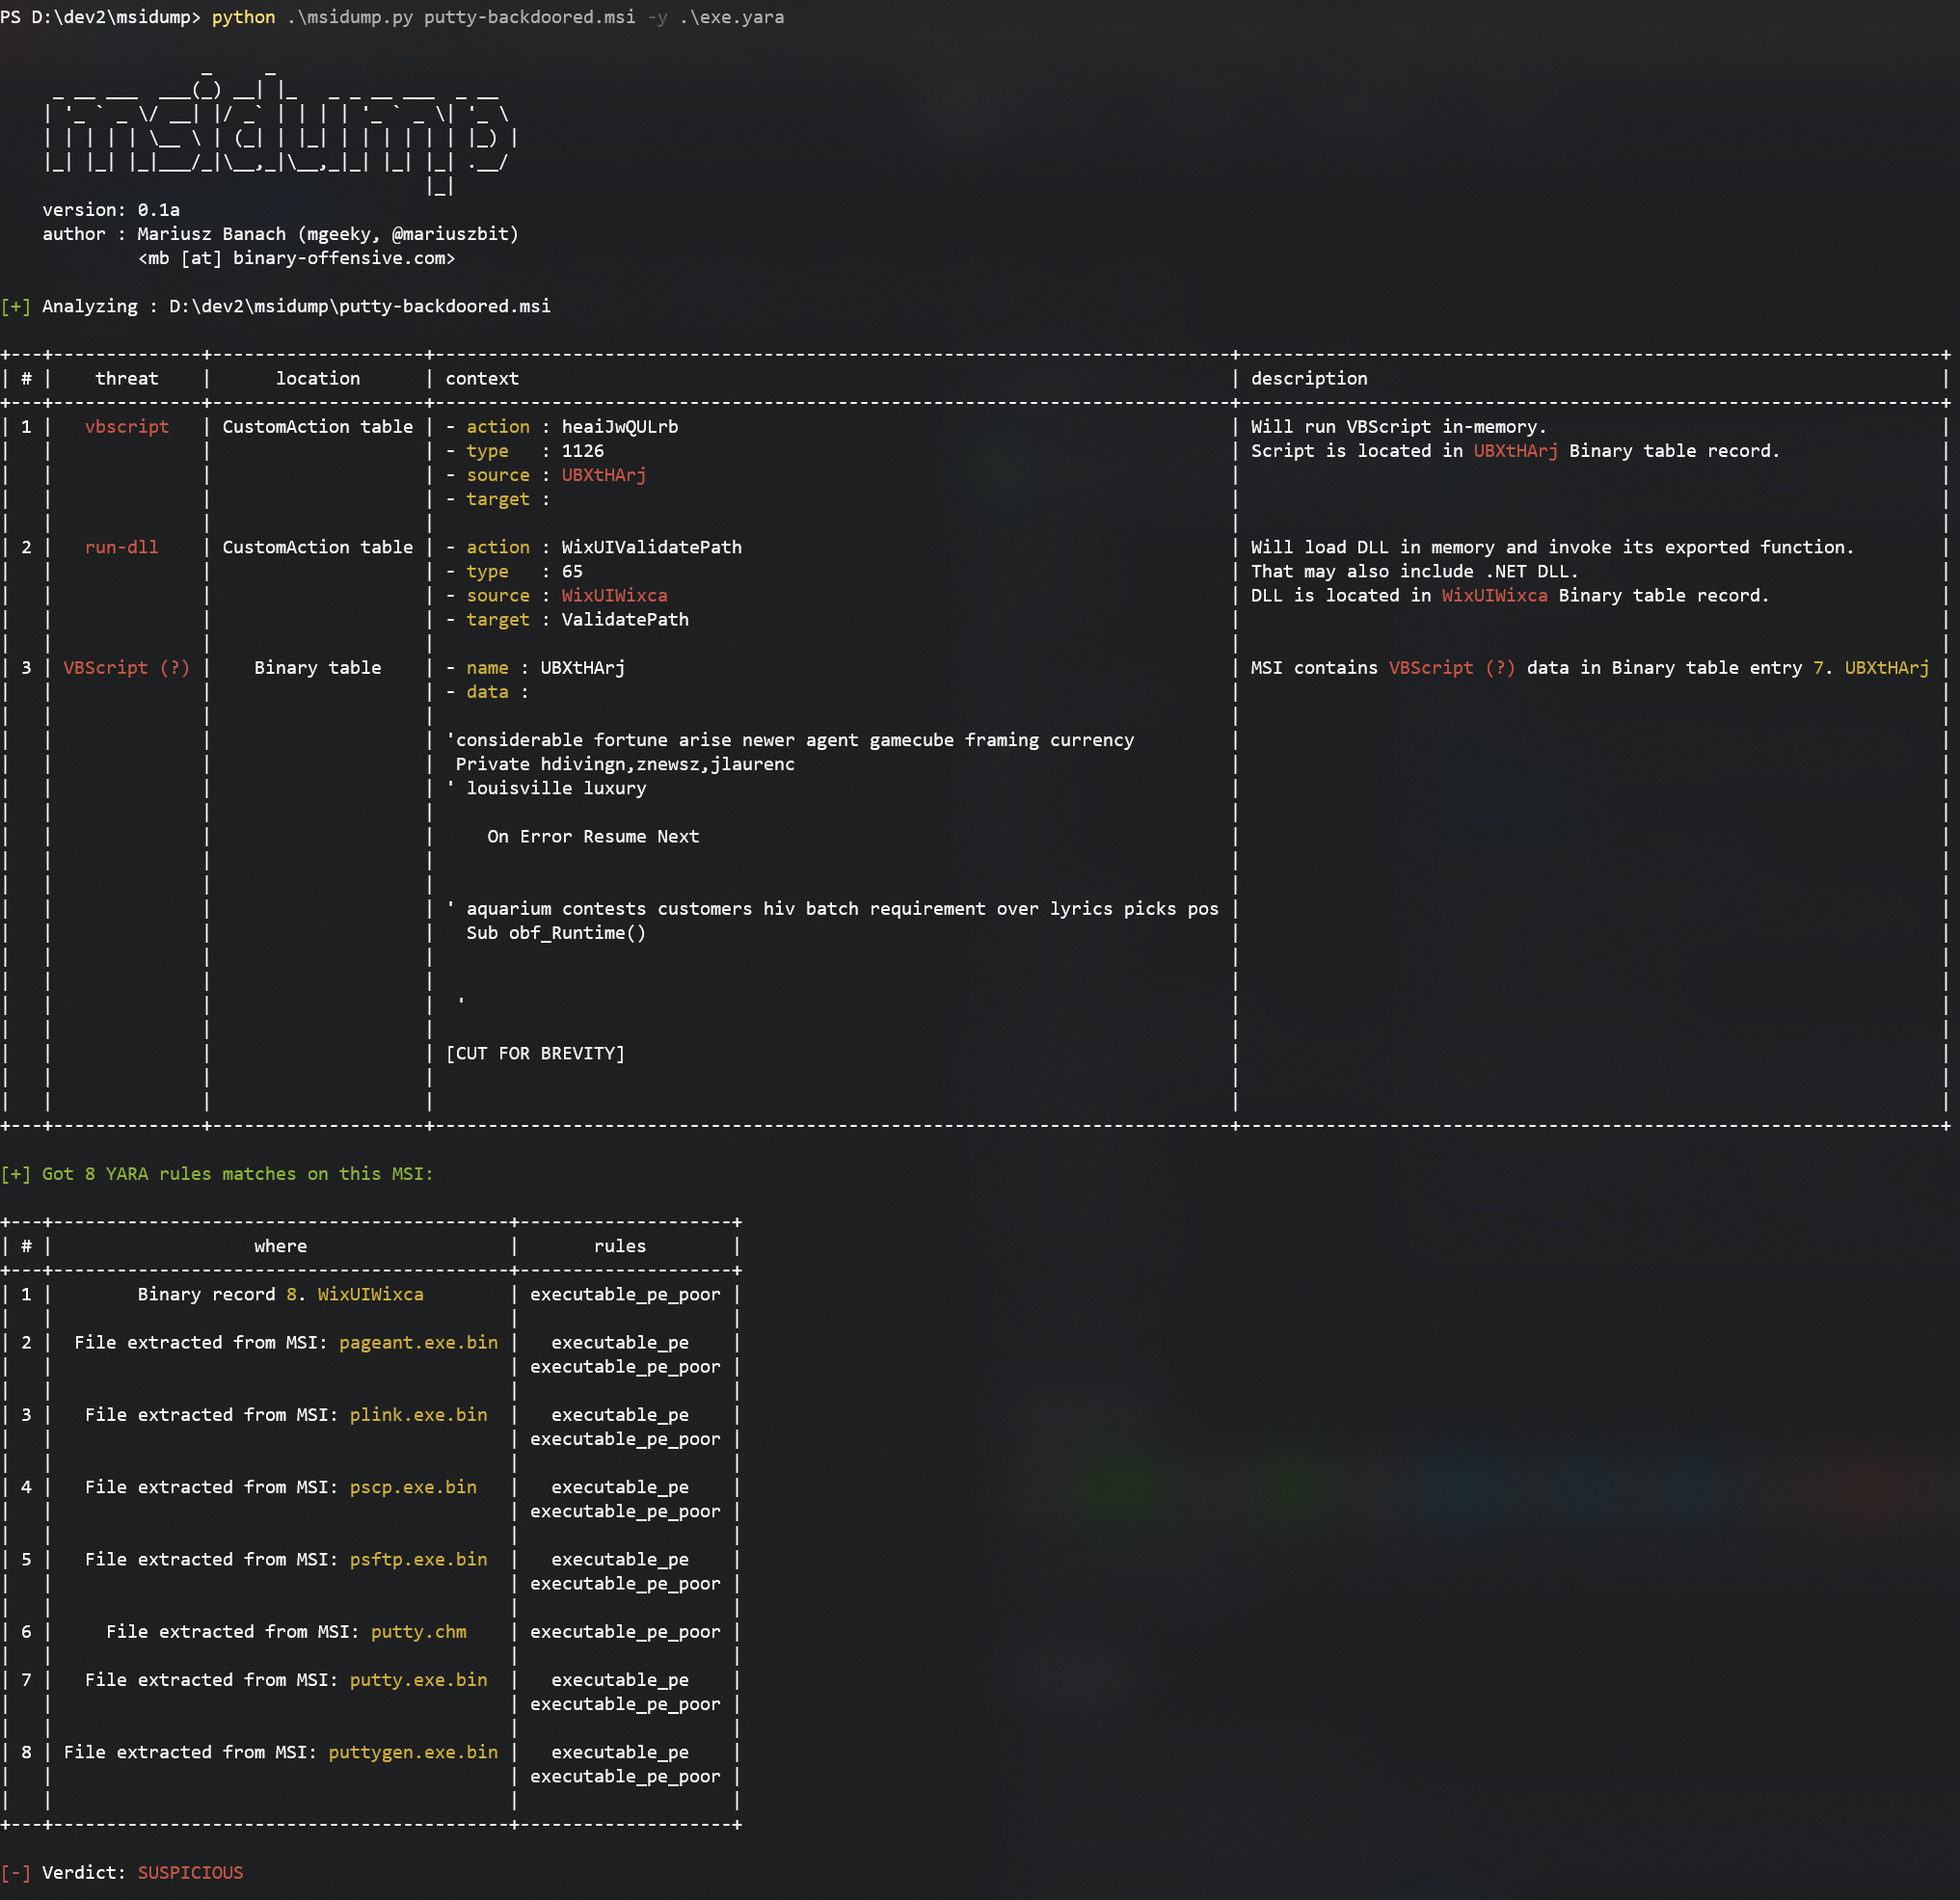
msidump

GitHubmgeeky/msidump

MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.

binary-analysisforensicsmalware-analysis+1
2323 years ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.
digital-forensicsforensicsincident-response+2
2684 years ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
2292 years ago
hacksguard preview

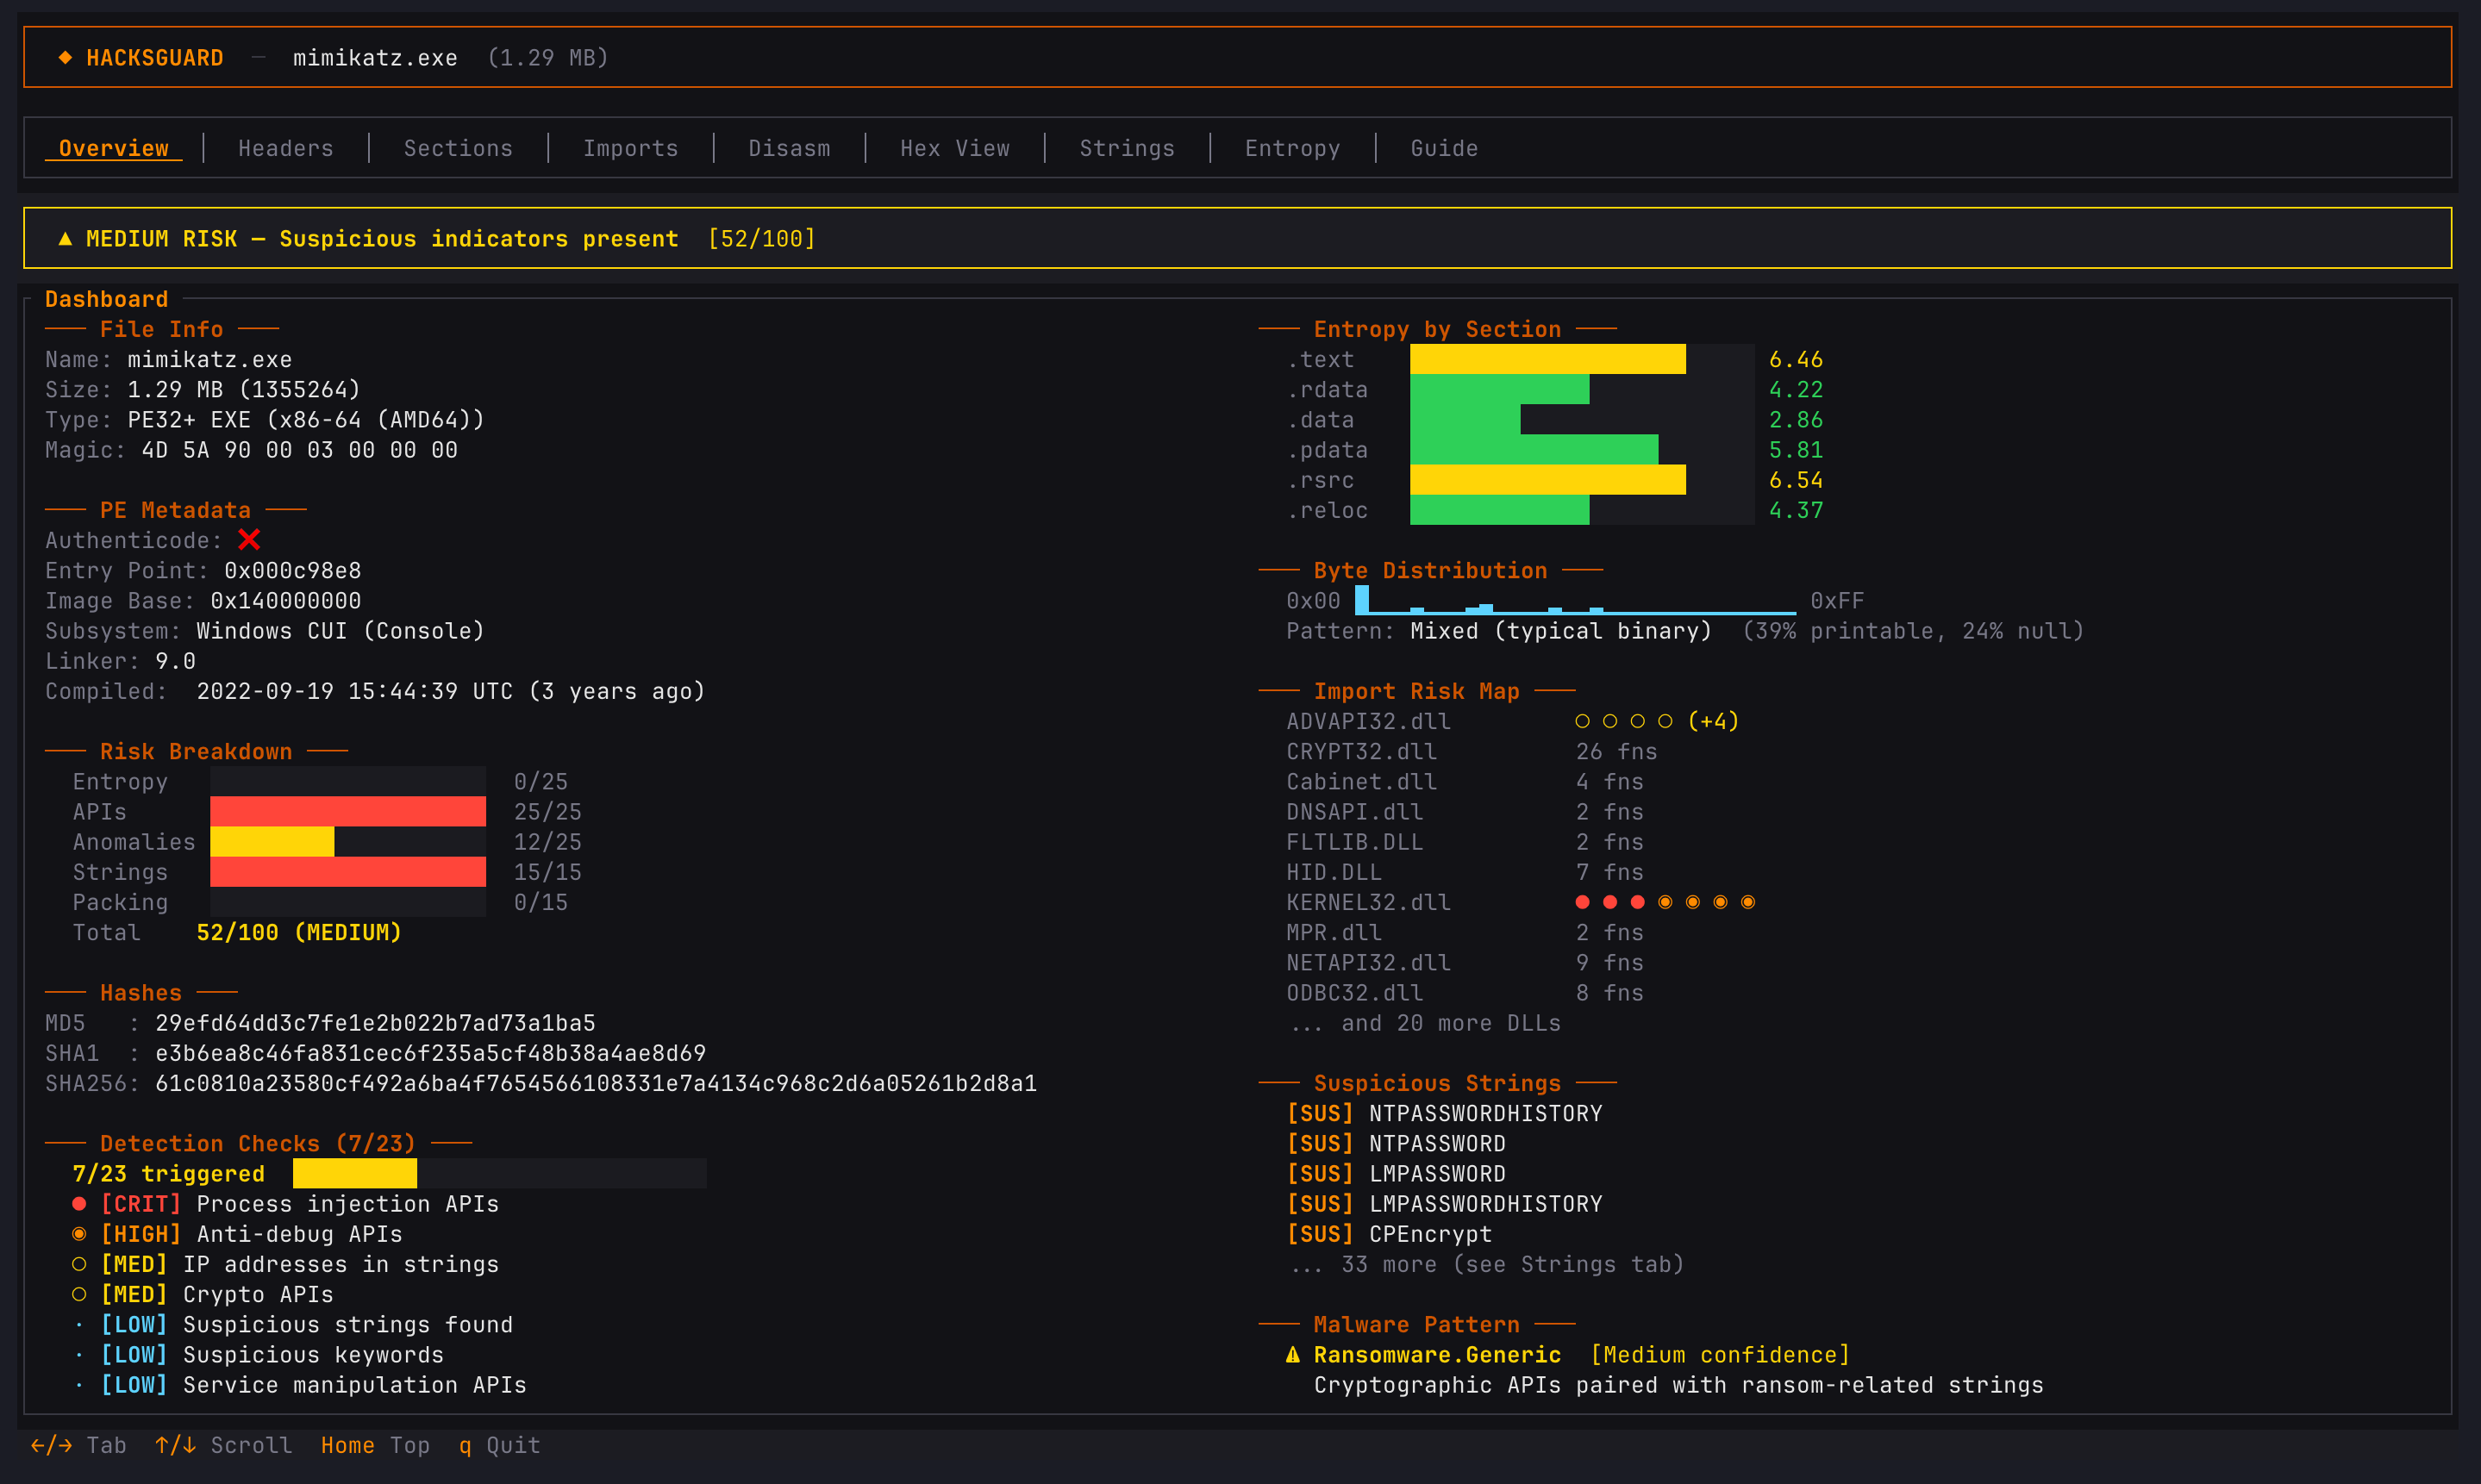
hacksguard

GitHubrhacknarok/hacksguard

A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
binary-analysisforensicsmalware-analysis+2
2151 month ago
sandfly-entropyscan preview

sandfly-entropyscan

GitHubsandflysecurity/sandfly-entropyscan

Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…

binary-analysisforensicsincident-response+1
1702 years ago
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
19716 days ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
1362 months ago
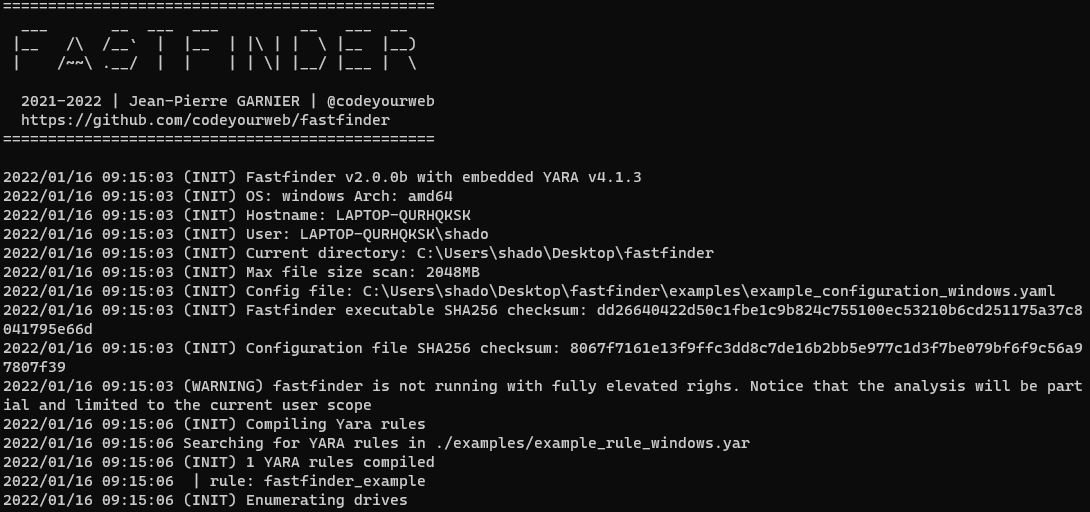
fastfinder preview

fastfinder

GitHubcodeyourweb/fastfinder

Incident Response - Fast suspicious file finder
digital-forensicsforensicsincident-response+1
2619 months ago
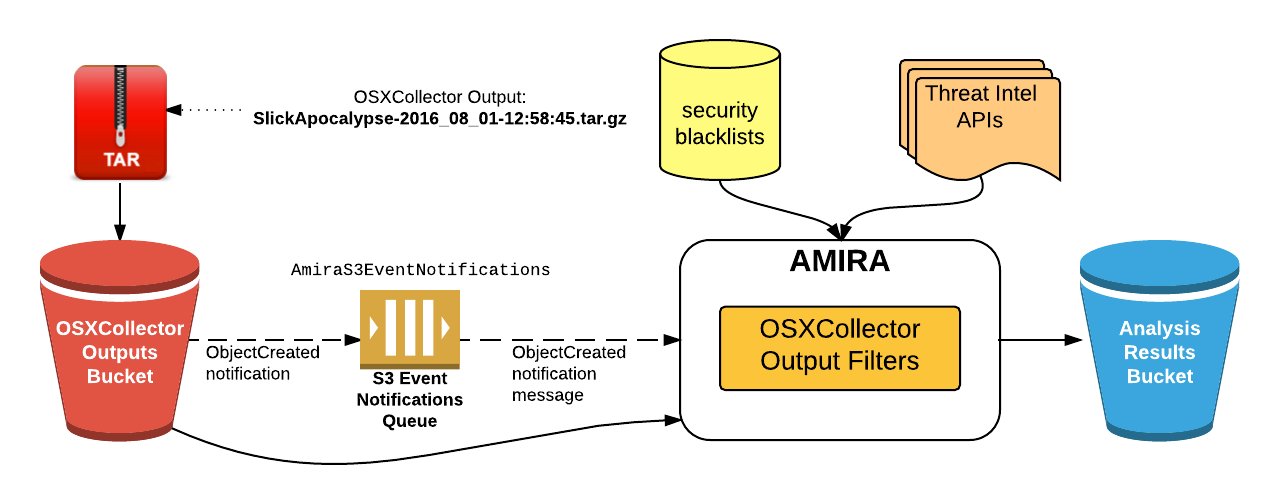
amira preview

amira

GitHubyelp/amira

AMIRA: Automated Malware Incident Response & Analysis
cloud-securityforensicsincident-response+1
1526 months ago
RogueAssemblyHunter preview

RogueAssemblyHunter

GitHubbohops/rogueassemblyhunter

Rogue Assembly Hunter is a utility for discovering 'interesting' .NET CLR modules in running processes.
defensive-toolsforensicsincident-response+2
1204 years ago
VolExp preview

VolExp

GitHubmemoryforensics1/volexp

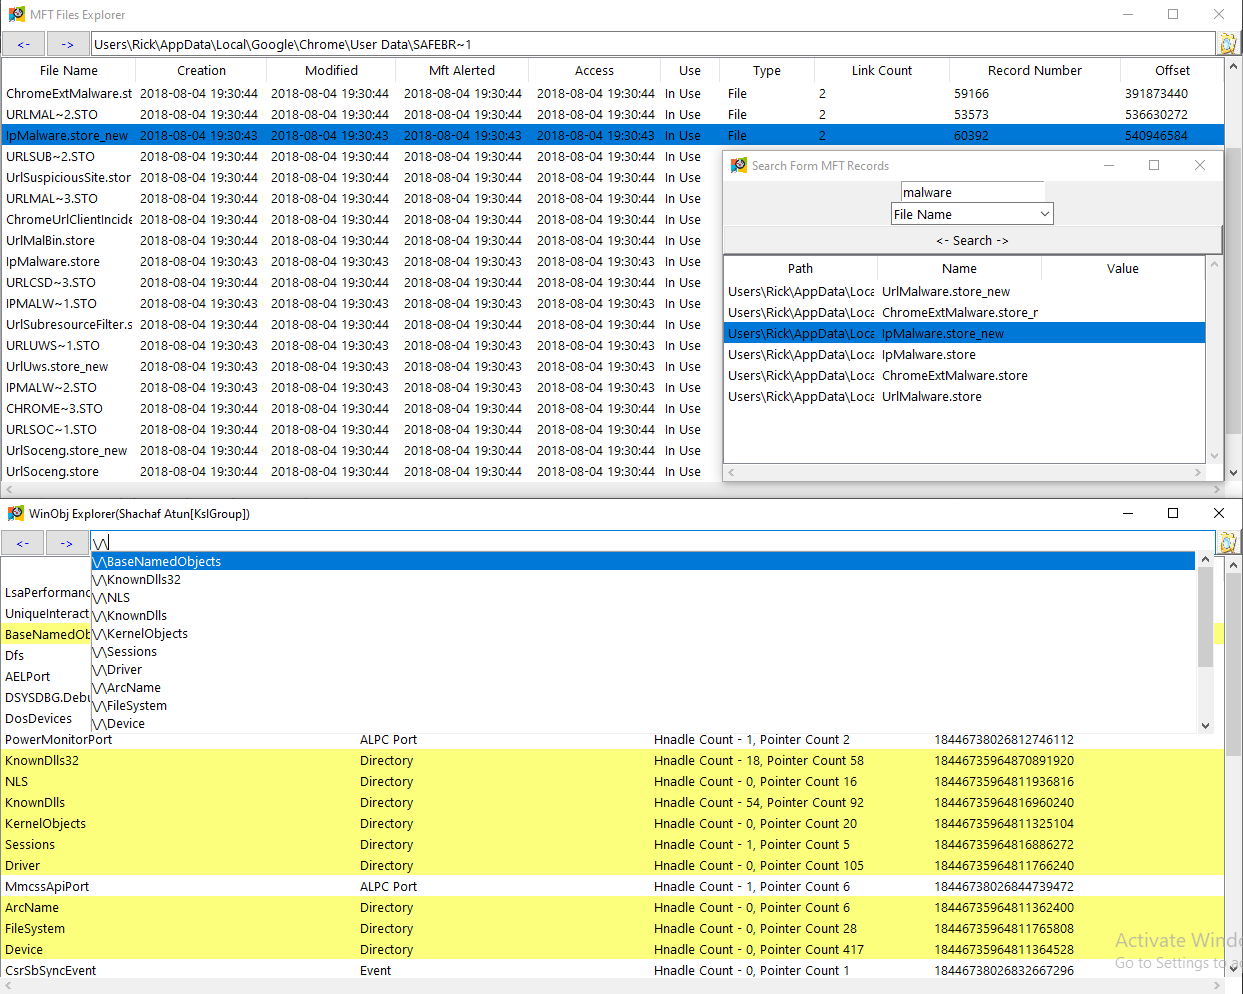
volatility explorer (volatility 2)
digital-forensicsforensicsincident-response+2
955 years ago
yaralyzer preview

yaralyzer

GitHubmichelcrypt4d4mus/yaralyzer

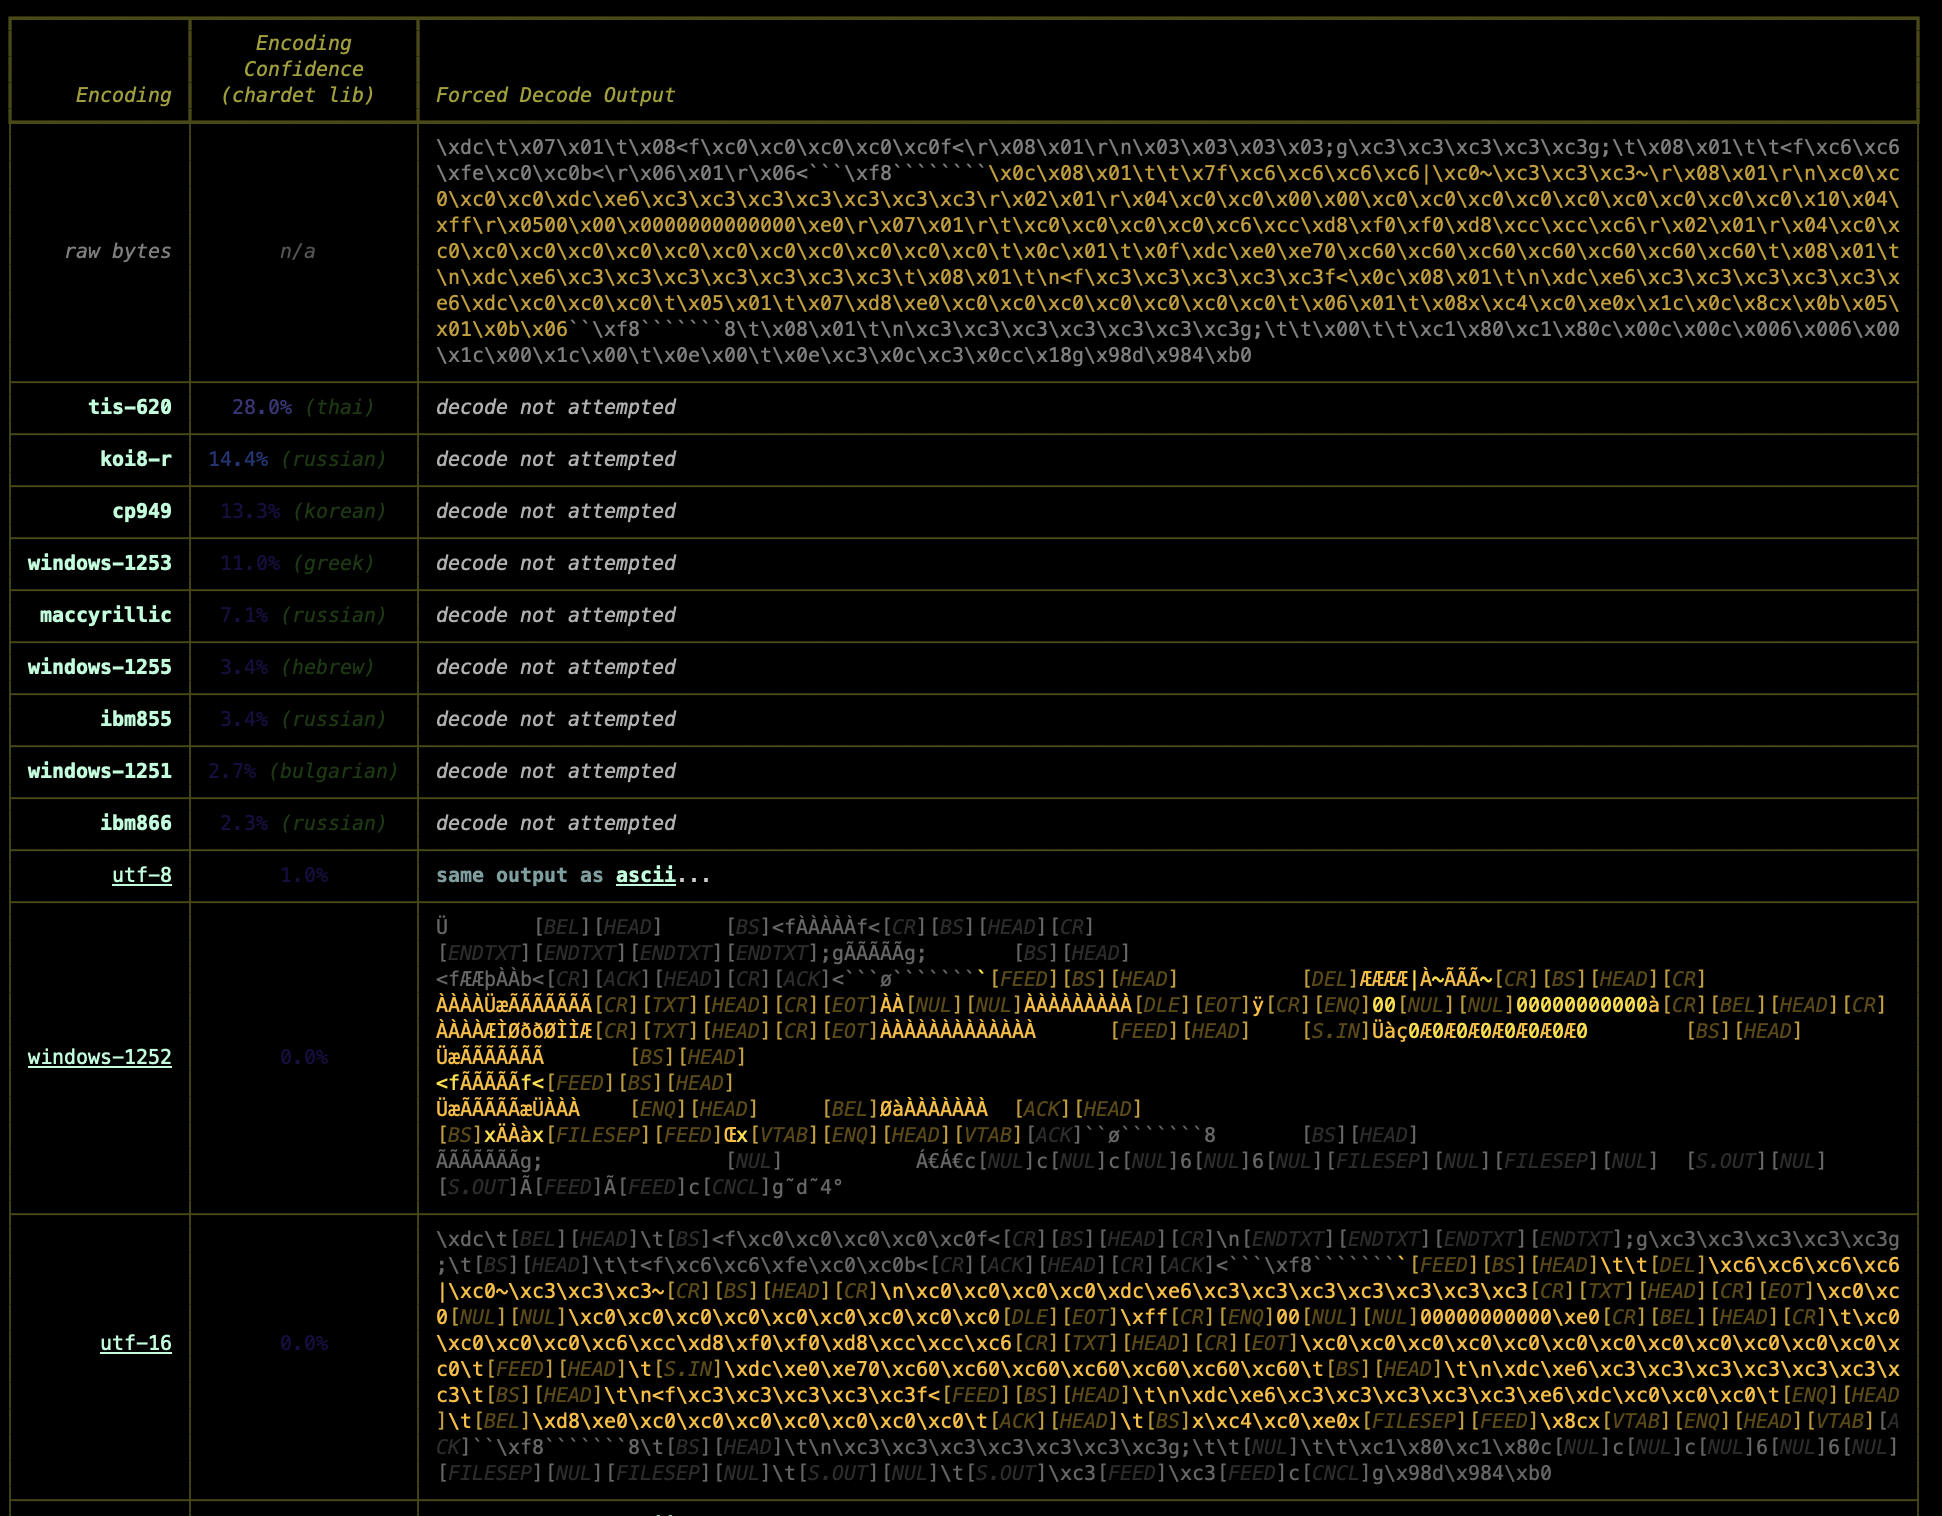
Visually inspect and force decode YARA and regex matches found in both binary and text data with colors. Lots of colors.
binary-analysisforensicsmalware-analysis+1
1538 months ago
amcache-evilhunter preview

amcache-evilhunter

GitHubcristianzsh/amcache-evilhunter

Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
digital-forensicsforensicsincident-response+2
1144 days ago
webshell-analyzer preview

webshell-analyzer

GitHubtstillz/webshell-analyzer

Web shell scanner and analyzer.
forensicsmalware-analysisstatic-analysis+2
1143 years ago
CIRTKit preview

CIRTKit

GitHubopensourcesec/cirtkit

Tools for the Computer Incident Response Team :computer:
digital-forensicsforensicsincident-response+2
1539 years ago
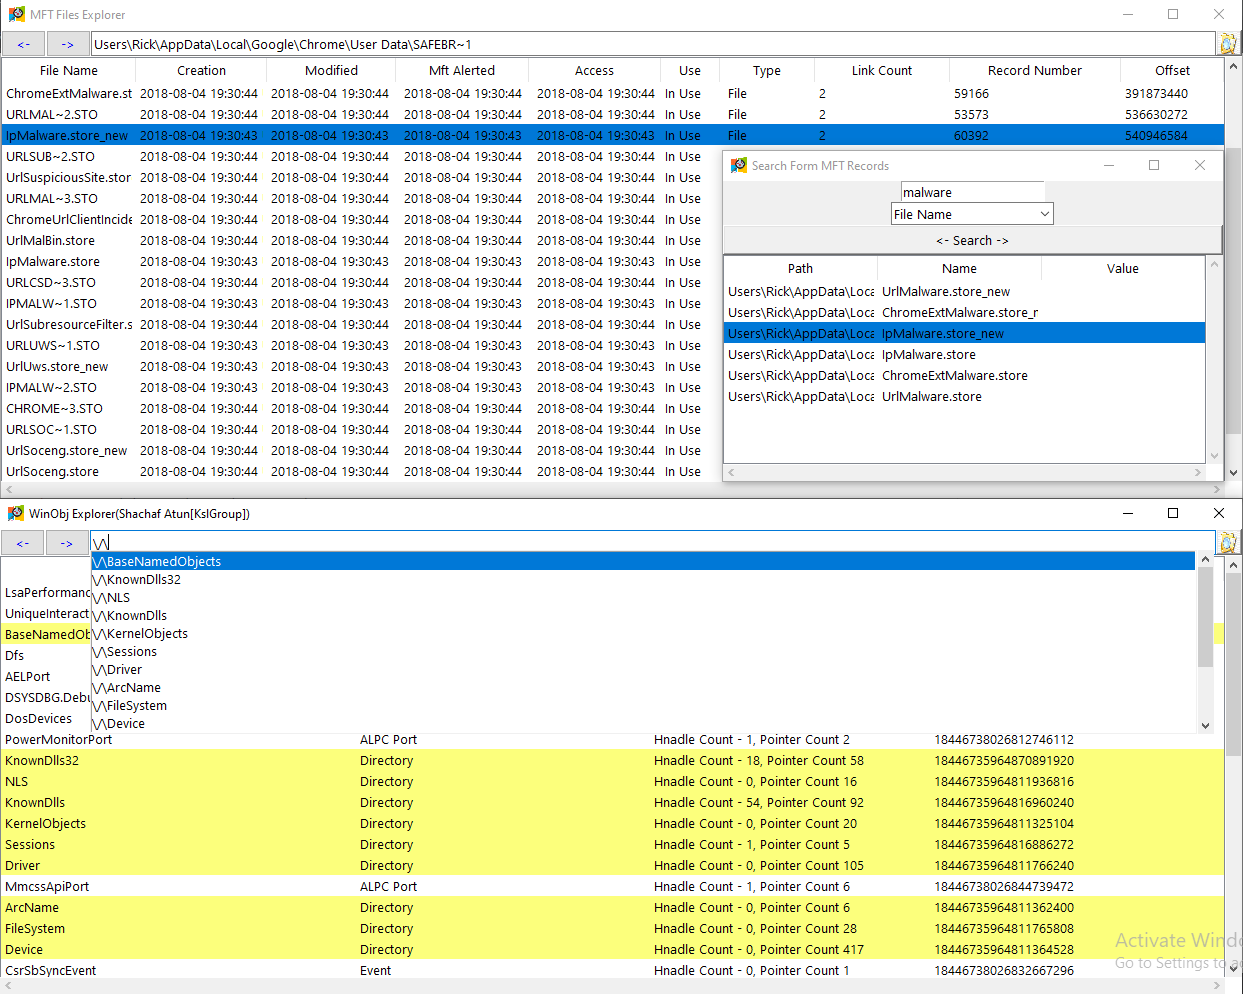
Vol3xp preview

Vol3xp

GitHubmemoryforensics1/vol3xp

Volatility Explorer Suit (volatility 3)
digital-forensicsforensicsincident-response+3
703 years ago
qs_old preview

qs_old

GitHubtylabs/qs_old

Command line tool for scanning streams within office documents plus xor db attack

forensicsmalware-analysisstatic-analysis+1
1273 years ago
Previous123456Next