
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
275 results
Collect-MemoryDump preview

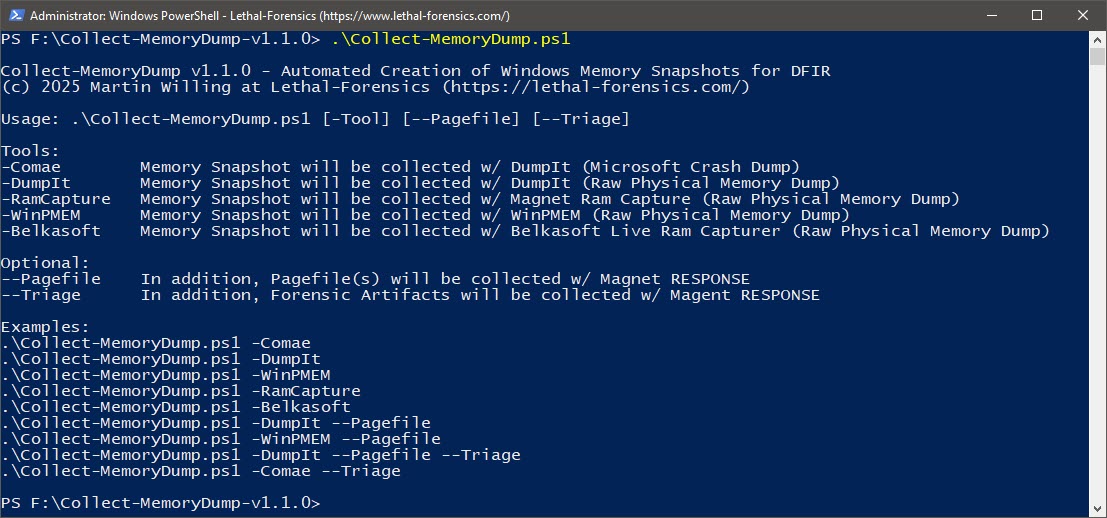
Collect-MemoryDump

GitHublethal-forensics/collect-memorydump

Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…

digital-forensicsforensicsincident-response+1
265
1 year ago
autoresponder preview

autoresponder

GitHublawiet47/autoresponder

Automates incident response tasks via Carbon Black Response API: file/registry deletion, process killing, sensor isolation, binary collection, and…

forensicsincident-response
565 years ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.3k20 days ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

binary-analysisforensicsmalware-analysis+2
3.9k4 months ago
oletools preview

oletools

GitHubdecalage2/oletools

Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…

code-analysisdigital-forensicsforensics+3
3.4k9 months ago
investigations preview

investigations

GitHubamnestytech/investigations

Indicators of Compromise from Amnesty International's cyber investigations

forensicsinformation-gatheringioc-management+3
1.7k1 year ago
hollows_hunter preview

hollows_hunter

GitHubhasherezade/hollows_hunter

Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…

defensive-toolsforensicsincident-response+2
2.4k4 months ago
APT-Hunter preview

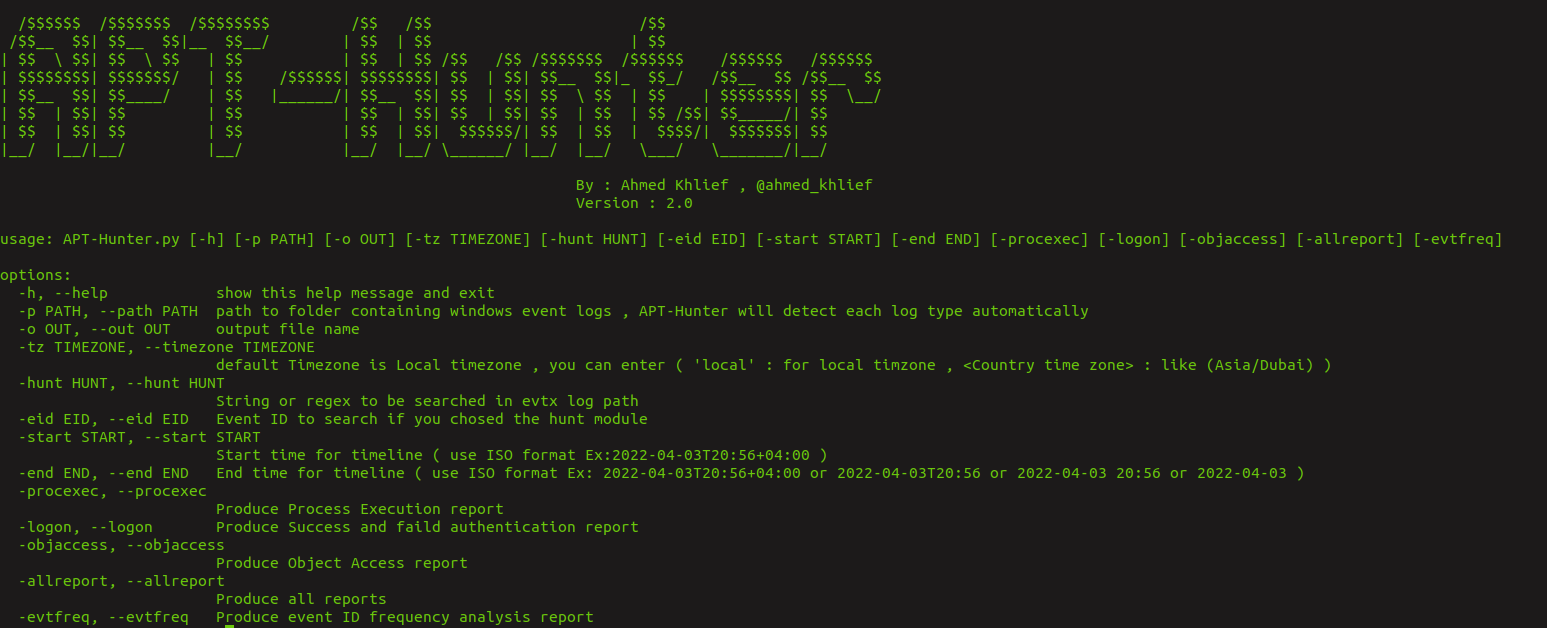
APT-Hunter

GitHubahmedkhlief/apt-hunter

APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…

forensicsincident-responselog-analysis+1
1.4k1 month ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

digital-forensicsforensicsincident-response+3
1.4k1 month ago
turbinia preview

turbinia

GitHubgoogle/turbinia

Automation and Scaling of Digital Forensics Tools

cloud-securitydigital-forensicsforensics+1
79215 days ago
hashID preview

hashID

GitHubpsypanda/hashid

Software to identify the different types of hashes -

forensicshash-analysisinformation-gathering+3
1.5k11 years ago
ngrep preview

ngrep

GitHubjpr5/ngrep

ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…

dns-analysisforensicsinformation-gathering+3
1.0k8 months ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…

binary-analysisdefensive-toolsforensics+3
6789 months ago
chepy preview

chepy

GitHubsecurisec/chepy

Chepy is a python lib/cli equivalent of the awesome CyberChef tool.

cryptographyctfforensics+2
1.0k6 months ago
wholeaked preview

wholeaked

GitHubutkusen/wholeaked

a file-sharing tool that allows you to find the responsible person in case of a leakage

data-exfiltrationforensicsinformation-gathering+2
1.1k4 years ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

digital-forensicsforensicsincident-response+4
2188 years ago
iocextract preview

iocextract

GitHubpedramamini/iocextract

Defanged Indicator of Compromise (IOC) Extractor.

digital-forensicsforensicsinformation-gathering+5
5842 years ago
MalConfScan preview

MalConfScan

GitHubjpcertcc/malconfscan

Volatility plugin for extracts configuration data of known malware

digital-forensicsforensicsincident-response+3
4992 years ago
Previous1234…16Next