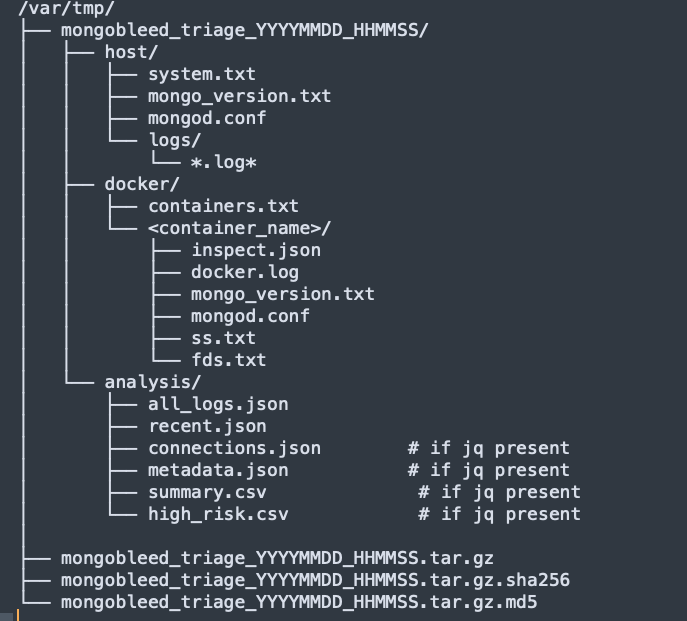
MongoBleed-DFIR-Triage-Script-CVE-2025-14847

The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…

A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…

Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…

Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.

Your everyday Linux distribution gone Super Saiyan.

A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner

Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)

CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script

VirusTotal Wanna Be - Now with 100% more Hipster

⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

Automates incident response tasks via Carbon Black Response API: file/registry deletion, process killing, sensor isolation, binary collection, and…

OsintNET is a browser-based OSINT platform for domain intelligence, website risk scanning, SERP discovery, image intelligence and AI image detection.

Graphical interface for PortEx, a Portable Executable and Malware Analysis Library

Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…

Shell script to detect the CVE-2024-3094 backdoor in XZ Utils by checking for malicious code in liblzma build artifacts and identifying affected…

Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.