

Mortimer
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
forensicsioc-managementlog-analysis+3
12
nccgroup/mortimerA collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 onapsis/onapsis_cve-2025-31324_scanner_tools
Python-based scanner for CVE-2025-31324 that identifies vulnerable SAP NetWeaver Visual Composer instances and detects indicators of compromise from…
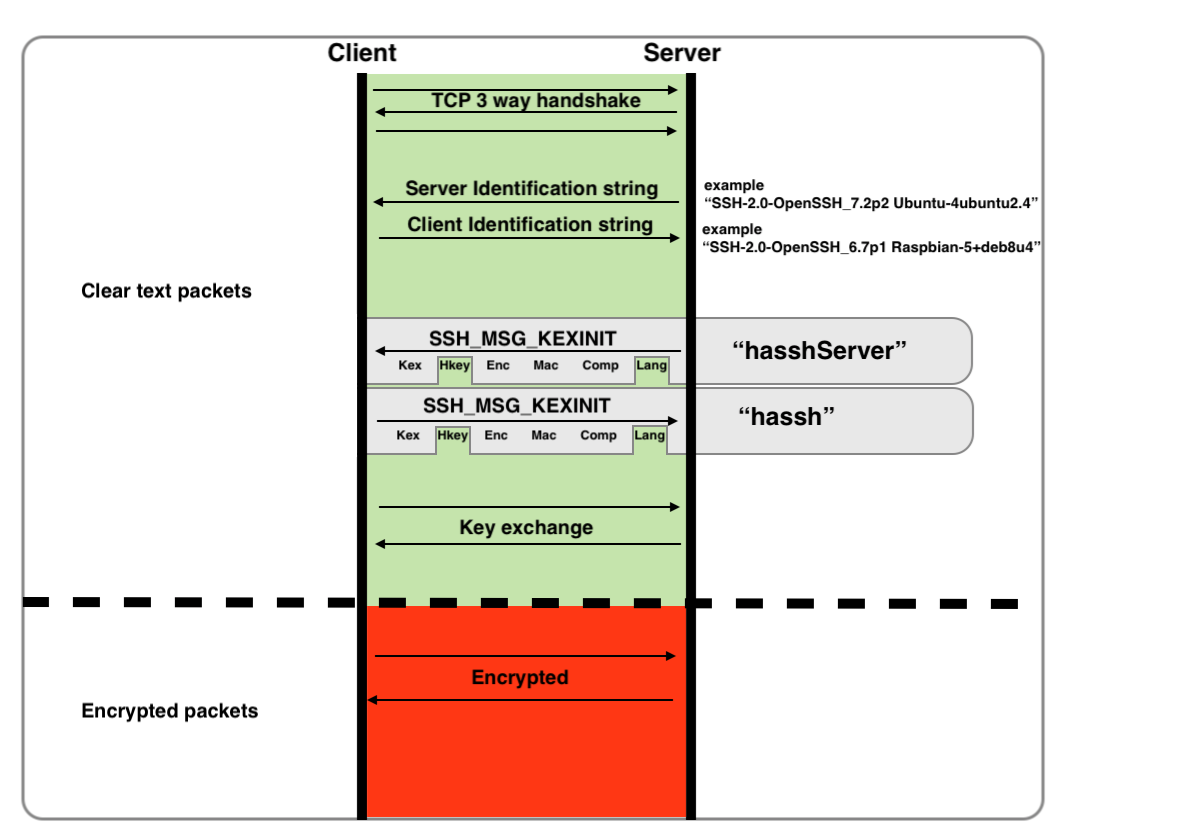 corelight/hassh
Fingerprint SSH clients and servers.
 onapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment
CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
 navytitanium/eitest-tools-scripts-iocs
IOC feed and analysis toolkit for EITest campaigns, featuring C2 data decryption, victim payload decoding, and sinkhole log processing for threat…
 rjsudlow/proxynotshell-ioc-checker
Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781
 mrrawbit/sonicwall-sma1000-zero-day-ioc-check
Unofficial Bash IoC checker for SonicWall SMA1000 appliances affected by actively exploited CVE-2026-15409 and CVE-2026-15410.
 ace-responder/cve-2022-47966_checker
Run on your ManageEngine server
 hackinglz/panrapidcheck
Extract useful information from PANOS support file for CVE-2024-3400
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
 nkopylov/tanscript-exploit-check
IOC checker for the TanStack/Mini Shai-Hulud npm supply chain attack (CVE-2026-45321)
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 rxwx/pulse-meter
Parses the System Snapshot from an Ivanti Connect Secure applicance to identify possible IOCs related to CVE-2023-46805, CVE-2024-21887 and…
 ma1am/cve-2022-26134-exploit-detection
This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…
 b401/clickstudio-compromised-certificate
Repository containing the compromised certificate seen in recent CVE-2022-30190 (Follina) attacks.
 cyb3rtus/keepass_cve-2023-24055_yara_rule
Contains a simple yara rule to hunt for possible compromised KeePass config files