
IRTriage
 ajmartel/irtriage
Incident Response Triage - Windows Evidence Collection for Forensic Analysis
digital-forensicsforensicsincident-response+1
ajmartel/irtriageIncident Response Triage - Windows Evidence Collection for Forensic Analysis
 apsdehal/awesome-ctf
A curated list of CTF frameworks, libraries, resources and softwares
 volatilityfoundation/volatility
An advanced memory forensics framework
 thehackingsage/hackdroid
Curated catalog of 364 Android pentesting and security APKs organized by category, covering forensics, MITM, sniffing, OSINT, wireless, and privacy…
 zardus/ctf-tools
Some setup scripts for security research tools.
 horrister/solarwinds-sunburst-cve-2020-10148
Curated vulnerability writeups with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for real-world software…
 renat0z3r0/notepadpp-supply-chain-iocs
IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…
 synacktiv/veeam-velociraptor
Proof-of-concept Velociraptor artifacts pack to showcase a remote Veeam forensics pipeline.
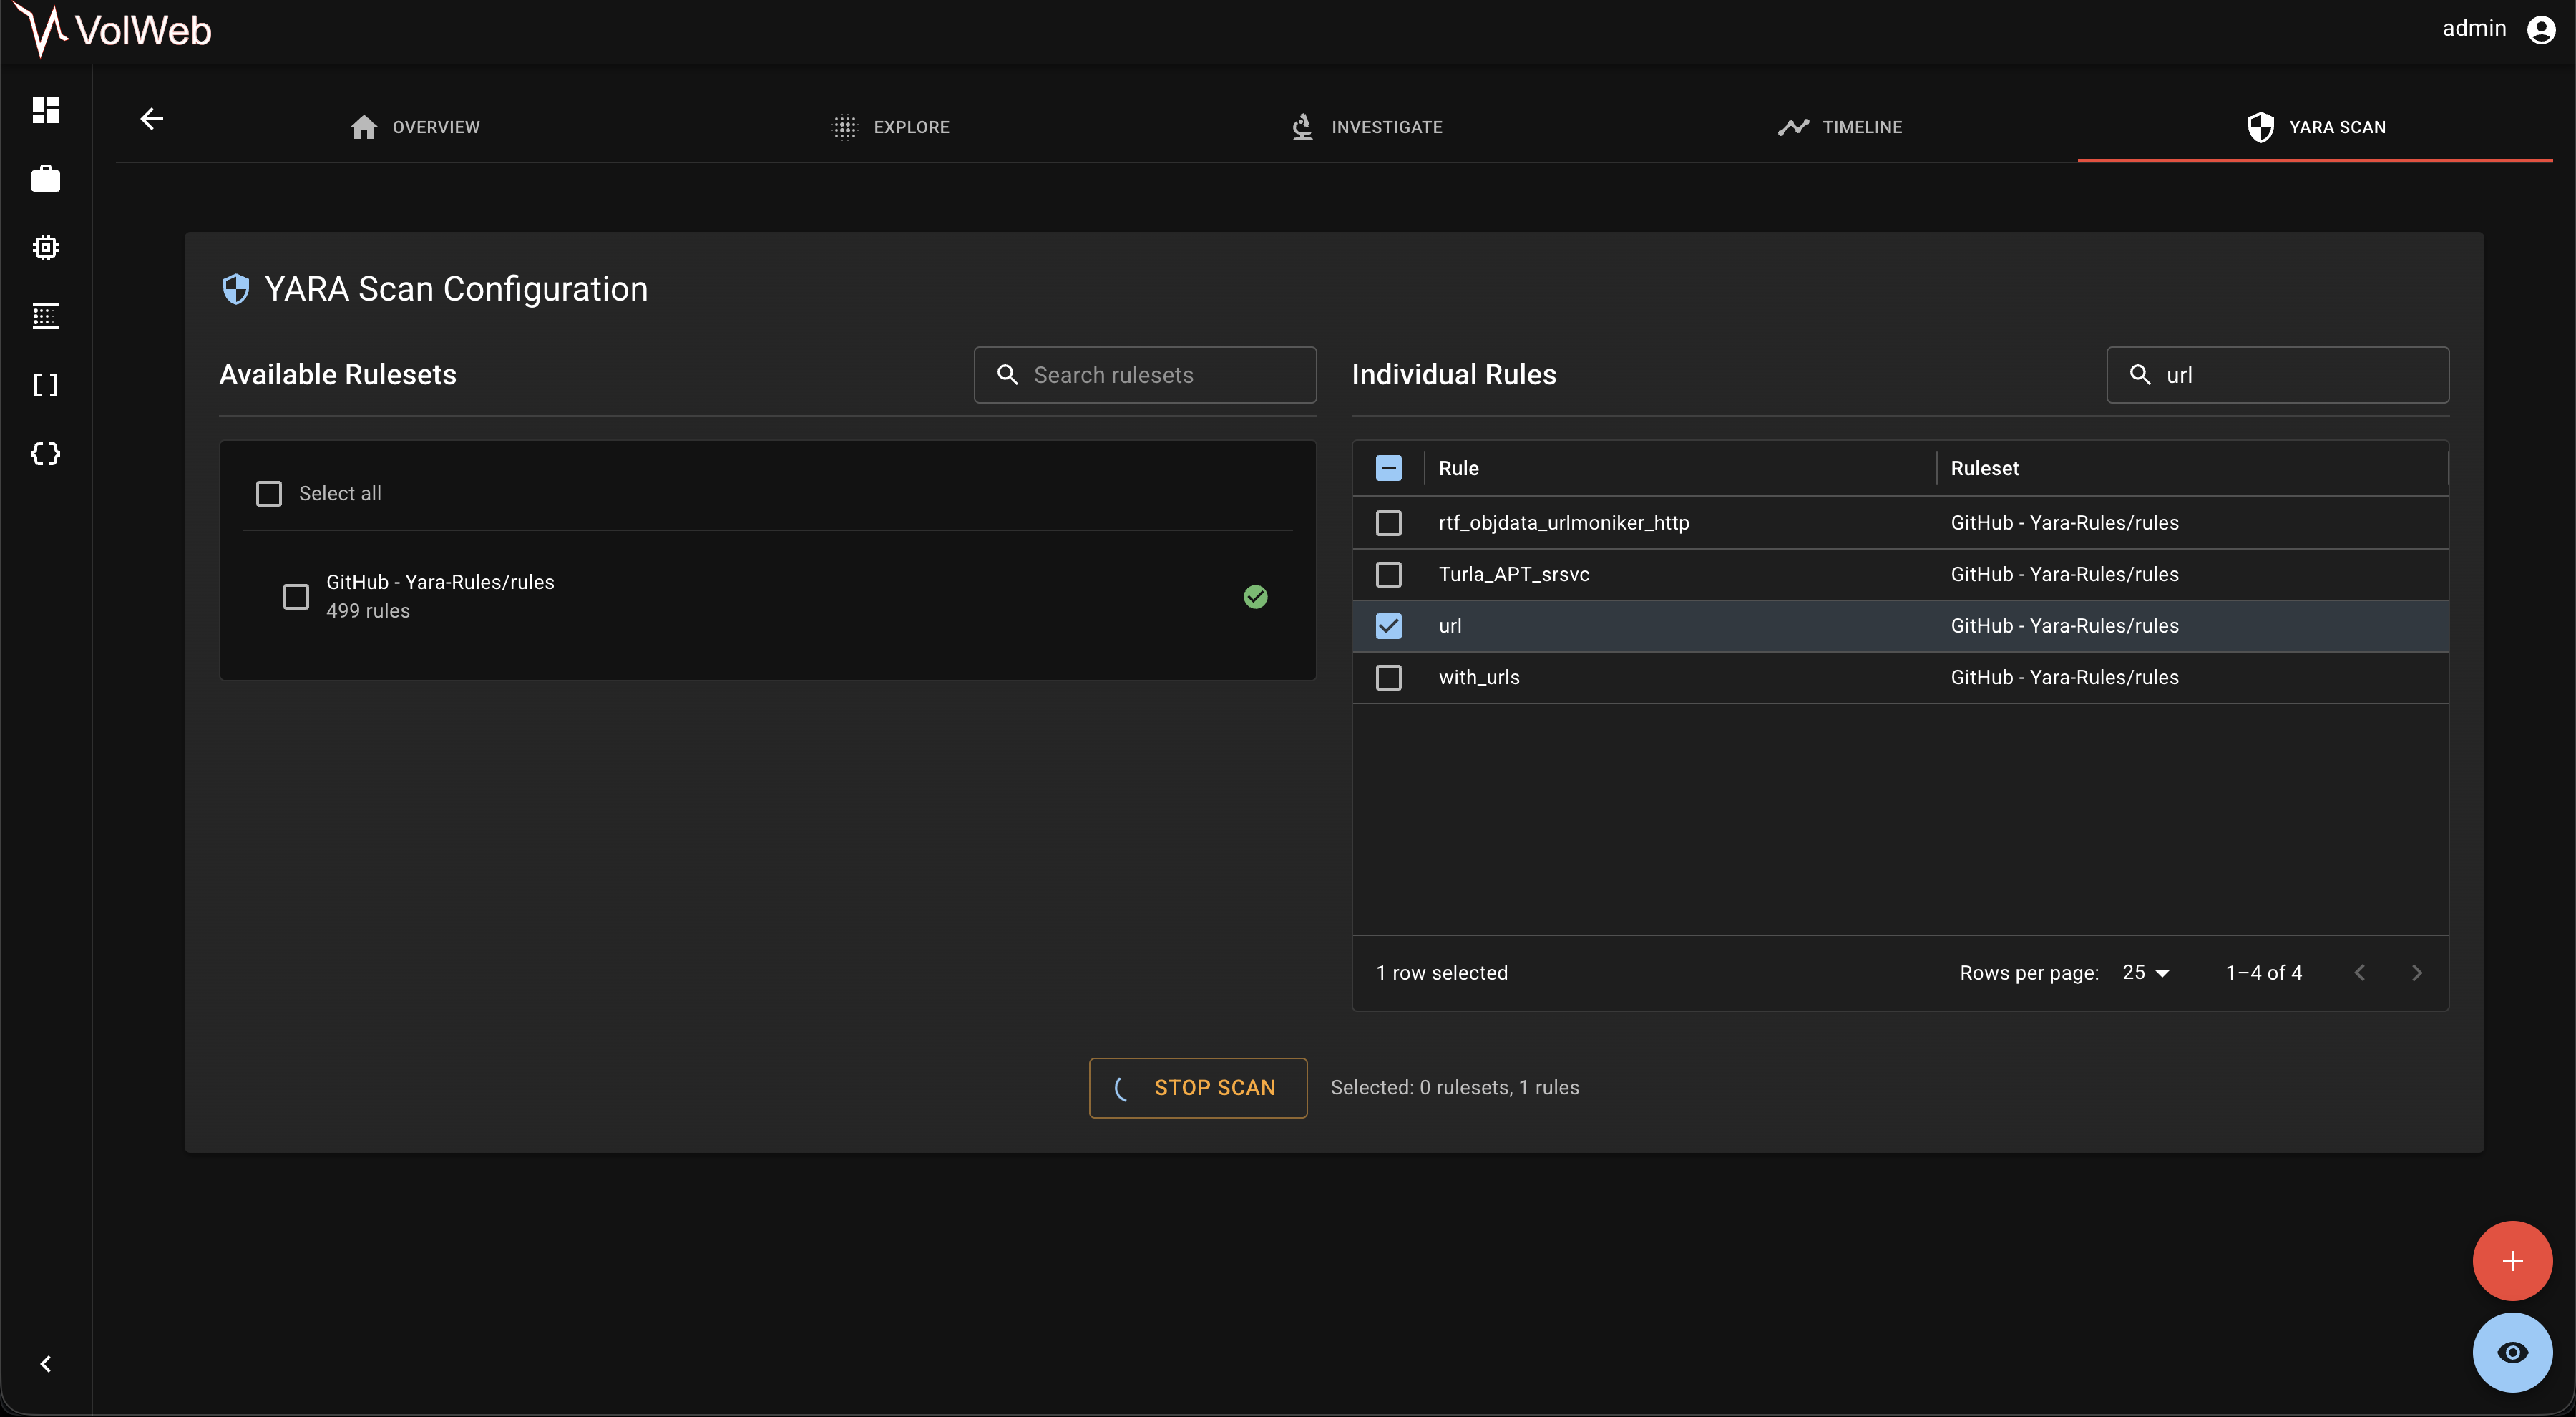 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
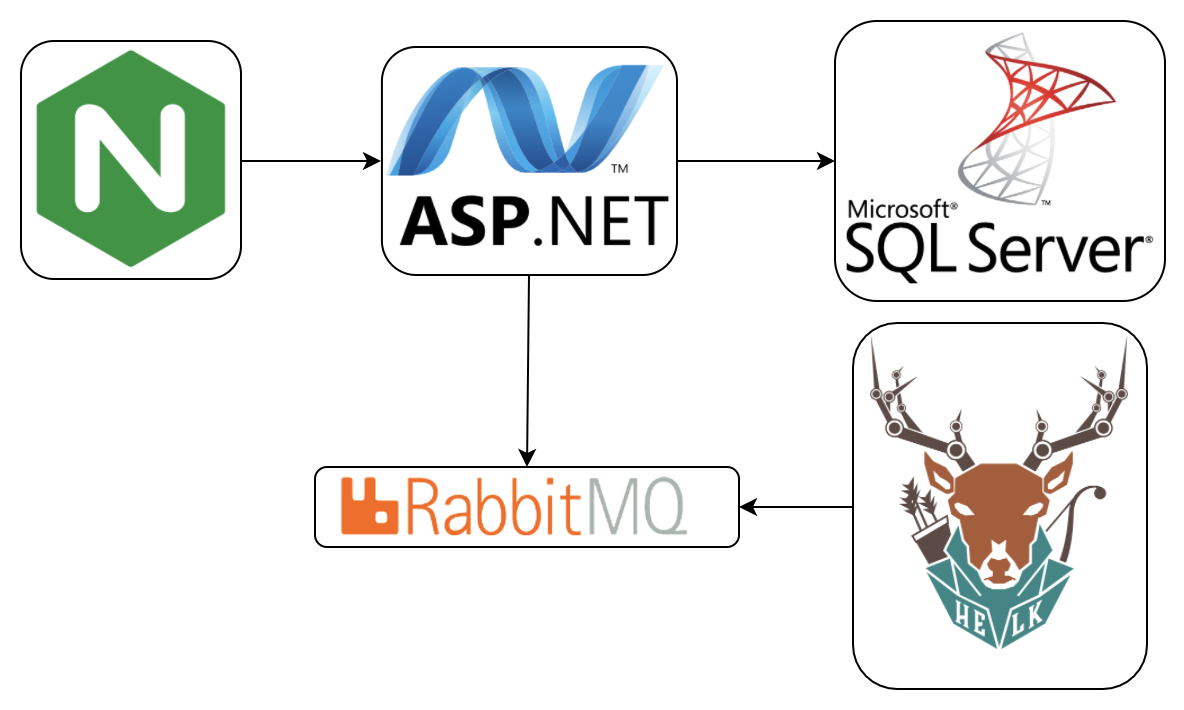 invoke-ir/ace
Automated, Collection, and Enrichment Platform
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
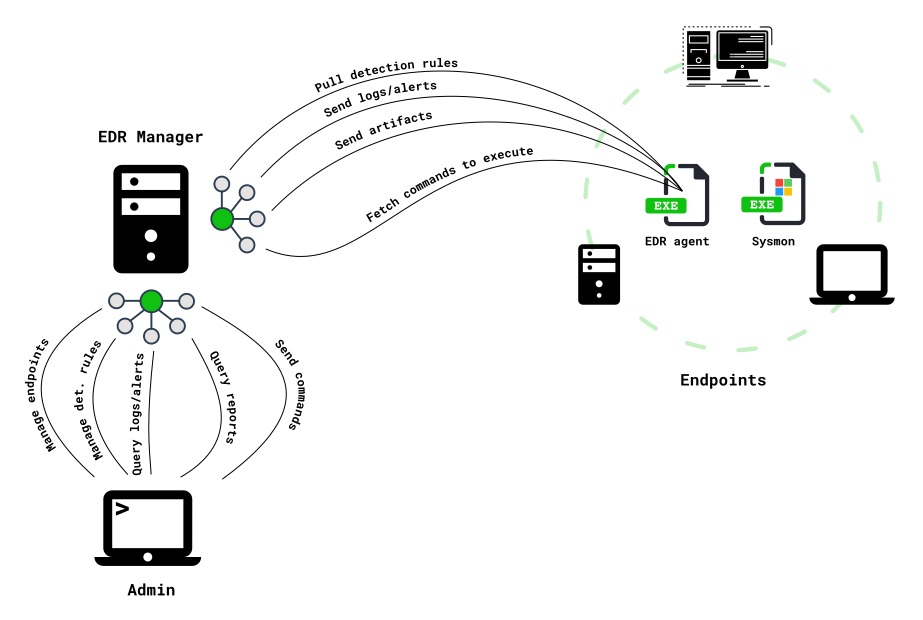 0xrawsec/whids
Windows EDR with Gene-based detection engine, real-time artifact collection, Sysmon integration, and REST API for managing endpoints, rules, and…