


 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 withsecurelabs/esfang
ESF modular ingestion tool for development and research.
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
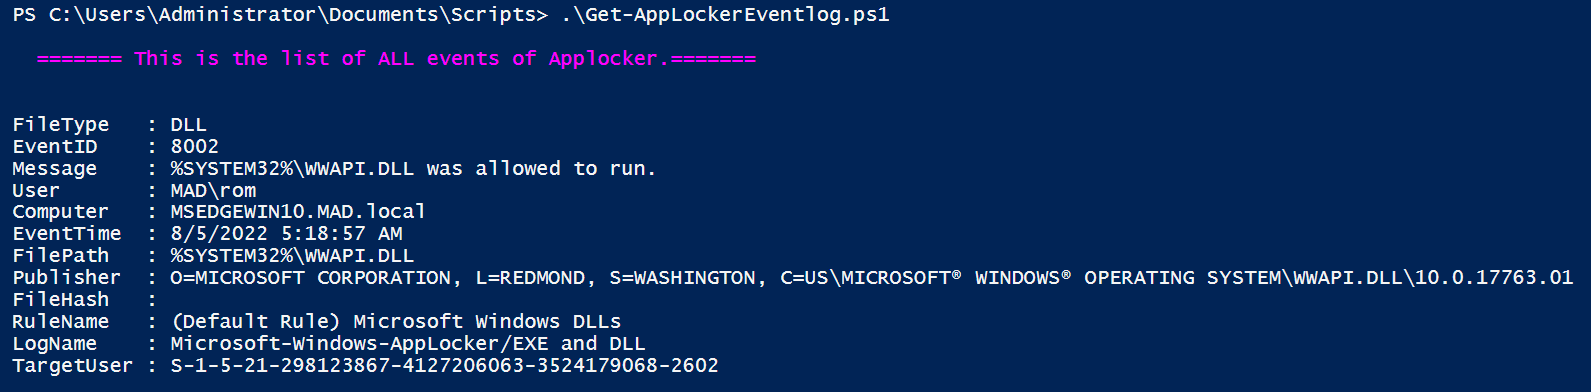 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 manishrawat21/soc-automation-lab
Documented SOC automation workflow using Wazuh, N8N, Caldera, and Velociraptor
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
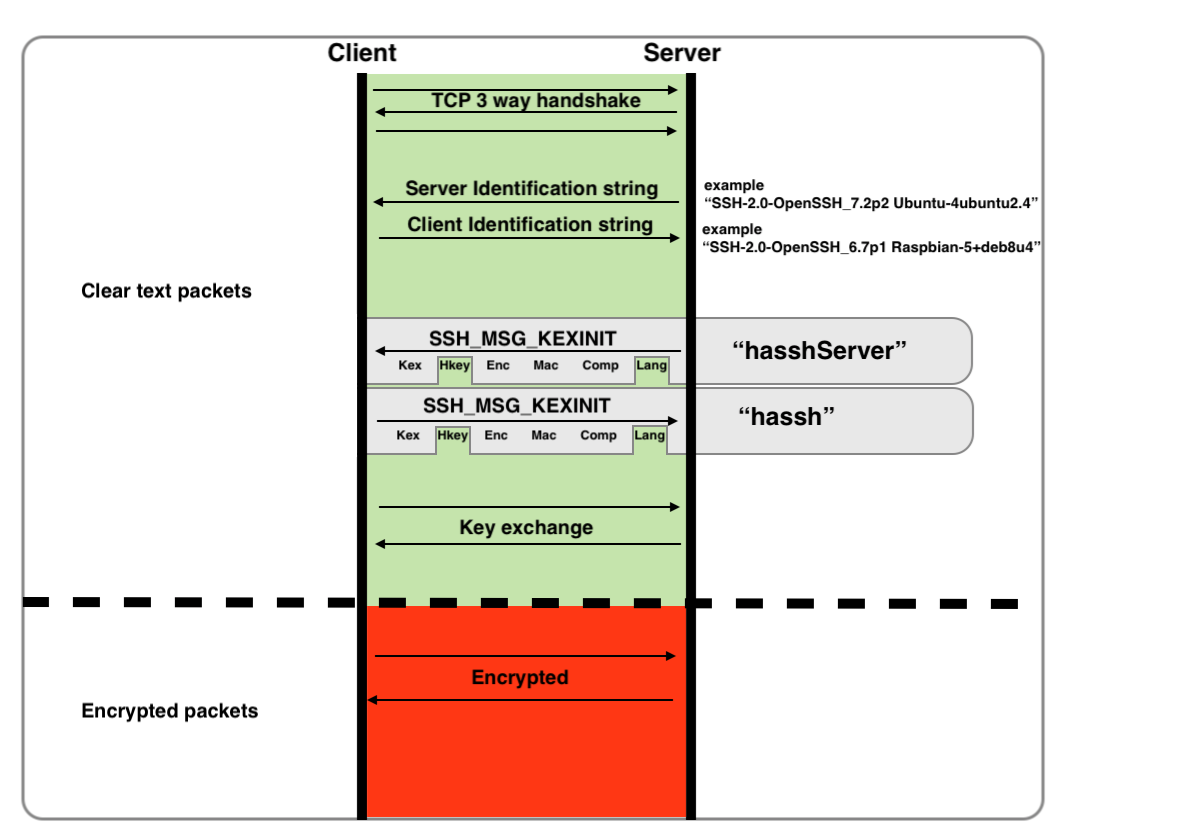 corelight/hassh
Fingerprint SSH clients and servers.
 hexastrike/ivanti-connect-secure-logs-parser
A Python script for examining Ivanti Secure Connect (ICS) event logs, designed to support investigations into vulnerabilities CVE-2025-0282,…
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 verveindustrialprotection/cve-2021-44228-log4j
Provides BigFix Fixlets and analyses to detect Log4j vulnerabilities (CVE-2021-44228, CVE-2021-45046, CVE-2021-45105) across Windows and Linux…
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 muhammad-ali007/follina_msdt_cve-2022-30190
Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…