
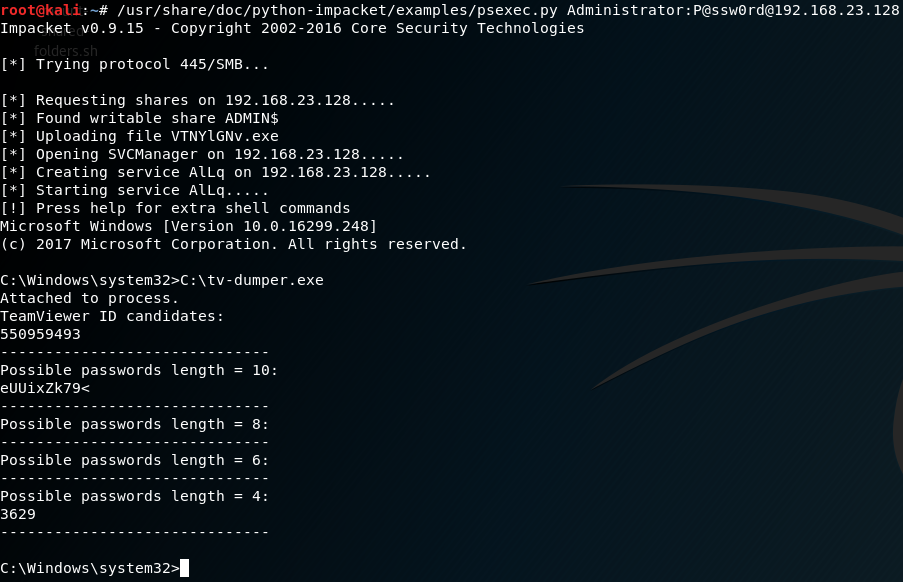
teamviewer-dumper
 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
digital-forensicsforensicsinformation-gathering+3
98
attackercan/teamviewer-dumperDump TeamViewer ID and password from memory. Works much better than other tools.
 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
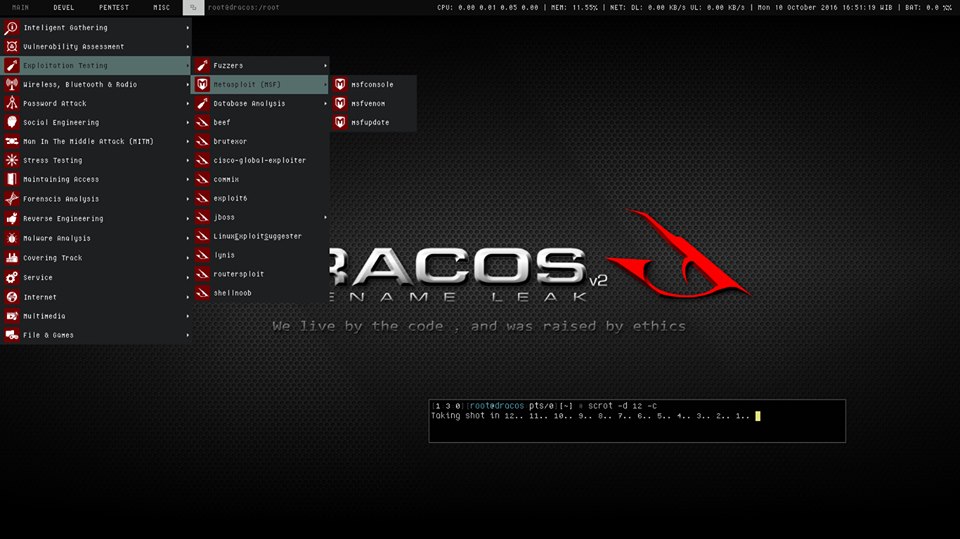 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 emrekybs/douglas-042
Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…
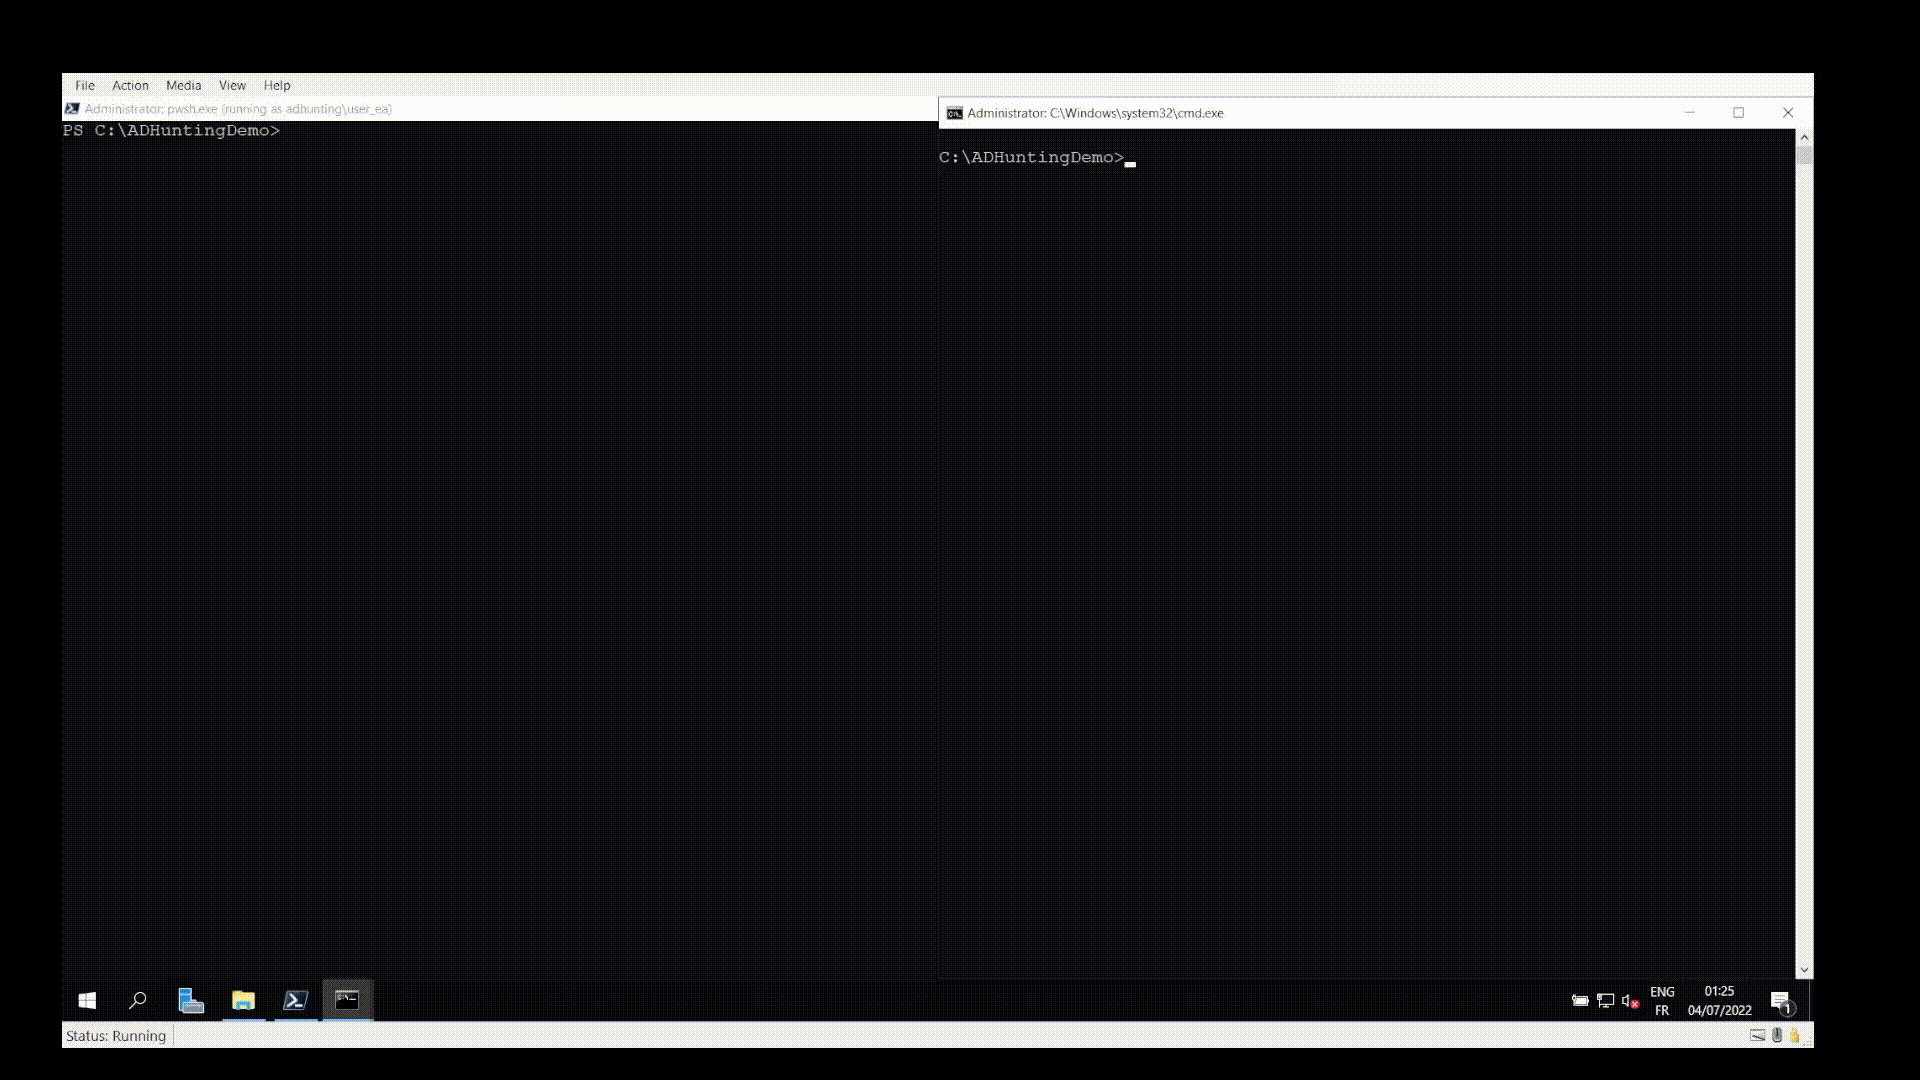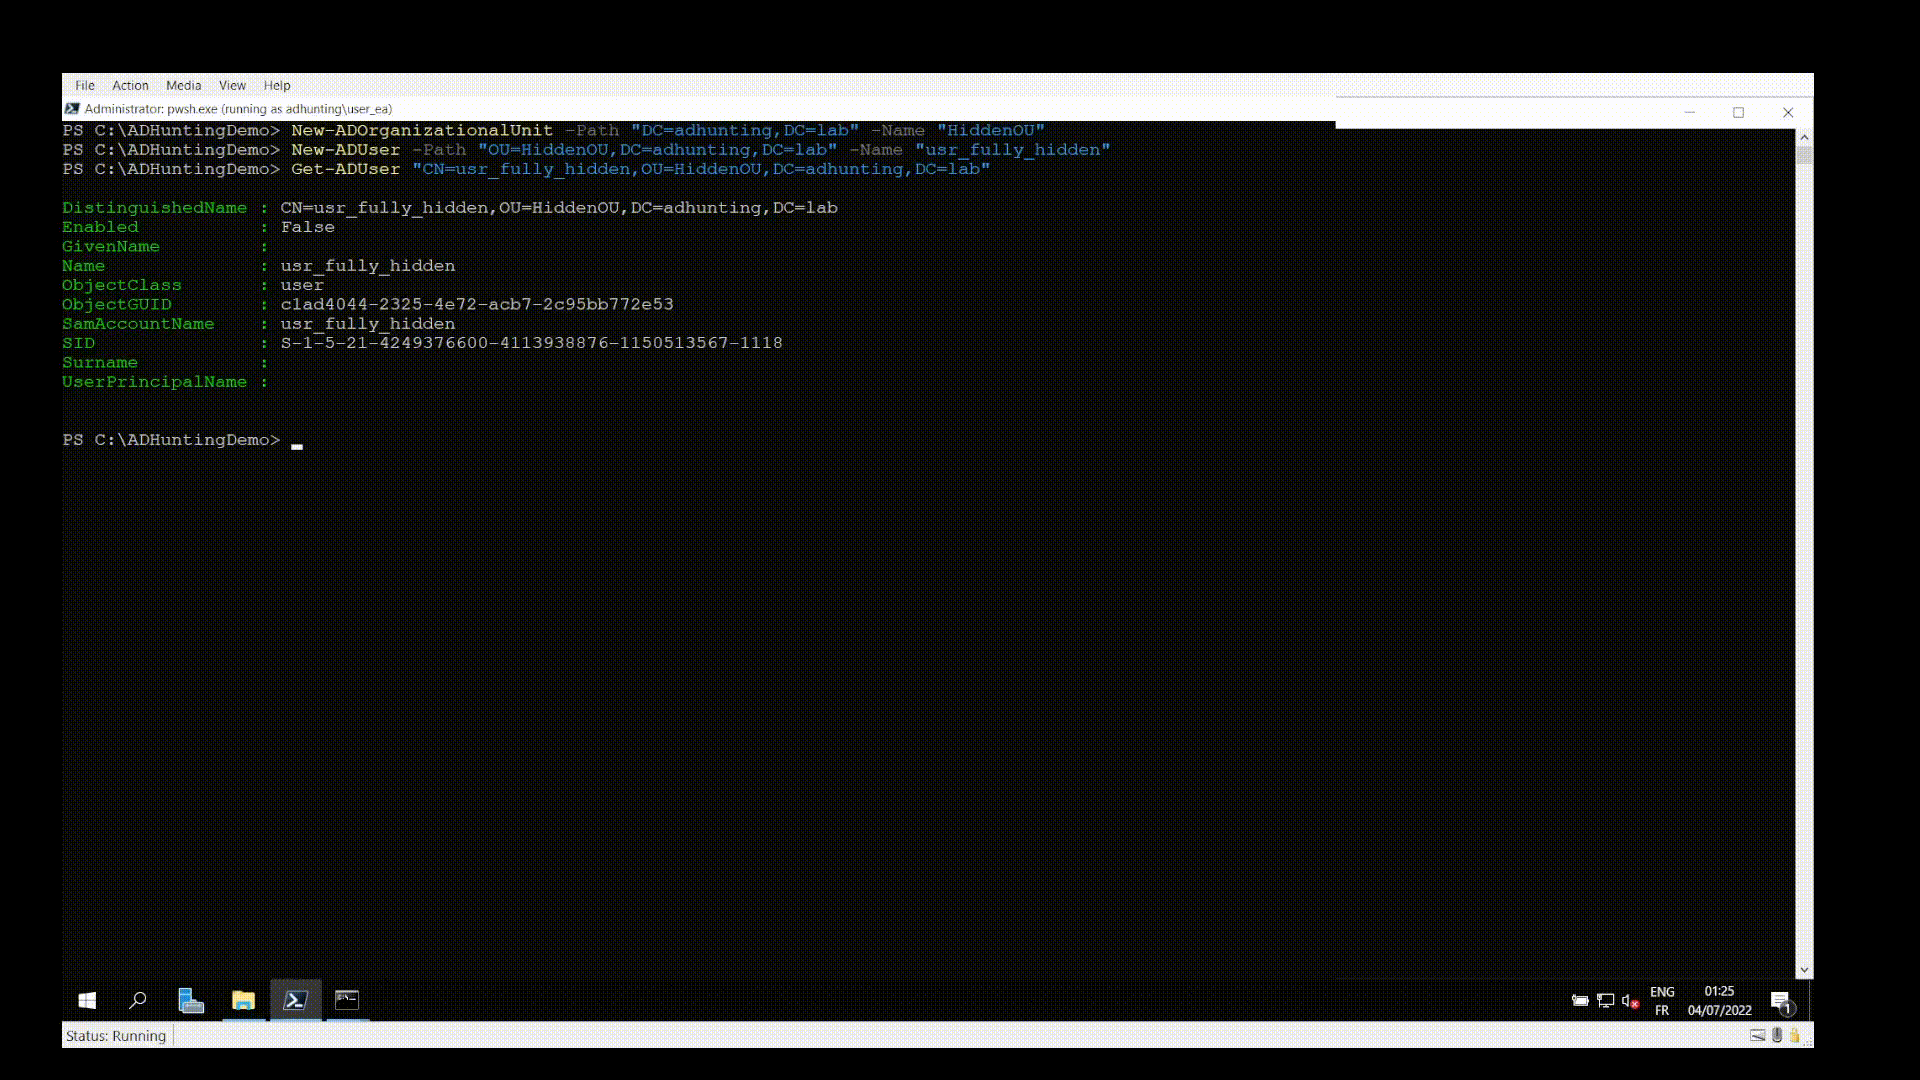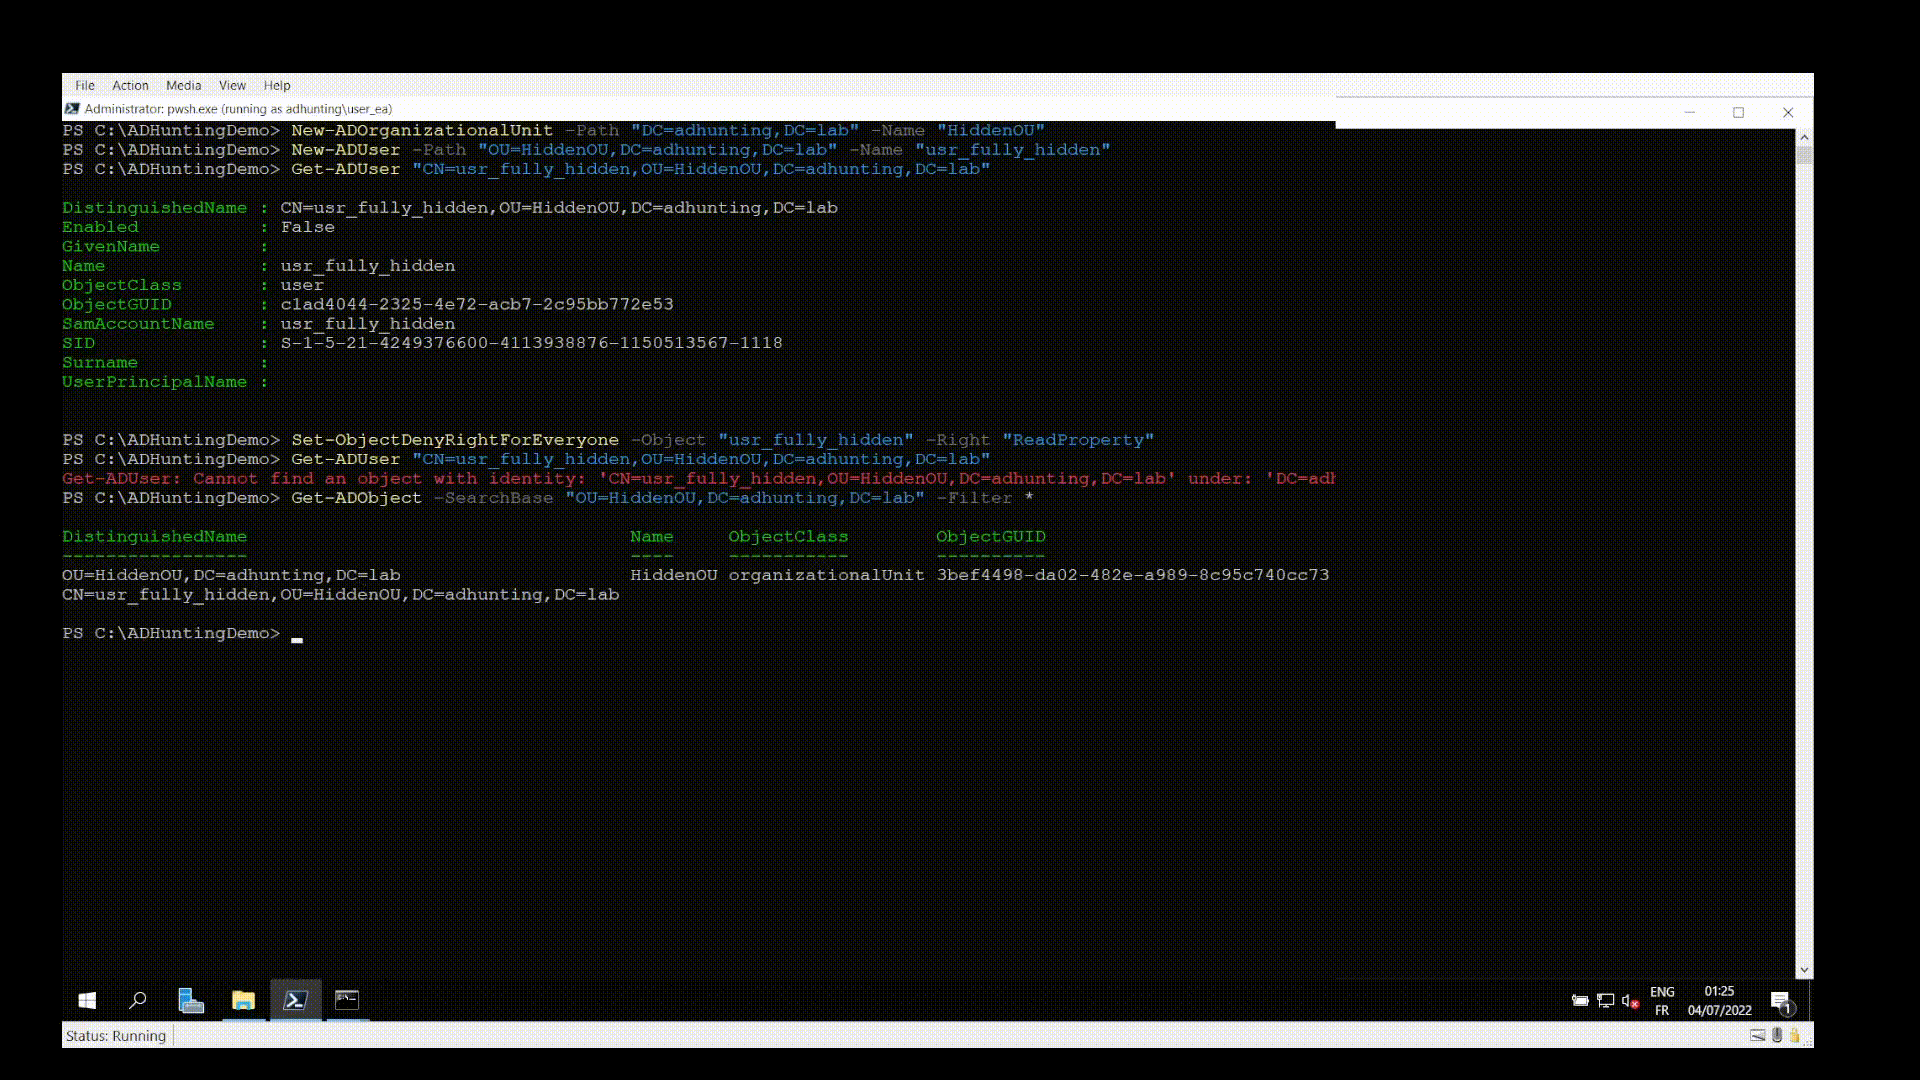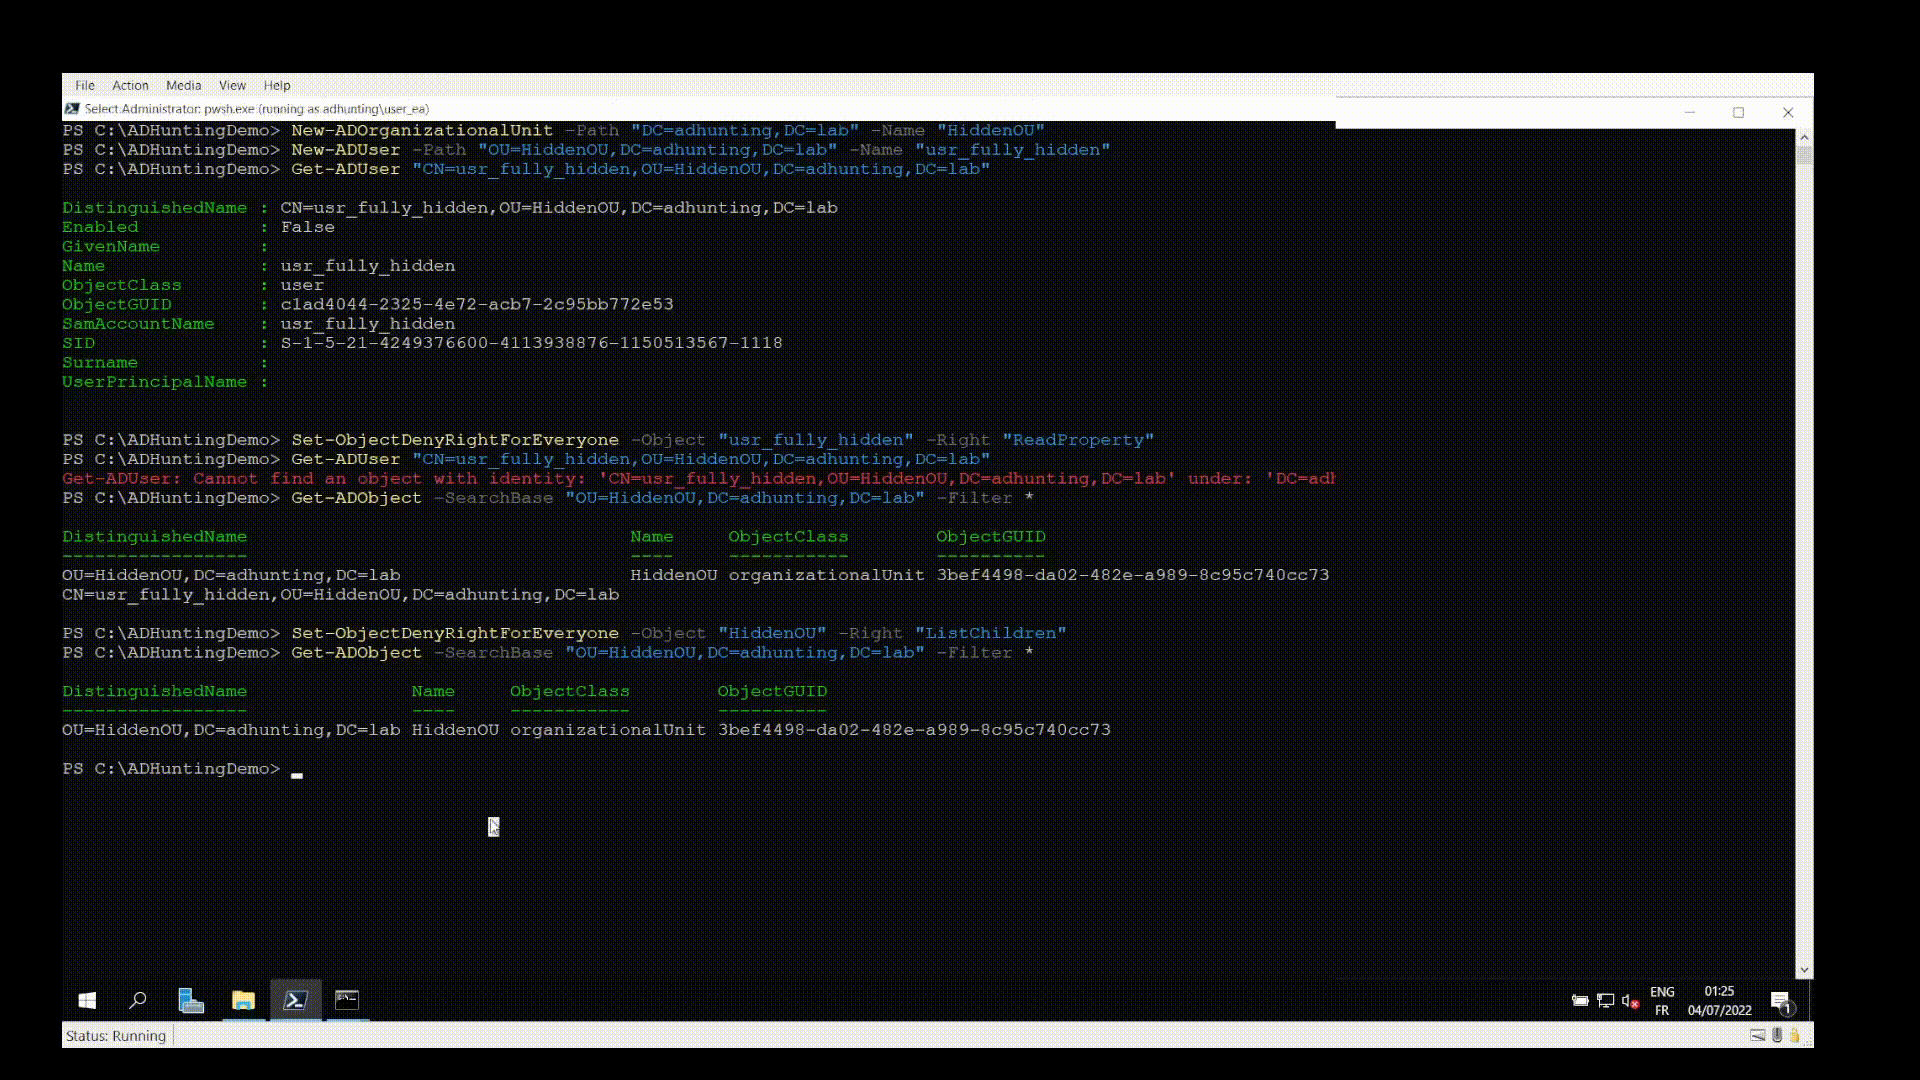 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 d4vinci/chrome-extractor
Python script that will extract all saved passwords from your google chrome database on windows only
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
 lgggreg/skype-log-viewer
Download and View Skype History Without Skype
 circl/factual-rules-generator
Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…
 paul-tew/lifer
Windows link file (shortcuts) examiner
 m0n1x90/exif-gps-tracer
A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in…
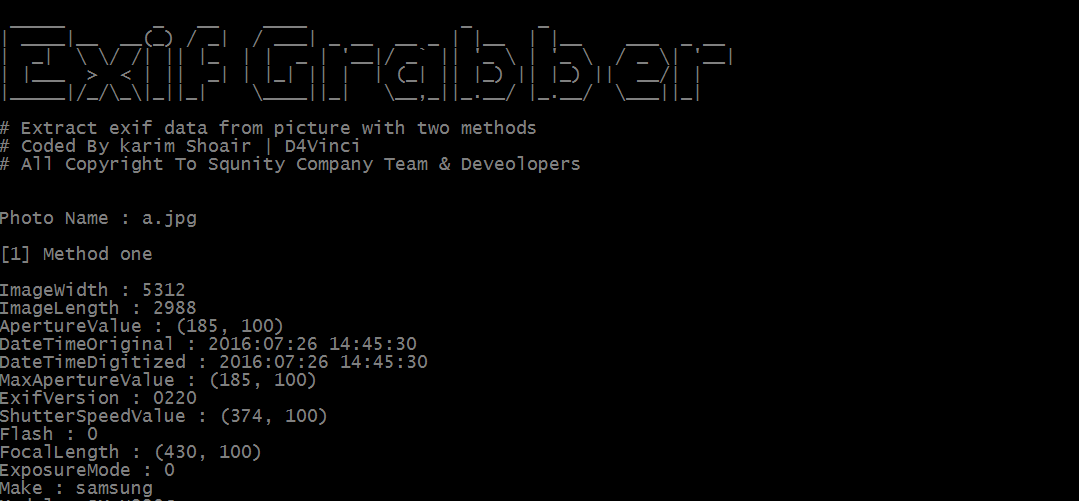 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
 eurecom-s3/linux_screenshot_xwindows
Volatility plugin to extract X screenshots from a memory dump
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally