
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
magika preview

magika

GitHubgoogle/magika

Fast and accurate AI powered file content types detection
code-analysisforensicsgeneral-purpose-utilities+3
18.7k4h 13m ago
copyfail-rs preview

copyfail-rs

GitHubliverwortenuresis371/copyfail-rs

Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
authenticationbinary-exploitationexploitation+7
4 days ago
rikune preview

rikune

GitHublast-emo-boy/rikune

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…

binary-analysisdynamic-analysis-sandboxingeducation+8
24015 days ago
yara preview

yara

GitHubvirustotal/yara

The pattern matching swiss knife

forensicsmalware-analysisstatic-analysis+2
9.9k16 days ago
Office-Malware-Forensics-Lab-REMnux-Static-Analysis preview

Office-Malware-Forensics-Lab-REMnux-Static-Analysis

GitHubmo200909/office-malware-forensics-lab-remnux-static-analysis

Static analysis of 2 malicious Office documents on REMnux using oletools; identified CVE-2017-11882 and obfuscated macros.
code-analysisdigital-forensicseducation+6
24 days ago
hacksguard preview

hacksguard

GitHubrhacknarok/hacksguard

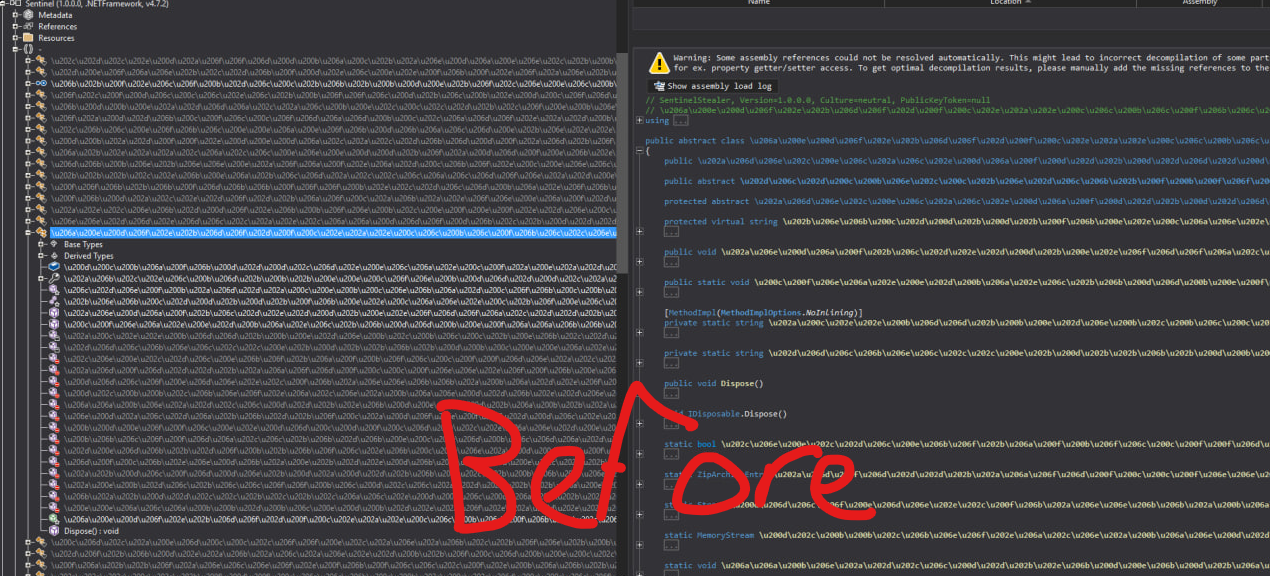
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
binary-analysisforensicsmalware-analysis+2
21329 days ago
UnConfuserEx preview

UnConfuserEx

GitHubzypherion-technologies/unconfuserex

A ConfuserEx2 deobfuscator with support for anti tamper, compressor, constants, control flow, and resource recovery.
binary-analysiscode-analysisdynamic-analysis-sandboxing+6
442 months ago
OffsetInspect preview

OffsetInspect

GitHubwarpedatom/offsetinspect

PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
binary-analysisdefensive-toolsexploitation+8
862 months ago
PolinRider preview

PolinRider

GitHubopensourcemalware/polinrider

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
code-analysiscurated-resourceseducation+8
983 months ago
hedgehog-tools preview

hedgehog-tools

GitHubstruppigel/hedgehog-tools

Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
binary-analysisdynamic-analysis-sandboxingforensics+4
1443 months ago
jsp-webshell-scanner preview

jsp-webshell-scanner

GitHubrespondiq/jsp-webshell-scanner

🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
code-analysisdigital-forensicsforensics+6
13 months ago
glassworm-hunter preview

glassworm-hunter

GitHubafine-com/glassworm-hunter

Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
code-analysisdevsecopseducation+9
304 months ago
browser-xpi-malware-scanner preview

browser-xpi-malware-scanner

GitHubernos/browser-xpi-malware-scanner

A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…
code-analysiseducationforensics+5
85 months ago
hyperhives-macos-infostealer-analysis preview

hyperhives-macos-infostealer-analysis

GitHubdarksp33d/hyperhives-macos-infostealer-analysis

Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
curated-resourceseducationforensics+6
326 months ago
CVE-2025-50422 preview

CVE-2025-50422

GitHublandw-hub/cve-2025-50422

Proof-of-concept for CVE-2025-50422: demonstrates heap memory disclosure in Poppler's pdftocairo, allowing local attackers to recover clear-text PDF…
data-recoverydigital-forensicsexploitation+3
16 months ago
PortEx preview

PortEx

GitHubstruppigel/portex

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
anomaly-detectionbinary-analysisforensics+3
5386 months ago
JarHunter preview

JarHunter

GitHubprophetcraft/jarhunter

JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
binary-analysiscode-analysisdigital-forensics+5
86 months ago
wcw-cyberring-pav-decryptor preview

wcw-cyberring-pav-decryptor

GitHubblakebratcher/wcw-cyberring-pav-decryptor

Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…

binary-analysiscryptographydata-recovery+5
258 months ago
Previous123Next