
Process-Dump
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k1 day ago
glmcdona/process-dumpWindows tool for dumping malware PE files from memory back to disk for analysis.
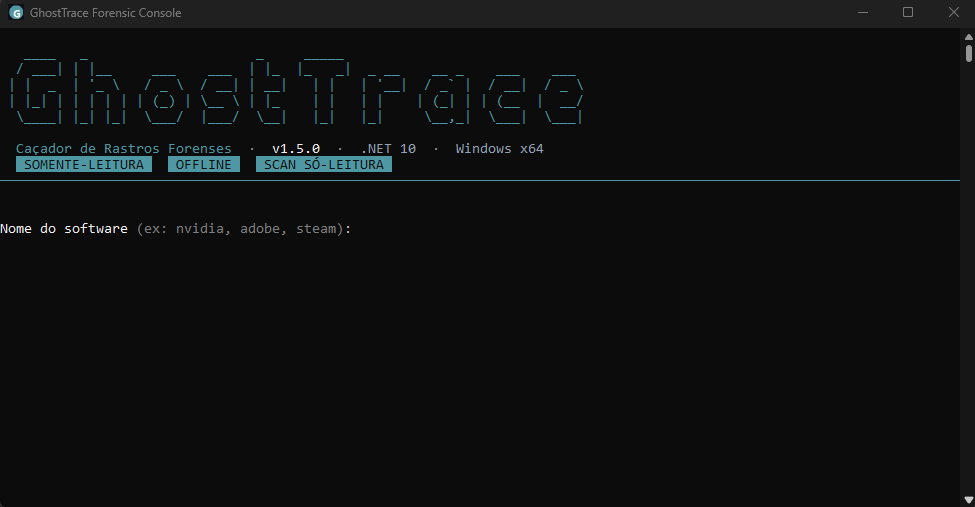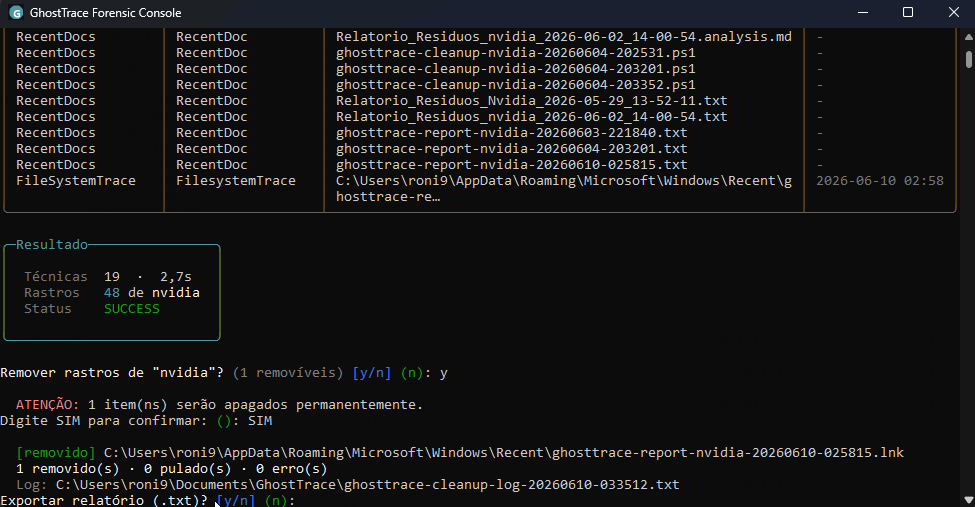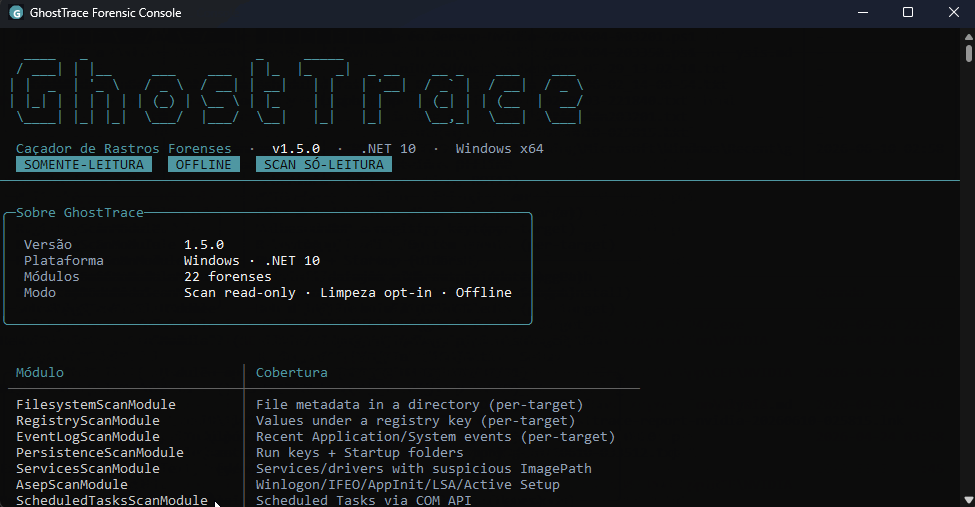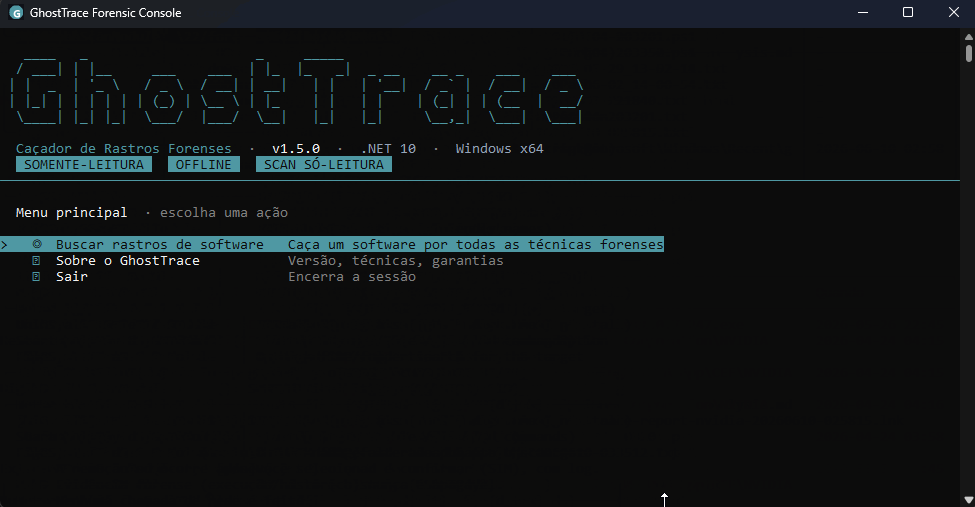 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 momenbasel/htb-writeups
Structured collection of 500+ Hack The Box machine writeups, 400+ challenge solutions, and interactive learning tools including knowledge graphs,…
 grizzzer/cve-2026-42978-poc-research
CVE-2026-42978 — Use-After-Free race condition in Windows Push Notifications (WpnService). Patch diff, root cause analysis, TOCTOU lab, Sysmon/ETW…
 rfxn/cpanel-sessionscribe
Detection, mitigation, and reverse-engineering tooling for CVE-2026-41940 (SessionScribe): the cPanel/WHM unauthenticated session-forgery…
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 msedek/btrfs_fixes
Custom BTRFS repair tools for severe extent tree corruption where btrfs check --repair fails (segfault, loop, or deadlock)
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 busindre/dumpzilla
Extract all forensic interesting information of Firefox, Iceweasel and Seamonkey browsers
 cosmic-zip/witchcraft
WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…
 synacktiv/veeam-velociraptor
Proof-of-concept Velociraptor artifacts pack to showcase a remote Veeam forensics pipeline.
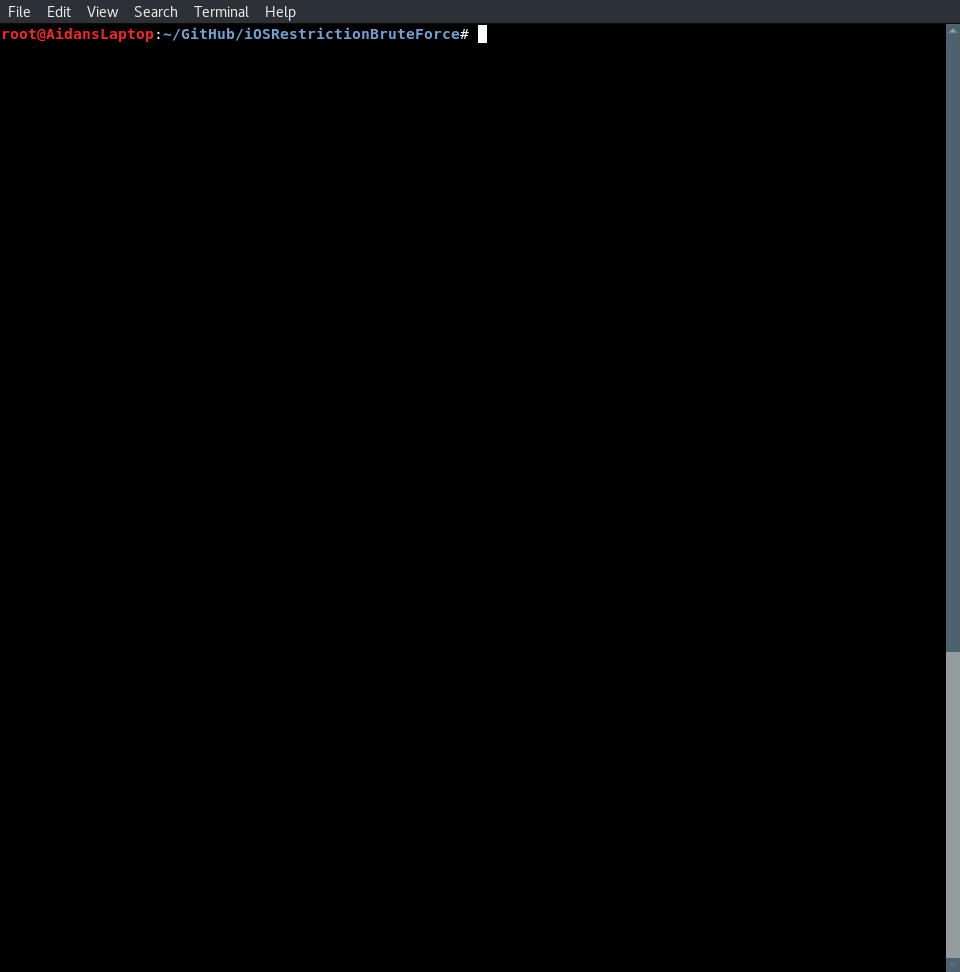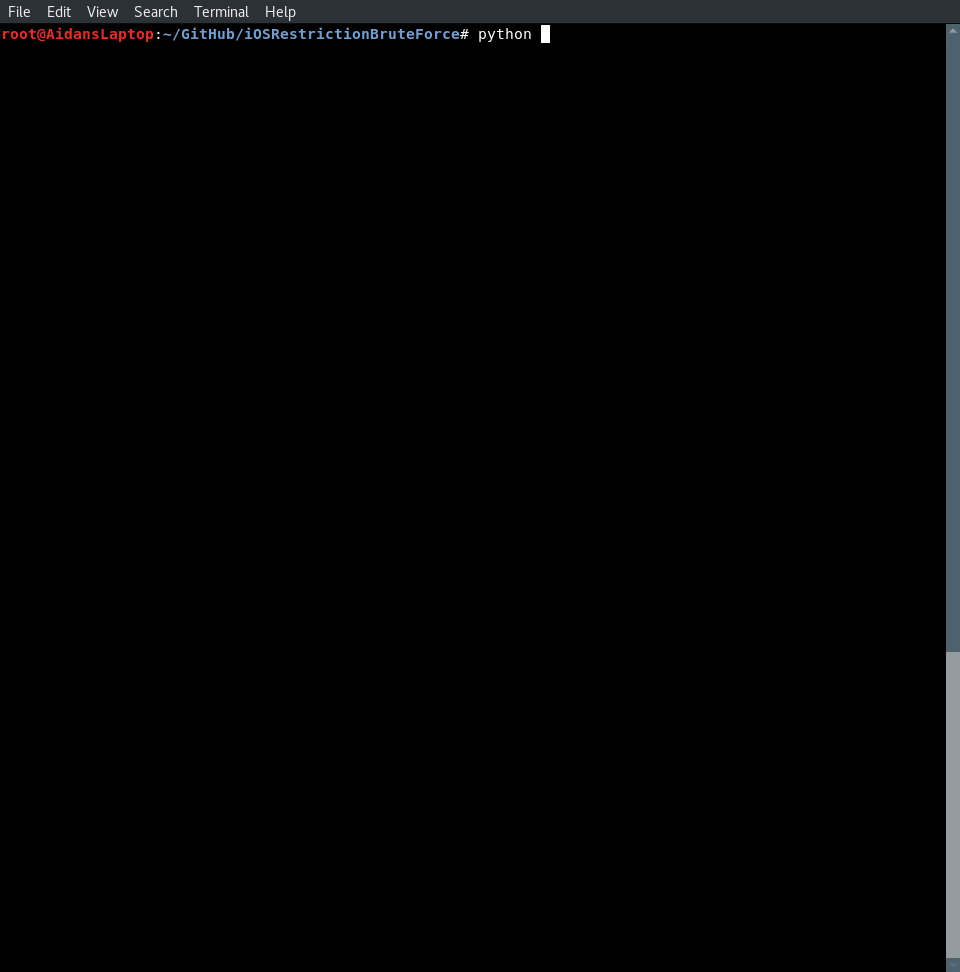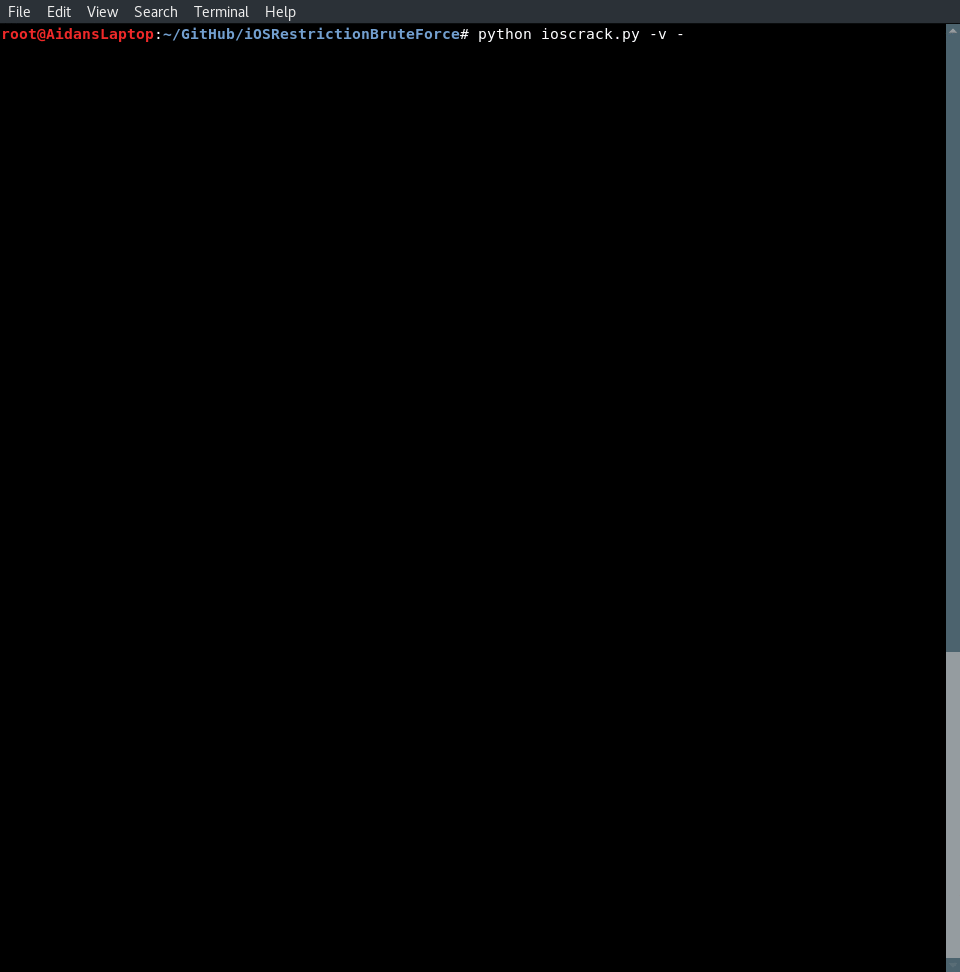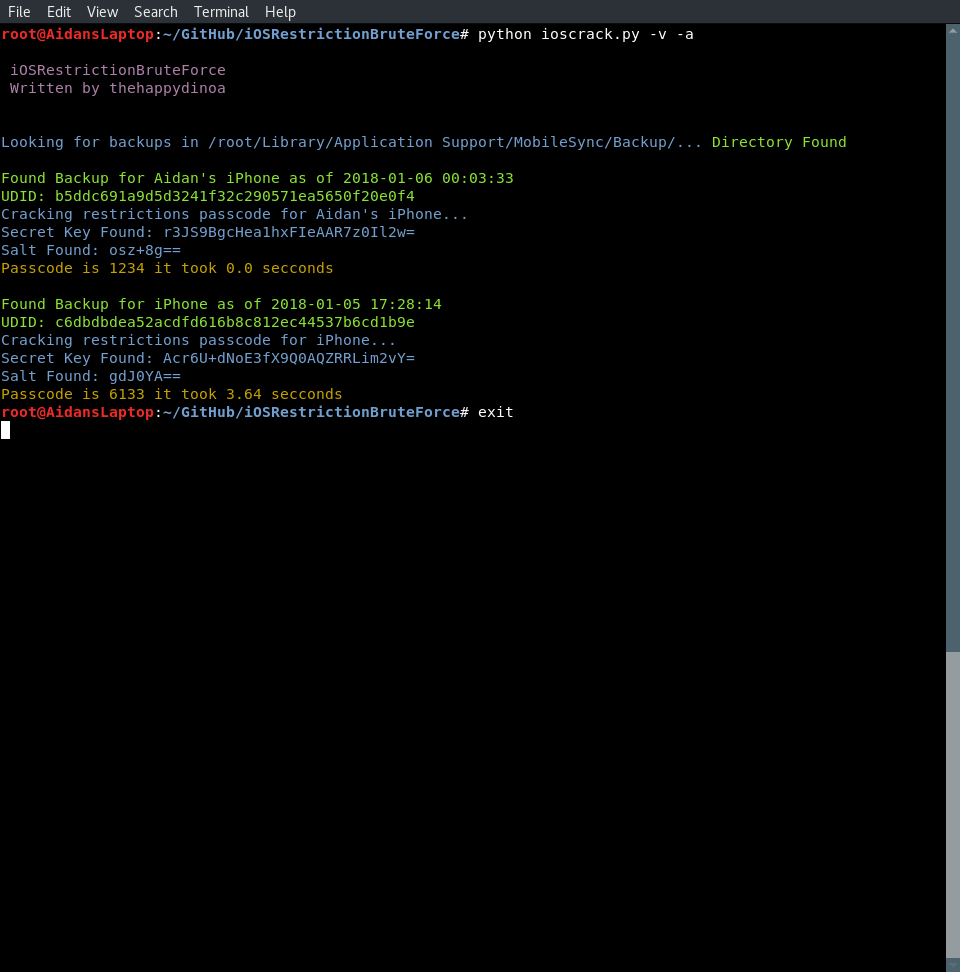 thehappydinoa/iosrestrictionbruteforce
Crack iOS Restriction Passcodes with Python
 ashemery/anti-forensics
A Repository to Track Anti-Forensic Techniques
 hellgatecorp/docxnginxfx
Deep File Forensic. Create or manipulate Wordlists out of Text Documents (ex: for BruteForcing). Save it Line by Line as a Binary .BIN File or as a…
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 yuejd/ios_restriction_passcode_crack---python-version
Crack ios Restriction PassCode in Python