

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
53 results
rustnet preview

rustnet

GitHubdomcyrus/rustnet

Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.

cloud-securitycontainer-securitydns-analysis+5
5.2k17h 27m ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.3k1 day ago
cicd-sensor preview

cicd-sensor

GitLabcicd-sensor/cicd-sensor

eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…

cloud-securitydevsecopsforensics+3
11 day ago
CyberChef preview

CyberChef

GitHubgchq/cyberchef

The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis

binary-analysiscryptographyctf+9
36.2k6 days ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

data-recoverydigital-forensicsdisk-forensics+9
3.1k7 days ago
ptcpdump preview

ptcpdump

GitHubmozillazg/ptcpdump

eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…

cloud-securitycontainer-securitydigital-forensics+5
1.3k15 days ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k19 days ago
clawdstrike preview

clawdstrike

GitHubbackbay-labs/clawdstrike

Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
ai-securitycloud-securitycontainer-security+5
29824 days ago
Nightingale preview

Nightingale

GitHubrajanagori/nightingale

Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
container-securityeducationforensics+7
3151 month ago
mac-monitor preview

mac-monitor

GitHubbrandon7cc/mac-monitor

Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
dynamic-analysis-sandboxingeducationforensics+2
1.4k1 month ago
whatfiles preview

whatfiles

GitHubspieglt/whatfiles

Log what files are accessed by any Linux process

digital-forensicsforensicsgeneral-purpose-utilities
9481 month ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

digital-forensicsforensicsincident-response+3
1.5k1 month ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

digital-forensicsdisk-forensicsforensics+7
3781 month ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
android-securitycryptographydynamic-analysis-sandboxing+8
101 month ago
TransitionPlayer preview

TransitionPlayer

GitHubcanyie/transitionplayer

CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
android-securitybinary-exploitationeducation+4
401 month ago
Douglas-042 preview

Douglas-042

GitHubemrekybs/douglas-042

Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…
forensicsincident-responseinformation-gathering+1
451 month ago
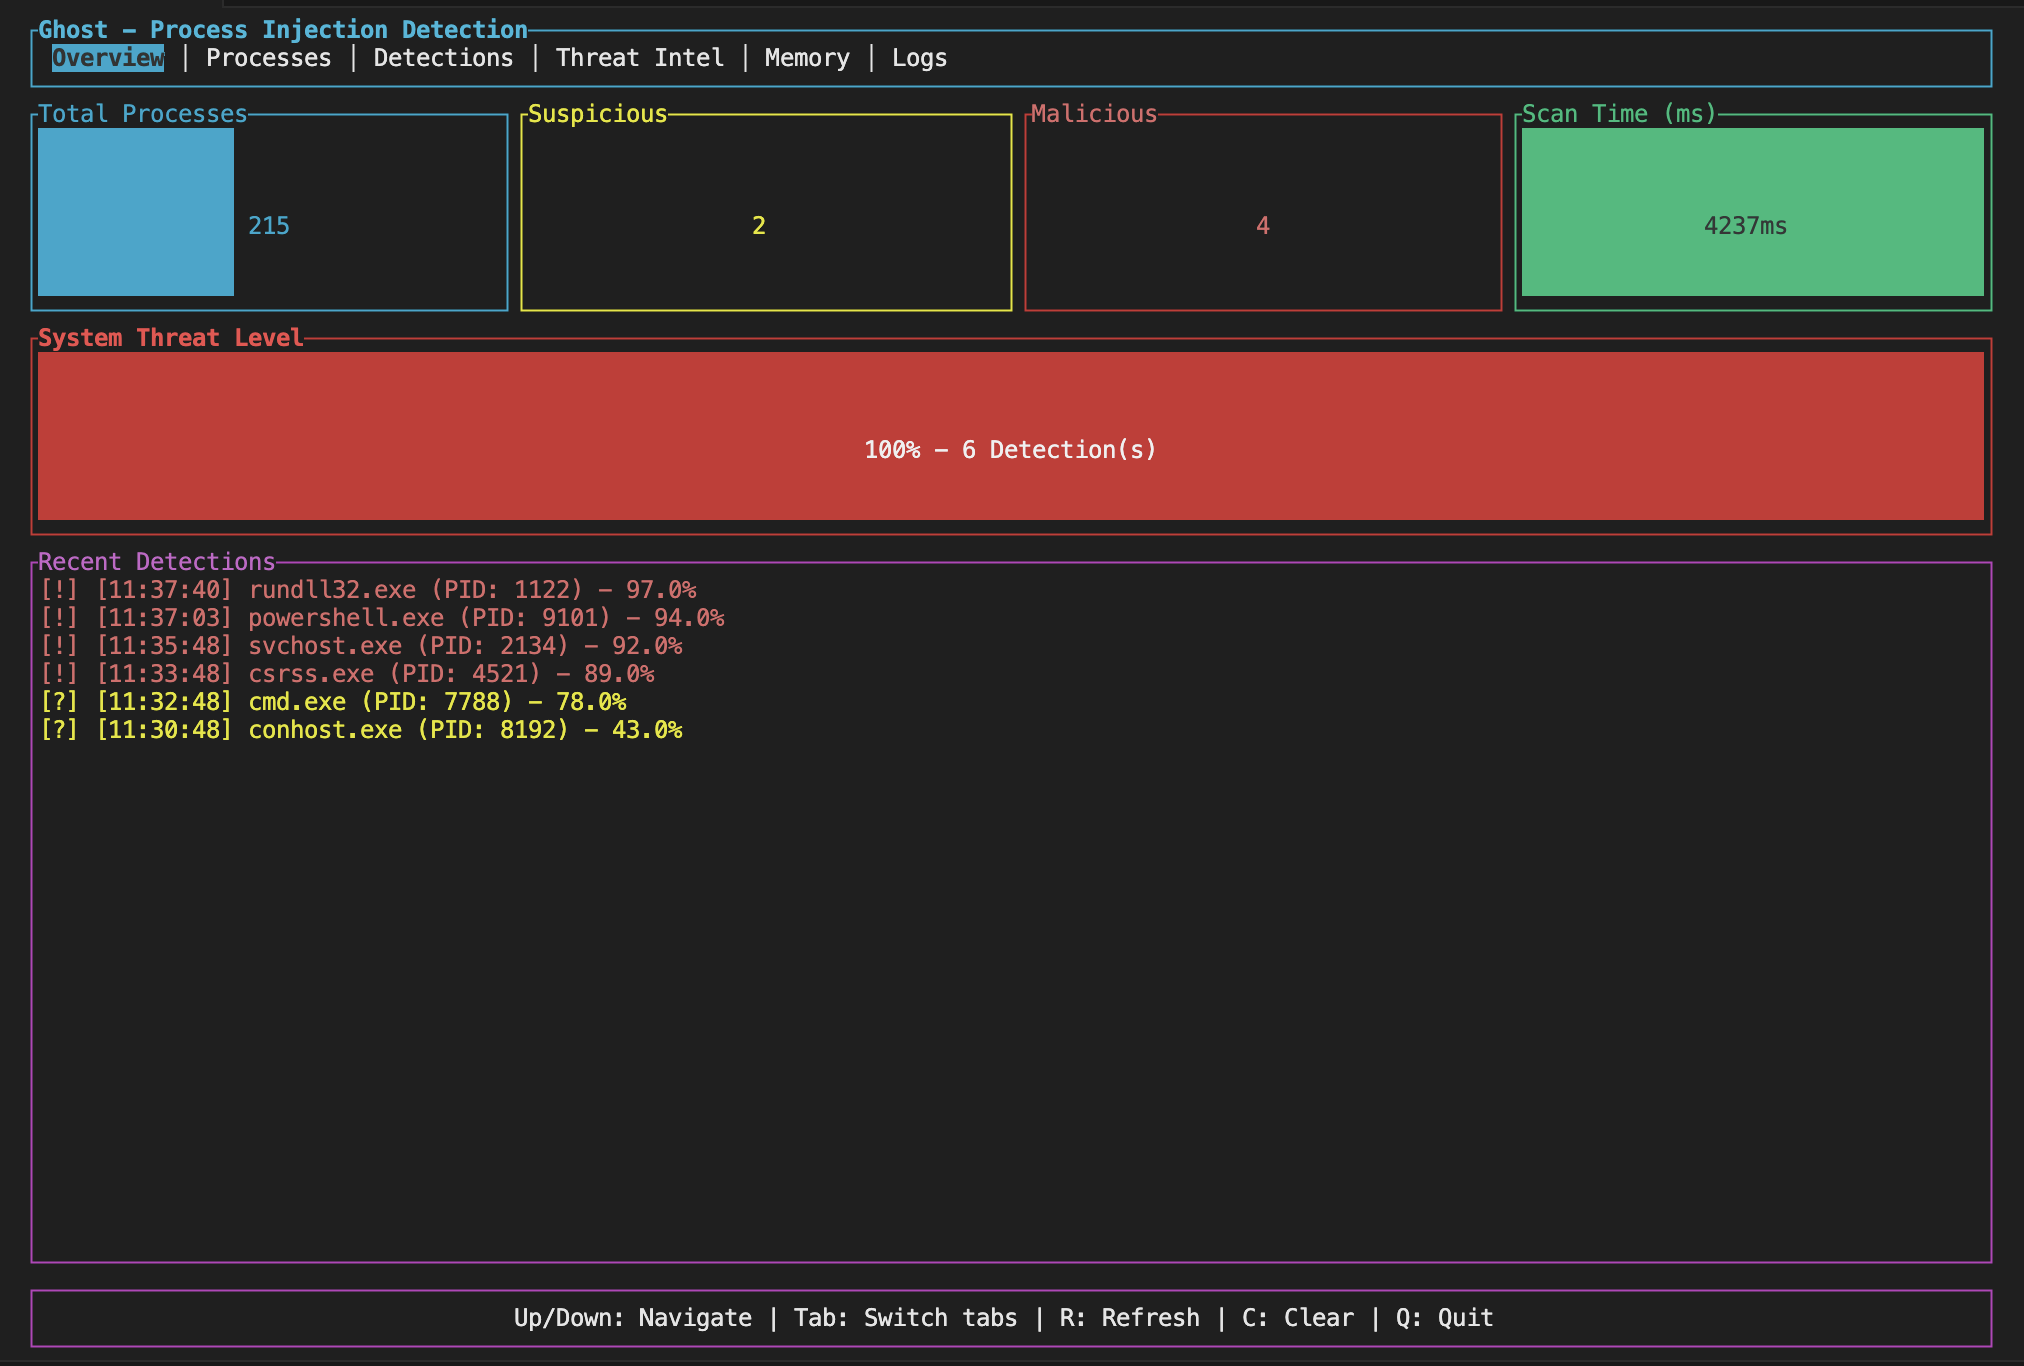
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

binary-analysisdefensive-toolsforensics+6
3922 months ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
253 months ago
Previous123Next