
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
18 results
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
digital-forensicsforensicsincident-response+3
1.5k8 days ago
clawdstrike preview

clawdstrike

GitHubbackbay-labs/clawdstrike

Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
ai-securitycloud-securitycontainer-security+5
28824 days ago
Douglas-042 preview

Douglas-042

GitHubemrekybs/douglas-042

Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…

forensicsincident-responseinformation-gathering+1
4524 days ago
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
binary-analysiseducationforensics+7
22 months ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

binary-analysisforensicsmalware-analysis+2
3.9k3 months ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs

digital-forensicsforensicsioc-management+3
8482 years ago
FACT preview

FACT

GitHubunicornunicode/fact

Collects, processes, and visualizes forensic data from cloud and on-premise machine clusters for incident response and digital investigations.
cloud-securitydigital-forensicsforensics
173 years ago
Skadi preview

Skadi

GitHuborlikoski/skadi

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

curated-resourcesdigital-forensicsdisk-forensics+9
5193 years ago
DMA-ProcessDumper preview

DMA-ProcessDumper

GitHubgmh5225/dma-processdumper

Simple Process Dumper using DMA over a PCIe FPGA device
data-exfiltrationforensicshardware-hacking+3
4 years ago
xpid preview

xpid

GitHubkrisnova/xpid

Linux Process Discovery. C Library, Go bindings, Runtime.
forensicsinformation-gathering
2244 years ago
DetectWindowsCopyOnWriteForAPI preview

DetectWindowsCopyOnWriteForAPI

GitHubnccgroup/detectwindowscopyonwriteforapi

Enumerate various traits from Windows processes as an aid to threat hunting
anomaly-detectiondefensive-toolsforensics+3
1984 years ago
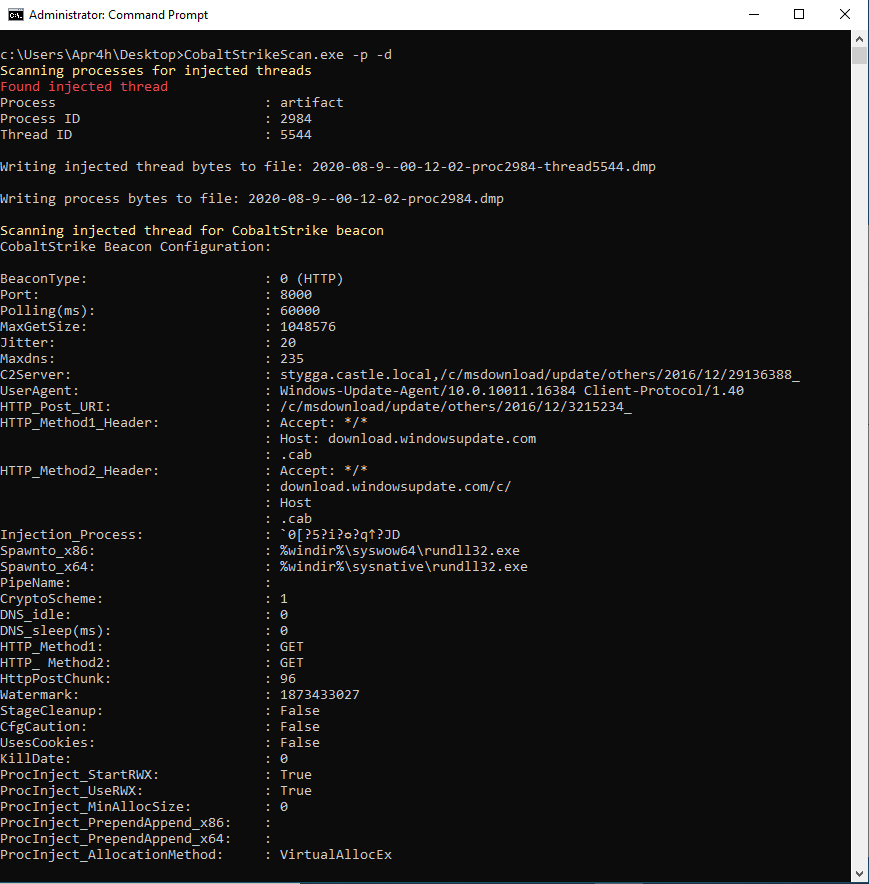
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
9175 years ago
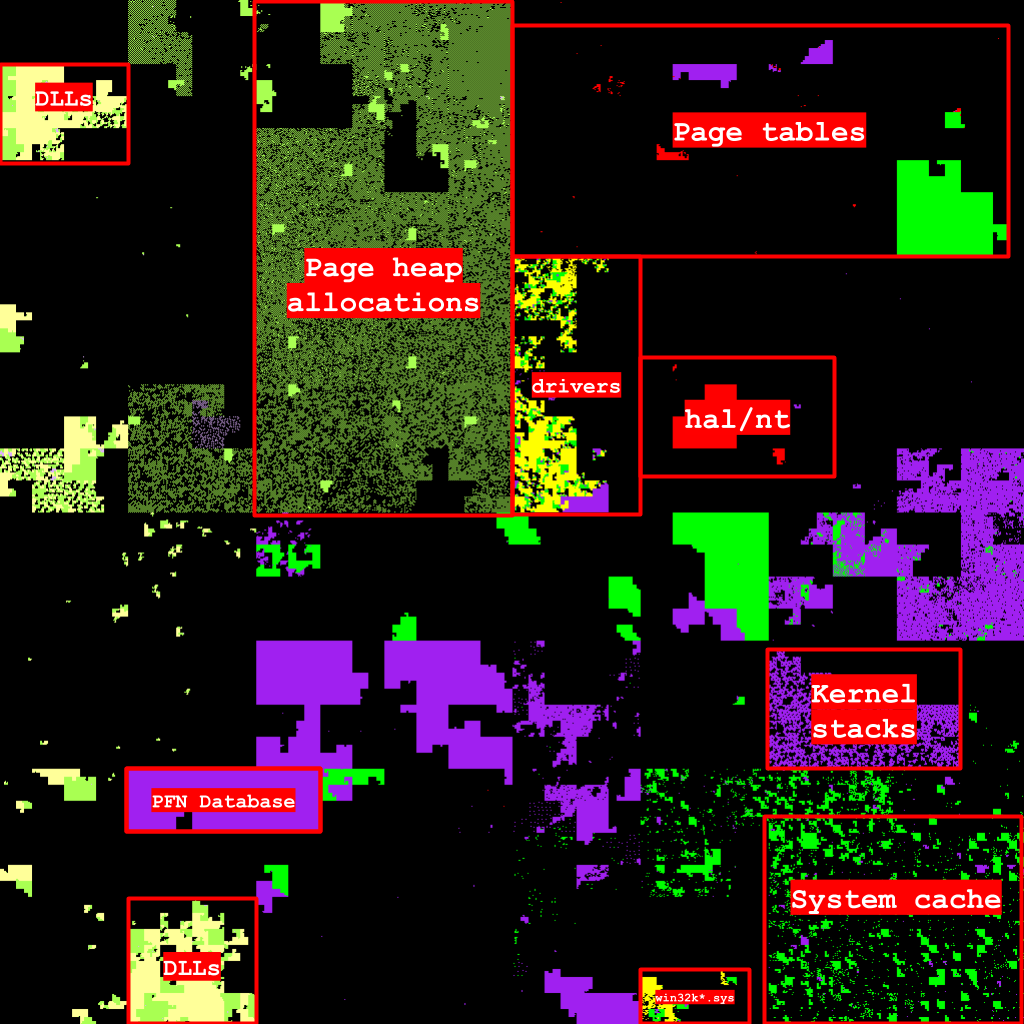
clairvoyance preview

clairvoyance

GitHub0vercl0k/clairvoyance

Visualize the virtual address space of a Windows process on a Hilbert curve.
digital-forensicsforensicsmemory-forensics
3115 years ago
noia preview

noia

GitHub0x742/noia

Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…

android-securitydynamic-analysis-sandboxingforensics+3
1285 years ago
autoresponder preview

autoresponder

GitHublawiet47/autoresponder

Automates incident response tasks via Carbon Black Response API: file/registry deletion, process killing, sensor isolation, binary collection, and…
forensicsincident-response
565 years ago
norimaci preview

norimaci

GitHubmnrkbys/norimaci

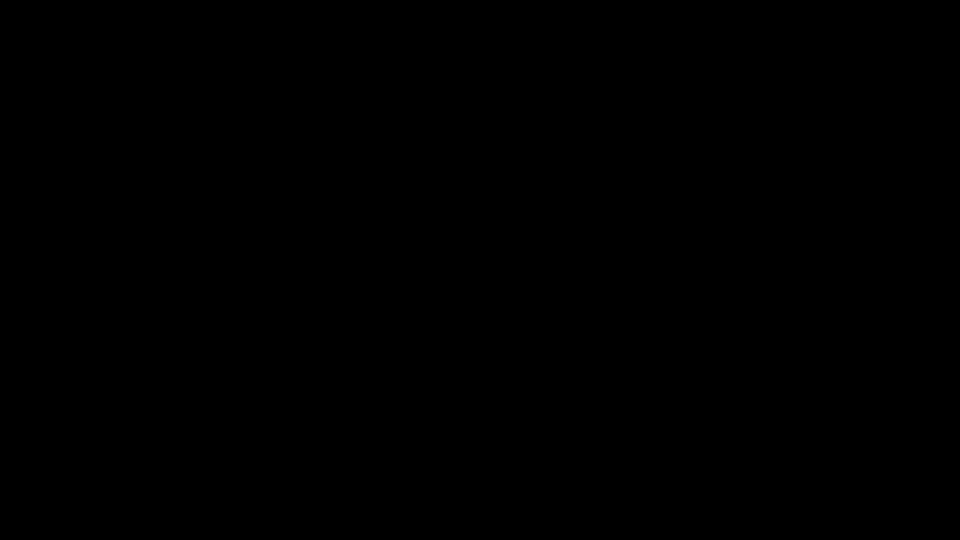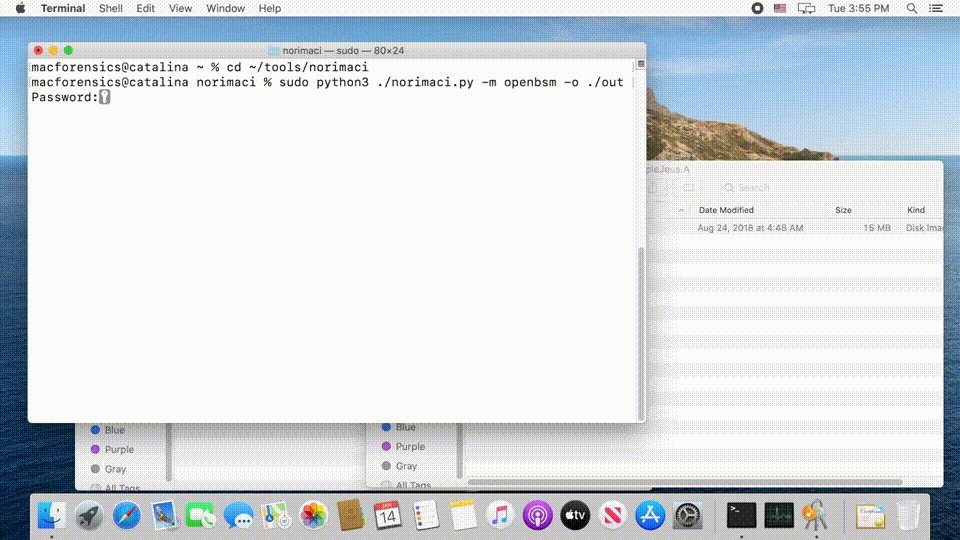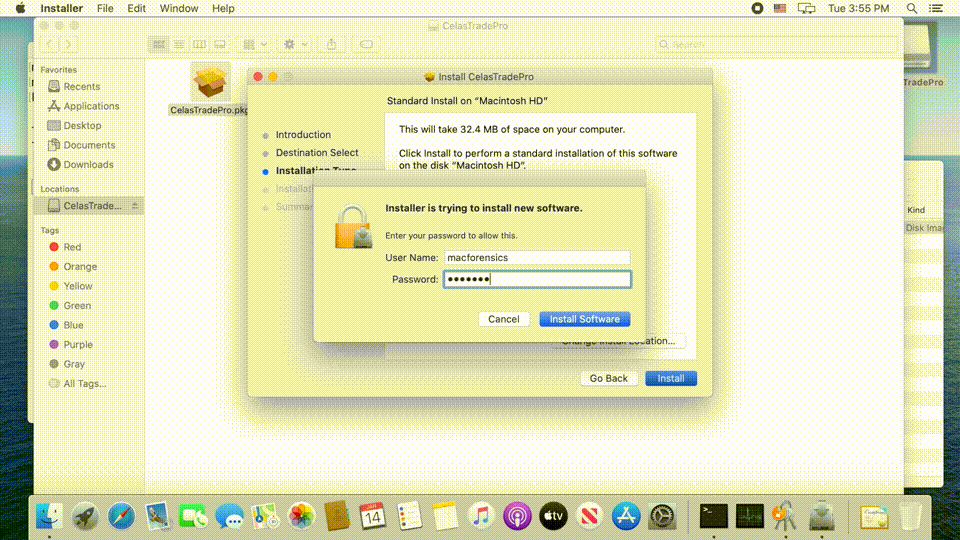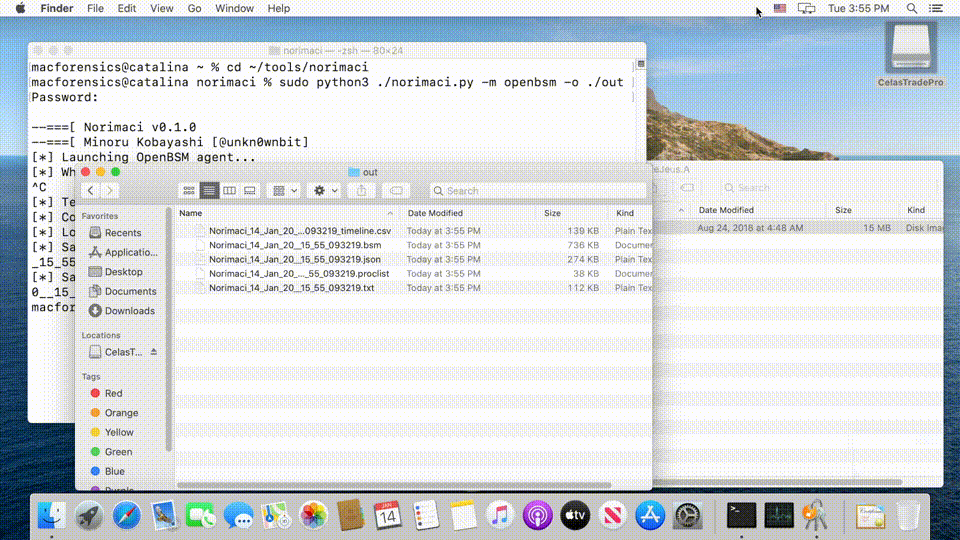
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…

dynamic-analysis-sandboxingforensicsmalware-analysis
716 years ago
An-Integrated-Wireless-Network-Forensic-Analysis-Framework preview

An-Integrated-Wireless-Network-Forensic-Analysis-Framework

GitHubbenadia/an-integrated-wireless-network-forensic-analysis-framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
digital-forensicsforensicsnetwork-forensics+2
68 years ago
vboxdie-cracker preview

vboxdie-cracker

GitHubsinfocol/vboxdie-cracker

VirtualBox Disk Image Encryption password cracker

encryption-decryption-toolsforensicspassword-cracking
3310 years ago