
pacmap
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
dns-analysisforensicsincident-response+4
m0vi0/pacmapGraph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
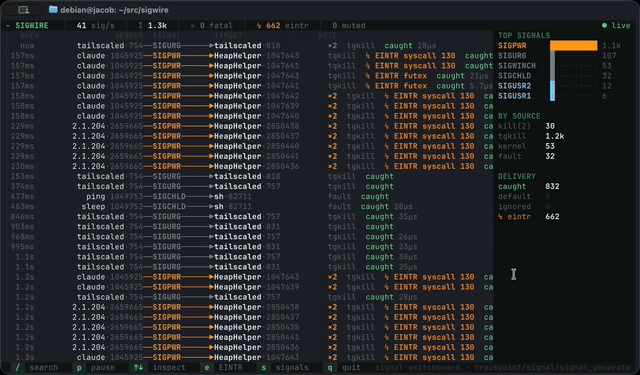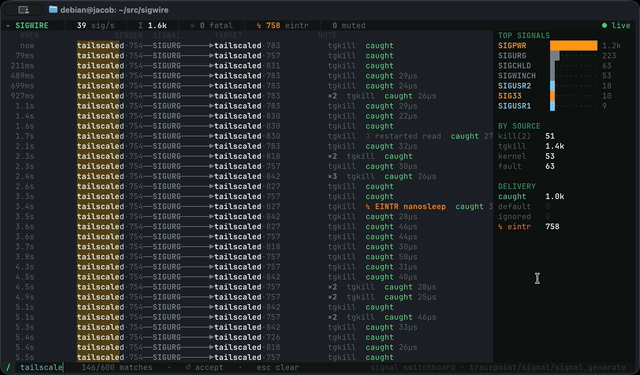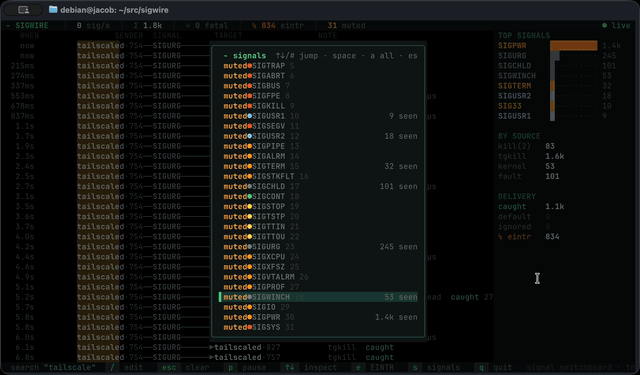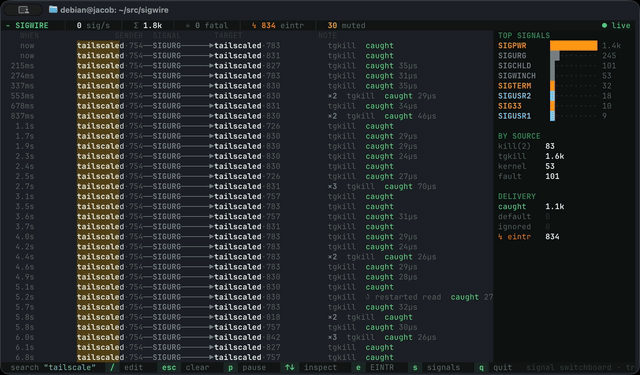 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 gilberto47831/network-filesystem-forensics
Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)
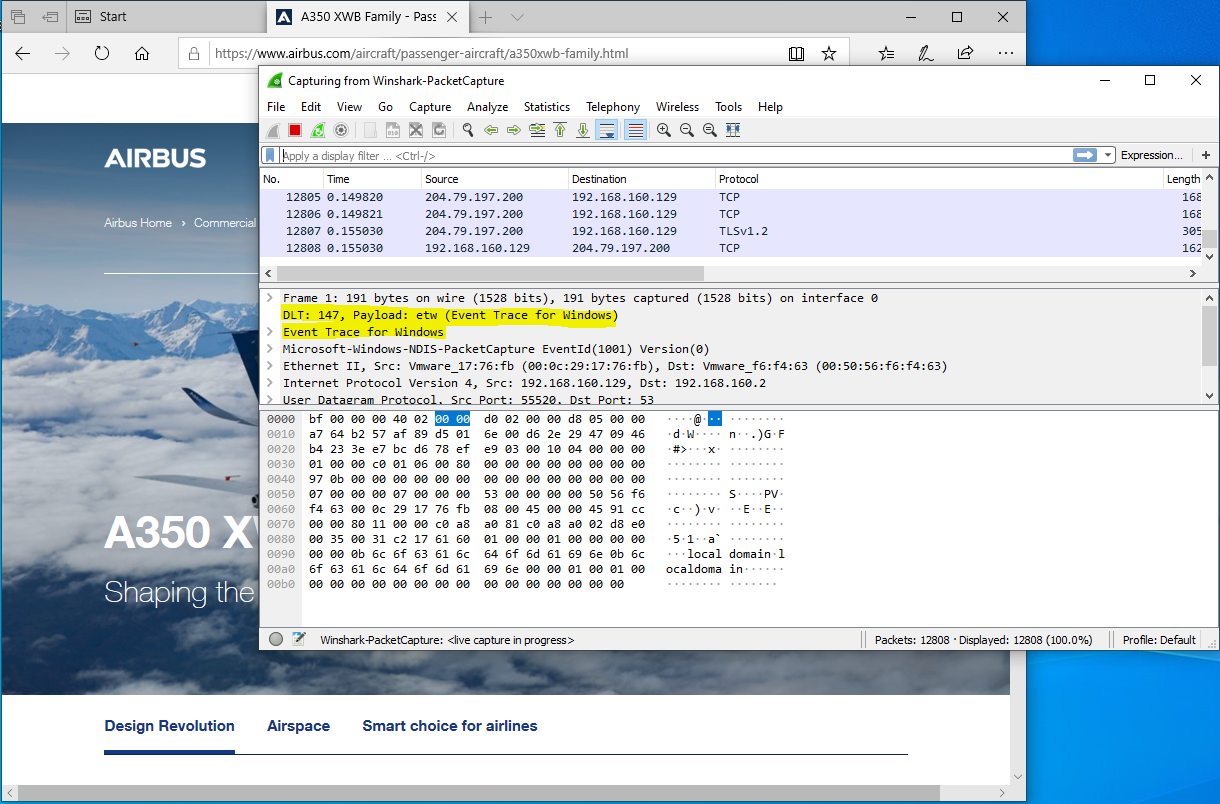 airbus-cert/winshark
A wireshark plugin to instrument ETW
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture