

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
29 results
sleuthkit preview

sleuthkit

GitHubsleuthkit/sleuthkit

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

data-recoverydigital-forensicsdisk-forensics+3
3.2k
2 days ago
Veto preview

Veto

GitHubprofessorquantumuniverse/veto

Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
android-securitydynamic-analysis-sandboxingforensics+8
1914 days ago
PortEx preview

PortEx

GitHubstruppigel/portex

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
anomaly-detectionbinary-analysisforensics+3
5386 months ago
PCredz preview

PCredz

GitHublgandx/pcredz

This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
forensicsinformation-gatheringnetwork-security+3
2.6k7 months ago
hashr preview

hashr

GitHubgoogle/hashr

Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…

digital-forensicsdisk-forensicsforensics+2
1337 months ago
dotnetfile preview

dotnetfile

GitHubpan-unit42/dotnetfile

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
binary-analysisforensicshash-analysis+4
1187 months ago
HashTag preview

HashTag

GitHubsmeegesec/hashtag

Password Hash Identification

digital-forensicsforensicshash-analysis+3
2228 months ago
MongoBleed-DFIR-Triage-Script-CVE-2025-14847 preview

MongoBleed-DFIR-Triage-Script-CVE-2025-14847

GitHubjemhadar/mongobleed-dfir-triage-script-cve-2025-14847

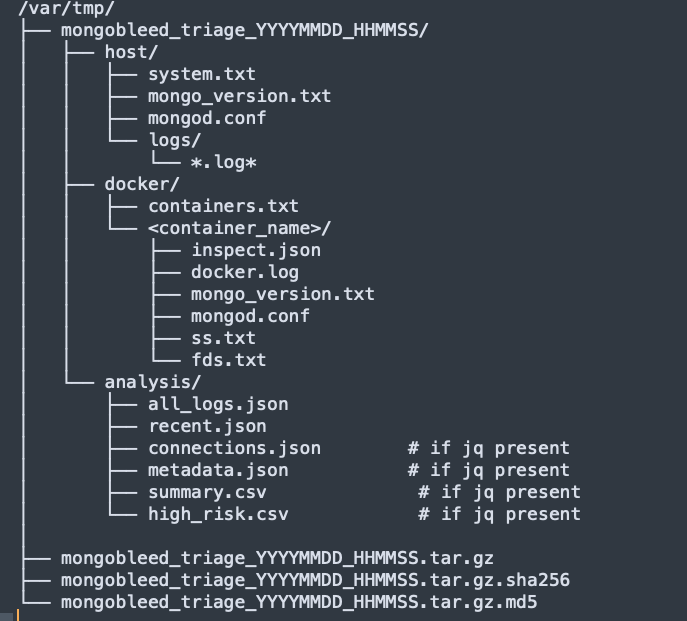
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
container-securitydatabase-securitydigital-forensics+5
9 months ago
vt-py-scanner preview

vt-py-scanner

GitHubneorai/vt-py-scanner

Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…

forensicshash-analysisinformation-gathering+3
610 months ago
DeadMatter preview

DeadMatter

GitHubqsecure-labs/deadmatter

Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
691 year ago
PortexAnalyzerGUI preview

PortexAnalyzerGUI

GitHubstruppigel/portexanalyzergui

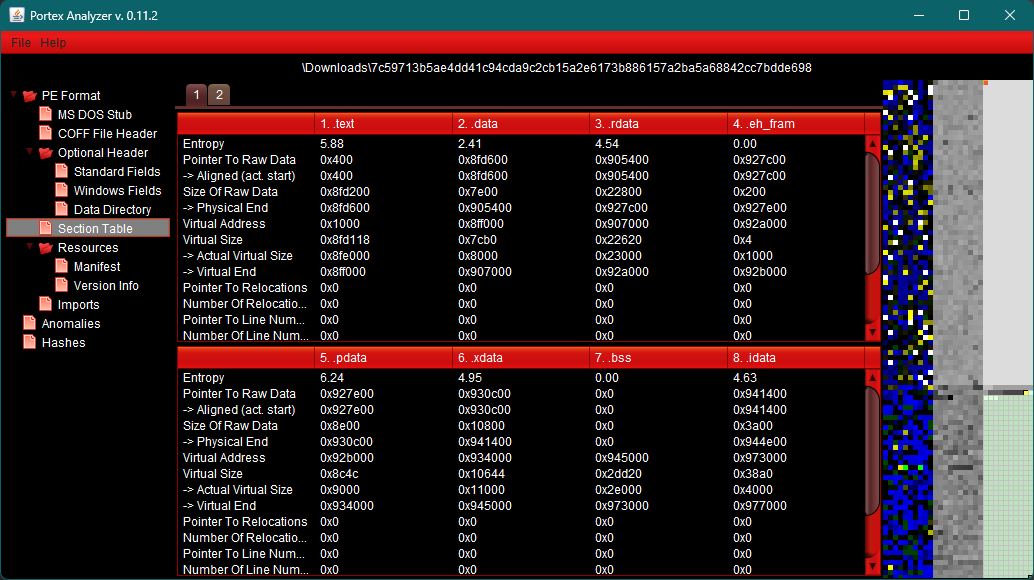
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library

binary-analysisforensicshash-analysis+3
1511 year ago
RCLocals preview

RCLocals

GitHubyjesus/rclocals

Linux startup analyzer

defensive-toolsforensicshash-analysis+4
651 year ago
CVE-2023-32784-password-combinator-fixer preview

CVE-2023-32784-password-combinator-fixer

GitHubg4sp4rcs/cve-2023-32784-password-combinator-fixer

After using the KeePass password dumper maybe some character parsed as ● is incorrect and you want to know the real character
data-recoveryexploitationforensics+2
1 year ago
FileWatchTower preview

FileWatchTower

GitHubiomoath/filewatchtower

FWT is a security analysis and file monitoring tool that utilizes Sysmon events.

digital-forensicsforensicshash-analysis+4
292 years ago
sandfly-entropyscan preview

sandfly-entropyscan

GitHubsandflysecurity/sandfly-entropyscan

Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
binary-analysisforensicsincident-response+1
1702 years ago
DataSurgeon preview

DataSurgeon

GitHubdrew-alleman/datasurgeon

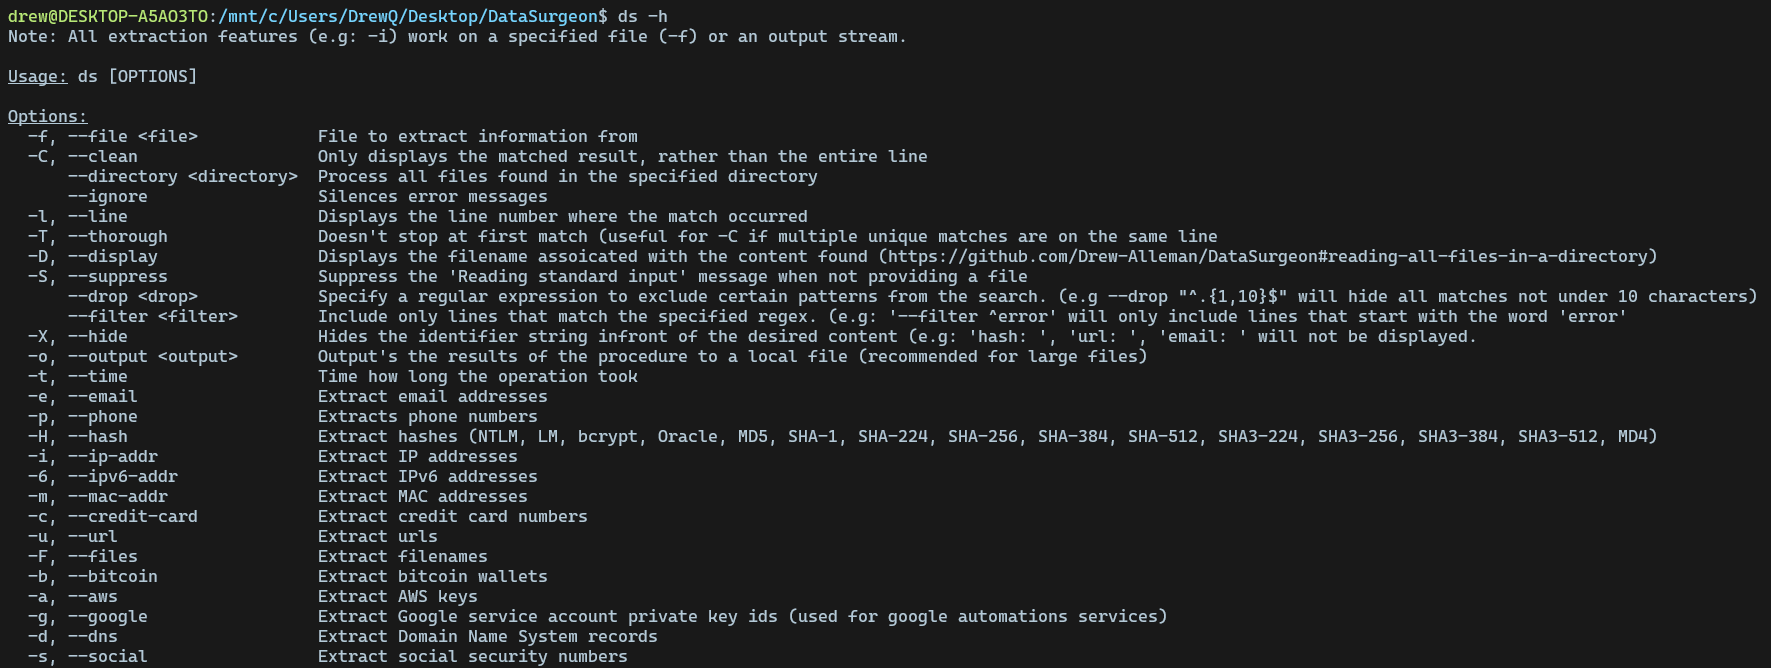
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
ctfdata-exfiltrationforensics+6
9062 years ago
NTLMRawUnHide preview

NTLMRawUnHide

GitHubmlgualtieri/ntlmrawunhide

NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…

forensicsinformation-gatheringnetwork-security+2
3932 years ago
Random-Scripts preview

Random-Scripts

GitHubstar-sg/random-scripts

Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…

digital-forensicsforensicshash-analysis+5
23 years ago
Previous12Next