


 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 vulnex/bytesrevealer
Online Reverse Enginerring viewer
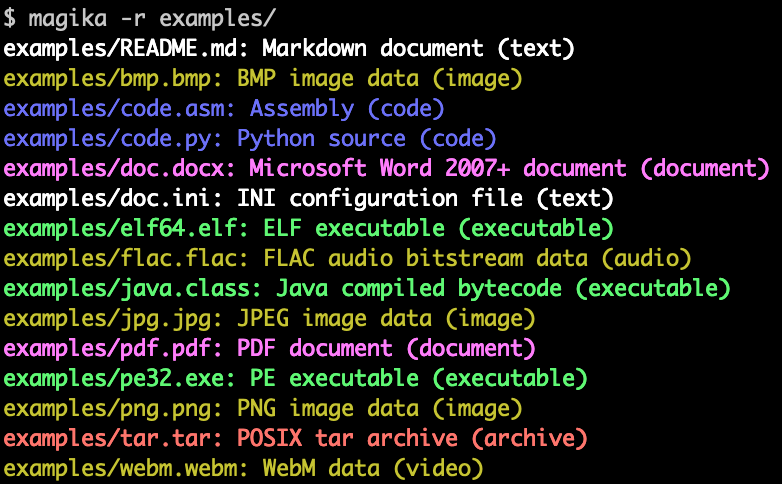 google/magika
Fast and accurate AI powered file content types detection

 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
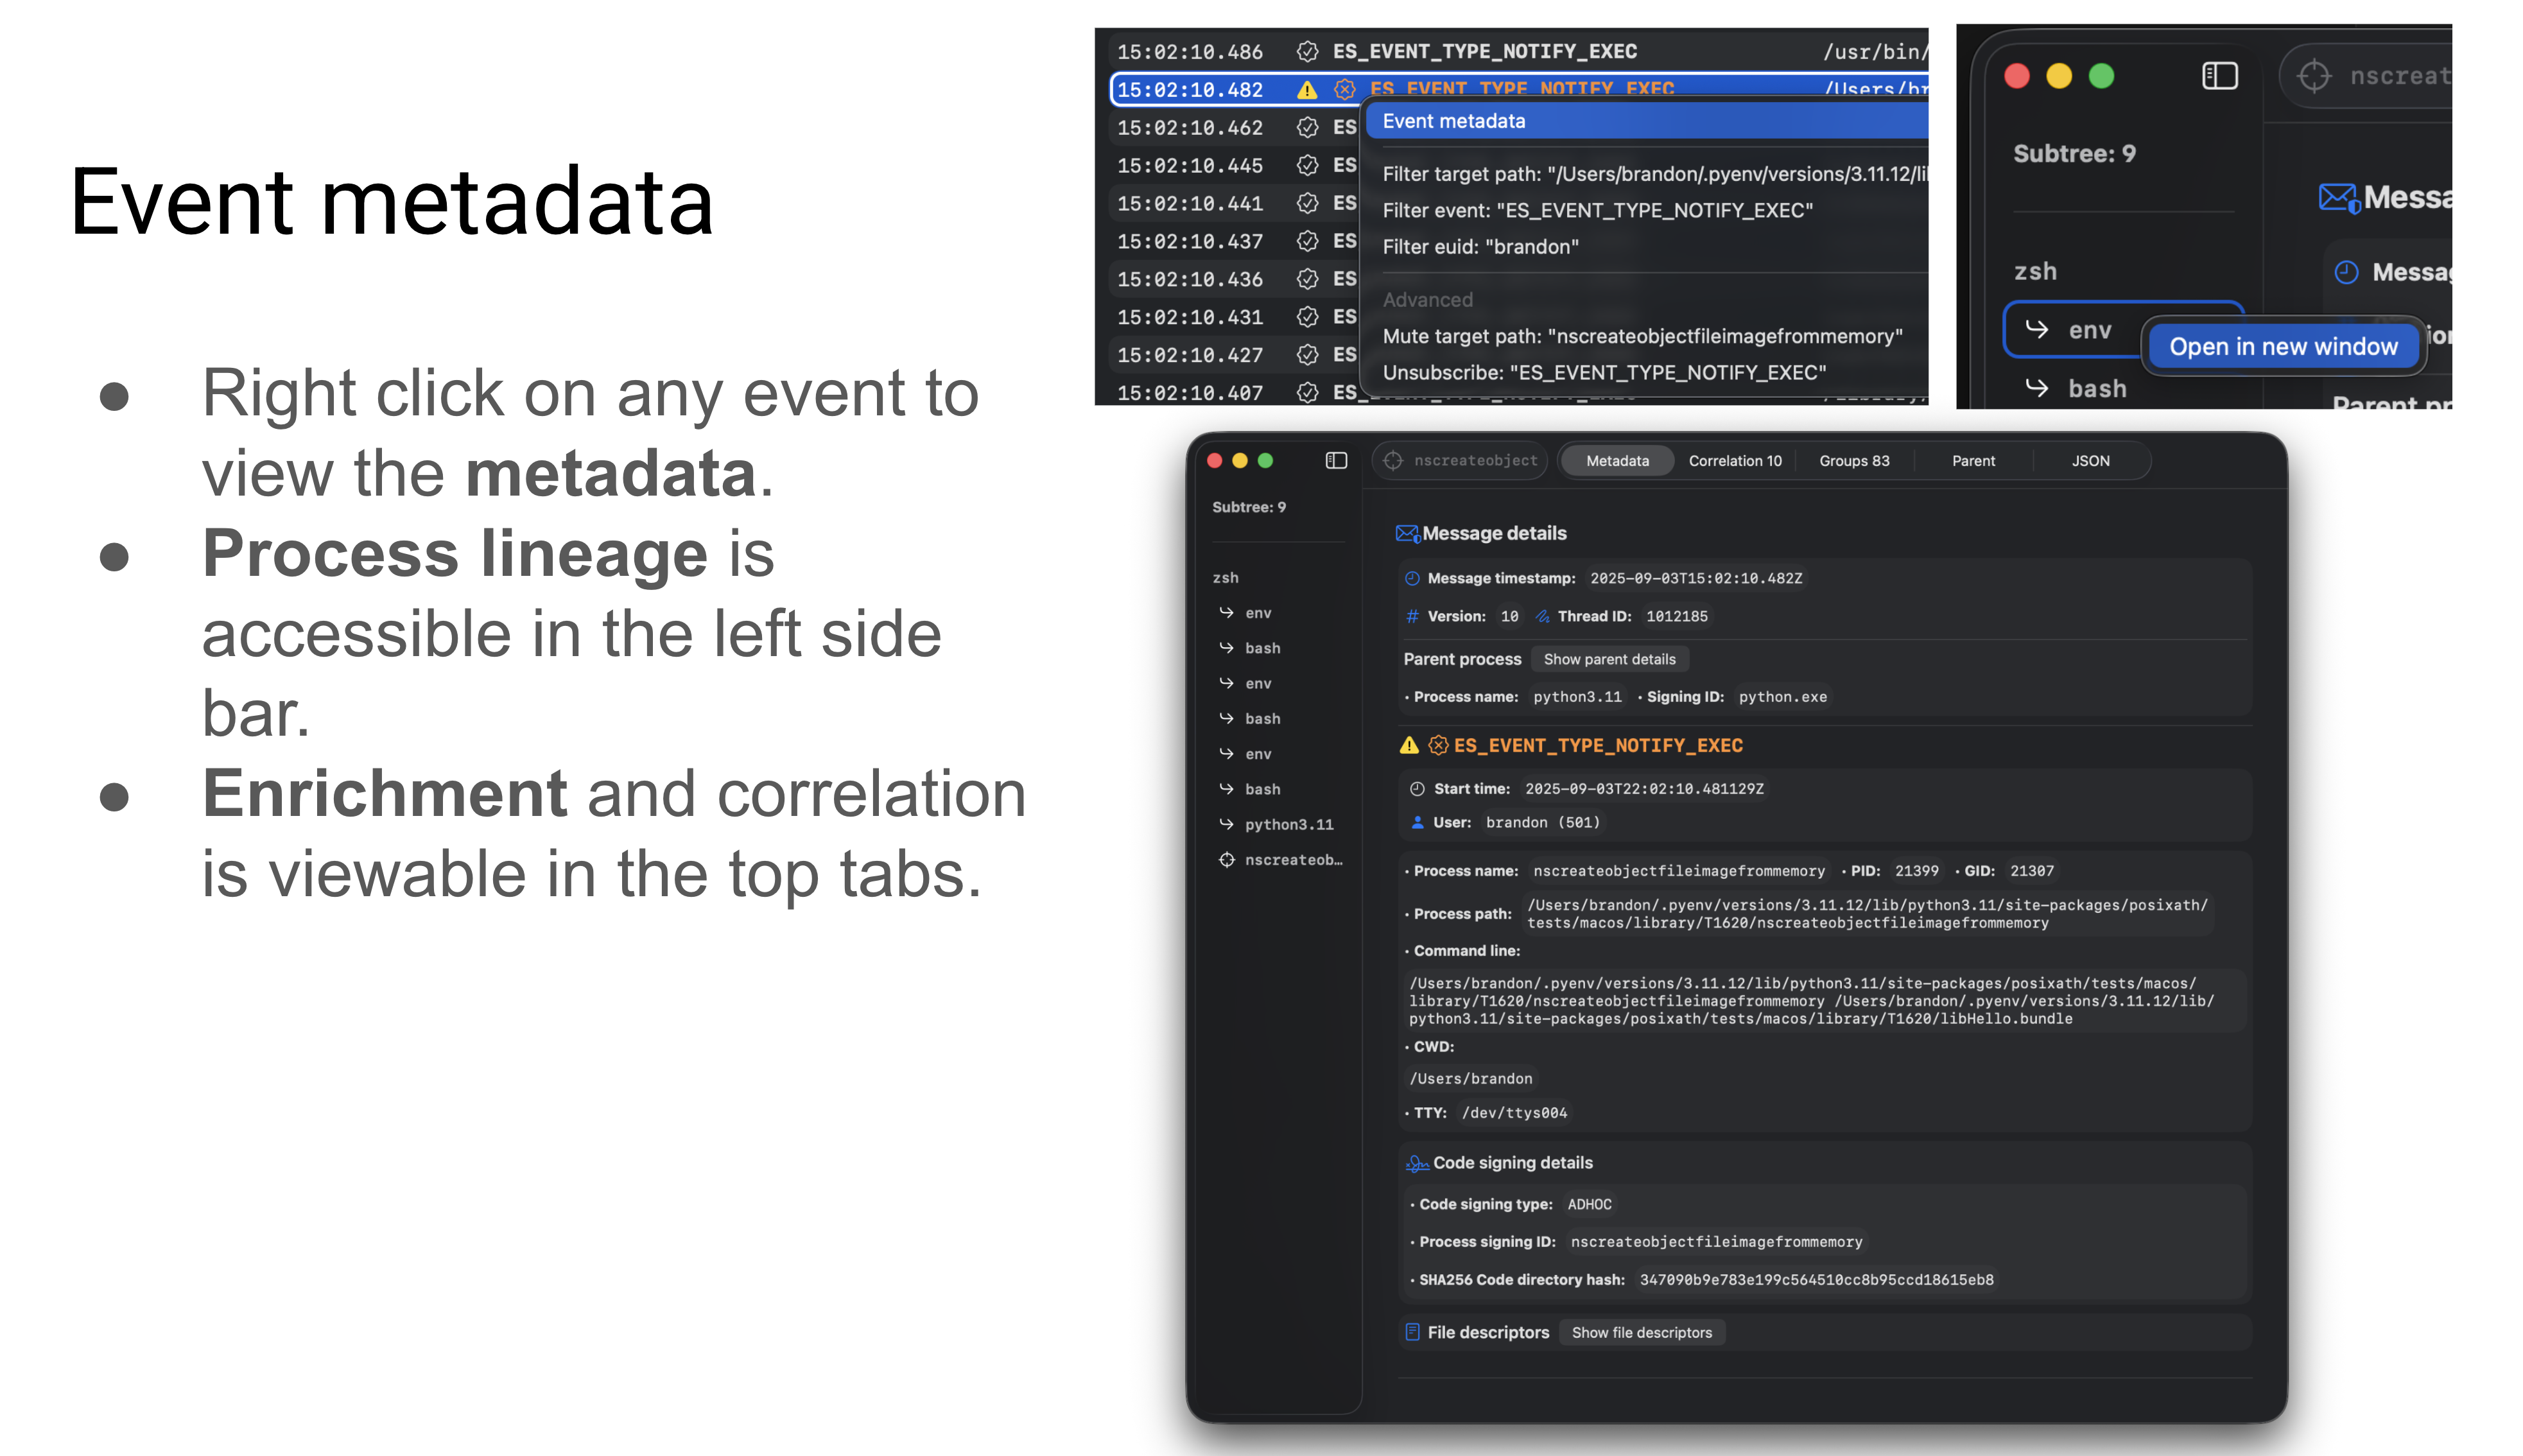 brandon7cc/mac-monitor
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 cleasbycode/jdvrif
Steganography Tool for JPG Images
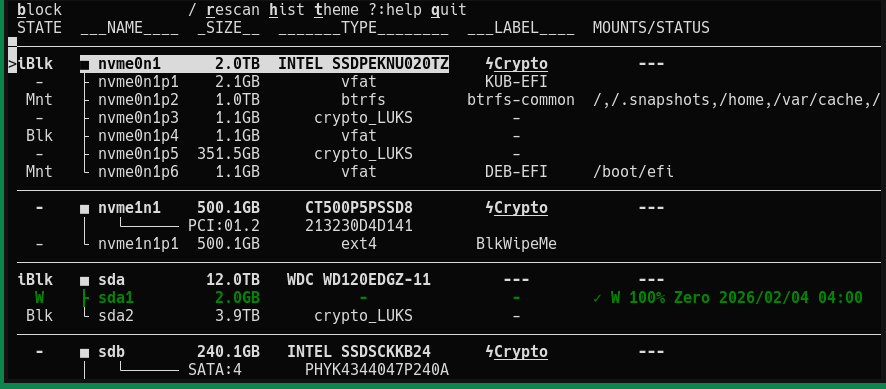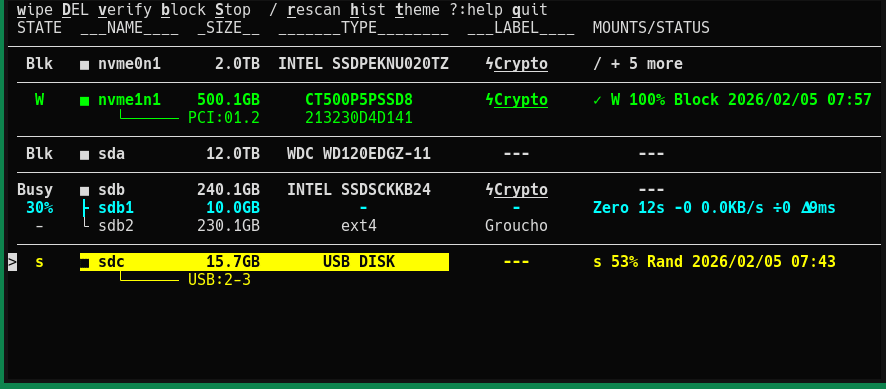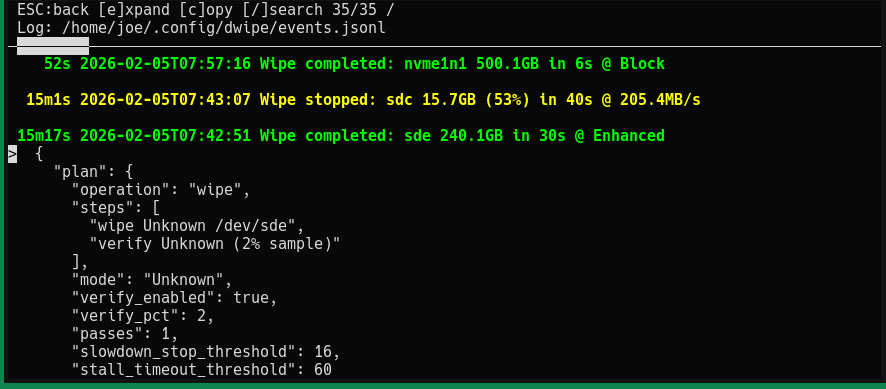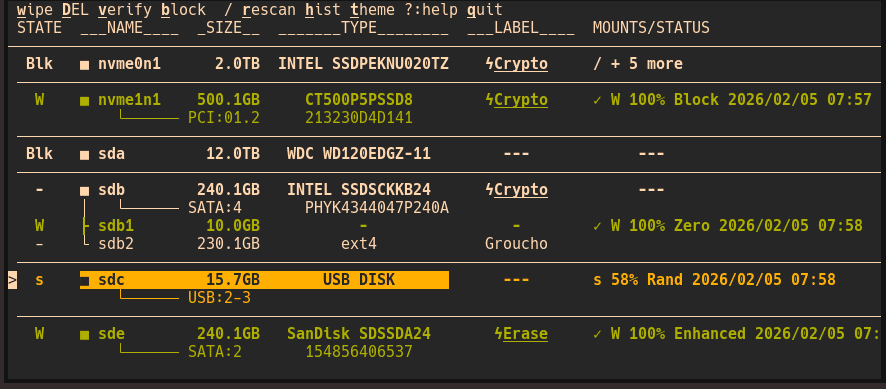 joedefen/dwipe
Tool to securely and efficiently wipe devices and partiitions for Linux
 owasp/agentic-evidence
OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox