
FLAIR
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
digital-forensicsforensicsincident-response+2
withsecurelabs/flairLightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 qazeer/farsightad
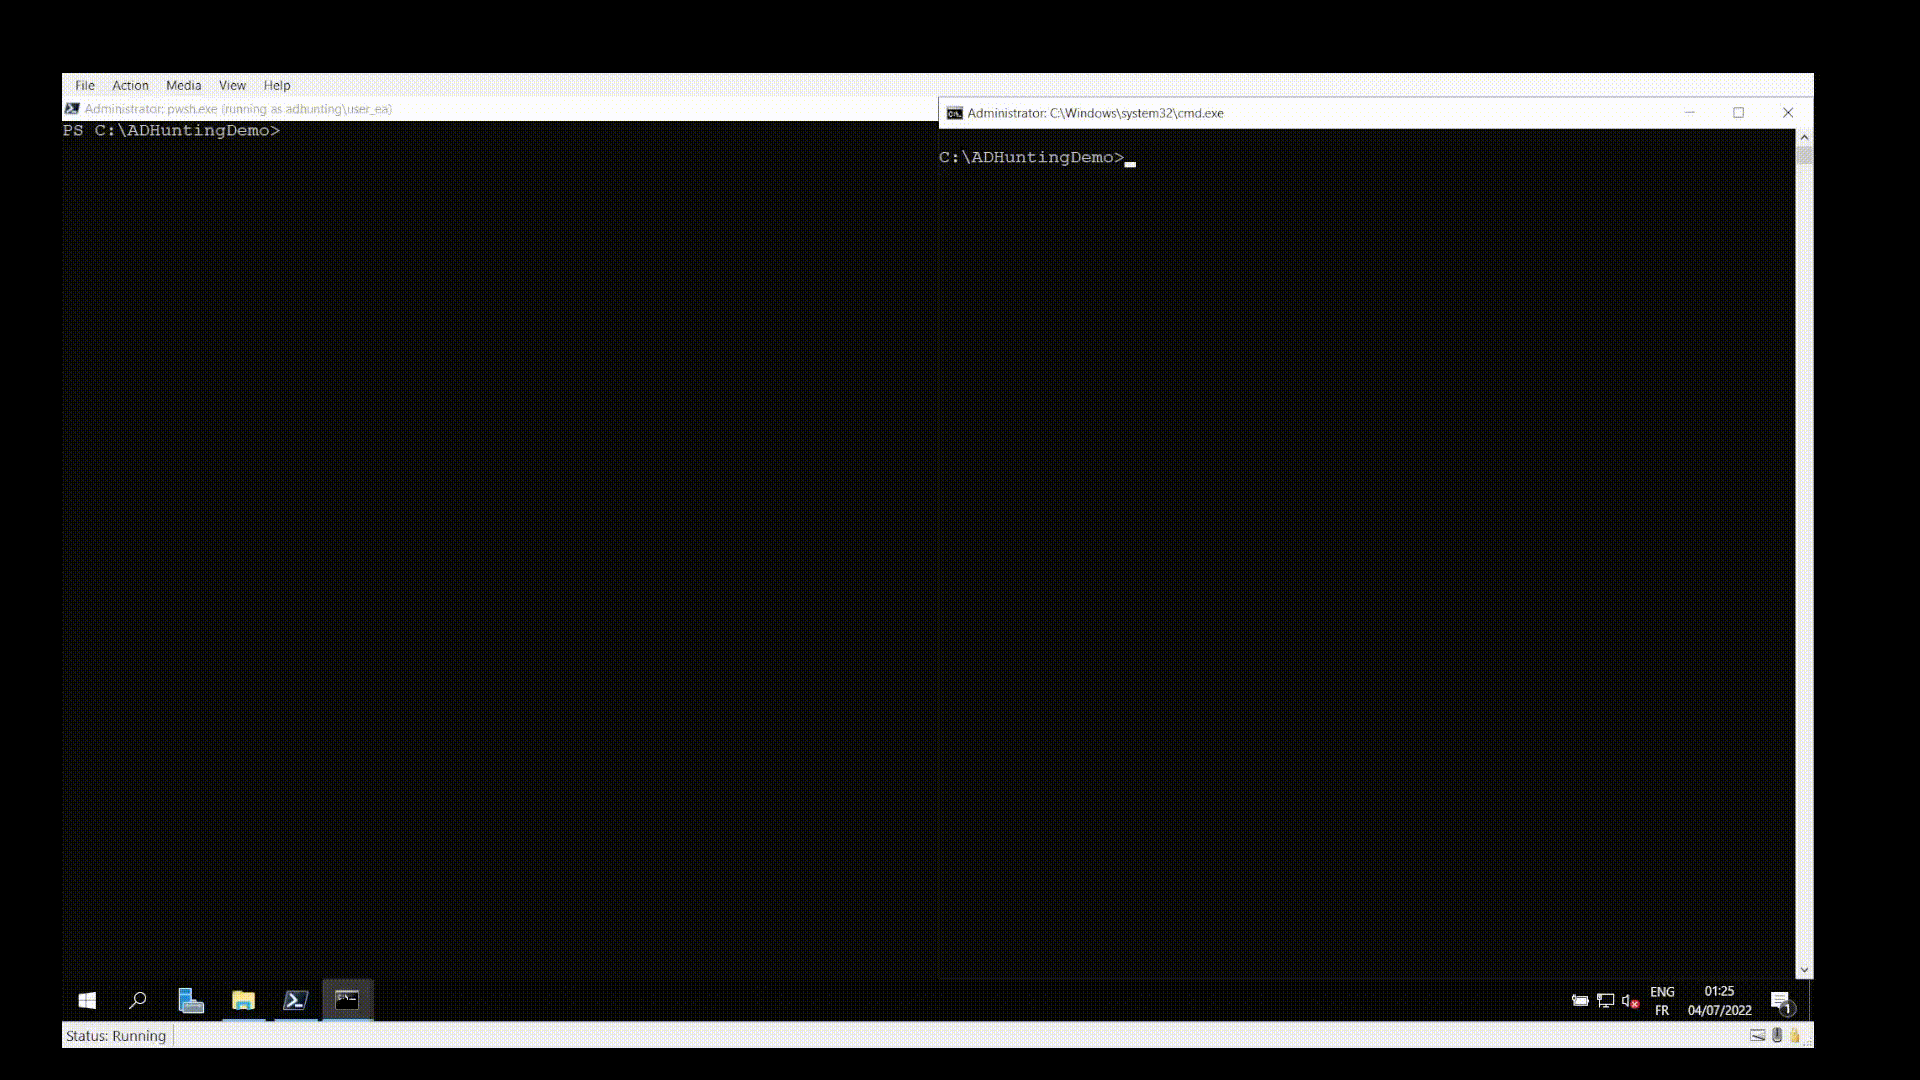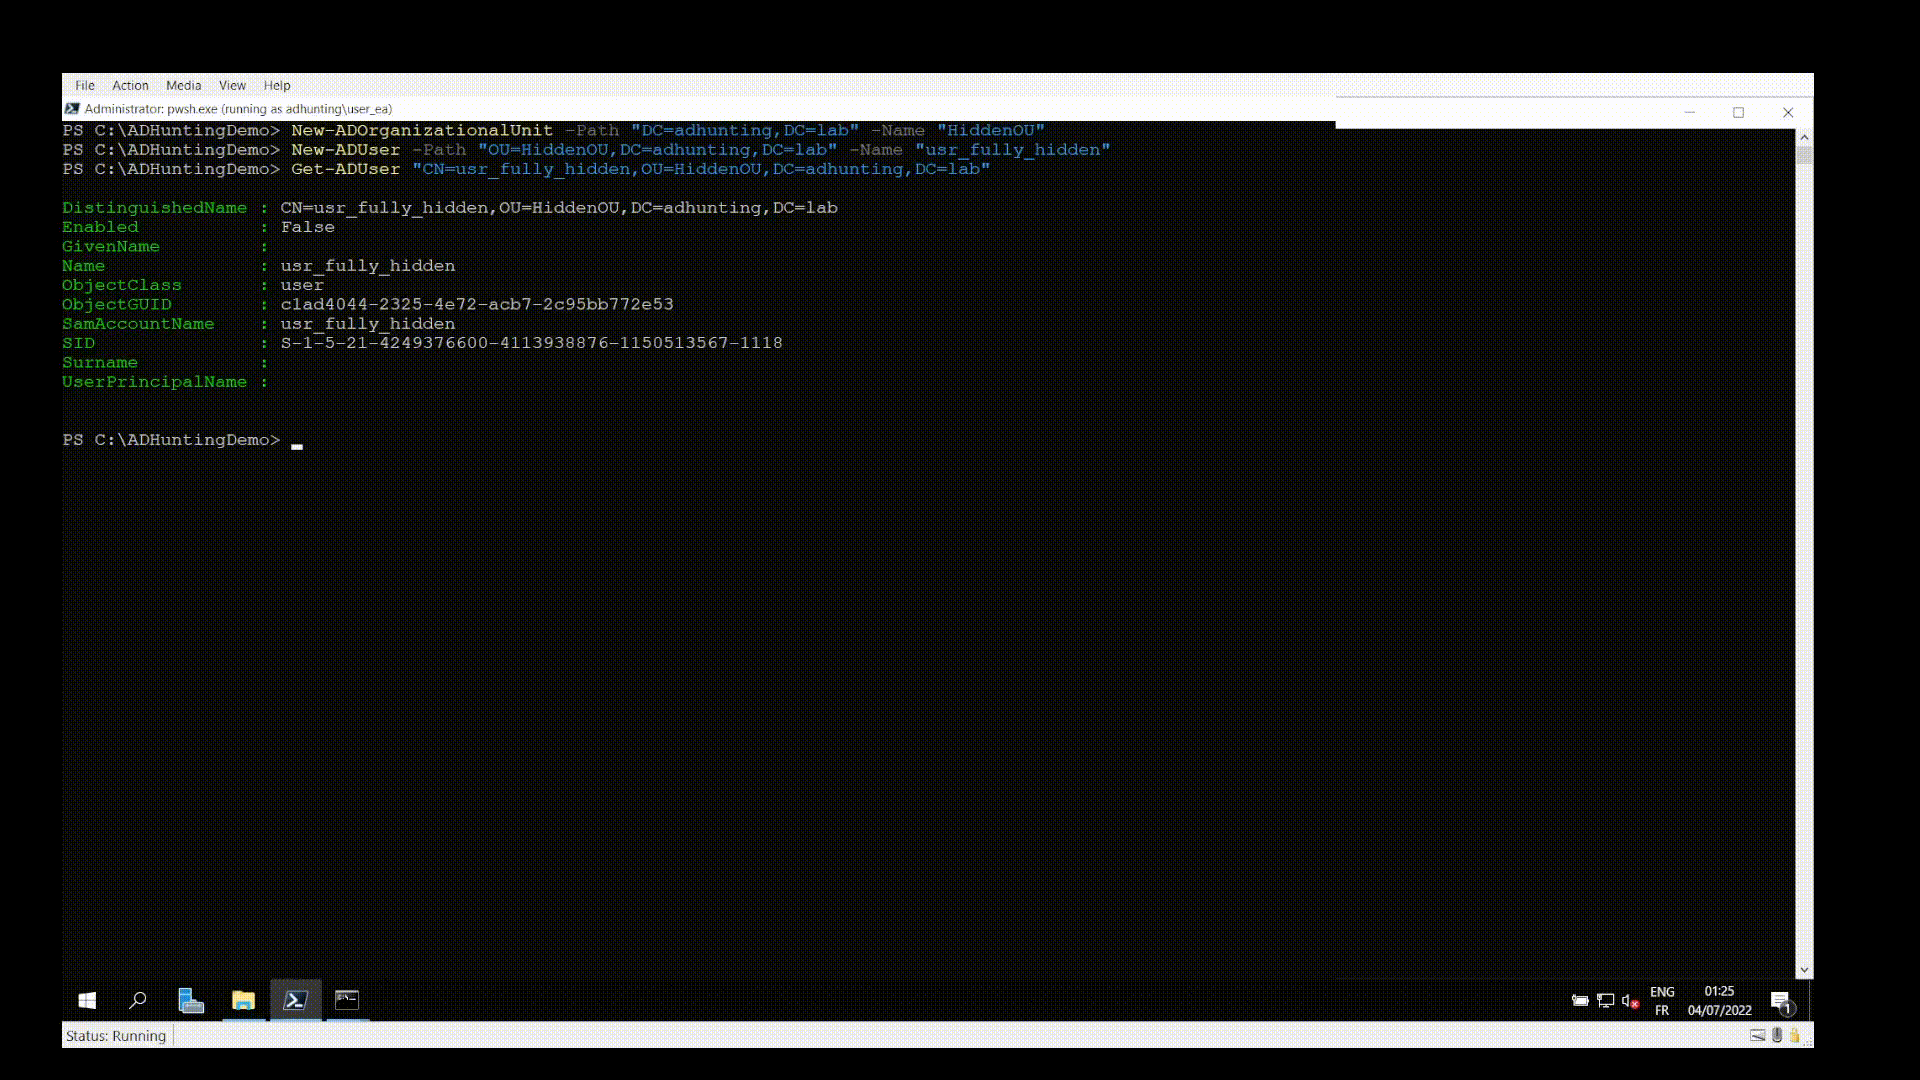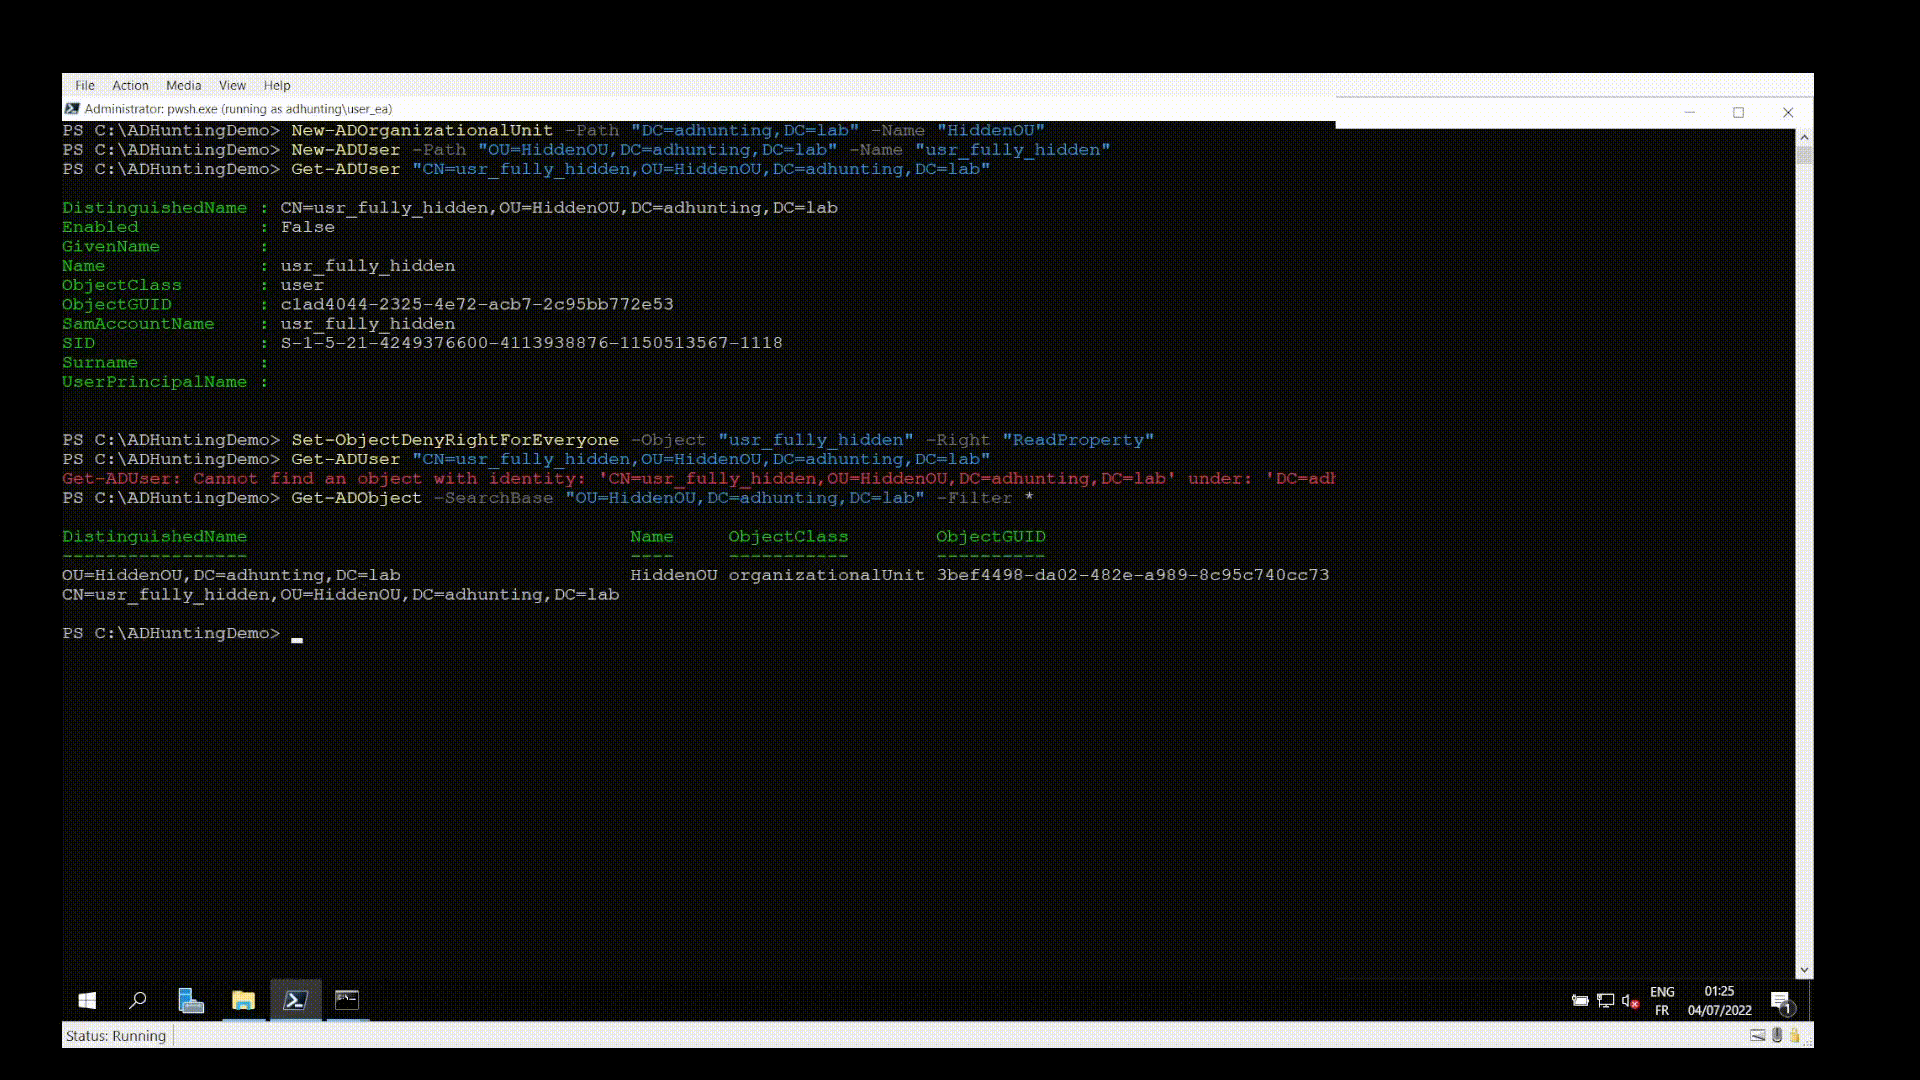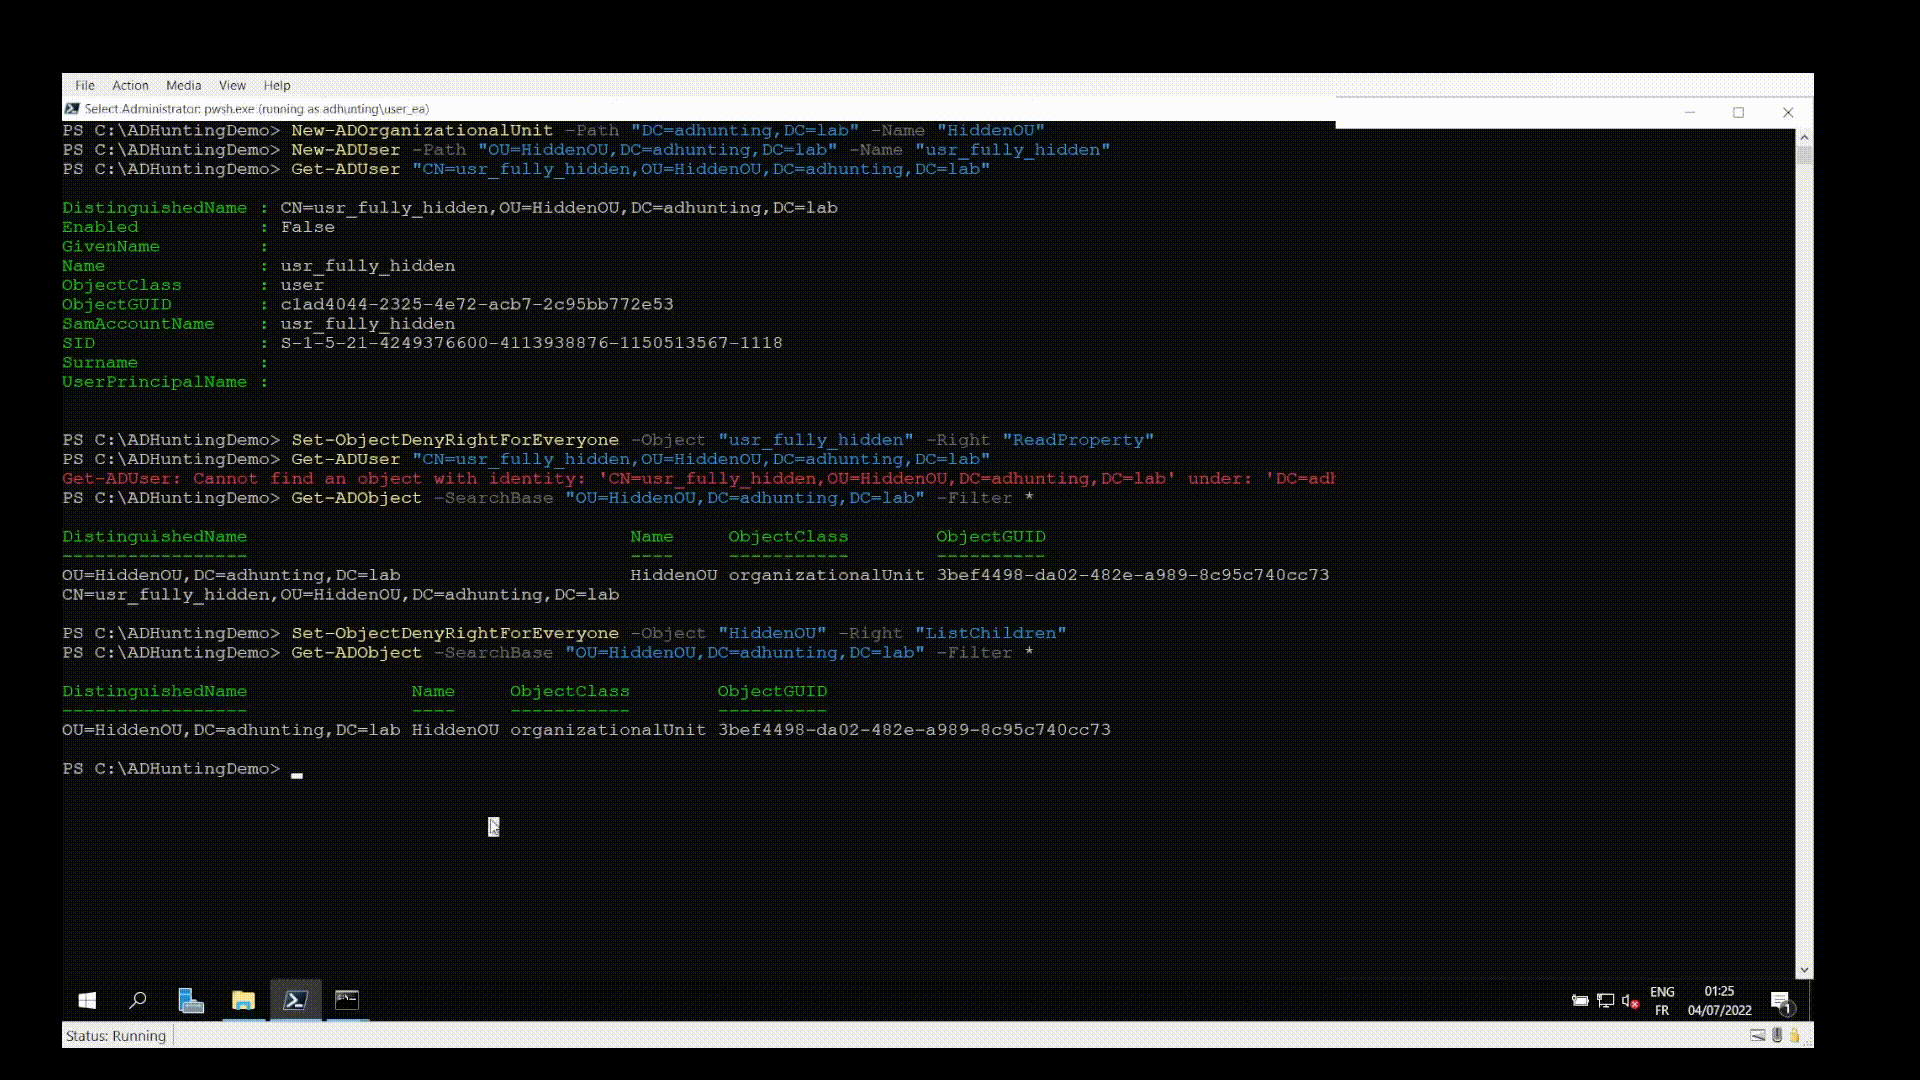
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
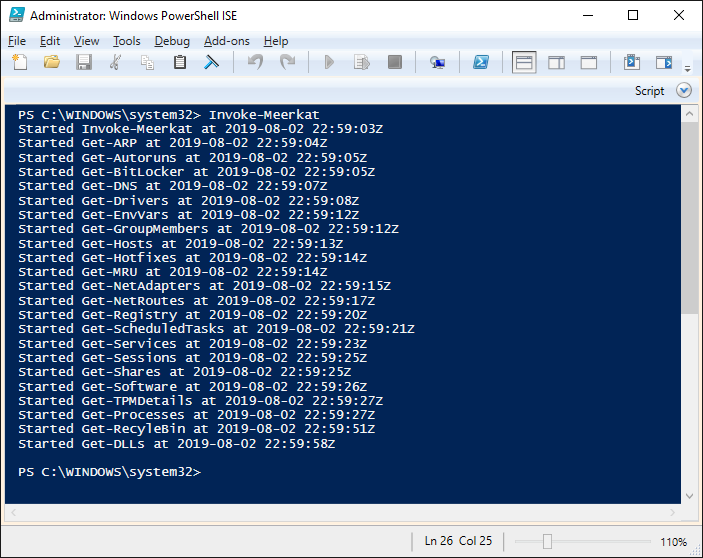 tonyphipps/meerkat
A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.